Destroylist
Every confirmed domain, published openly and updated around the clock. 220K+ entries.

Inside PhishDestroy · since 2019
How a phishing domain goes from first report to offline in minutes: where we find it, how we confirm it, what we keep as evidence, who we notify, and how we make sure it stays down.
The process
The same pipeline handles a single report or thousands a day. Nothing is reported before it is verified and captured.
Step 01
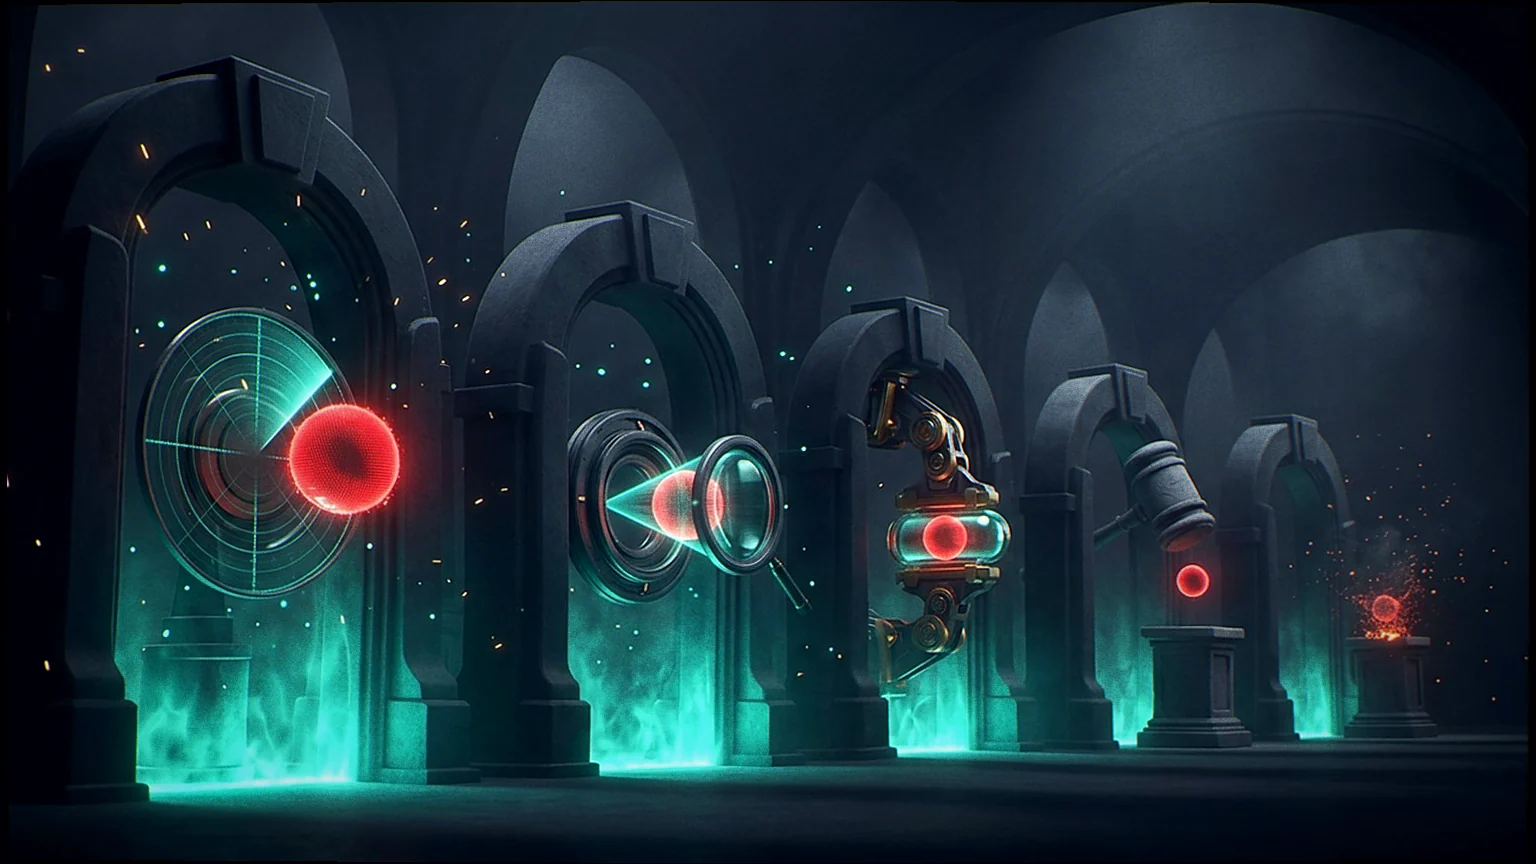
Leads come from three directions: people who report links to our Telegram bot, our own parsers that watch search ads and new domains, and feeds shared by partners and researchers.
Step 02
Nothing is reported until it is confirmed. Analysts and automated checks look at the page, the payload and the targeting. False positives stay under 0.5% across 100,000+ validated reports. Contributors with 100+ accurate reports get trusted status and skip moderation.
Step 03
Before the report goes out, the site is captured: HTML, screenshots, network calls and JavaScript payloads, through urlscan.io, the Wayback Machine and our own snapshots. Scammers delete their traces. We keep copies.
Step 04
Reports go to the registrar, the host and more than 50 antivirus vendors and threat-intel platforms that recognise our submissions. A confirmed phishing site can be offline within minutes. Cases with attribution or money trails go to law enforcement or CERT teams as full evidence packages.
Step 05
A takedown is not finished when the abuse desk replies. We keep checking until the site is offline and stays offline, and re-check removed domains so resurfacing infrastructure is caught within hours.
Speed
When PhishDestroy started, taking down one malicious domain could take weeks. The same takedown now often takes minutes.
Most of that comes from two things: tooling we keep improving, and the reputation behind our reports. We have focused on phishing and almost nothing else since 2019, which kept the false-positive rate low and earned the trust of the companies that act on what we send.
Detection
Phishing rarely hides. It has to advertise to reach victims, and that is where we catch it.
People send links to @PhishDestroy_bot on Telegram. It is our main public intake. @PhishDestroy_bot
Custom parsers watch Google Ads, Bing and Yandex sponsored results for wallet, exchange and bridge keywords, so a scam is caught when it first pays for placement.
Threat-intelligence feeds shared with us by partners and independent researchers.
Honeypot networks and seed-phrase canary tokens alert us the moment scammers try to use stolen data.
Monitoring of new registrations and Certificate Transparency for look-alike domains aimed at protected brands.
Evidence
Every operation leaves a trail that supports attribution and prosecution long after the domain is gone.
Every confirmed domain, published openly and updated around the clock. 220K+ entries.
Admin panels, Telegram chat exports, payment flows, victim records and IOCs from scam operations.
140,000+ phishing reports from our suspended X account, kept public.
Registrars
How fast a takedown happens depends on the registrar and the host. Our data splits them into two groups.
Act within hours
Ignore abuse reports
In practice this makes them safe havens for scam operations.
Pushback
We read organised backlash as confirmation that the takedowns cost scammers money.
Attacks on our infrastructure, absorbed by Cloudflare.
Coordinated PR placements against us.
Organised reporting of our social accounts to get them shut down.
Our account with 140,000+ documented reports was suspended after registrar pressure.
Who we are
Our job is to document and dismantle malicious operations, then support the people with legal authority to act on the evidence.
Non-profit. Not a company or legal entity, with no ties to any government.
Reports and evidence are published on GitHub, Telegram and Mastodon. Nothing is held back.
In major cases we hand full evidence packages to law enforcement or CERT teams, only when the intelligence is verified and actionable.
We store no personal data about contributors. That protects whistleblowers, and leaves nothing to leak.
By the numbers
Join in
Every takedown on this page started with a report. Collective action is the strongest defence we have.
Send a suspicious link to the bot and get an instant check.
@PhishDestroy_botUse the form if you have more context: screenshots, wallets, how you found it.
Open the formNew takedowns and campaigns, posted as they happen.
@PhishDestroyAlertsAdd the list to your DNS filter, firewall or security stack.
Get the listKeep reading
 Investigation$0 Takedowns: how we disrupt phishing infrastructure
 MetricsImpact metrics: 500K+ phishing threats neutralised
 InvestigationNameSilo, Webnic, NiceNic: registrars enabling scams
 ToolkitTools for fighting phishing: 225 tools, checked and linked
PhishDestroy is a non-commercial, independent project, and our research may carry a bias against scam infrastructure and the services that enable it. Read it critically. Transparency statement · Blog archive