How We Operate
Our model is boring on purpose. We scan for phishing infrastructure, archive evidence, file structured abuse reports, and remove domains. There are no PR wars or ego plays, just automation and email.

Published Updated
Since 2019, we've removed thousands of phishing domains at zero cost. Scammers retaliated with DDoS attacks, fake companies, mass reports, and forged legal documents. None of it worked, and the evidence is below.
Since 2019, scammers have answered PhishDestroy's zero-cost takedowns with email floods, a UK shell company with forged documents, DDoS attacks, a forged OnlyFans DMCA notice, mass-reporting of social accounts and 9,000+ fake appeals. The page says none of it worked: after a 283M-request DDoS in March 2026 forced a hosting move, takedowns continued with zero downtime.
An estimate; filters delete the messages automatically.
On October 7 our GitHub account was blocked. So far we have no understanding of why, and we have received no email. We are looking into it. For now we have deployed at github.com/phishdestroy (GitLab) everything that was there.
We don't think it is connected to any investigation concerning elite lawyers or anyone else. We think the cause was the mass update of IOC lists covering the two weeks during which our four registrar repositories and ShortDot were not working. But any ban has a reason. Possibly an automatic trigger fired.
Overall, we don't blame or accuse anyone until the real reason is known. It is also possible that the very fact that we maintained a phishing database violates GitHub's rules, but that is not certain. We are not going to make a tragedy out of this or shout that someone got it banned. That is not the case.
github.com with gitlab.com.Our model is boring on purpose. We scan for phishing infrastructure, archive evidence, file structured abuse reports, and remove domains. There are no PR wars or ego plays, just automation and email.
No doxx by default. We focus on infrastructure, not individuals. When threat actors cross legal lines (threats, fraud, identity theft), we escalate to law enforcement with full evidence packages. Otherwise, we just turn off their domains.
Over the years, threat actors have thrown everything they could think of at us. Below is every tactic they tried, and why each one was a waste of their money.
| Attack | Method | Their Cost | Our Impact | Status |
|---|---|---|---|---|
| Email floods | 2,000-5,000 msgs/day for months | $50-300/mo | Zero | Failed |
| UK shell company | Paper company + forged "ownership" docs | $500-2,000 | Zero | Failed |
| Social takedowns | Mass-reporting X, Telegram, Medium | $100-500 | Accounts suspended, archives live | Nuisance |
| DDoS attacks | Rented botnets against our lander | $200-2,000 | Zero | Failed |
| Bot farms | Fake followers/likes/reports | $50-300 | Zero | Failed |
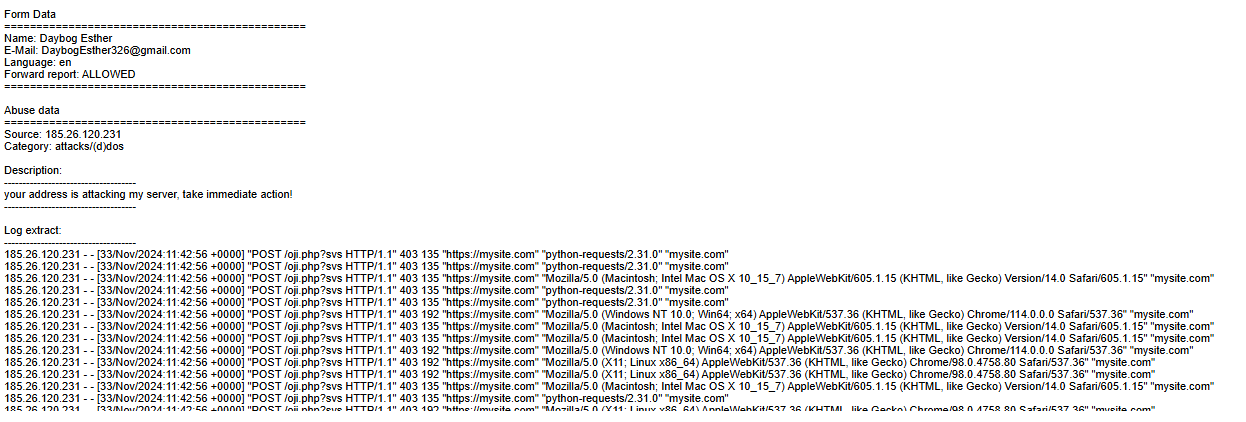
| False abuse reports | Fake complaints to our hosting provider | Time | Zero | Failed |
| Content swapping | Inject illegal content to trigger auto-bans | Time | Zero | Failed |
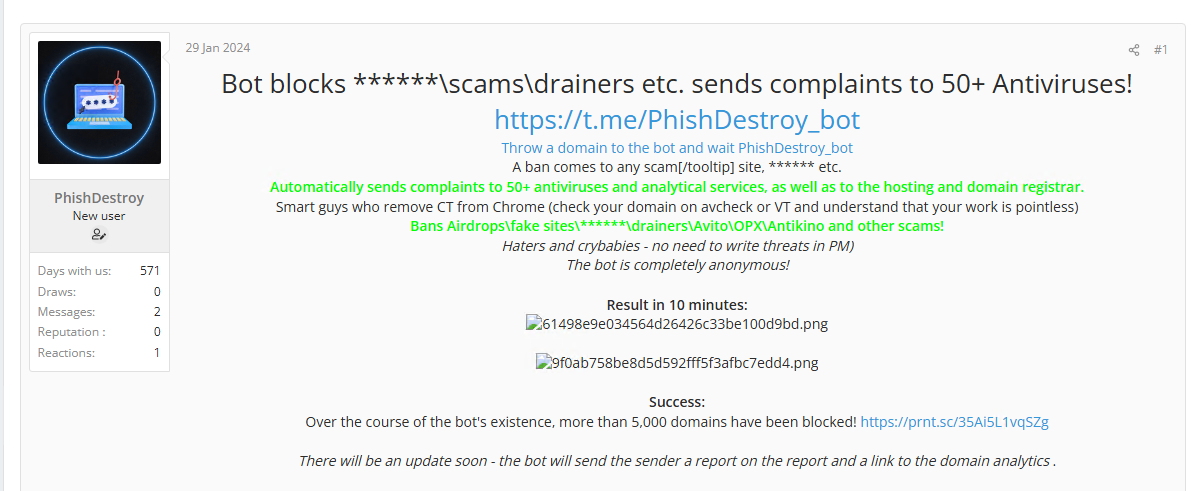
| Impersonation | Fake "Russian hacker" forums selling our work | Time | Zero | Failed |
| DDoS → host kill | 283M requests / 1.21 TB (Namecheap dropped us) | $2,000+ | Migrated to Cloudflare + Hetzner | Nuisance |
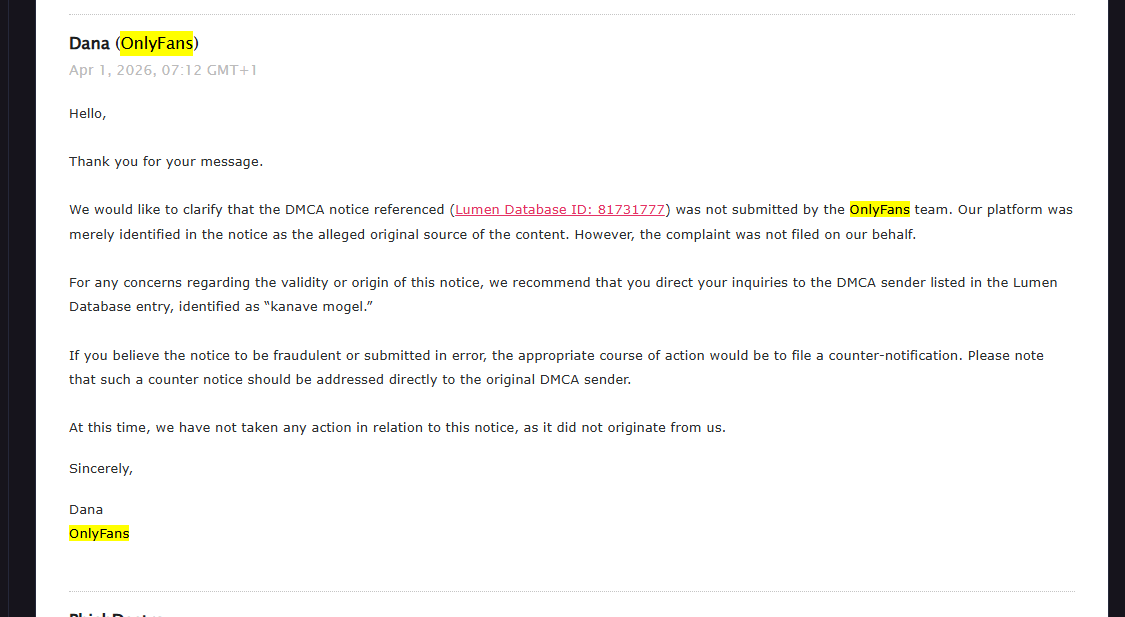
| Fake DMCA | Forged OnlyFans copyright claim to Google | Time | Zero (OnlyFans denied filing) | Failed |
| Trust user infiltration | Trusted user injected 46 false-positive domains | Time | Caught fast, hardened all roles | Failed |
| Appeals form spam | 9,000+ fake domain appeals via hCaptcha solving | $100-500 | Zero (trivially filtered) | Failed |
| Email bombing (ongoing) | 400,000+ messages, non-stop, auto-deleted | $500+/mo | Zero | Failed |
| X/Twitter ban (again) | Gov-style emergency request → account suspended | $3,000+ | Not restoring. Done with X. | Nuisance |
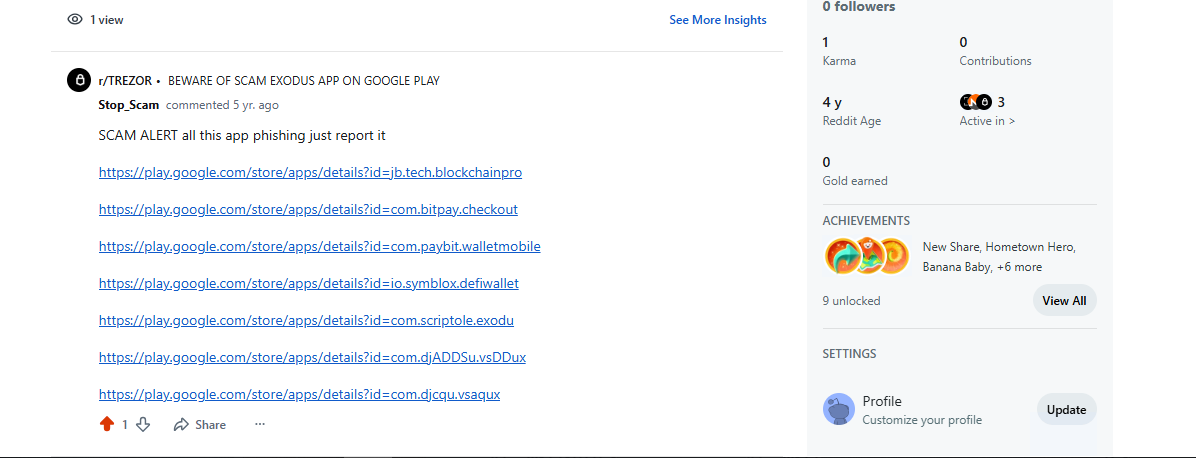
| Reddit ban | Account banned. 1 post from 5 years ago. | Time | Zero | Failed |
They spend $3,000+ per "government-style" social takedown. We spend $0 per domain removal. Our takedown pipeline is email-based automation, and the website is optional. DDoS attacks against a lander are like bombing a billboard: the mail trucks keep moving.
Below is documented evidence of specific incidents. Click any card to view the full-size screenshot. All evidence is preserved for transparency and potential legal proceedings.
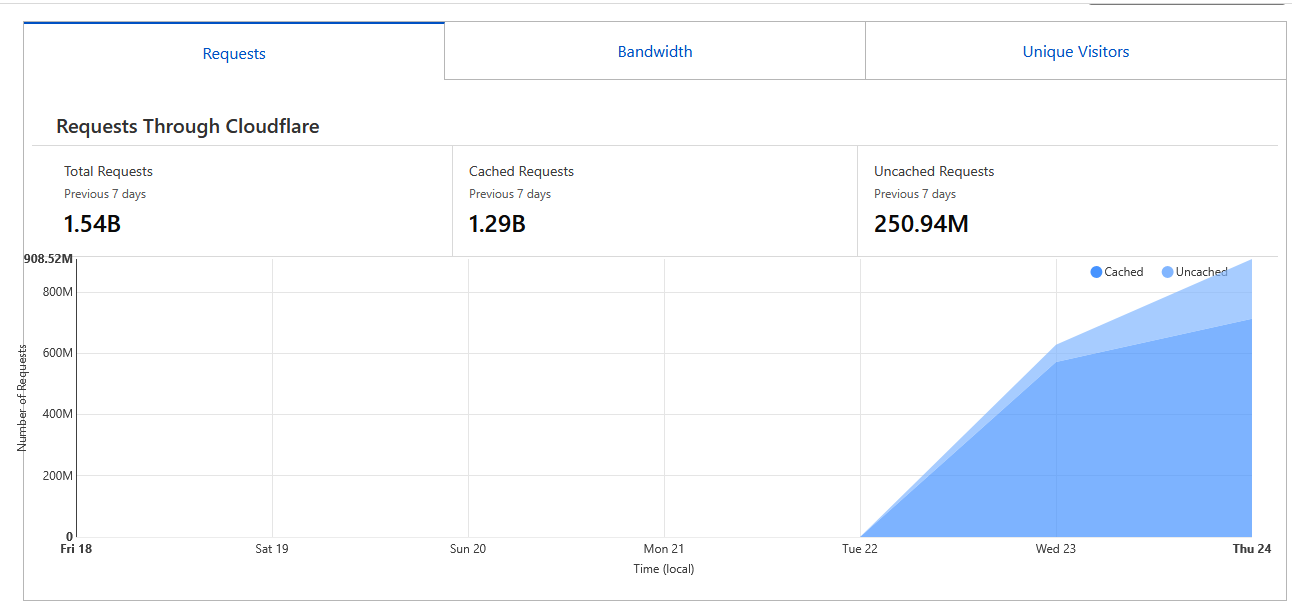
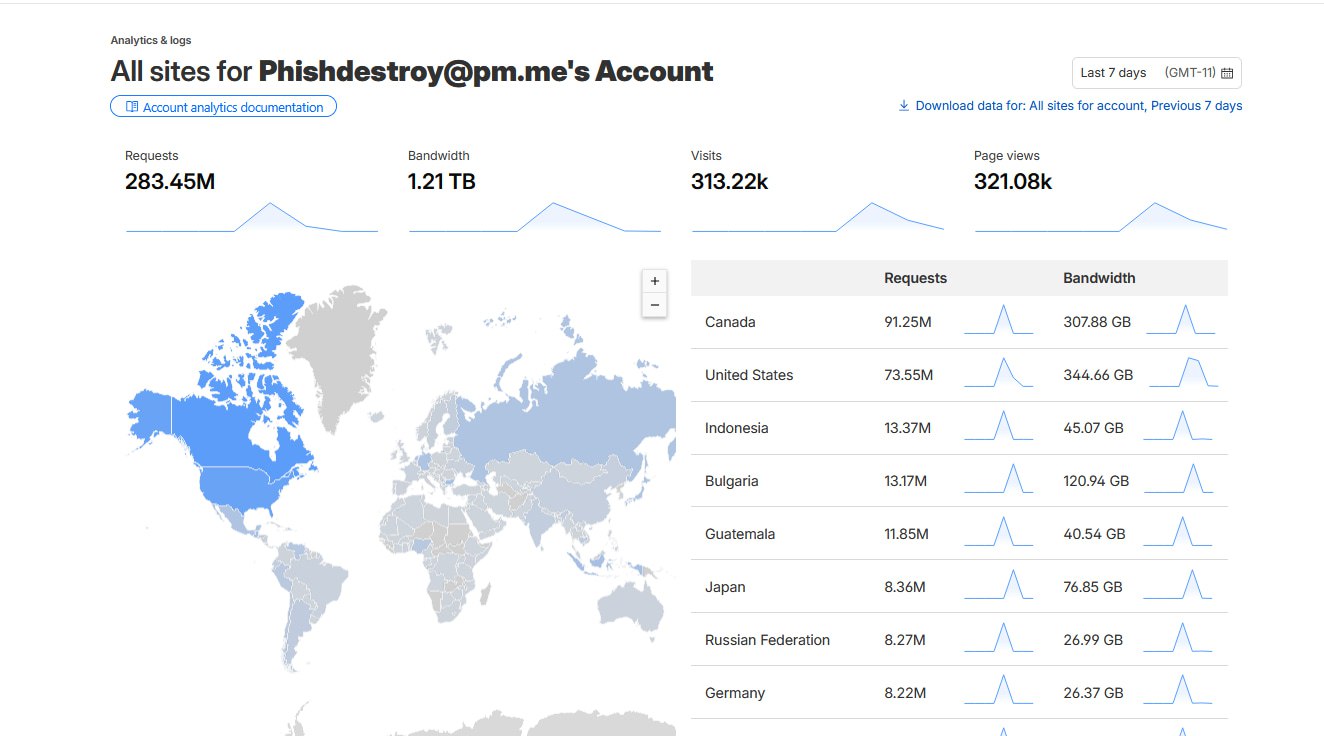
On March 6, 2026, scammers launched the largest DDoS attack against our infrastructure to date: 283.45 million requests and 1.21 TB of bandwidth in just 7 days. The attack came from a global botnet spanning Canada (91M requests), United States (73M), Indonesia (13M), Bulgaria (13M), Guatemala (12M), Japan, Russia, and Germany.
Namecheap's $8/month hosting couldn't handle it and terminated our account. We migrated to Cloudflare + Hetzner ($25/month). After the migration they tried again and, predictably, face-planted. Cloudflare absorbed everything without breaking a sweat. We had zero downtime and zero impact on takedown operations.
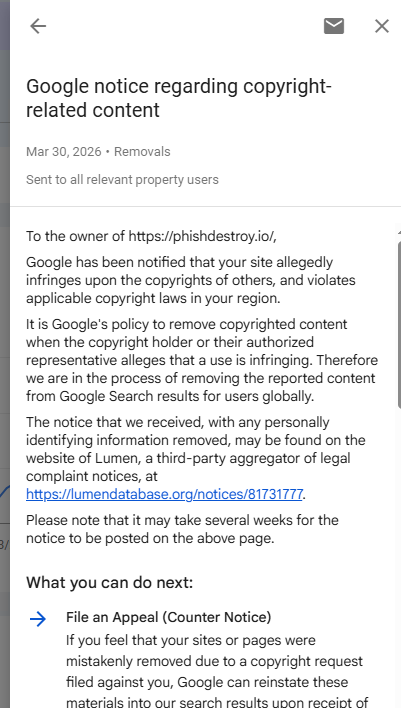
On March 30, 2026, Google notified us of a copyright complaint against our domain report page phishdestroy.io/domain/hbmhcw.net/. The claim alleged that our page contained copyrighted OnlyFans content belonging to performers "Mibadbitch, Bri naranjo, or Brianna naranjo". The complaint was filed by someone named "kanave mogel".
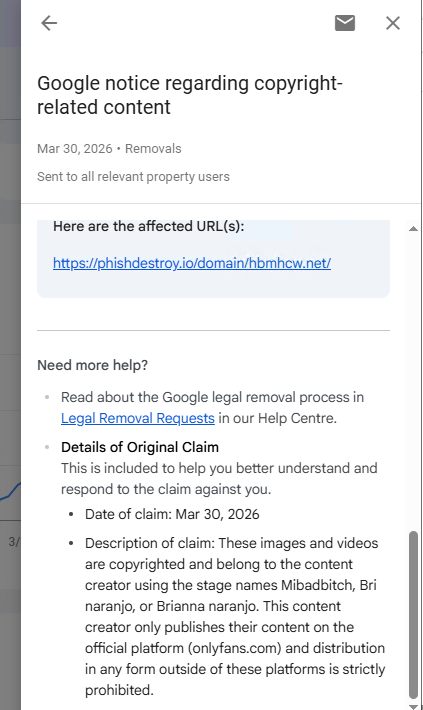
We contacted OnlyFans directly. Their response was clear: "The DMCA notice referenced (Lumen Database ID: 81731777) was not submitted by the OnlyFans team. Our platform was merely identified in the notice as the alleged original source of the content. However, the complaint was not filed on our behalf."
lumendatabase.org/notices/81731777: the full fraudulent DMCA notice is public record. It was filed by "kanave mogel", a scammer trying to use copyright law to remove evidence of their phishing domains from our reports.
Our social accounts are systematically targeted. Accounts on X (Twitter), Telegram, Medium, and Reddit were all suspended or banned through mass reports, likely using forged government emergency requests. Our latest X account was killed in April 2026. We've decided not to restore it. We're done playing whack-a-mole with platform suspensions.
After the second suspension, we decided: enough. We're not wasting time restoring accounts on platforms where scammers with money can file fake government requests to kill accounts. Our operations never depended on social media. The takedowns continue regardless.
We tell the truth and help block what needs to be blocked. Some people don't like that. They think banning or deleting our accounts will stop us or hurt us. We're not complaining; honestly, it's funny at this point. We're ready for any bans and takedowns. Scammers with money and no brains = buying attacks and attempting to destroy us. But PhishDestroy is still here. And we destroy.
Every action we take follows a strict evidence preservation protocol designed for maximum transparency and potential legal proceedings:
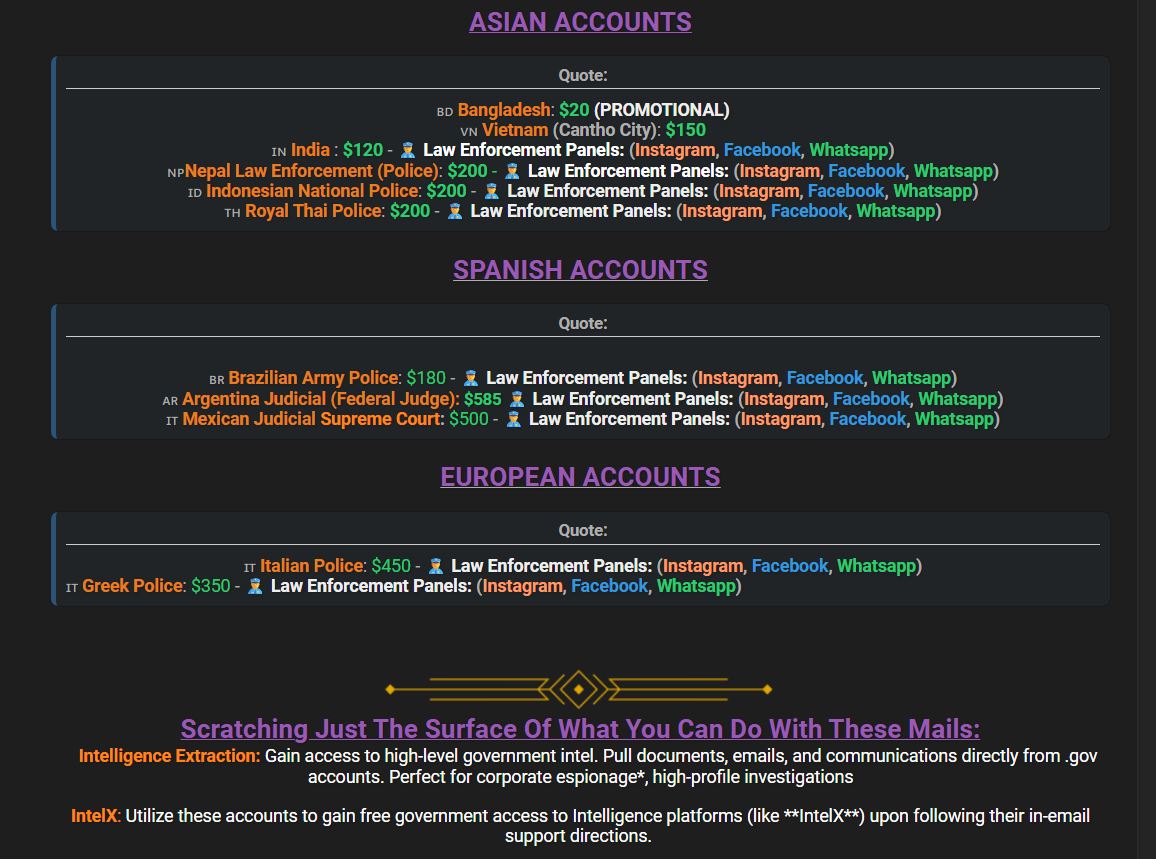
Infosecurity Magazine: Law Enforcement & Government Emails. Registrar response quality varies dramatically. Namecheap consistently acts fast; others, less so.
Our cost structure is asymmetric on purpose: every dollar they spend on retaliation is wasted, and every domain we remove costs us nothing.
| Their spend | Our spend |
|---|---|
| $3,000+ per "government-style" social takedown | $0 per automated abuse report |
| $200-2,000 for DDoS botnet rental | $0 (behind Cloudflare, email flows continue) |
| $500-2,000 for UK paper company + legal forgeries | $0 (private registration, claims auto-rejected) |
| $50-300/mo for email flood services | $0 (we don't use inbound email for operations) |
| $50-300 for bot farm fake reports | $0 (reported and wiped by platforms) |
They burn thousands trying to stop us, while we spend $0 to remove their infrastructure. Our automation scales, and their panic does not. We warn them: "your infra turns off soon", and then chaos begins on their end. Meanwhile, we keep it boring: scan, archive, report, remove.
If you've encountered a phishing site or want to contribute to the fight against crypto scams, start here: