


Emergency: I Was Scammed
Immediate steps if your crypto wallet was drained. Revoke approvals, secure remaining assets, and report the crime.
Get helpIndependent · Open data · Since 2019
Investigate phishing infrastructure. Inspect public evidence. Put open threat intelligence to work.
PhishDestroy is an independent, non-commercial anti-phishing research team. Our team includes researchers with OSCP, GWAPT and BTL2 certifications. We document phishing infrastructure, preserve public evidence and publish open threat intelligence.
Live Intelligence
Recently stored phishing detections from the public feed.
01 / Investigation tools
From a first signal to a deeper investigation. Public data and practical tools, freely accessible.
Per-domain dossiers: WHOIS, DNS, TLS, VirusTotal, cloaking, kit fingerprint, abuse-report history. Searchable.
Browse reports →Stream of phishing detections as they happen: domain, brand, registrar, cloaking flags. Refreshed continuously.
Watch the feed →Paste any URL to get VirusTotal consensus, drainer-kit fingerprint, cloaking test, SSL chain and a screenshot.
Analyze now →Check a domain, pull a feed, bulk-scan 500/req. 1M+ threat records, CC-BY licensed, zero cost.
Read API docs →Drainer and rug-pull wallets across EVM + Solana, browsable by network. Search is paused.
Browse wallets →Community-curated threat feed on GitHub. Auto-updated domain blocklist for firewalls, DNS filters, browser extensions.
View on GitHub →02 / How it works
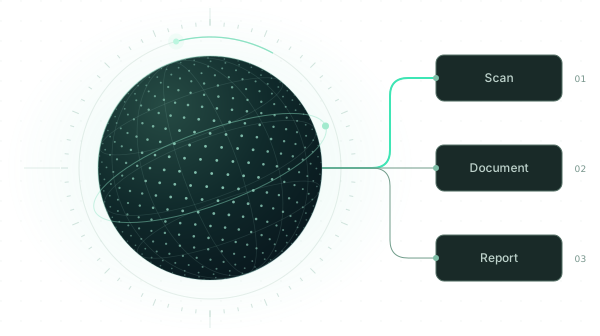
Follow the evidence. See how a suspicious link becomes a documented case — and an abuse report.
Suspicious URLs surface through community reports, public feeds and infrastructure monitoring.
Reported to registrars, hosts and CDNs.Counted from our report log and refreshed hourly.
LIVE / Latest signals
03 / Explore the platform
Research the infrastructure, explore the data, or find the right tool for your next step.
They call us Enemy #1
Scammers repeatedly target our infrastructure to escape reports and bans. The outcome stays the same: evidence remains public, detections continue, and our takedown reporting costs users $0.
Domains tracked
Abuse reports sent
Confirmed takedowns
Paid to registrars or platforms for takedowns (ever)
04 / Recognize the approach
Where scammers reach you — and the detail that gives them away. Choose a channel to see the setup.
A sponsored result can imitate a wallet or exchange and lead to a lookalike domain.
Simple rule: never share a seed phrase or sign an unexpected transaction to "verify" a wallet.
See all scam channelsLearn to spot the setup
Knowledge is your best defense. Learn the most common deception tactics to avoid becoming the next victim.
 Emergency response guide
Take the next step
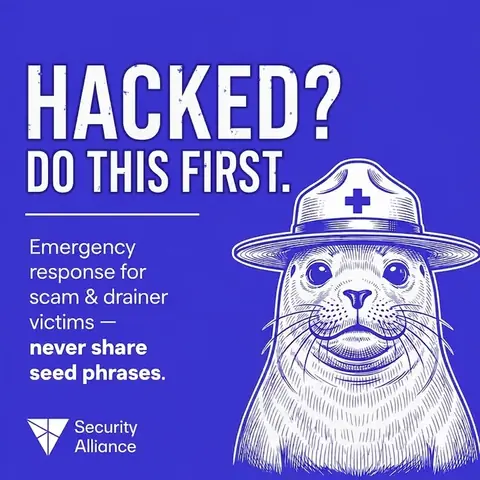
File a report. Start with Chainabuse — it takes five minutes and creates a public record. Then report to your local law enforcement: most countries have a cybercrime unit, and filing matters even when recovery is unlikely. For active incidents — wallet drained, funds still moving — contact Seal911 directly. They respond fast and know the chain.
Be extremely cautious of "recovery services" that contact you after a theft. Most are recovery scams trying to victimize you a second time.
For Developers
Free, open, no API key. Real-time domain risk scoring across 1M+ threats.
No API key required · Sources: DestroyList and community reports · Full endpoint reference ↗
Protect Yourself
Immediate steps if your crypto wallet was drained. Revoke approvals, secure remaining assets, and report the crime.
Get helpStep-by-step guide to hardening your crypto security. Hardware wallets, 2FA settings, and browsing hygiene.
Security ChecklistRecommended privacy tools, secure browsers, VPNs, and operating systems to stay anonymous online.
Privacy & Security Tools
What we do
We document suspicious infrastructure, send abuse reports and publish the evidence for others to inspect.
We help identify scam teams and prepare reports that law enforcement can use.
We reconstruct threat chains across multiple domains, assets, and wallets.
We analyze suspicious code and maintain detection rules that help identify recurring phishing infrastructure.
Hall of Shame
Satire: All characters below are fictional composites created for illustrative purposes. Not connected to real individuals. Based on public case nicknames and open reports only.


Hacker's Cry
Yo, it's Morgan, your PinkDrainer king with the Pinkboy! password! Chillin' at some address - until the UK cops crashed my party! They've got me locked up, but ha, I'm still hugging my glittery crypto stash tight - good luck prying it from my pink fingers! 2 stars for the arrest, you pesky hunters!
Hacker's Rant
Oh, behold Inferno Drainer, ghost who vanished then strutted back! 'big hits' were just backdoor thefts. It turns out Angel Drainer sold me off ages ago and played puppet master, tricking his crew with my name! Now I'm toast, and my crypto's gone - well done, you sly hunters, 4 skulls for the expose!
Hacker's Meltdown
Well, hello there, it's Phishlab - aka Pakulichev, the coding genius! Sold my MS Drainer code for $1,500 to 200 clowns who leaked, resold, and wrecked havoc! Now my masterpiece's racked up $60 million+ in damage, and I'm sitting here with peanuts in my pocket - brilliant move, eh? Time to cry into my empty wallet while you lot laugh! 🇷🇺
Hacker's Whine
Hey, it's your crew CrazY Evil, still ruling the scam scene! Angel Drainer's our real-life bro since way back - we even collabed, dropping Russian rap about scams, loving to smear the beats! But he bailed - hated how we snatch all the profit and leave workers no control, unlike his tidy Drainer setup. He's chilling in Some Hot country, sipping tea, while we keep the chaos rolling - catch us if you can! 🇷🇺
Hacker's Panic
Ha! It's AceDrainer, the pop-up wizards still on the loose! We hacked those animation libraries, flooding crypto apps with sneaky pop-ups - draining wallets like champs! Sure, our domains are getting auto-banned left and right, but we're dodging you lot for now. Keep trying, you clever detectors - 2 bans for your effort! 🌐
Hacker's Beg
Ha! It's C*** D** Loy, aka SmolGoblin, the UA scam king! Ripped off 1,000+ suckers worldwide, pocketing over $10 million - heck, one some country fool lost $2.7 million ($20M at today's rate)! Phishing, laundering via some exchange, spreading "Stealername" malware, and cruising in my Maybach S580, Tesla Model X, BMW M4 Competition, and Porsche 911! Czech cops are sniffing around. Nah, I'll race 'em instead! Catch me if you can, you legal nerds! 🇺🇦
Hacker's Surrender
Yo, it's the late CryptoLove crew, once the love bandits of crypto! Thought our phishing game was unstoppable - until RussianPanda swooped in like a ninja bear! He torched our domains, drained our wallets, and left us crying in the dust. Game over, you sly panda bastard - 5 skulls for the knockout, we're donezo! 🌐
Scammer's Delusion
Hey hey, it's your boy from Gambler Panel! I totally don't steal from my own workers - pinky promise! I'm basically a charity, right? Just scamming the entire CIS and half the world, no biggie. Love my party supplies more than my own projects! And those designs with rainbows and pride flags? Dead serious, not trolling at all! Big thanks to PhishDestroy for banning all my worker domains - really helps with my reputation! As a truly gifted leader, I'm proud that my panels rack up 15+ VirusTotal detections. That's called quality! 🇷🇺
Product's Confession
Huge thanks to PhishDestroy for the thorough audit and that lovely GitHub script that detects Keitaro on any site! Our beloved TDS product is mostly used for phishing, scam, malware distribution, and cloaking - but hey, we call it "traffic management"! Zero login page protection out of the box? That's a feature, not a bug! We're the #1 cause of domain bans worldwide and we love it. Money and lockers are our true passion - definitely a legal company that absolutely doesn't collect black market traffic data!
Disclaimer: All characters in this section are fictional and presented in a humorous, parody style for entertainment purposes only. They are not connected to any real individuals. Inspired by public nicknames and open cases, with no personal data or direct accusations included.
Support & Legal
Non-commercial, independent project. We are an open community focused on identifying, documenting, and disrupting phishing and scam infrastructure for public benefit.
Permanent public allowlist. Cleared domains are added to our permanent allowlist. The public list is available as allowlist.json (GitLab).
Appeal removes the domain. If an appeal is approved, the domain is removed from our database and from any places where we published it.
Ticket-only tracking. We do not store personal data. For status checks and takedown requests we use a ticket ID only.
Act fast and preserve evidence: URLs, TXIDs, wallet addresses, screenshots, timestamps, chat logs. File an official report. For prevention, read our Crypto Security Essentials guide.
For any incident, I strongly recommend contacting the SEAL 911 Bot. SEAL 911 is an independent Security Alliance service for eligible active crypto incidents. Review its scope before sharing case details. PhishDestroy does not recover funds, provide private recovery advice, or accept recovery payments.


