
Platform totals · all detection dates
All records in the platform database, independent of the month selected below. Statuses describe the latest stored observation, not confirmed takedown attribution. Snapshot: .
How these metrics are calculated
Offline rate = offline ÷ (offline + live): 110,097 ÷ 214,672. The remaining 19,479 records have other or unknown statuses and are excluded from this rate. VT coverage uses all 234,151 detections.
Monthly Intelligence Reports
Expand a month for its chart, status breakdown and summary. Open the full report for domain records and registrar analysis.
November 2026 Month to date · through Nov 8 3,264Detected domains 2.8%Offline at last check
So far in November 2026 (month in progress), PhishDestroy detected 3,238 phishing domains. 90 of them (2.8%) were offline at last check, while 2,968 were still reachable at their last check. The most abused registrar was Dynadot Inc with 548 malicious domains, followed by MarkMonitor Inc. (521). Attackers targeted signal hardest, with celer a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
October 2026 +31.2% vs Sep 19,515Detected domains 9.1%Offline at last check
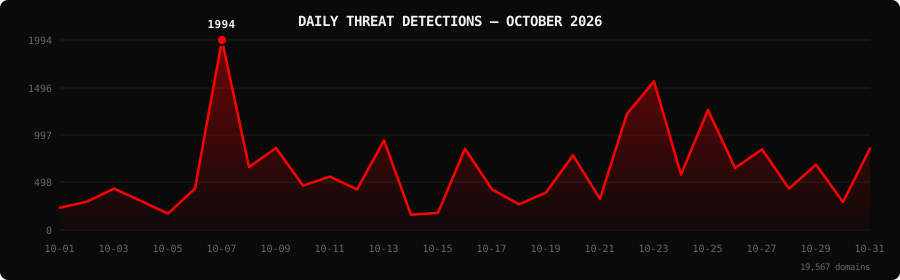
In October 2026, PhishDestroy detected 19,515 phishing domains, a 31.2% increase from September. 1,772 of them (9.1%) were offline at last check, while 16,978 were still reachable at their last check. The most abused registrar was Dynadot Inc. with 5,002 malicious domains, followed by Dynadot Inc (2,307). Attackers targeted MetaMask hardest, with PayPal a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
September 2026 -15% vs Aug 14,869Detected domains 30.6%Offline at last check
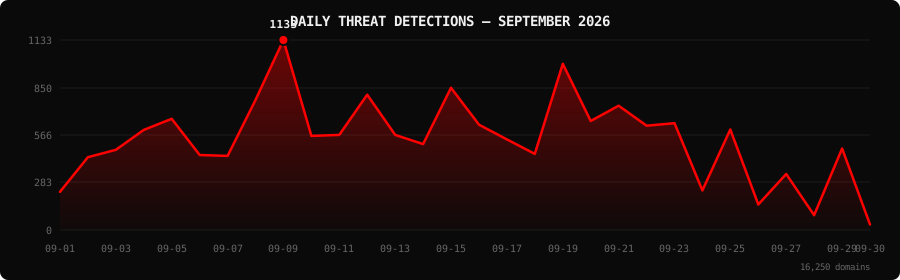
In September 2026, PhishDestroy detected 14,869 phishing domains, a 15% decrease from August. 4,554 of them (30.6%) were offline at last check, while 9,850 were still reachable at their last check. The most abused registrar was Dynadot Inc with 1,196 malicious domains, followed by Dynadot Inc. (1,174). Attackers targeted Unknown hardest, with MetaMask a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
August 2026 -5% vs Jul 17,488Detected domains 40.8%Offline at last check
In August 2026, PhishDestroy detected 17,488 phishing domains, a 5% decrease from July. 7,135 of them (40.8%) were offline at last check, while 9,612 were still reachable at their last check. The most abused registrar was NICENIC INTERNATIONAL GROUP CO., LIMITED with 1,724 malicious domains, followed by Cloudflare Pages (1,054). Attackers targeted Unknown hardest, with MetaMask a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
July 2026 -16% vs Jun 18,418Detected domains 37.7%Offline at last check
In July 2026, PhishDestroy detected 18,418 phishing domains, a 16% decrease from June. 6,940 of them (37.7%) were offline at last check, while 10,519 were still reachable at their last check. The most abused registrar was NICENIC INTERNATIONAL GROUP CO., LIMITED with 2,275 malicious domains, followed by Fewmoretaps OU d/b/a Trustname.com (924). Attackers targeted Unknown hardest, with Google a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
June 2026 +196.9% vs May 21,929Detected domains 40.8%Offline at last check

In June 2026, PhishDestroy detected 21,929 phishing domains, a 196.9% increase from May. 8,944 of them (40.8%) were offline at last check, while 11,574 were still reachable at their last check. The most abused registrar was NICENIC INTERNATIONAL GROUP CO., LIMITED with 3,523 malicious domains, followed by Wix Studio (1,112). Attackers targeted Unknown hardest, with Trezor a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
May 2026 -55.7% vs Apr 7,387Detected domains 49.5%Offline at last check

In May 2026, PhishDestroy detected 7,387 phishing domains, a 55.7% decrease from April. 3,654 of them (49.5%) were offline at last check, while 3,276 were still reachable at their last check. The most abused registrar was NICENIC INTERNATIONAL GROUP CO., LIMITED with 711 malicious domains, followed by Cloudflare, Inc. (644). Attackers targeted Unknown hardest, with Ledger a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
April 2026 -20.3% vs Mar 16,688Detected domains 48.6%Offline at last check

In April 2026, PhishDestroy detected 16,688 phishing domains, a 20.3% decrease from March. 8,118 of them (48.6%) were offline at last check, while 7,504 were still reachable at their last check. The most abused registrar was Cloudflare, Inc. with 4,459 malicious domains, followed by Wix Studio (1,620). Attackers targeted Ledger hardest, with Trezor a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
March 2026 -47.6% vs Feb 20,935Detected domains 49.8%Offline at last check

In March 2026, PhishDestroy detected 20,935 phishing domains, a 47.6% decrease from February. 10,428 of them (49.8%) were offline at last check, while 7,016 were still reachable at their last check. The most abused registrar was NICENIC INTERNATIONAL GROUP CO., LIMITED with 4,867 malicious domains, followed by CloudFlare, Inc. (4,337). Attackers targeted Unknown hardest, with Ledger a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
February 2026 +348.9% vs Jan 39,927Detected domains 61.1%Offline at last check

In February 2026, PhishDestroy detected 39,927 phishing domains, a 348.9% increase from January. 24,388 of them (61.1%) were offline at last check, while 10,575 were still reachable at their last check. The most abused registrar was NiceNIC International Group Co., Limited with 8,814 malicious domains, followed by Cloudflare, Inc. (6,190). Attackers targeted Unknown hardest, with Coinbase a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
January 2026 -23.6% vs Dec 8,894Detected domains 63.7%Offline at last check

In January 2026, PhishDestroy detected 8,894 phishing domains, a 23.6% decrease from December. 5,664 of them (63.7%) were offline at last check, while 2,380 were still reachable at their last check. The most abused registrar was NiceNIC International Group Co., Limited with 1,320 malicious domains, followed by PDR Ltd. d/b/a PublicDomainRegistry.com (974). Attackers targeted Unknown hardest, with Binance a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
December 2025 -6.7% vs Nov 11,646Detected domains 57.2%Offline at last check

In December 2025, PhishDestroy detected 11,646 phishing domains, a 6.7% decrease from November. 6,666 of them (57.2%) were offline at last check, while 4,155 were still reachable at their last check. The most abused registrar was NiceNIC International Group Co., Limited with 1,284 malicious domains, followed by Cloudflare, Inc. (1,145). Attackers targeted Unknown hardest, with coinbase a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
November 2025 +42% vs Oct 12,482Detected domains 66.8%Offline at last check

In November 2025, PhishDestroy detected 12,482 phishing domains, a 42% increase from October. 8,338 of them (66.8%) were offline at last check, while 3,223 were still reachable at their last check. The most abused registrar was Dynadot LLC with 2,109 malicious domains, followed by Cloudflare, Inc. (1,498). Attackers targeted Google hardest, with Unknown a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
October 2025 +21.2% vs Sep 8,793Detected domains 58.1%Offline at last check

In October 2025, PhishDestroy detected 8,793 phishing domains, a 21.2% increase from September. 5,110 of them (58.1%) were offline at last check, while 2,577 were still reachable at their last check. The most abused registrar was NiceNIC International Group Co., Limited with 1,206 malicious domains, followed by Cloudflare, Inc. (827). Attackers targeted Unknown hardest, with Google a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
September 2025 +92.8% vs Aug 7,253Detected domains 68.4%Offline at last check

In September 2025, PhishDestroy detected 7,253 phishing domains, a 92.8% increase from August. 4,962 of them (68.4%) were offline at last check, while 1,584 were still reachable at their last check. The most abused registrar was NiceNIC International Group Co., Limited with 779 malicious domains, followed by Web Commerce Communications Limited (677). Attackers targeted Unknown hardest, with SushiSwap a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
August 2025 +442.9% vs Jul 3,762Detected domains 69.4%Offline at last check

In August 2025, PhishDestroy detected 3,762 phishing domains, a 442.9% increase from July. 2,611 of them (69.4%) were offline at last check, while 970 were still reachable at their last check. The most abused registrar was Web Commerce Communications Limited with 276 malicious domains, followed by NameSilo, LLC (253). Attackers targeted Unknown hardest, with Ethereum a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
July 2025 +23000% vs Jun 693Detected domains 77.9%Offline at last check

In July 2025, PhishDestroy detected 693 phishing domains, a 23000% increase from June. 540 of them (77.9%) were offline at last check, while 114 were still reachable at their last check. The most abused registrar was Web Commerce Communications Limited with 84 malicious domains, followed by NameSilo, LLC (78). Attackers targeted Unknown hardest, with ethereum a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
June 2025 3Detected domains 100%Offline at last check

In June 2025, PhishDestroy detected 3 phishing domains. 3 of them (100%) were offline at last check. The most abused registrar was NameSilo, LLC with 1 malicious domains, followed by Web Commerce Communications Ltd. (1). Attackers targeted chainlink hardest, with amazon a close second.
Summary written from the data snapshot of Nov 8, 2026 03:40 UTC. Counts on the card are live and can differ slightly from this text.
Detection Trends
Monthly domain volume, offline rate, and live threats over time.
Monthly Detected Domains
Offline rate %
Data table: detected domains and offline rate per month
| Month | Detected domains | Offline rate |
|---|---|---|
| Jun 25 | 3 | 100% |
| Jul 25 | 693 | 77.9% |
| Aug 25 | 3,762 | 69.4% |
| Sep 25 | 7,253 | 68.4% |
| Oct 25 | 8,793 | 58.1% |
| Nov 25 | 12,482 | 66.8% |
| Dec 25 | 11,646 | 57.2% |
| Jan 26 | 8,894 | 63.7% |
| Feb 26 | 39,927 | 61.1% |
| Mar 26 | 20,935 | 49.8% |
| Apr 26 | 16,688 | 48.6% |
| May 26 | 7,387 | 49.5% |
| Jun 26 | 21,929 | 40.8% |
| Jul 26 | 18,418 | 37.7% |
| Aug 26 | 17,488 | 40.8% |
| Sep 26 | 14,869 | 30.6% |
| Oct 26 | 19,515 | 9.1% |
| Nov 26 | 3,264 | 2.8% |
Explore More
Related intelligence pages and data feeds.