trustwallets.digital is a phishing domain built to impersonate TrustWallet. It targets people who hold or manage crypto in that wallet and might mistake the pluralized name for the real brand. PhishDestroy first flagged it on 2026-09-09. The site has been offline since 2026-09-11, and when last checked on 2026-10-19 its DNS was no longer resolving.
诈骗手法解析
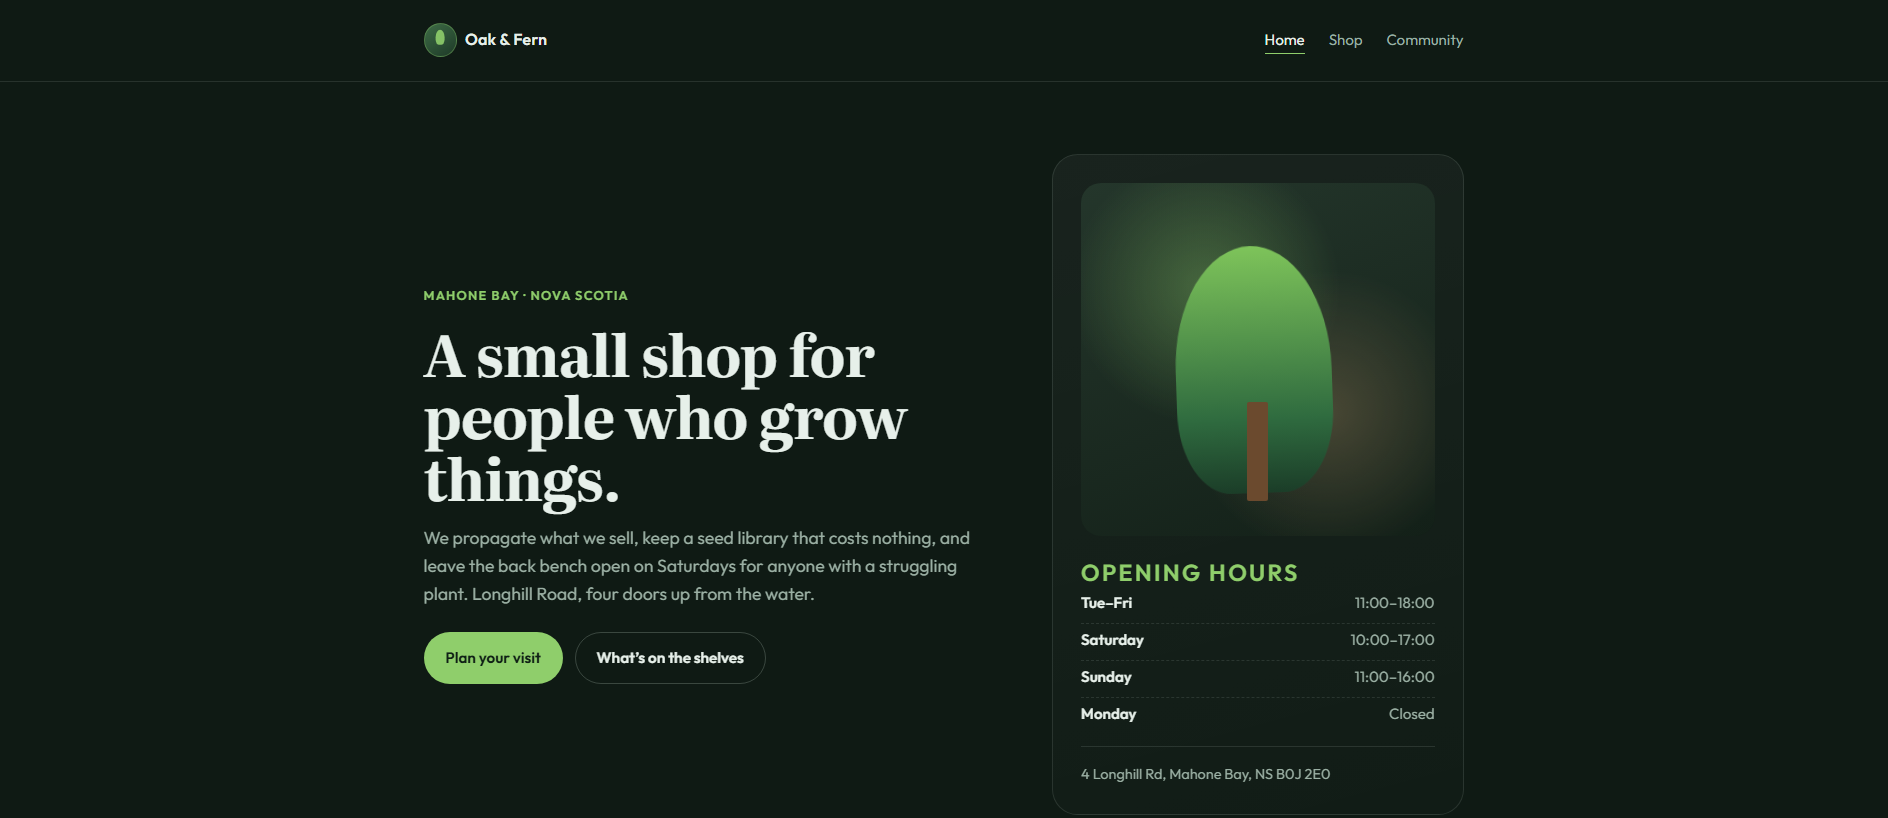
Wallet impersonation pages copy the look and wording of the real brand, then push visitors to type in their recovery phrase or private key under a pretext such as wallet validation, syncing or restoring access. Some instead prompt the visitor to connect a wallet and sign a request. A stolen recovery phrase hands the attacker full control of every asset in that wallet, and a malicious signature can authorize transfers. The page title read "Oak & Fern — Plant Shop & Growing Community, Mahone Bay," while we classified the domain as TrustWallet impersonation phishing.
证据
Six of 89 VirusTotal engines flagged the domain on 2026-09-09: alphaMountain.ai, BitDefender, ESET, Fortinet, G-Data and Kaspersky. That count is modest, but these vendors work independently, and all of them reached a verdict within a day of registration. MetaMask and SEAL list the domain alongside PhishDestroy, and Spamhaus places it in its DBL under the phishing category. Four AlienVault OTX pulses also reference it.
基础设施
The domain was registered on 2026-09-08, one day before PhishDestroy detected it, and it went dark two days after that. A lifespan that short fits a disposable domain registered for a single campaign. It was registered through Atak Domain Bilgi Teknolojileri A.Ş. and served from Cloudflare's network in the US, which hides the origin server behind a shared proxy.
What to do
If you entered a recovery phrase or private key on this site, treat that wallet as compromised. Create a new wallet with a fresh phrase on a trusted device and move any remaining funds to it immediately. If you connected a wallet or signed anything, review and revoke token approvals granted around that time. Only ever install TrustWallet from official app stores, and remember that no genuine wallet service will ask for your recovery phrase. Defenders should block the domain and lookalike variants of the TrustWallet name, and check DNS and proxy logs for any visits between 2026-09-08 and 2026-09-11.
trustwallets.digital is an impersonation phishing page posing as TrustWallet, aimed at crypto wallet users looking for the official TrustWallet site.
AI摘要
Overview trustwallets.digital is a phishing domain built to impersonate TrustWallet. It targets people who hold or manage crypto in that wallet and might mistake the pluralized name for the real brand. PhishDestroy first flagged it on 2026-09-09. The site has been offline since 2026-09-11, and when last checked on 2026-10-19 its DNS was no longer resolving. How the scam works Wallet impersonation pages copy the look and wording of the real brand, then push visitors to type in their recovery phrase or private key under a pretext such as wallet validation, syncing or restoring access. Some instead prompt the visitor to connect a wallet and sign a request. A stolen recovery phrase hands the attacker full control of every asset in that wallet, and a malicious signature can authorize transfers. The page title read "Oak & Fern — Plant Shop & Growing Community, Mahone Bay," while we classified the domain as TrustWallet impersonation phishing. Evidence Six of 89 VirusTotal engines flagged the domain on 2026-09-09: alphaMountain.ai, BitDefender, ESET, Fortinet, G-Data and Kaspersky. That count is modest, but these vendors work independently, and all of them reached a verdict within a day of registration. MetaMask and SEAL list the domain alongside PhishDestroy, and Spamhaus places it in its DBL under the phishing category. Four AlienVault OTX pulses also reference it. Infrastructure The domain was registered on 2026-09-08, one day before PhishDestroy detected it, and it went dark two days after that. A lifespan that short fits a disposable domain registered for a single campaign. It was registered through Atak Domain Bilgi Teknolojileri A.Ş. and served from Cloudflare's network in the US, which hides the origin server behind a shared proxy. What to do If you entered a recovery phrase or private key on this site, treat that wallet as compromised. Create a new wallet with a fresh phrase on a trusted device and move any remaining funds to it immediately. If you connected a wallet or signed anything, review and revoke token approvals granted around that time. Only ever install TrustWallet from official app stores, and remember that no genuine wallet service will ask for your recovery phrase. Defenders should block the domain and lookalike variants of the TrustWallet name, and check DNS and proxy logs for any visits between 2026-09-08 and 2026-09-11. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a08558-7e58-73a4-93d6-0c2419c47dac/ VirusTotal report: https://www.virustotal.com/gui/domain/trustwallets.digital Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=trustwallets.digital Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
证据层Availability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP注册
观测时间线last reachable: 2026-09-09 08:47 UTCcurrent episode first observed: 2026-09-30 16:14 UTCobserved RIP window: 2026-09-09 08:47 UTC → 2026-09-30 16:14 UTC · 511.47hmidpoint estimate ≈ 2026-09-20 00:30 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 172.67.189.99


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT