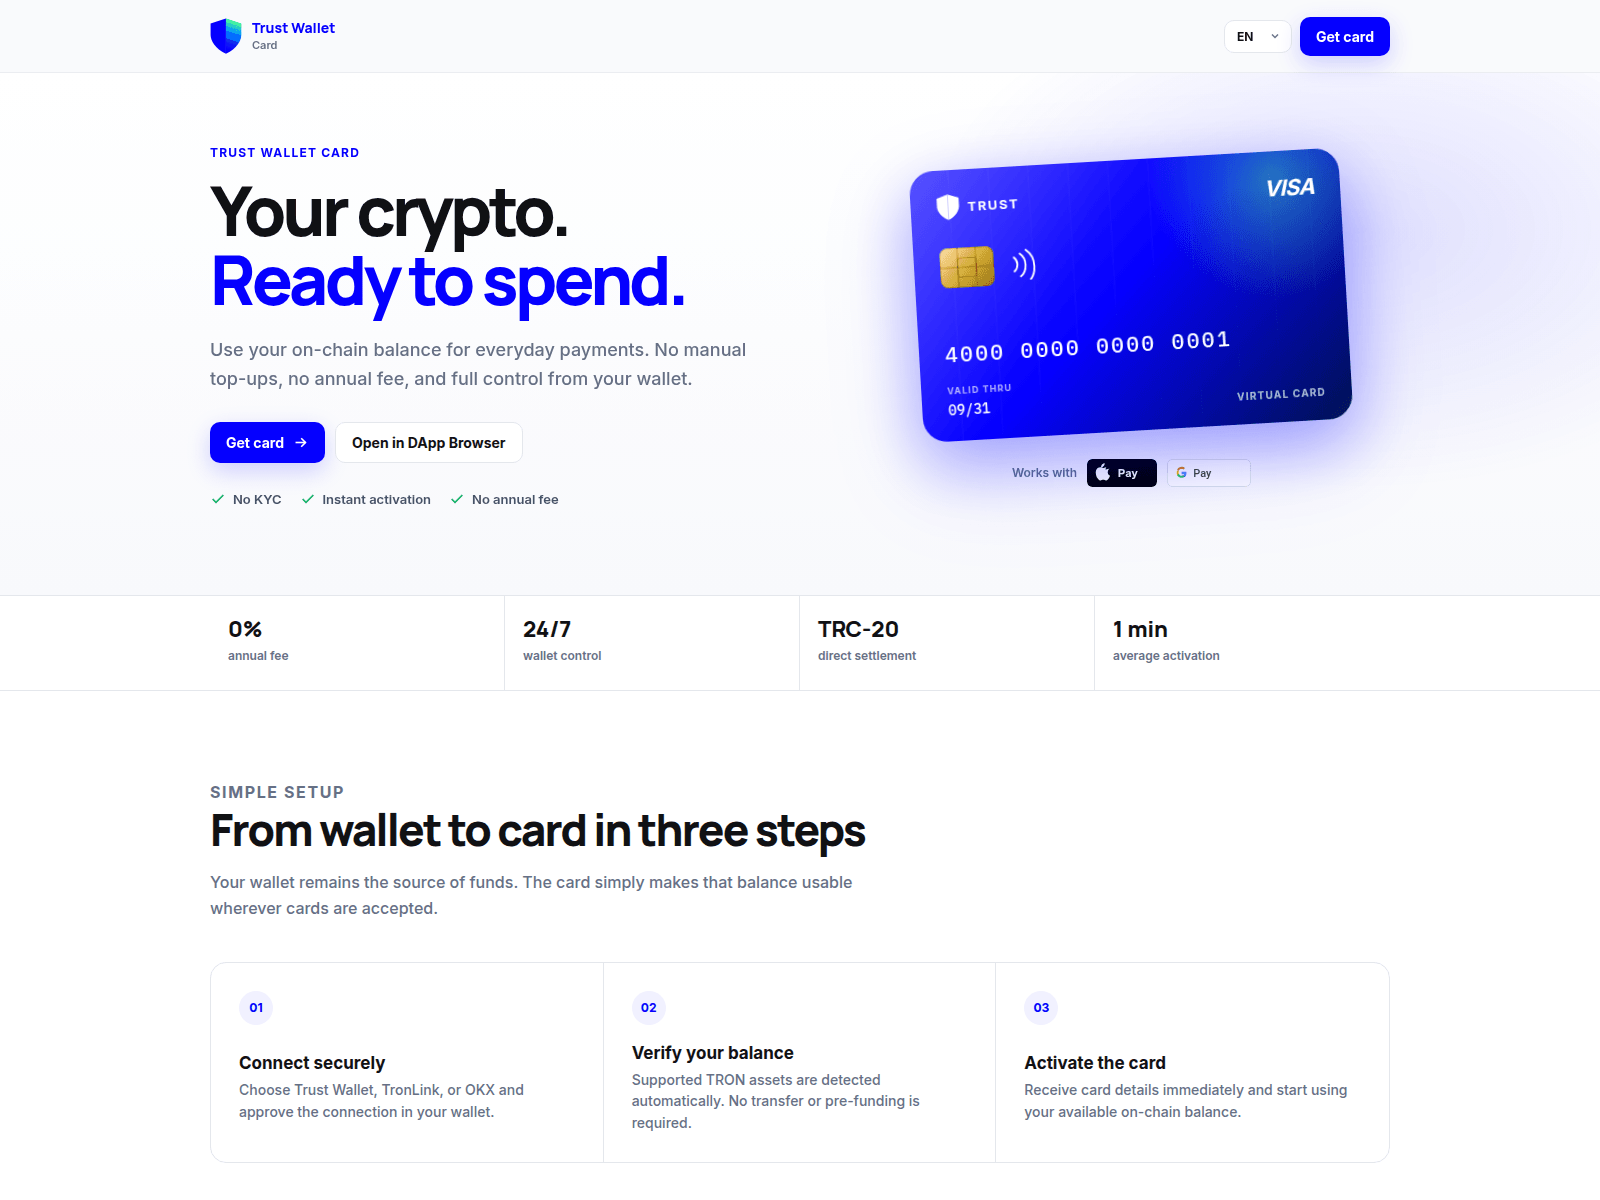
The calemonk.com page presents a promotional setup for a crypto debit card, featuring Trust Wallet branding and asking users to connect Web3 wallets. Anyone who already connected a wallet or approved token spending should immediately revoke permissions via a block explorer.
URLScan截图 · 2026-11-20 20:31 UTC · SHA-256 28df1206…a653d61
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Trust wallet crypto card setup page layout
The calemonk.com page opens with a clean, modern interface mimicking a crypto debit card service, featuring a prominent logo and heading that reads "Your crypto. Ready to spend." It displays a graphic of a blue virtual Visa card labeled "TRUST" alongside bullet points promising "No KYC", "Instant activation", and "No annual fee". Below the main banner, statistics highlight features like "0% annual fee", "24/7 wallet control", "TRC-20 direct settlement", and "1 min average activation". A section titled "Simple setup" outlines a three-step process: "Connect securely" by choosing Trust Wallet, TronLink, or OKX, "Verify your balance" automatically, and "Activate the card". Action buttons include "Get card" and "Open in DApp Browser", prompting visitors to initiate a wallet connection.
Domain timeline and independent security telemetry
The underlying timing of the infrastructure provides crucial context for evaluation, because it was registered on 19 Nov 2026, 1 day before it was first reported. Furthermore, 1 of 92 engines on VirusTotal flagged it on 20 Nov 2026, and MetaMask and SEAL block it, with Fortinet classifying the endpoint as spam and specialized Web3 filters flagging the route. PhishDestroy scores the evidence against it at 50/100 (high).
Risks of connecting a Web3 wallet
When a page invites users to connect external wallets like Trust Wallet, TronLink, or OKX to activate a service, proceeding can expose token balances to malicious smart contract approvals. Always verify card offers directly through official platforms rather than unverified promotional domains.
calemonk.com presents a Trust Wallet crypto card setup page asking visitors to connect a wallet, flagged by 1 VirusTotal engine; avoid entering credentials.
AI摘要
Trust wallet crypto card setup page layout The calemonk.com page opens with a clean, modern interface mimicking a crypto debit card service, featuring a prominent logo and heading that reads "Your crypto. Ready to spend." It displays a graphic of a blue virtual Visa card labeled "TRUST" alongside bullet points promising "No KYC", "Instant activation", and "No annual fee". Below the main banner, statistics highlight features like "0% annual fee", "24/7 wallet control", "TRC-20 direct settlement", and "1 min average activation". A section titled "Simple setup" outlines a three-step process: "Connect securely" by choosing Trust Wallet, TronLink, or OKX, "Verify your balance" automatically, and "Activate the card". Action buttons include "Get card" and "Open in DApp Browser", prompting visitors to initiate a wallet connection. Domain timeline and independent security telemetry The underlying timing of the infrastructure provides crucial context for evaluation, because it was registered on 19 Nov 2026, 1 day before it was first reported. Furthermore, 1 of 92 engines on VirusTotal flagged it on 20 Nov 2026, and MetaMask and SEAL block it, with Fortinet classifying the endpoint as spam and specialized Web3 filters flagging the route. PhishDestroy scores the evidence against it at 50/100 (high). Risks of connecting a Web3 wallet When a page invites users to connect external wallets like Trust Wallet, TronLink, or OKX to activate a service, proceeding can expose token balances to malicious smart contract approvals. Always verify card offers directly through official platforms rather than unverified promotional domains.
证据层Availability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP注册
观测时间线last reachable: 2026-11-21 11:13 UTClast content: 2026-11-21 11:13 UTCcurrent episode first observed: 2026-11-22 06:03 UTCobserved RIP window: 2026-11-21 11:13 UTC → 2026-11-22 06:03 UTC · 18.83hmidpoint estimate ≈ 2026-11-21 20:38 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 Tucows


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT