Зведена інформація про джерела
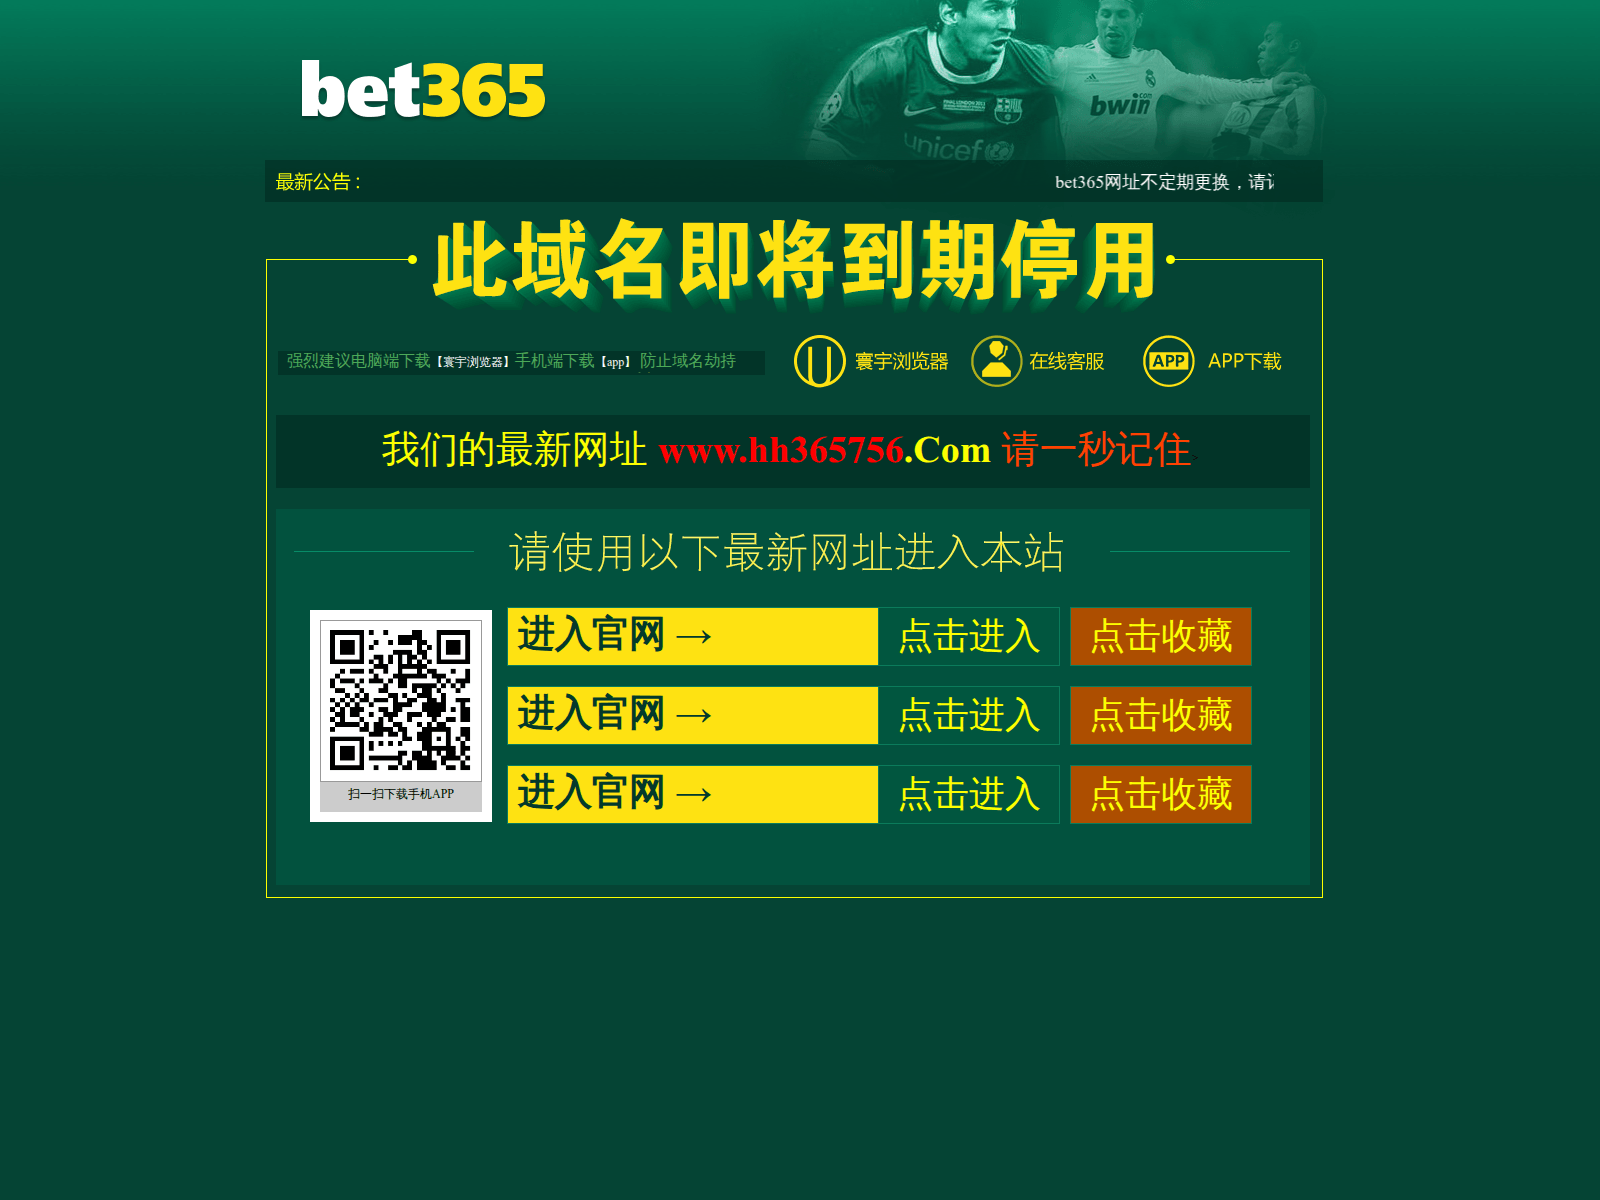
PhishDestroy first observed kk365756.com on Nov 8, 2026. Stored content metadata identifies Bet365 as the apparent target. The captured page title is “bet365最快线路检测中心”. Current evidence score: 90/100 (critical).
Positive findings are stored from 3 sources: VirusTotal, Cloudflare Radar, and URLScan. VirusTotal recorded 6 detections among 92 engines: CRDF, DNS8, SOCRadar, LevelBlue, Gridinsoft, alphaMountain.ai on Nov 7, 2026 at 00:21 UTC. Cloudflare Radar classified the hostname as malicious and assigned the categories phishing and security threats. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to bet365 and assigned phishing as its category on Nov 9, 2026 at 04:30 UTC. Additional recorded evidence: AlienVault OTX listed 1 community pulse reference (not vendor detections) on Nov 21, 2026 at 20:50 UTC.
HTTP 200 was recorded on Nov 22, 2026 at 11:24 UTC. Latest classified outcome: live content observed; cause content served on Nov 22, 2026 at 10:24 UTC. Registration records for the domain list GoDaddy.com, LLC as the registrar and Jan 23, 2026 as the creation date. At collection time, the hostname resolved to 103.255.47.24 on AS133201 (ABCDE GROUP COMPANY LIMITED). The recorded endpoint location is Hong Kong, HK. The stored server header is Microsoft-IIS/10.0. DOM analysis on Nov 8, 2026 at 15:20 UTC returned 0/100; the source detections above were recorded separately. The evidence archive retains 8 visual captures from URLScan and Cloudflare Radar. TLS metadata lists Certum DV TLS G2 R39 CA as the certificate issuer with validity through Apr 4, 2027.
The content indicators and 3 positive source findings support the current Bet365 impersonation and phishing classification. The target field identifies Bet365.

 GoDaddy
 103.255.47.24


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 «Касперський»
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT