
Здійснюйте пошук серед відстежуваних доменів та переглядайте збережені докази, виявлені випадки та останні дані щодо доступності.
220,207
Загальна кількість відстежених
214,485
Виявлено VT
91,989
Останнє підключення: активний
128,218
Недоступний під час останньої перевірки
0
VT — у процесі розгляду
How This Attack Works
Gambler Scam Panels exploit the allure of gambling to deceive users and extract financial information. Here's a breakdown of how these scams typically unfold:
STEP 1
Enticing Offer
Scammers create convincing gambling websites offering attractive bonuses or winnings.
STEP 2
User Engagement
Victims are drawn in by the promise of easy money and create accounts on these fraudulent platforms.
STEP 3
Data Collection
Scammers collect sensitive personal and financial data under the guise of account verification.
STEP 4
Financial Exploitation
Collected data is used for unauthorized transactions, leading to financial loss for the victim.
Technical Analysis
Gambler Scam Panels often utilize spoofed gambling websites that mimic legitimate platforms. Attackers use phishing kits to create replicas of popular gambling sites, embedding malicious scripts that capture user data. These sites are hosted on domains registered with less-regulated registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED, WEBCC, and Dominet (HK) Limited. Additionally, they may leverage obfuscated JavaScript to hide malicious activities from casual inspection. In some cases, these scams involve fake cryptocurrency gambling, where smart contracts are manipulated to always favor the scammer, utilizing functions that are poorly documented and hard to audit.
Real Cases
SpinWin Scam (2024)
$2 million stolen
Users were lured by promises of high returns on a fake cryptocurrency gambling site, resulting in significant financial losses.
QuickBet Fraud (2023)
$1.5 million stolen
This scam used a well-designed imitation of a major gambling platform to collect user data and funds.
LuckyStrike Hoax (2024)
$3 million stolen
A fake lottery site that promised huge winnings but instead harvested sensitive financial information from users.
How to Detect
Unusually high bonuses or winnings promised
Poor website design with multiple typos
Unsecured website (missing HTTPS)
Unusually urgent demands for personal information
Домен registered recently with a non-reputable registrar
How to Protect Yourself
1
Verify the legitimacy of gambling sites before using them
2
Use secure passwords and two-factor authentication
3
Be wary of sites with unsecured connections
4
Regularly monitor financial statements for unauthorized transactions
5
Звіт suspicious sites to authorities and platforms like PhishDestroy
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 10,179 domains tracked for this threat type
Gambler Scam Panel 10,179 domains

wilcardcity-casino-login.com

wildcardcasino-city.com

wildcasino2.com
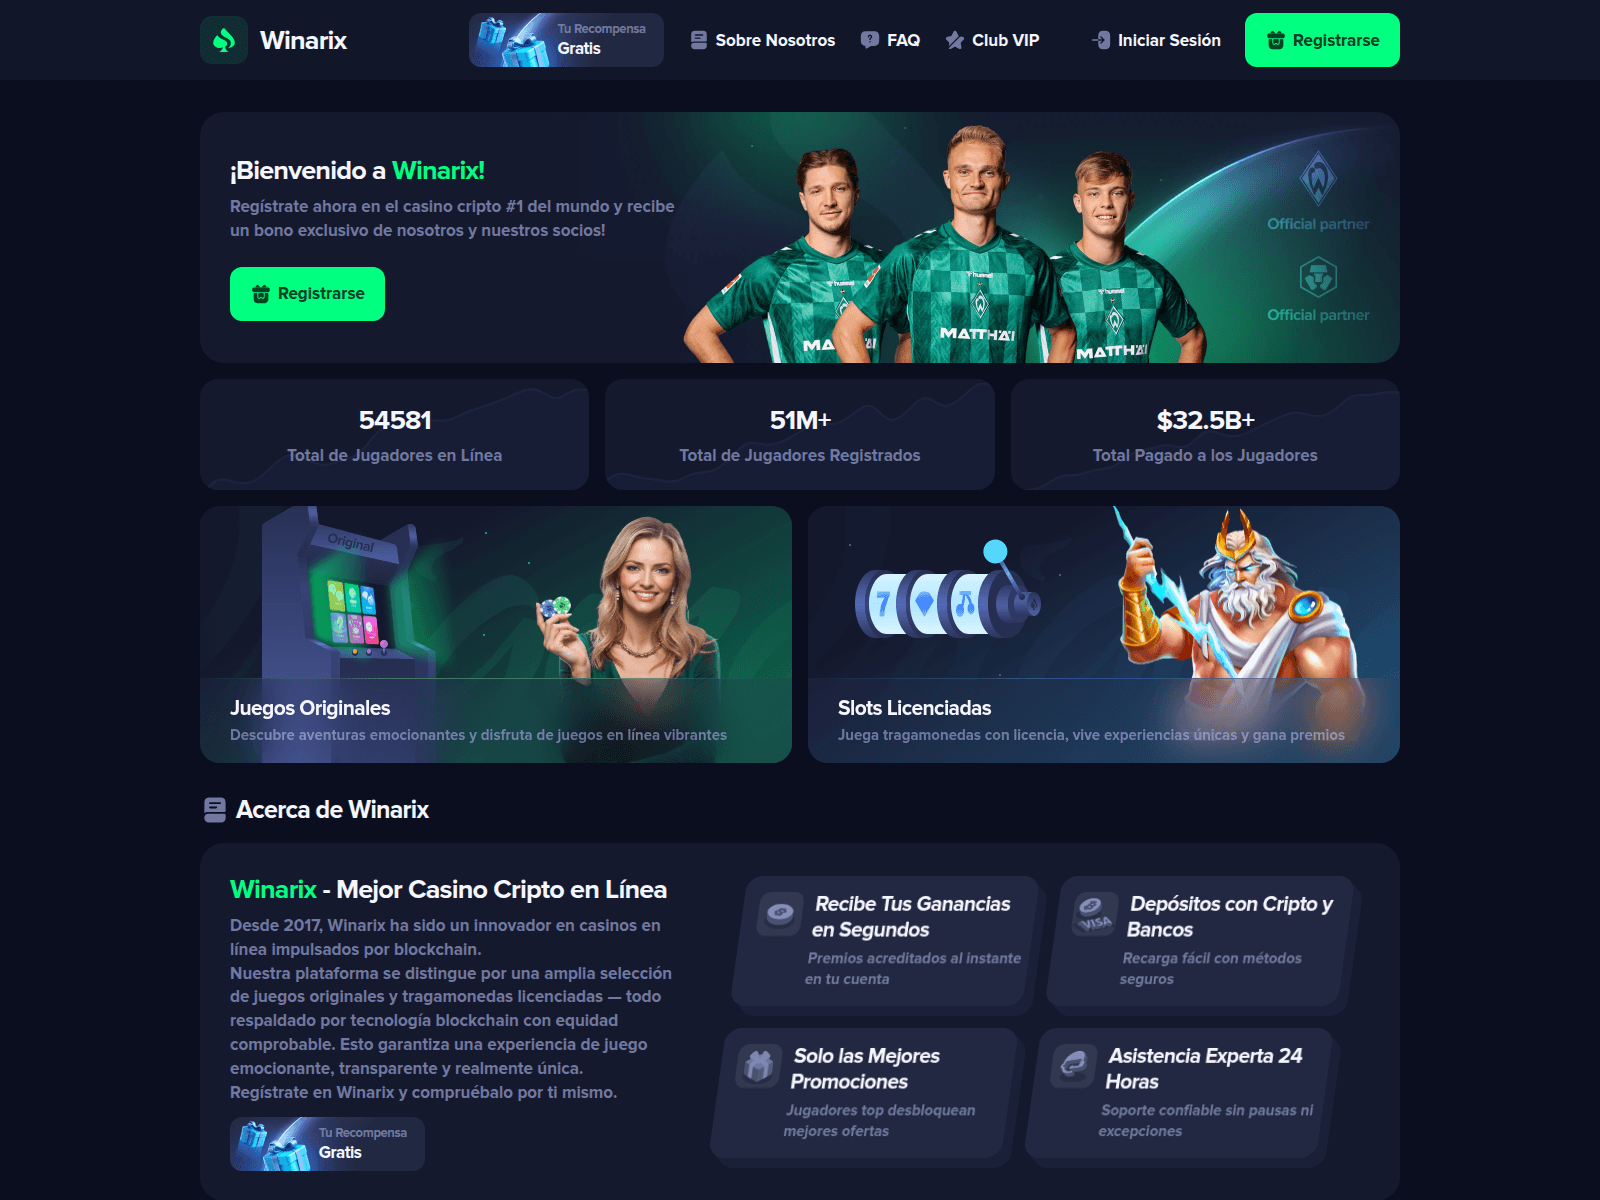
winarix.com
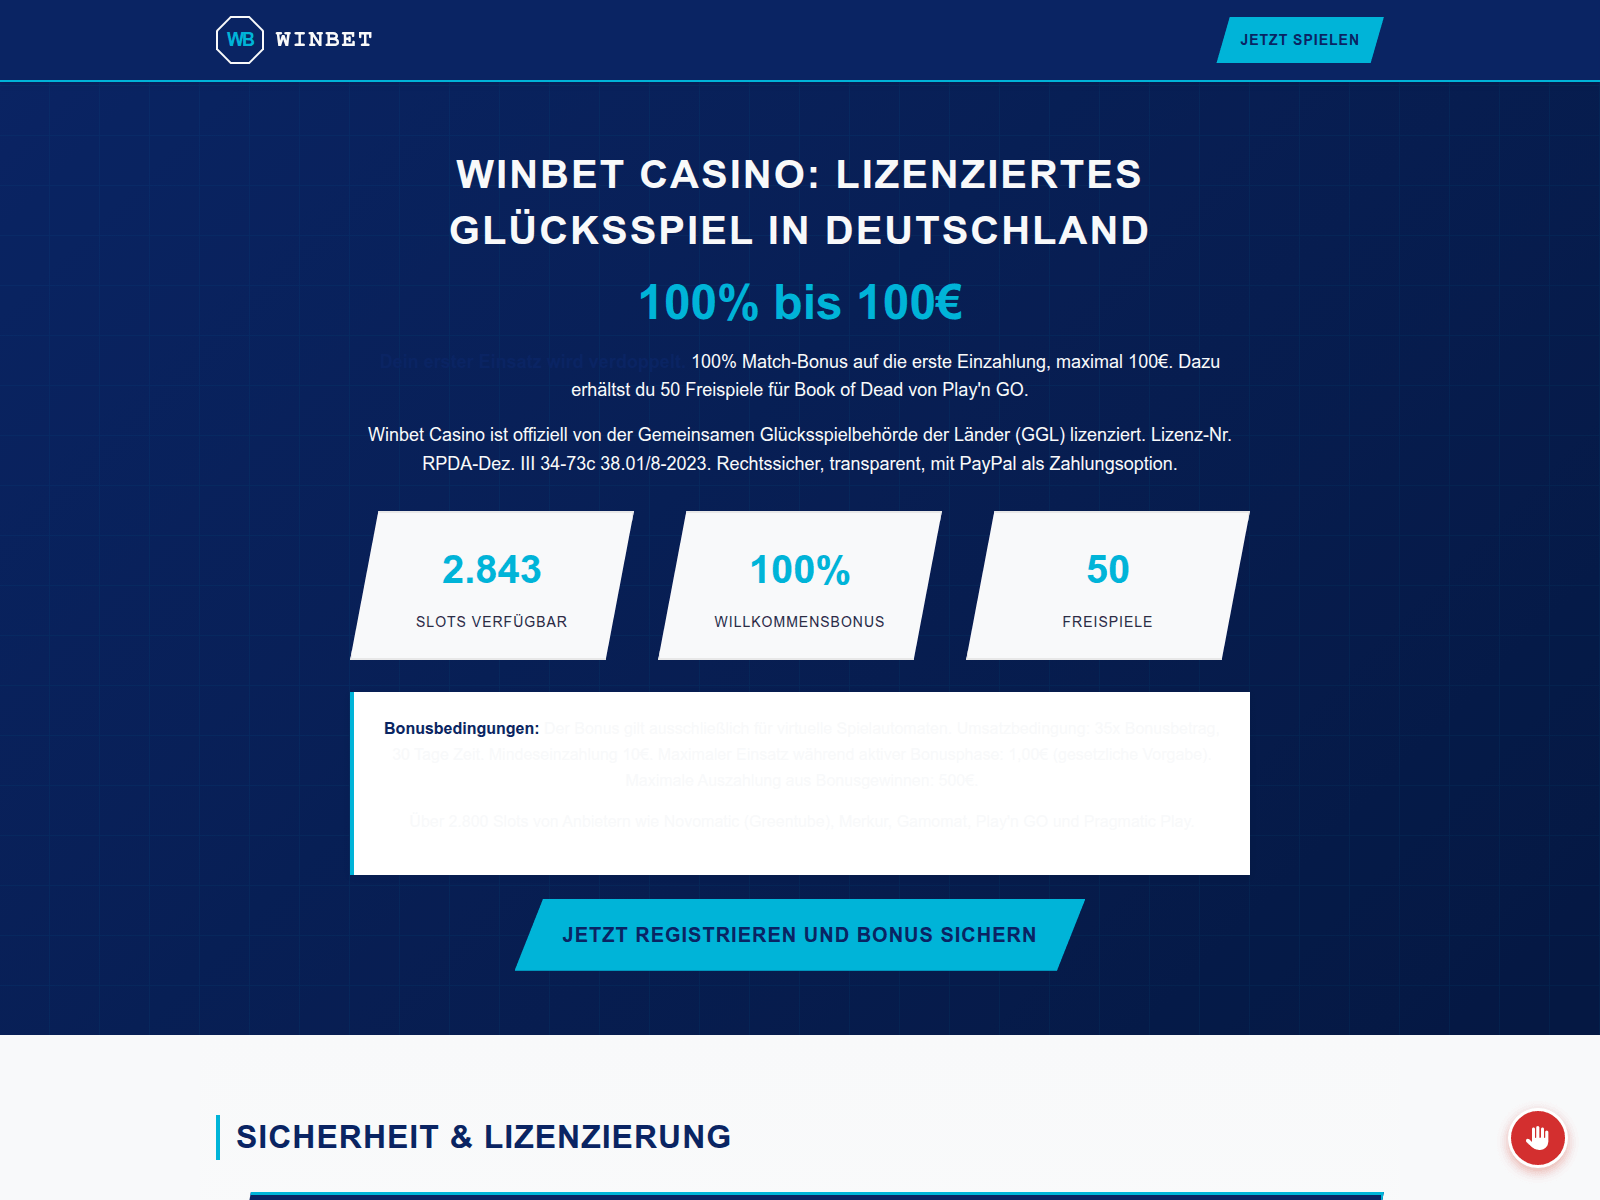
winbet-casino.de
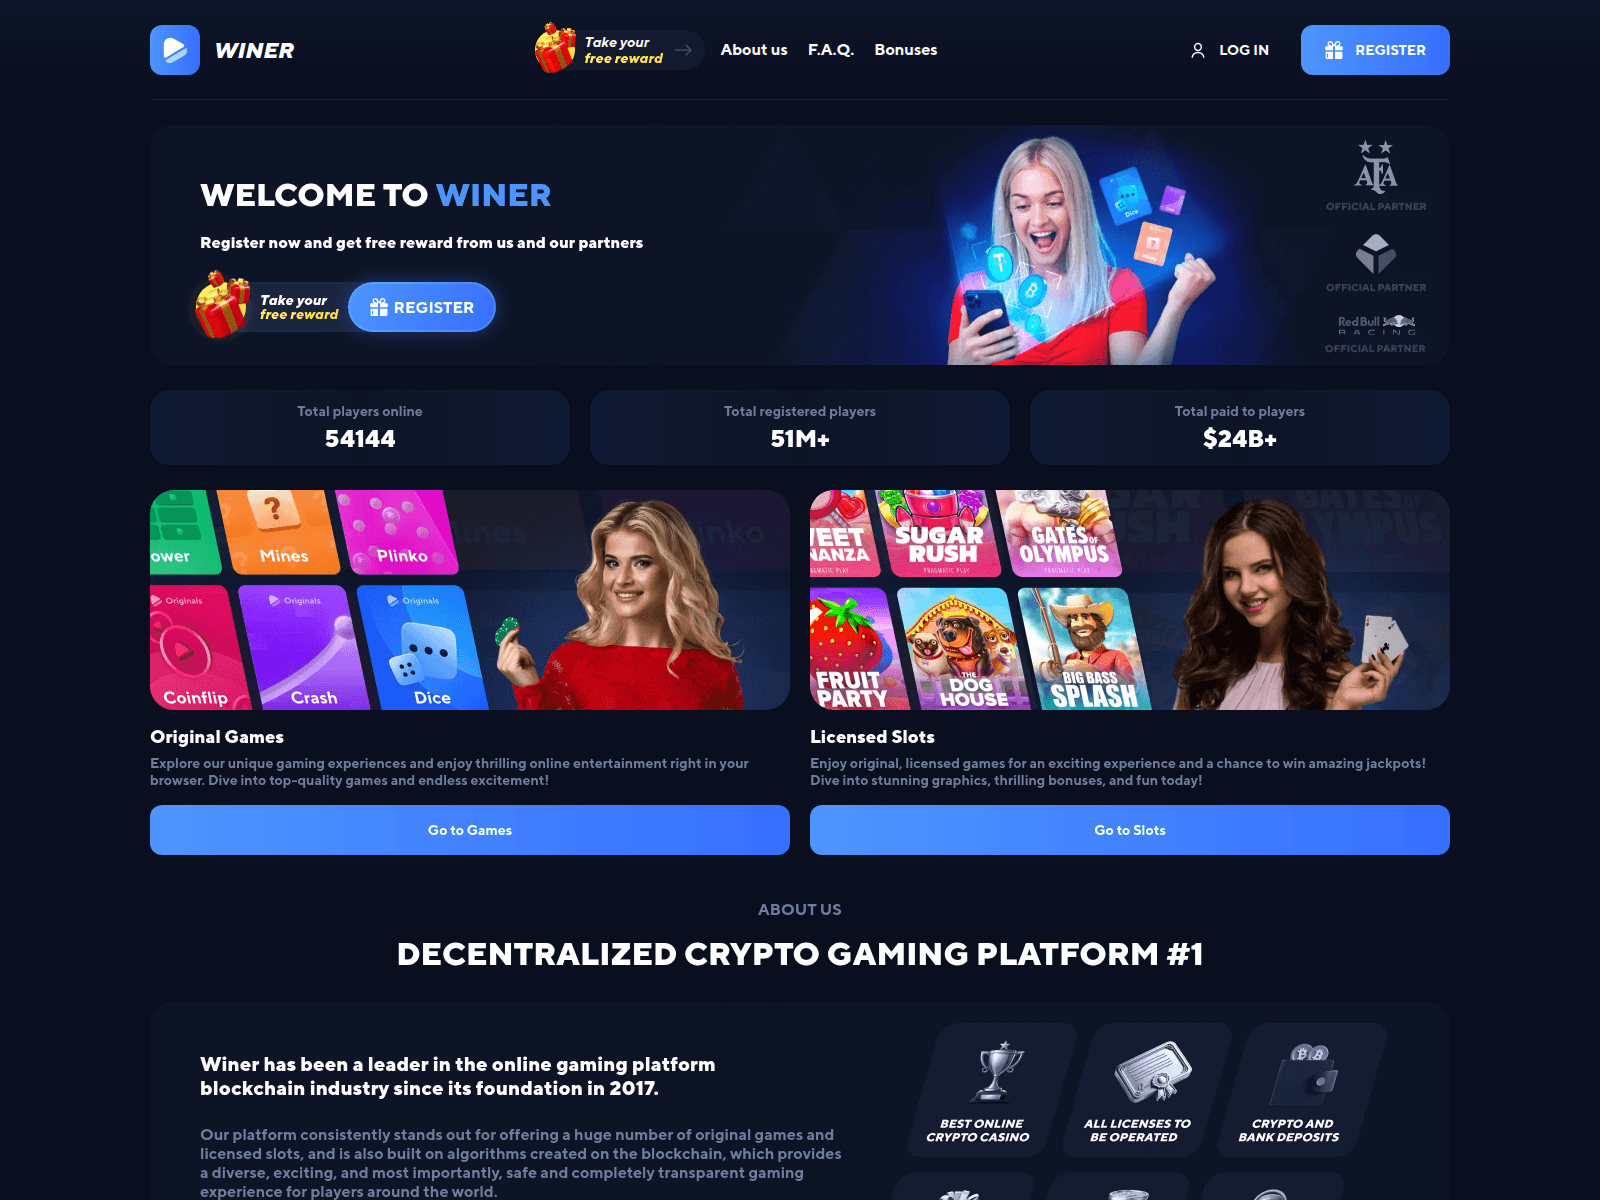
winer.top
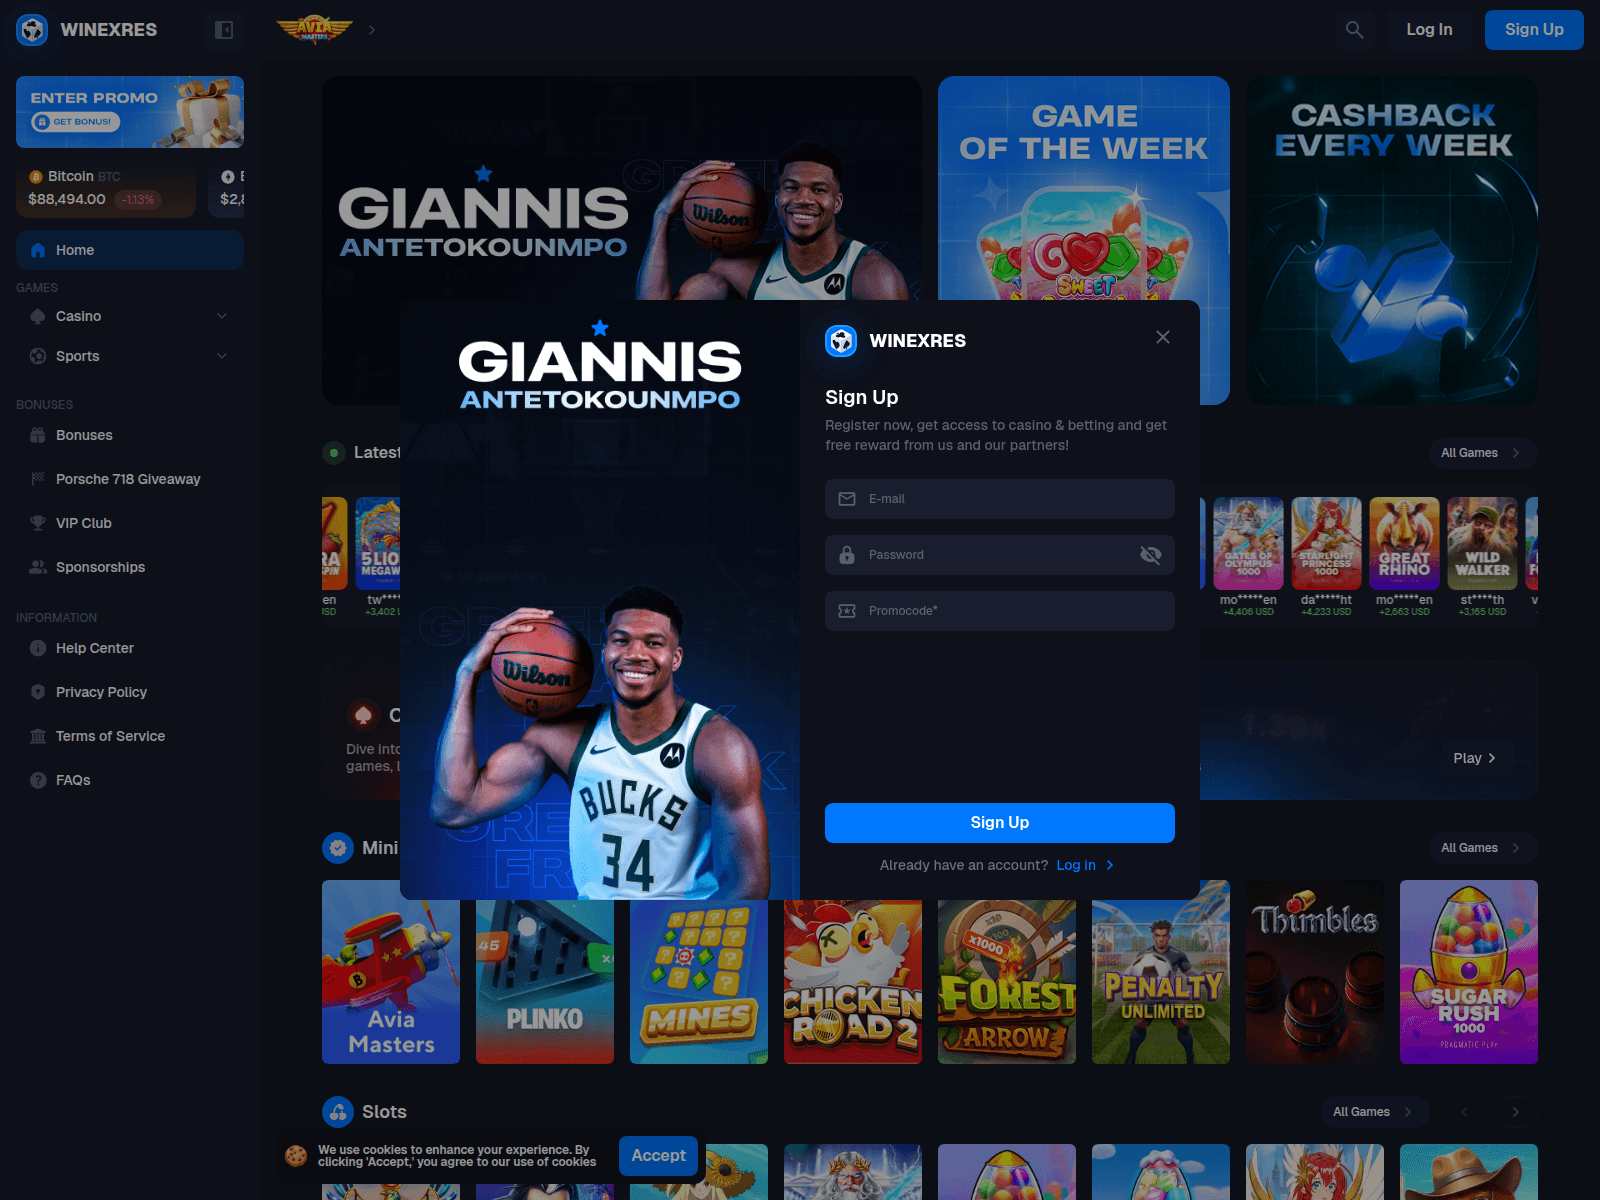
winexres.com
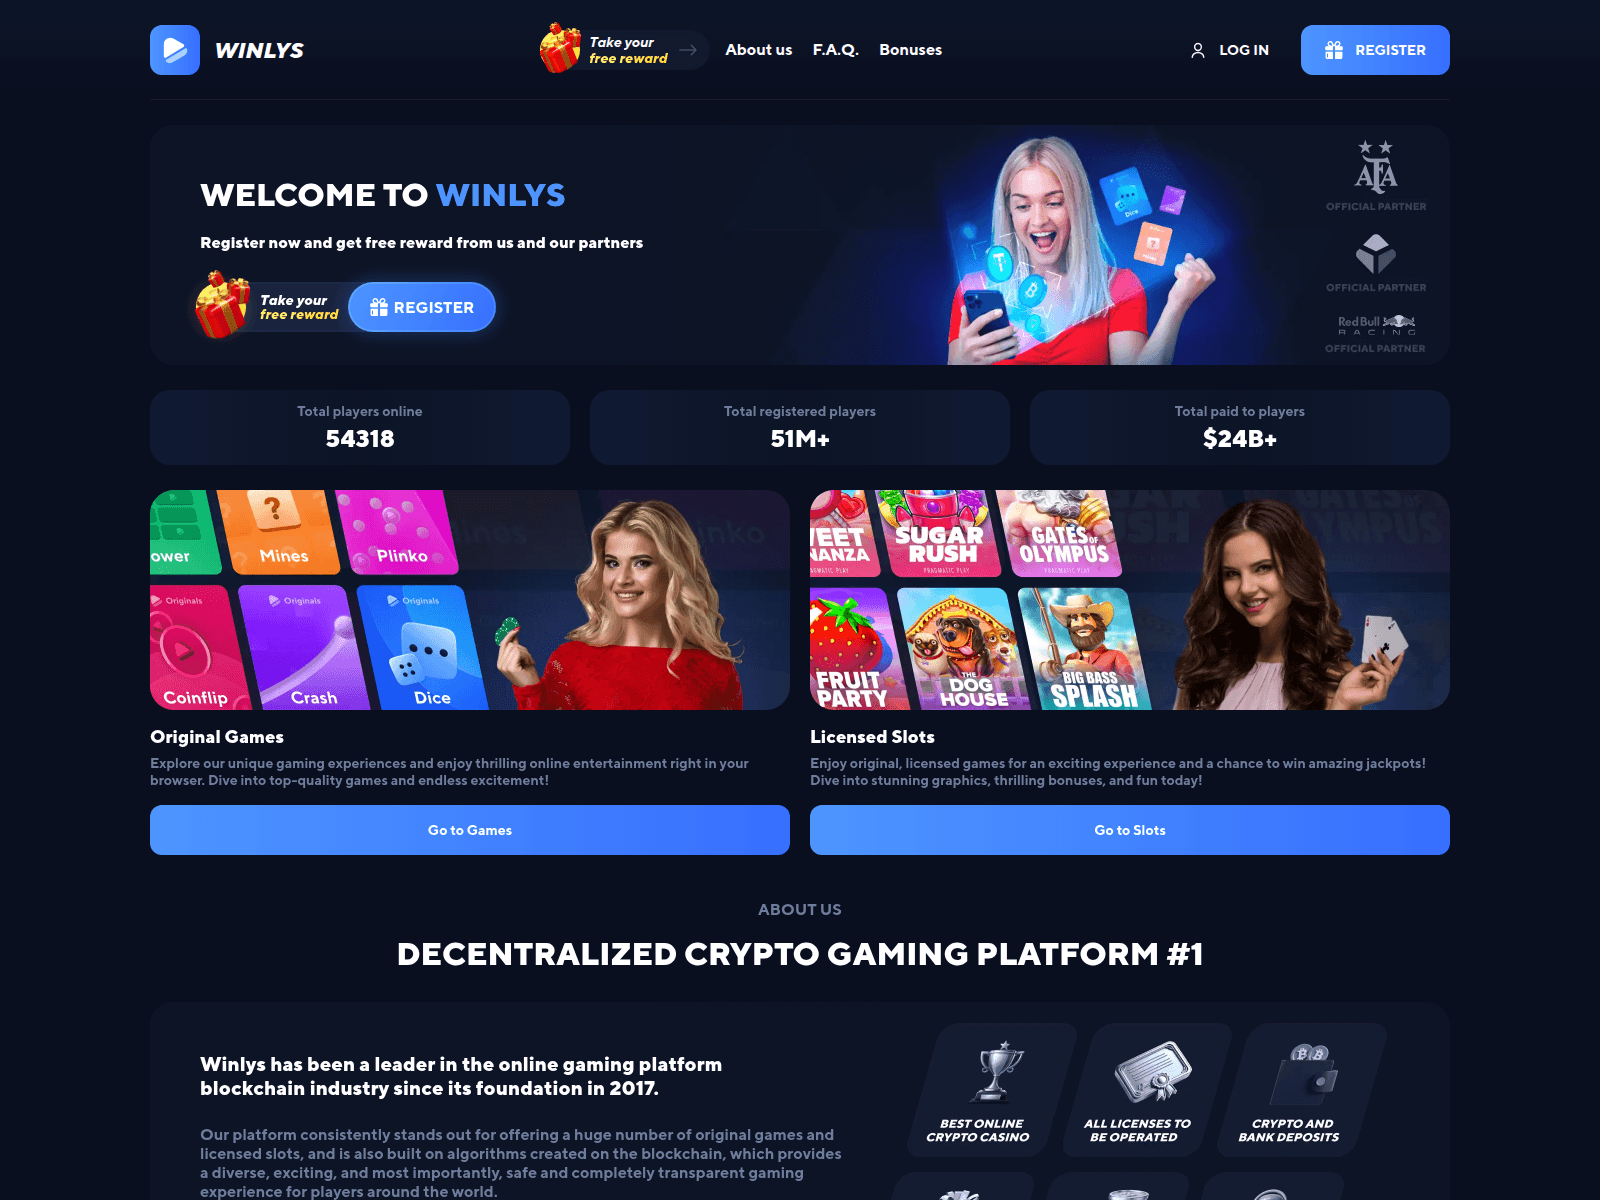
winlys.top

wintesone.com

winto.ink

wise-games.casino
wixboom.com
wonned.bet

xabeto.com
xcoinzo.com
xelucky.com
xgambler.com

xkcas.com

xkentcasino.com
xmaxe.bet

xmoonk.com

xobetx.com
zapepex.com

zayospin.com
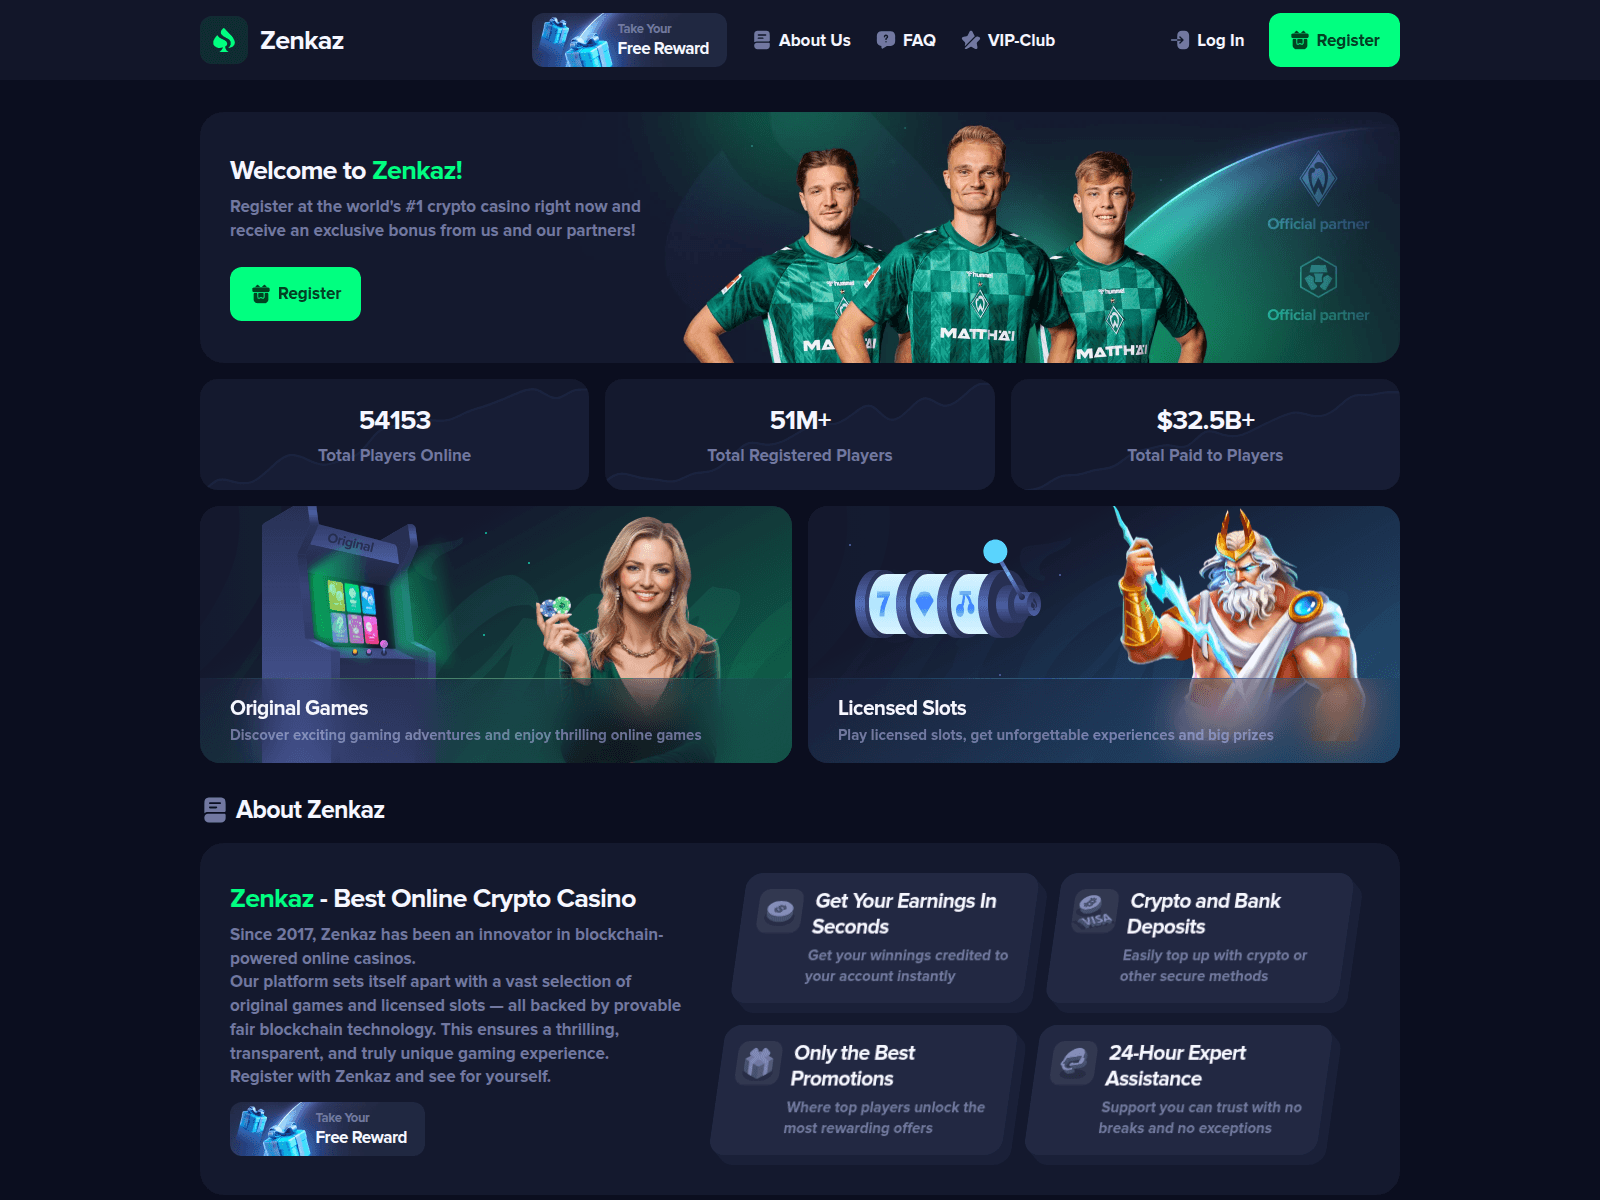
zenkaz.com

zenvado.bet

zipcasino.casino
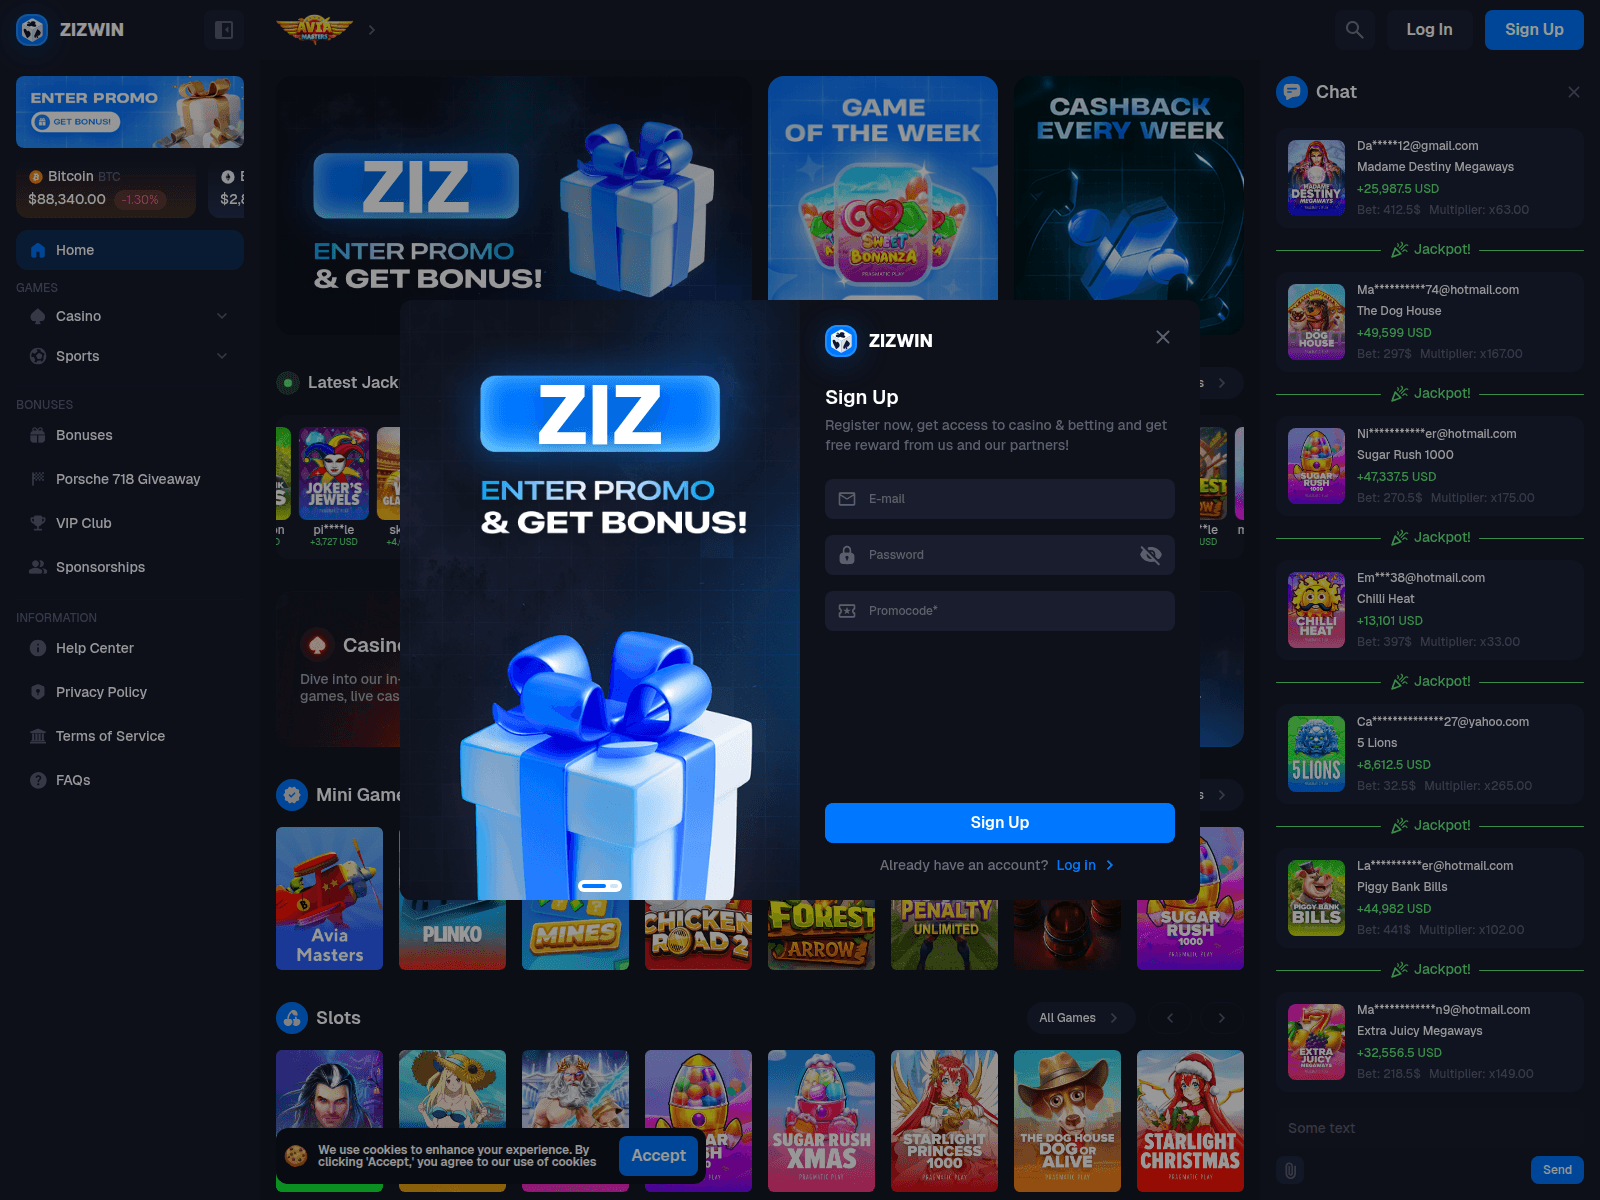
zizwin.com


zynibo.com

1onewinbet.com

ampunjfgaming168.store
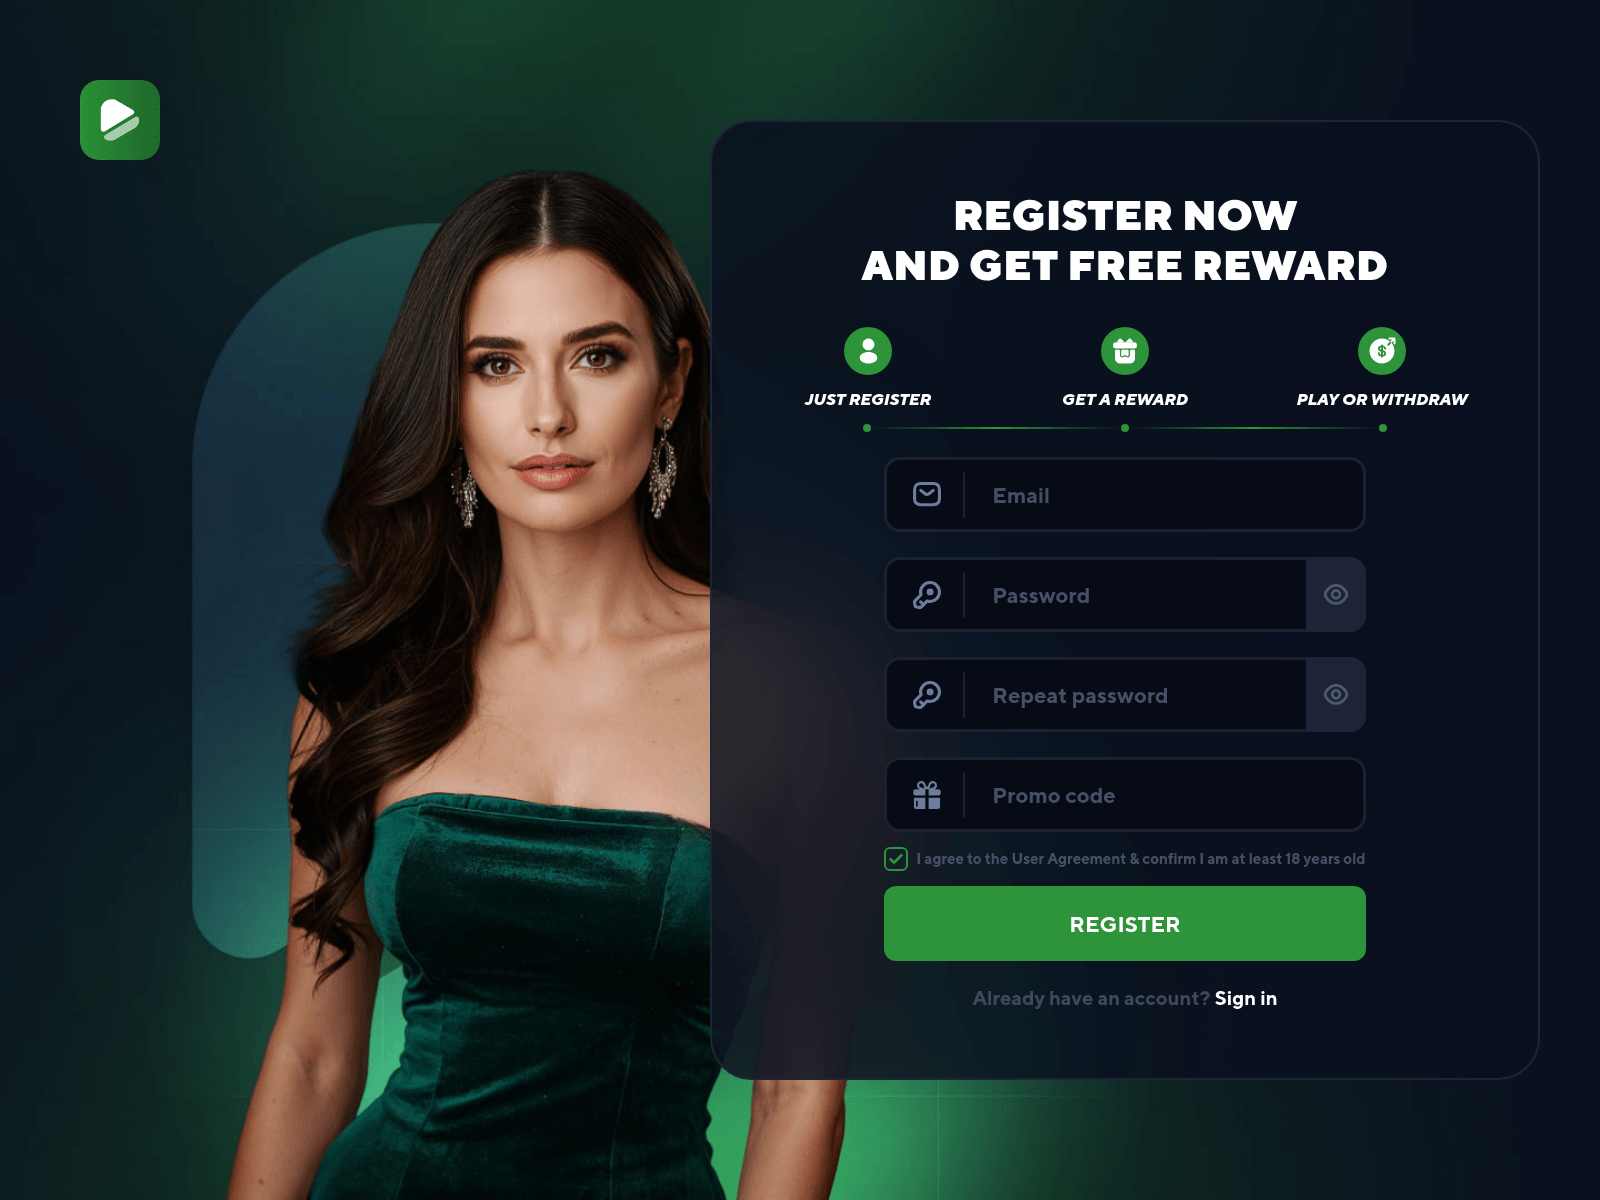
betreex.com

blazino.online

casinowebx.com
caswok.com
centxwin.com

cthulhubet.com
daddyske29.com

dragonbum.com

eblowex.com
excwin.com

feonax.com
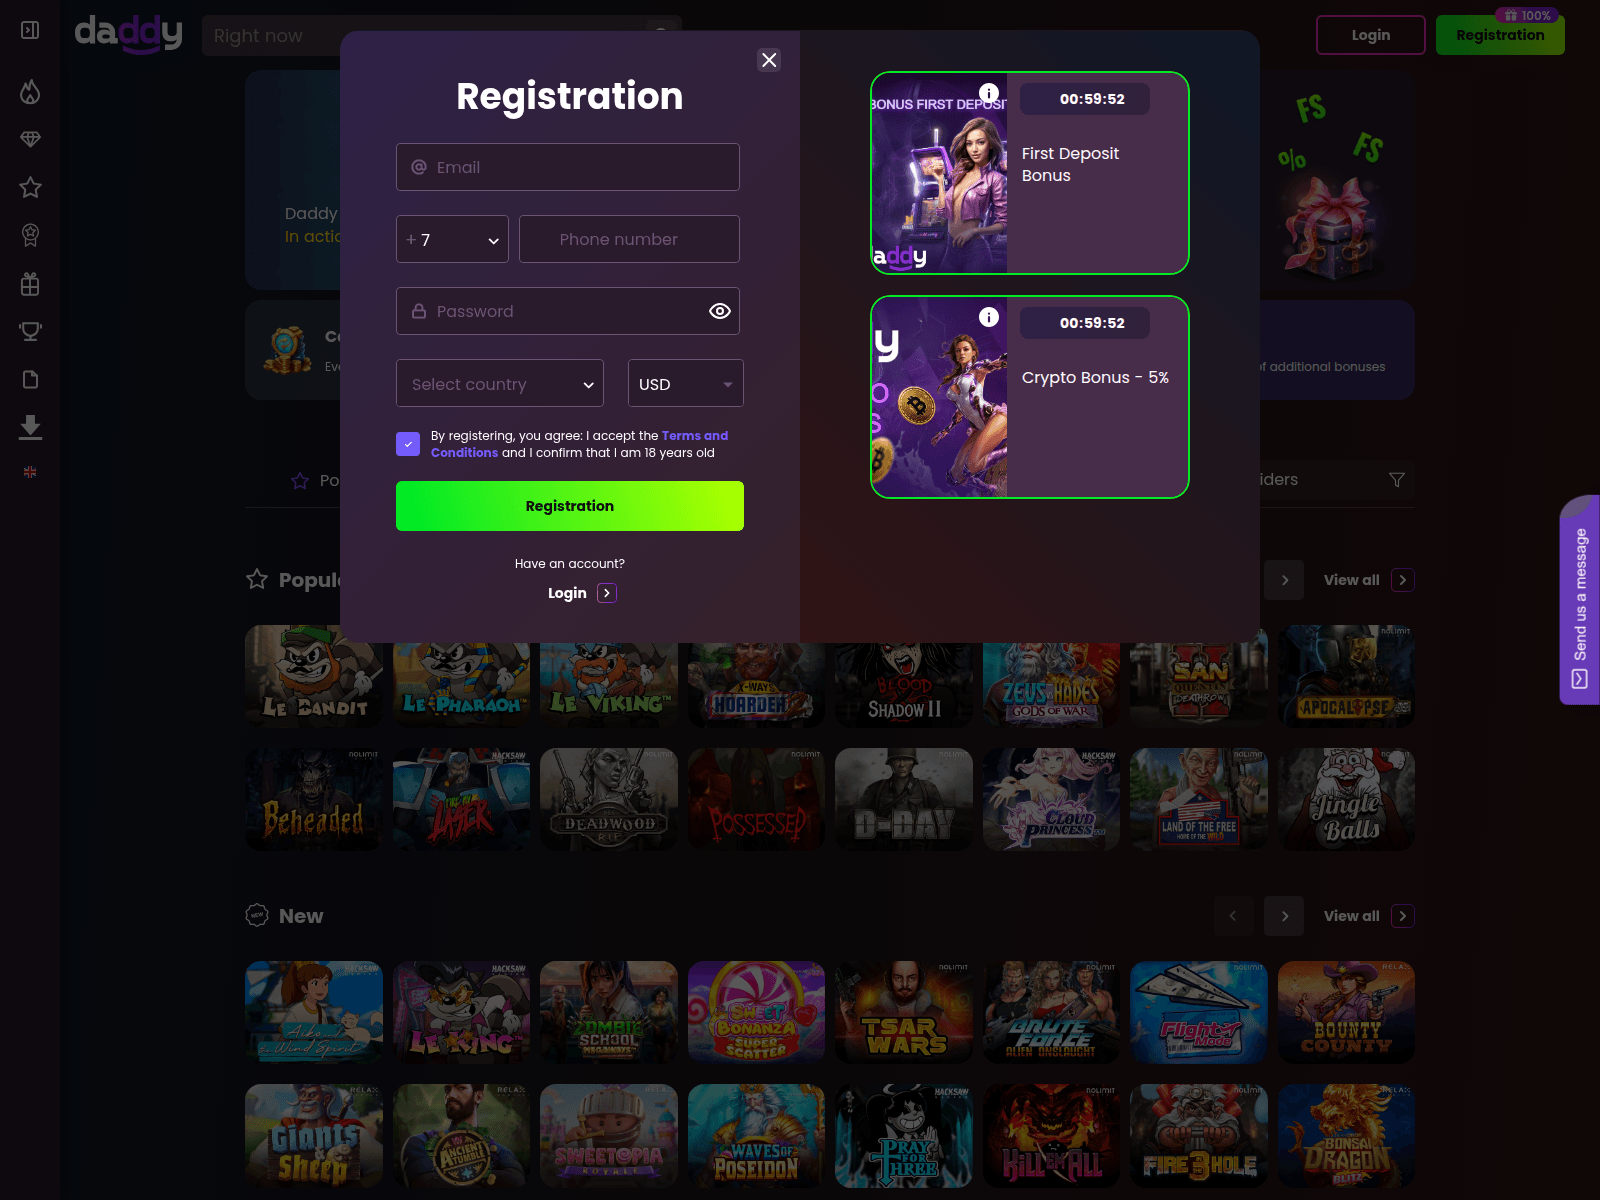
gmrediret.com
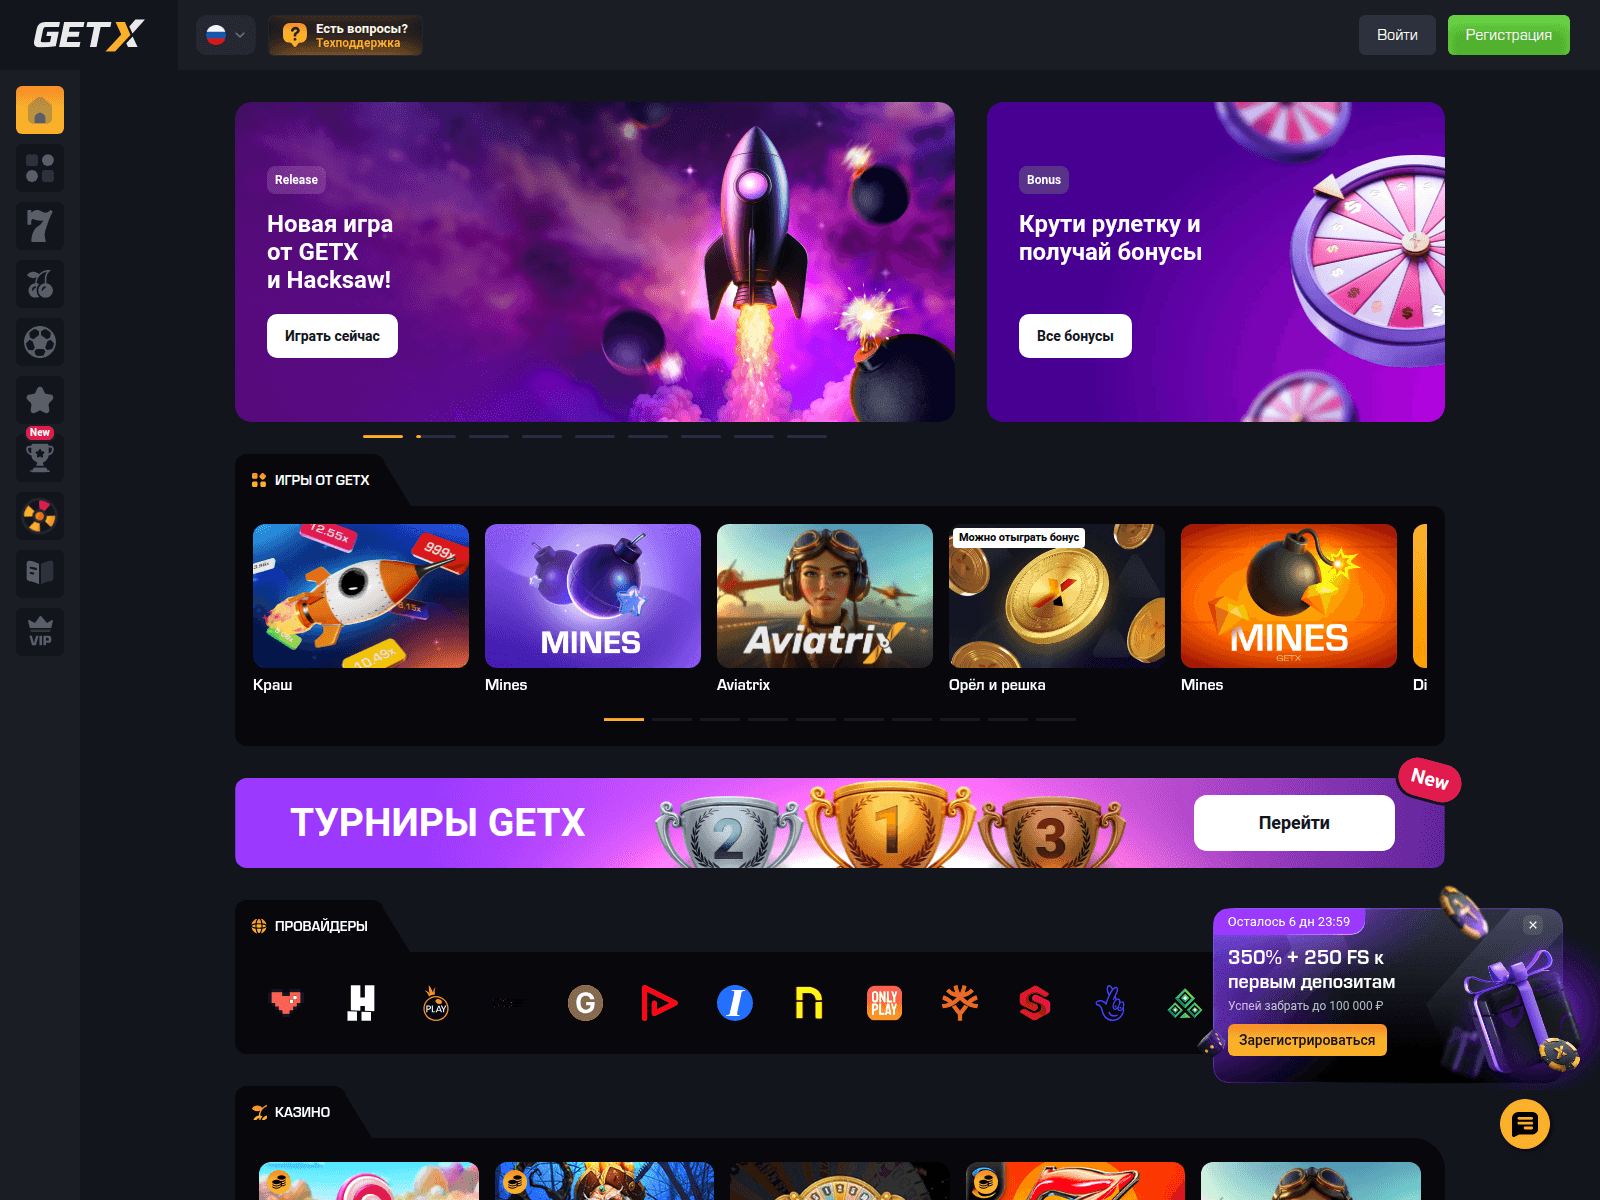
gwdz73x.top

gwfu87x.top
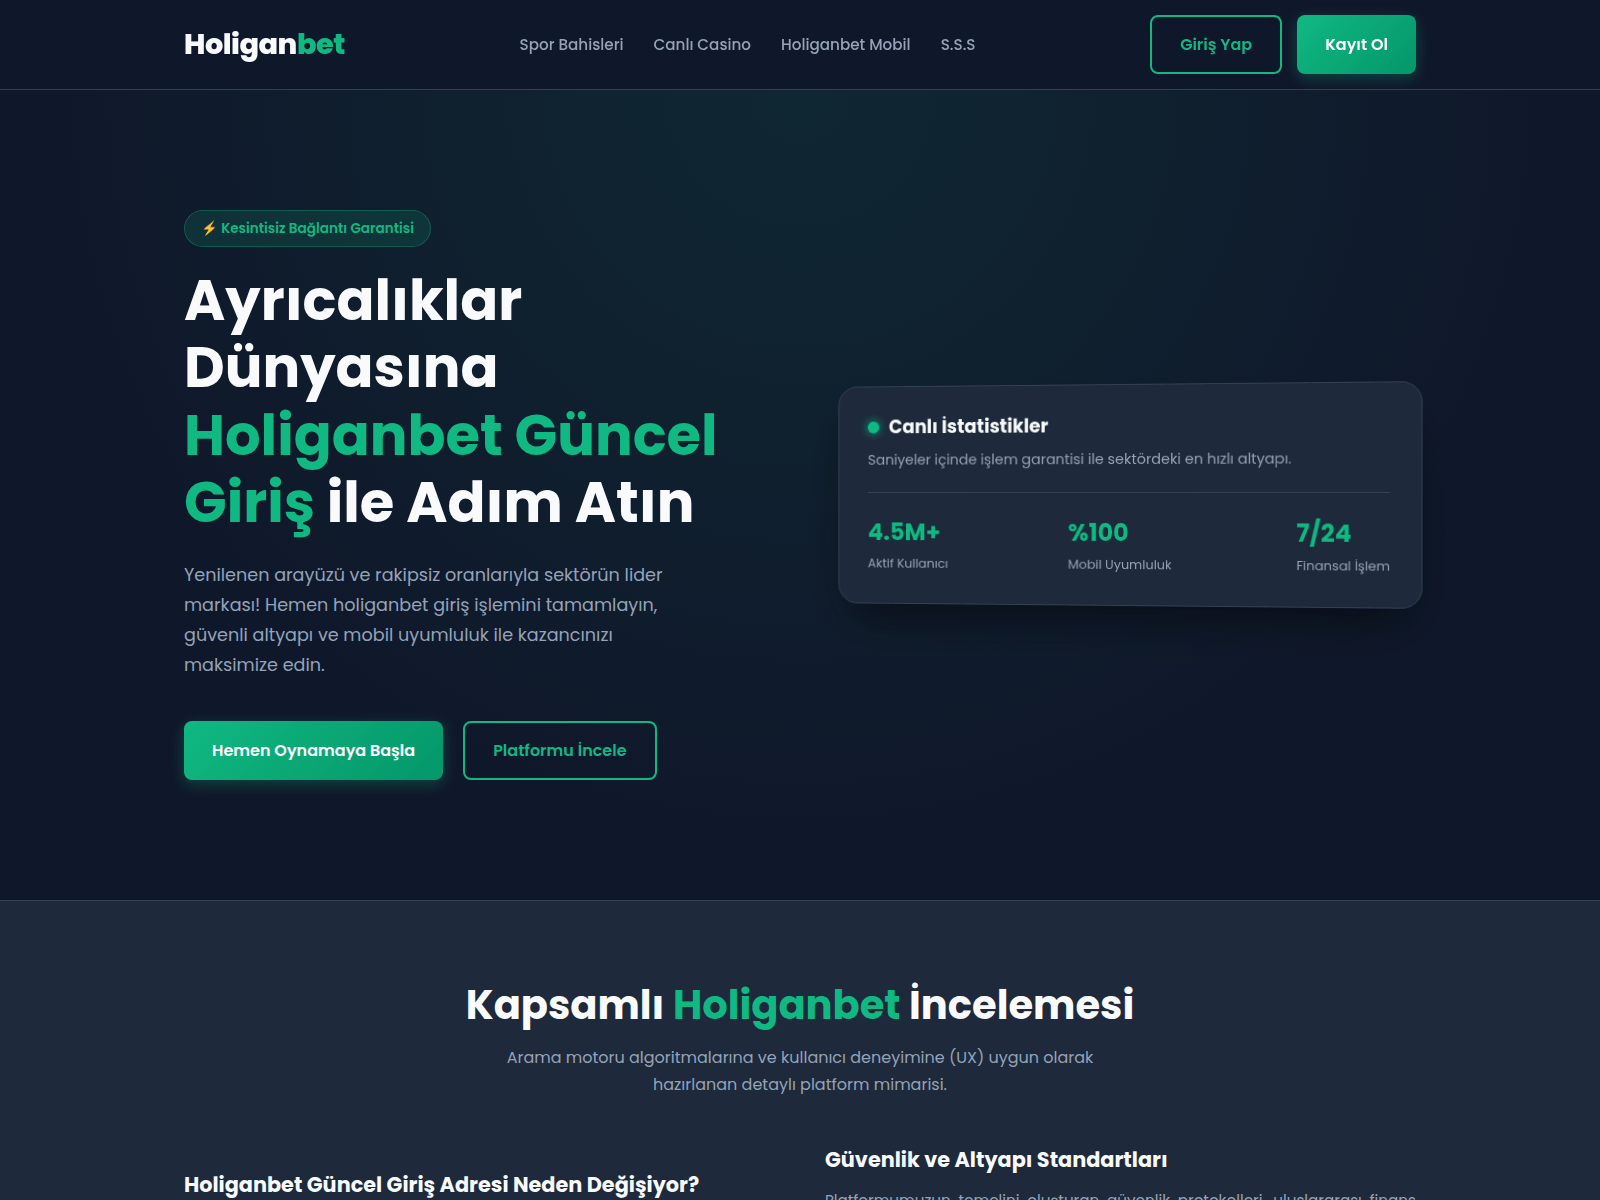
holiganbetcasino.icu

kent444cagam888.com
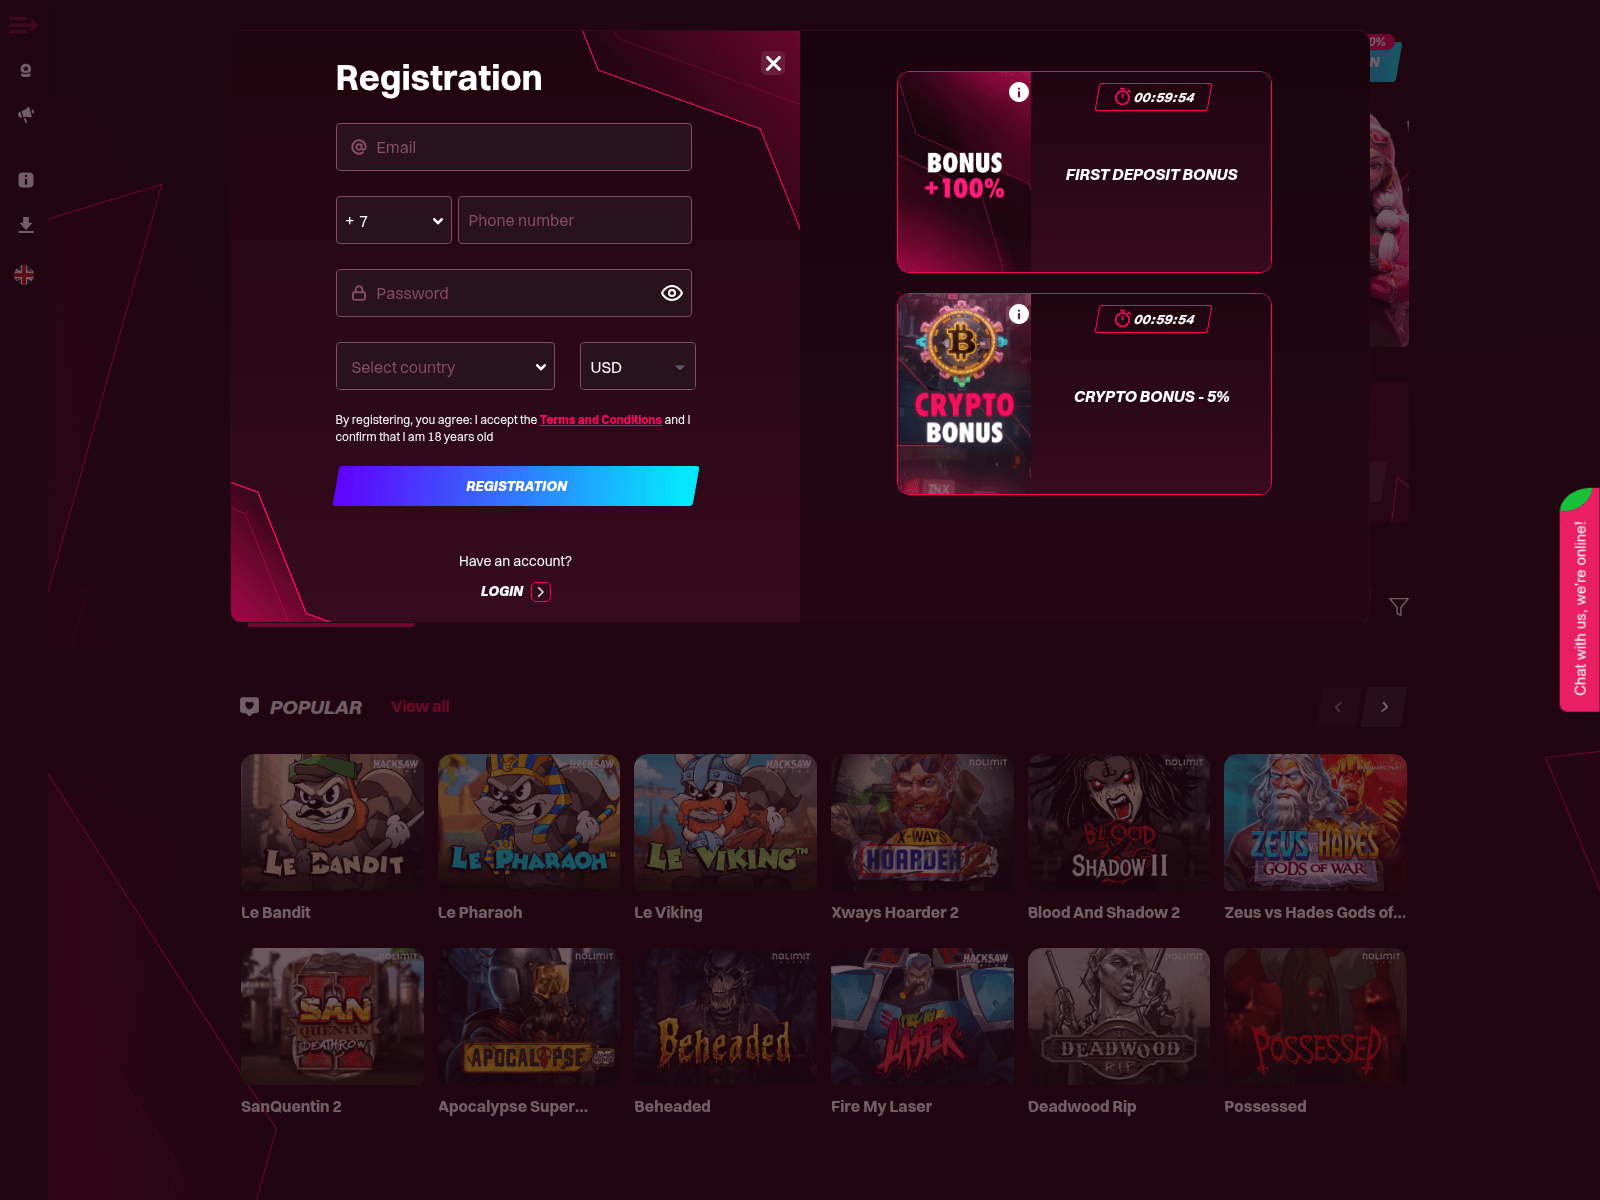
kentcasino195.com

kentcasino2829.com

krakencasinoonline-amp-tr.com

loregamb.com

luckygrands.com
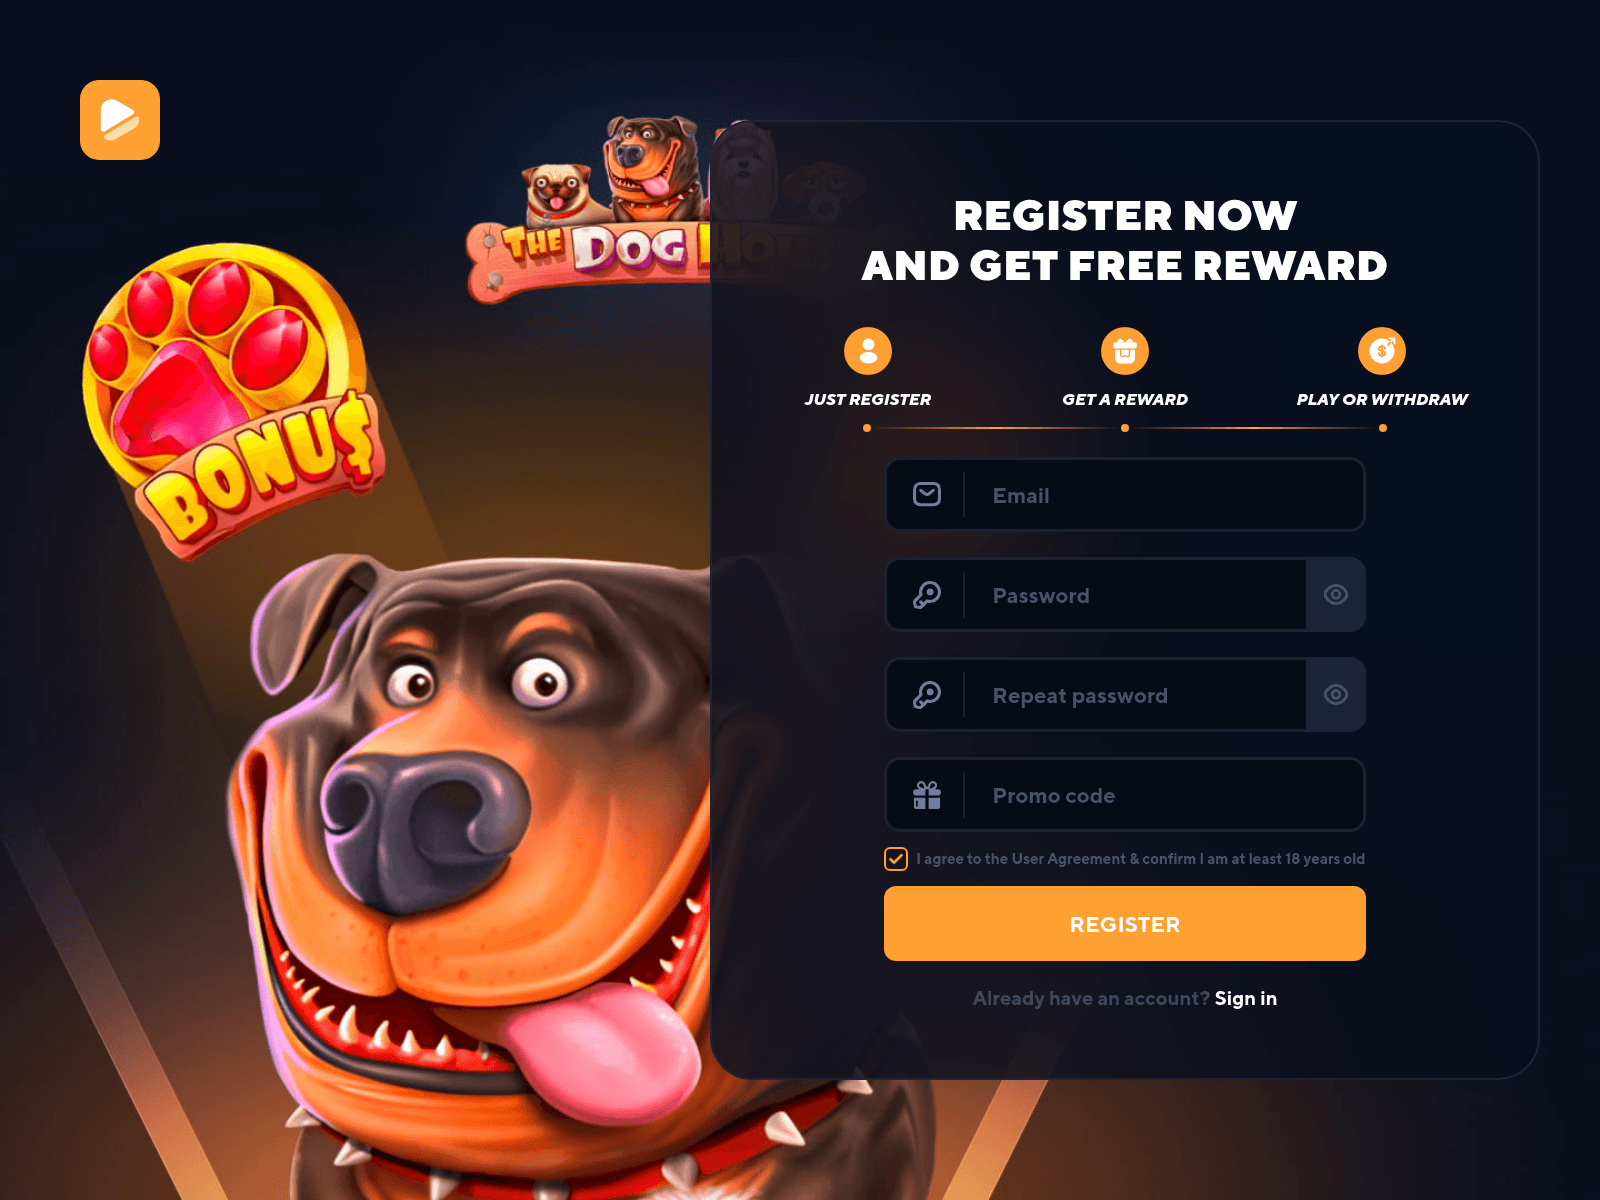
luckyranchroll.site
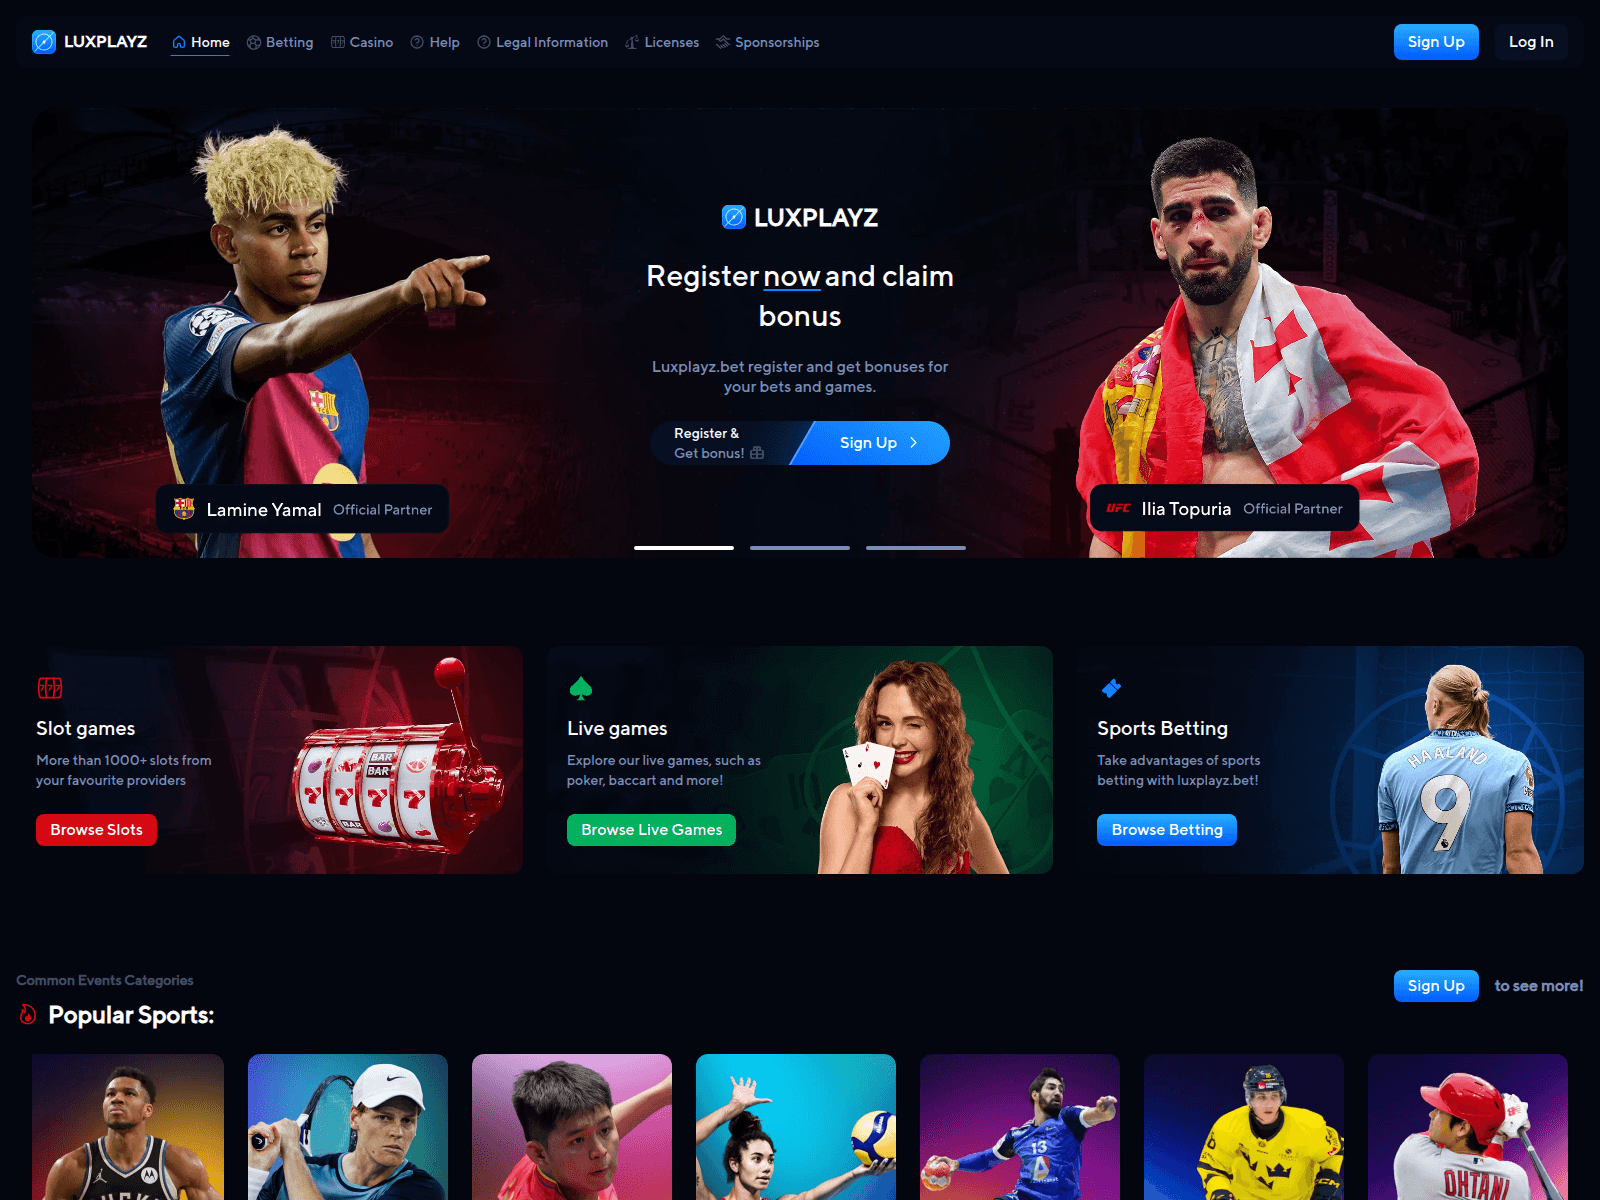
luxplayz.bet
meritking4871.com

mirage-3.com

primeviatest.online
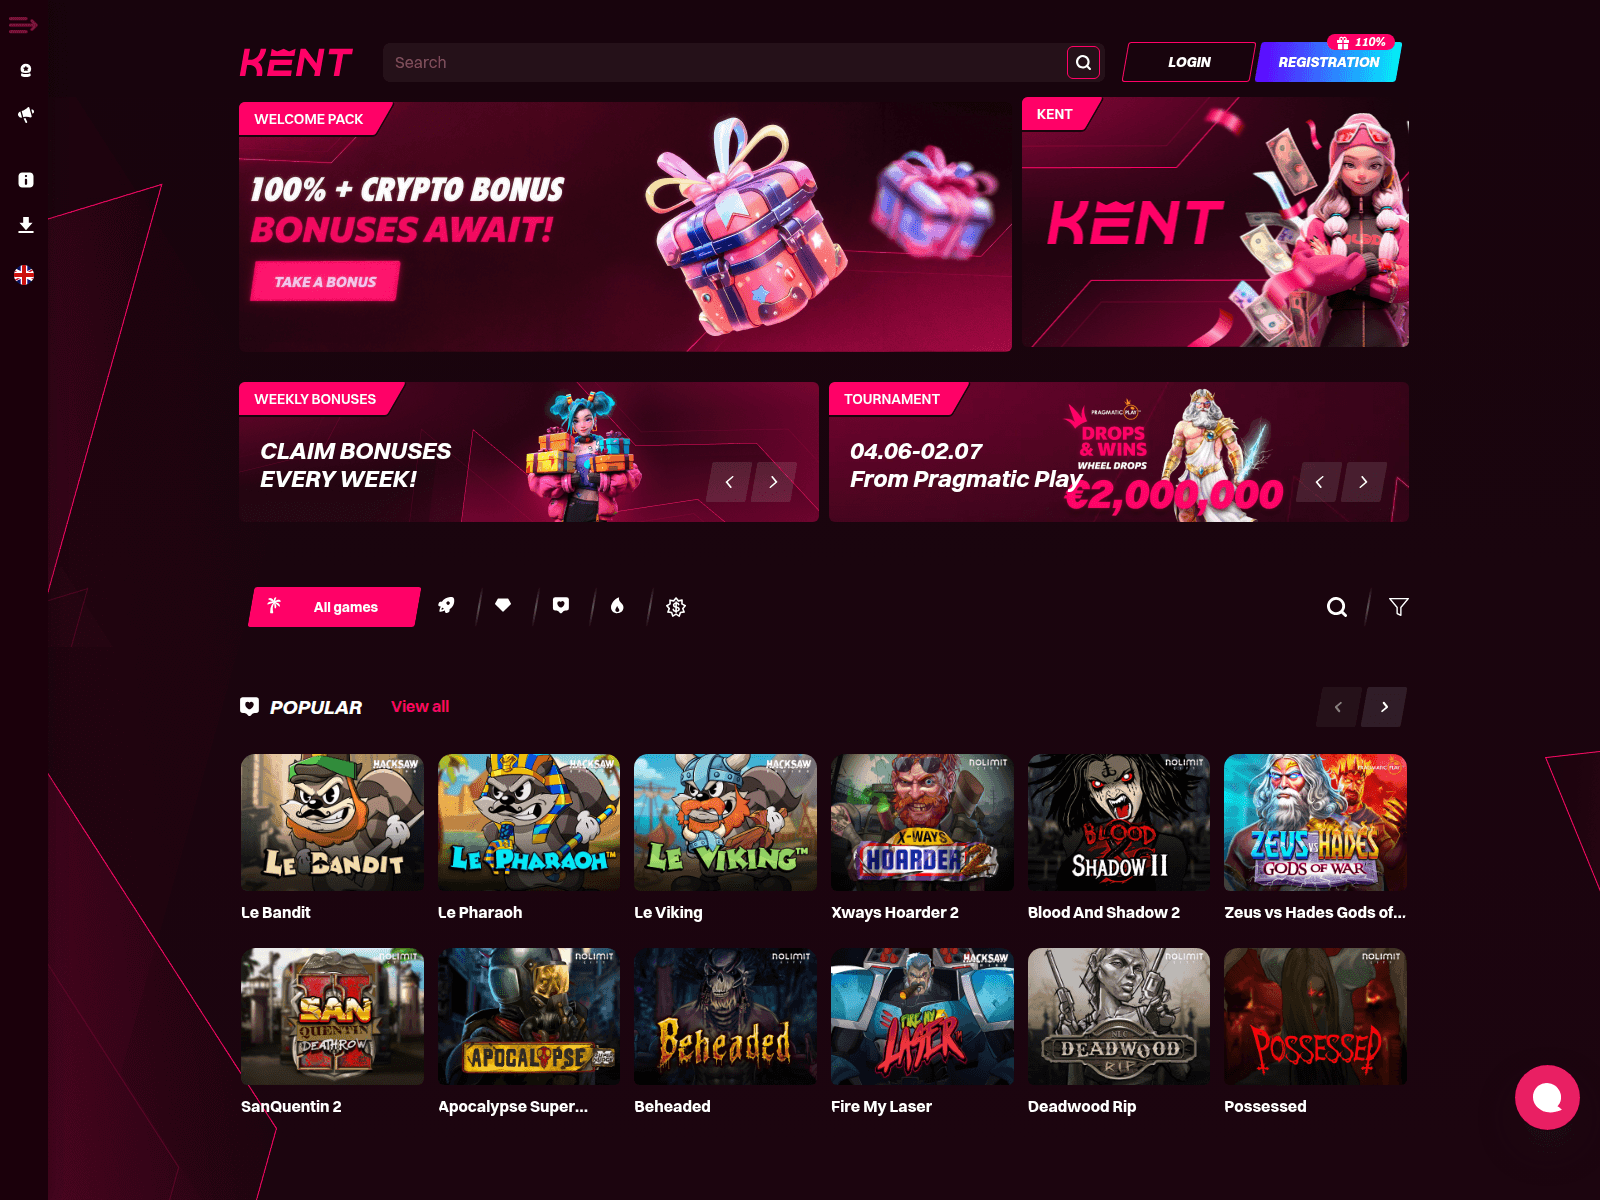
rash787kent.com
rollbitcasino.club
ruewax.com
sarowex.com

solwin.fr

spinchance.top
stake-try.com

swagspin.world

swetcas.com
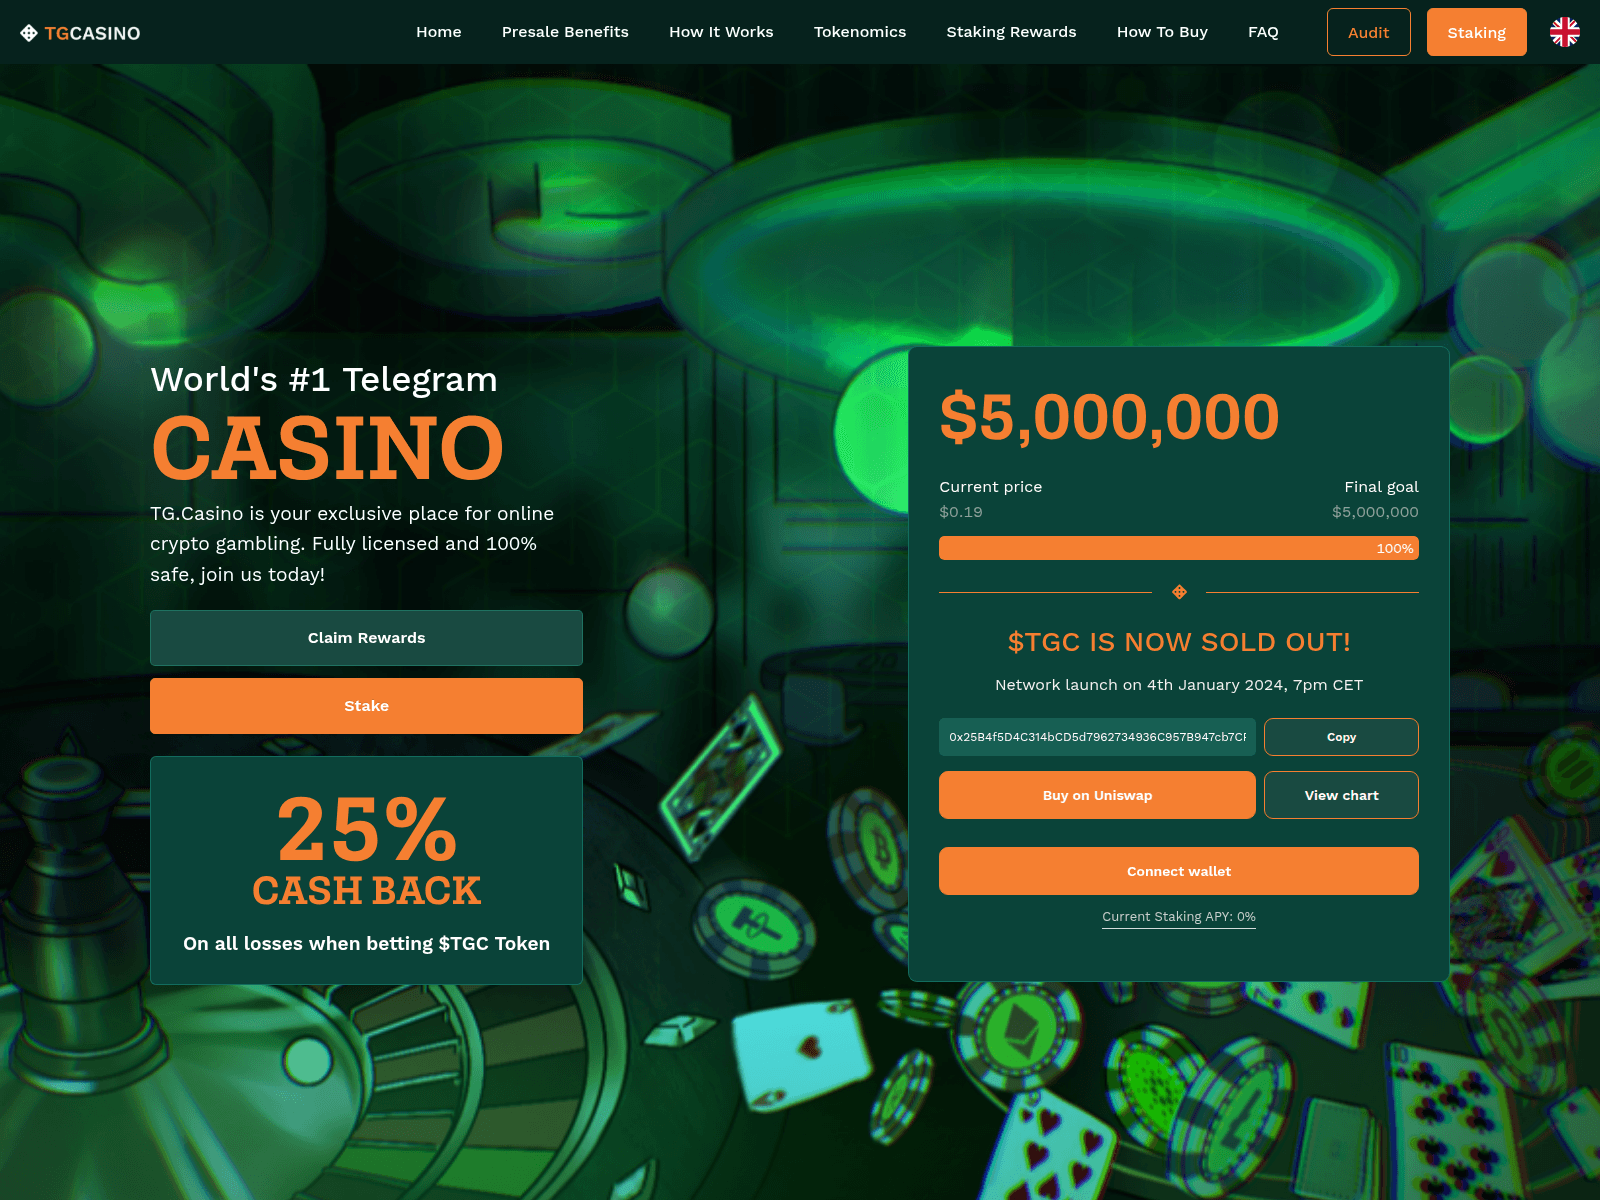
tg-casino-claim.pages.dev
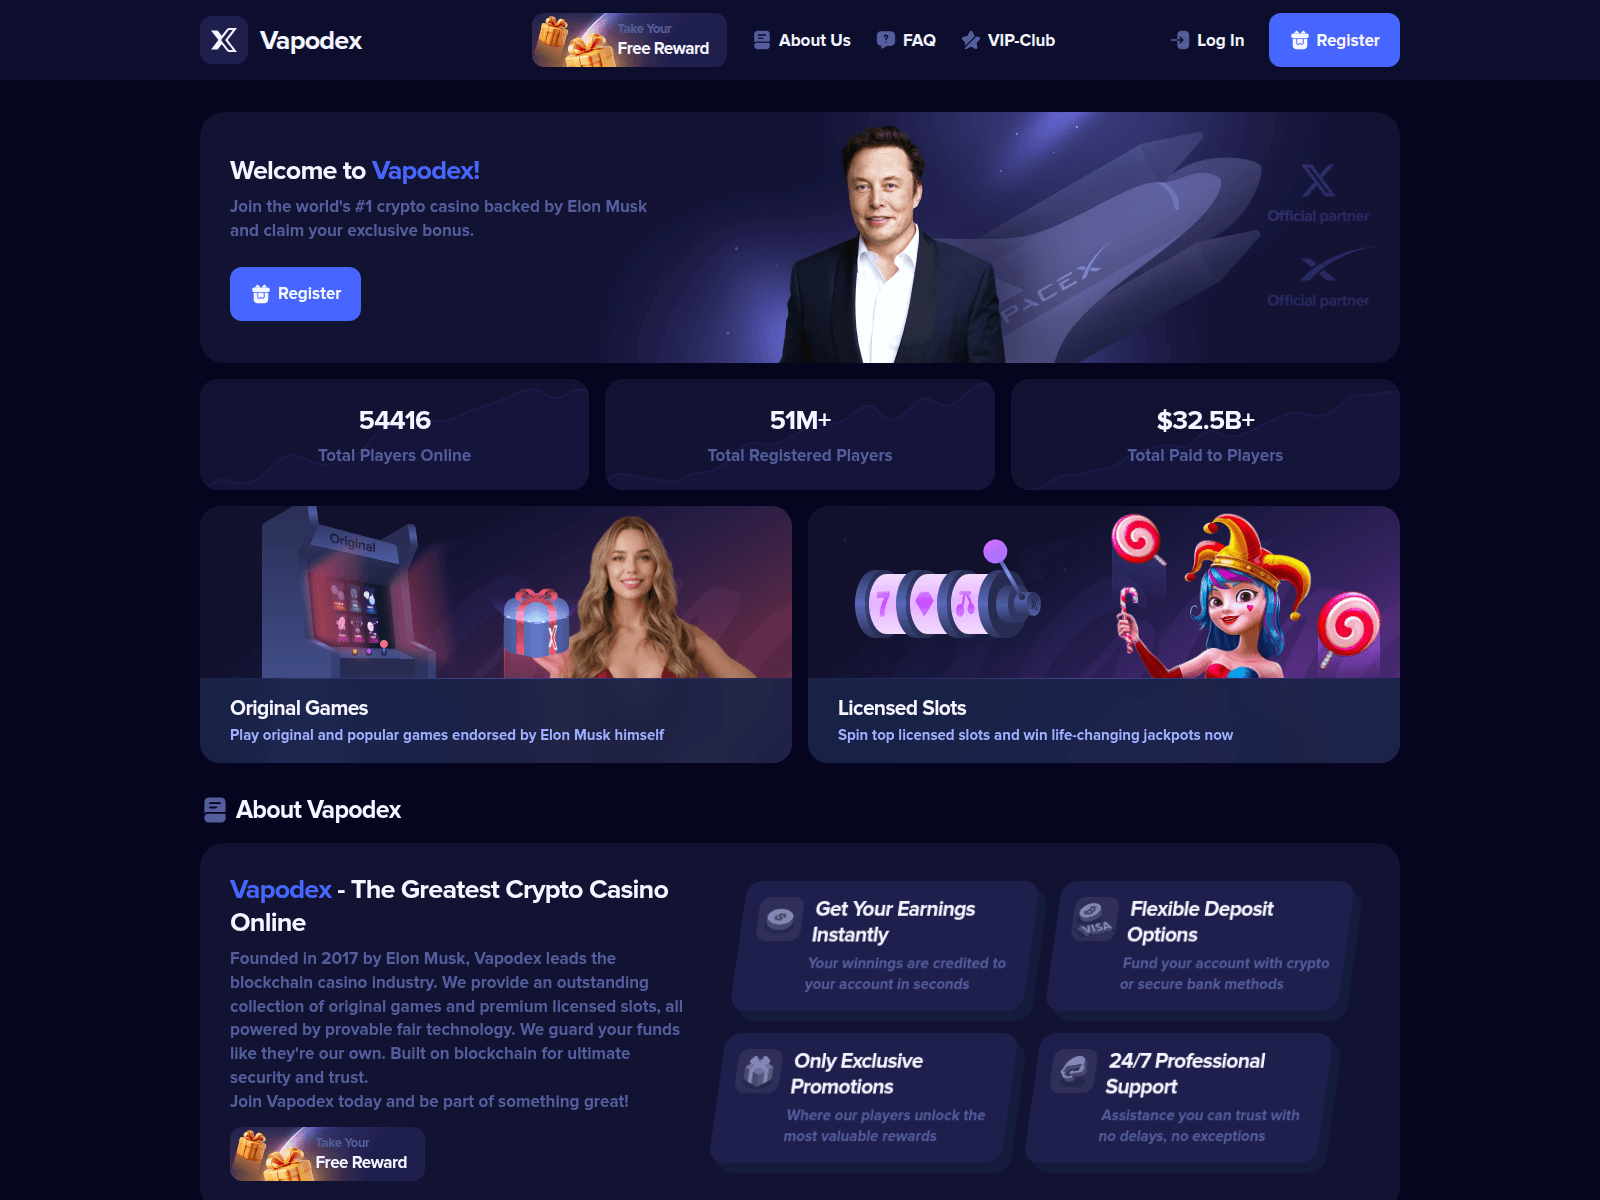
vapodex.com

vegcas.com

versbet.com
vngrcas.bet
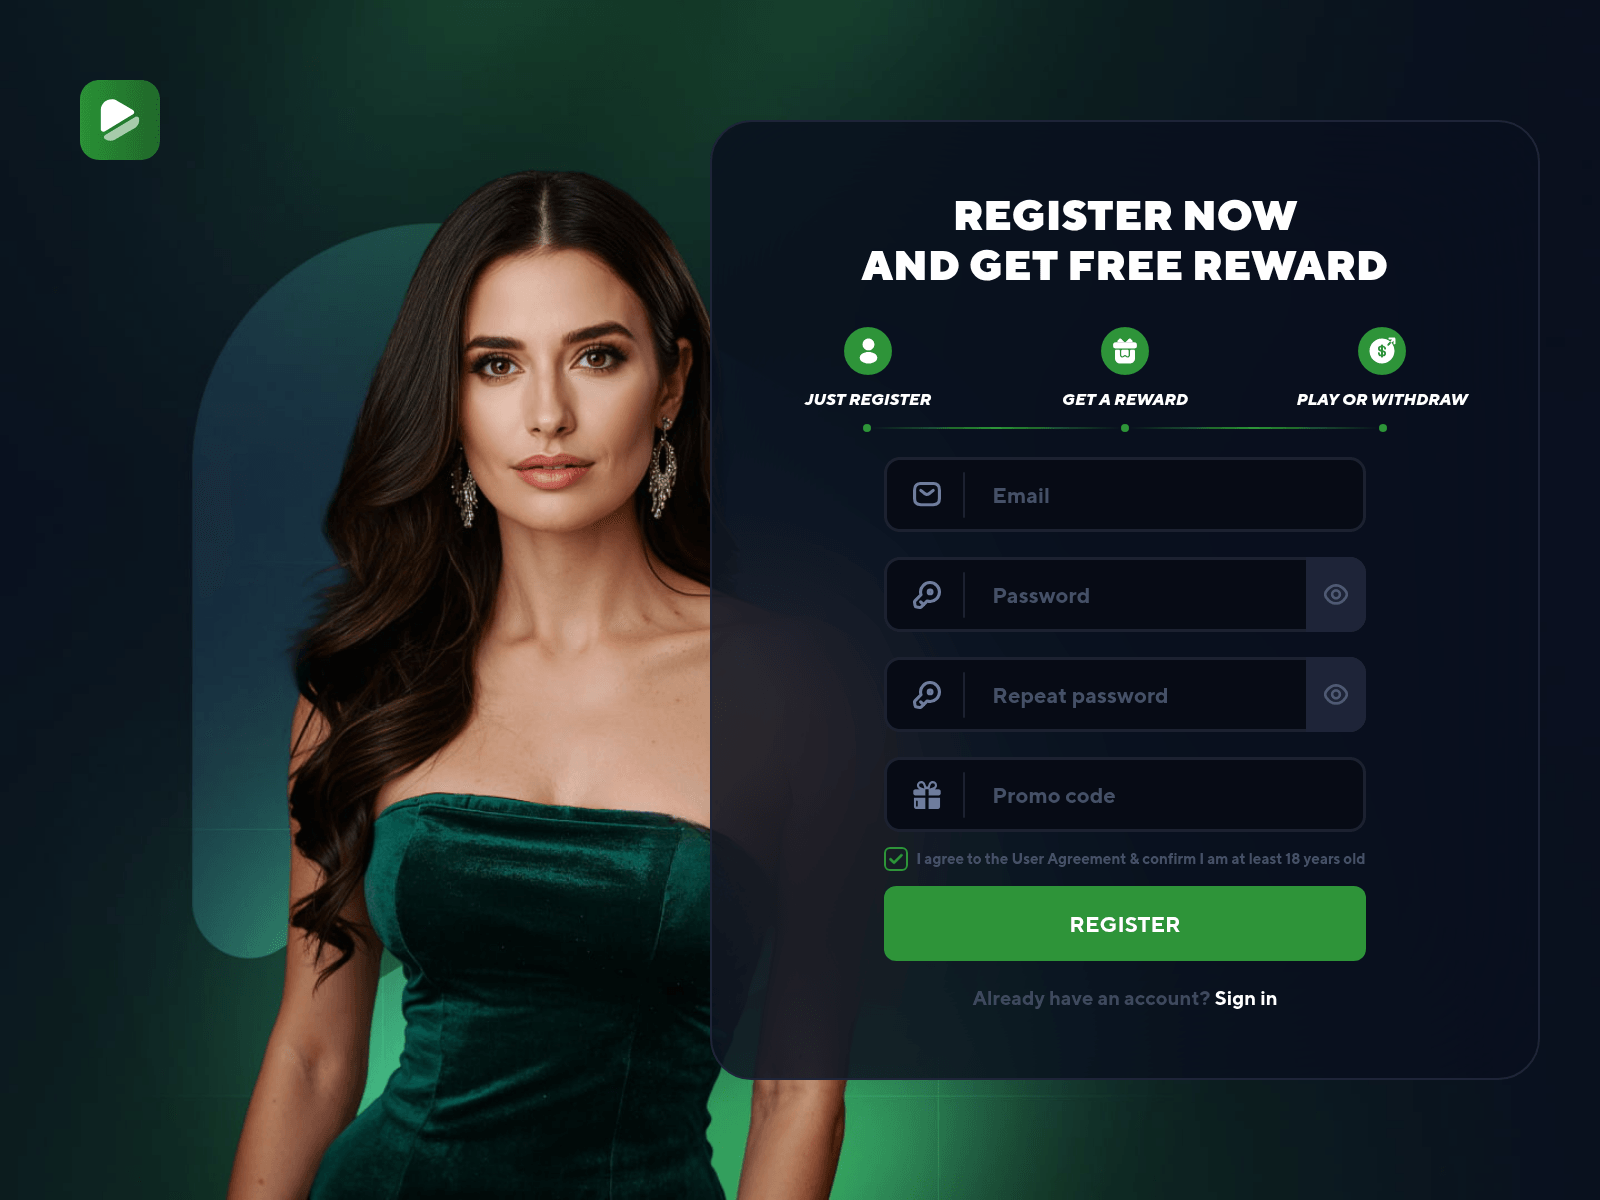
voscas.com
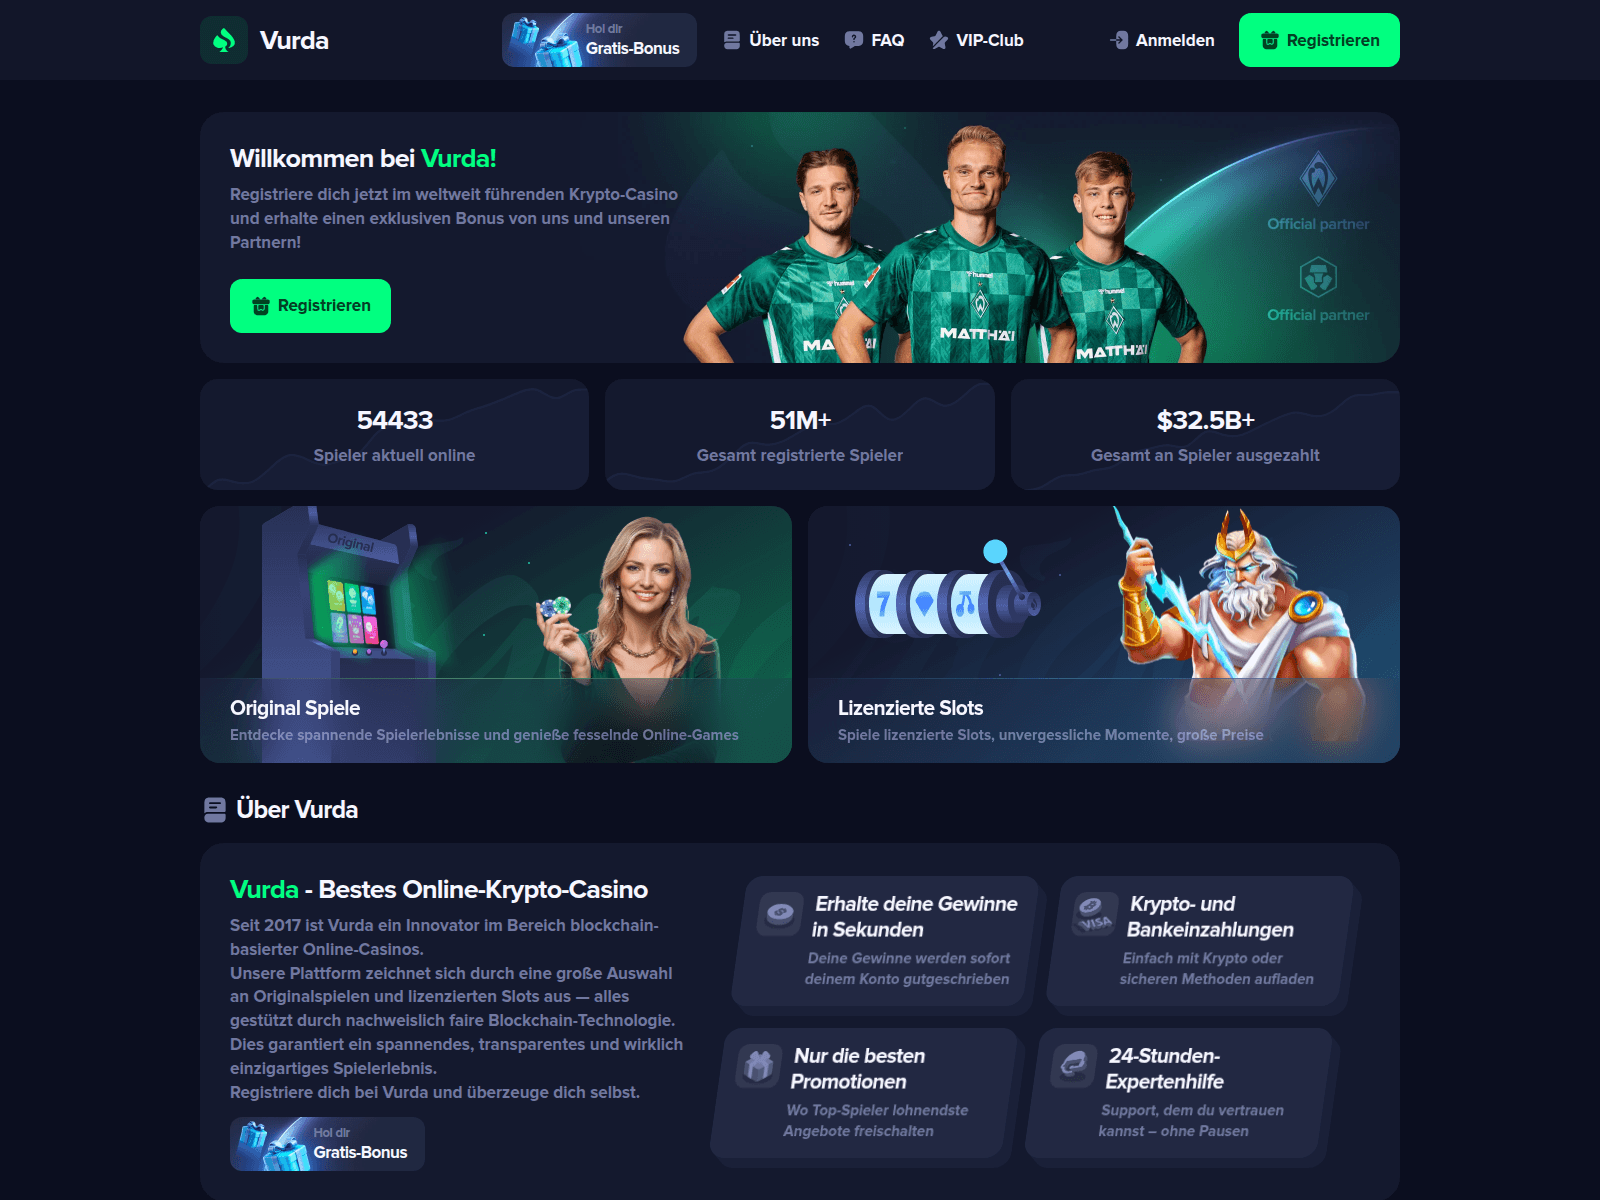
vurda.bet

wenredex.com
xebeto.com
Процес реагування на загрози Pipeline
Як перевіряється кожен домен у цьому хабі та як нейтралізуються підтверджені загрози. Повна візуалізація технологічного процесу →
Перевірки даних про загрози— кожен домен проходить сканування та перехресну перевірку щодо:
urlscan.ioЗнімок екрана · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ЗвітCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Безпека FiltersQuad9 · AdGuard · CleanBrowsingWeb-ПеревіритиFull surface scan
 crt.sh
Глобальна синхронізація постачальників— підтверджені випадки передаються 29 партнерам:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecОгляд сайтуAviraCloud detectionAvast / AVGWeb Shield«Касперський»OpenTIPDr.WebOnline scannerNetcraftЛіквідація APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ЗвітHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust