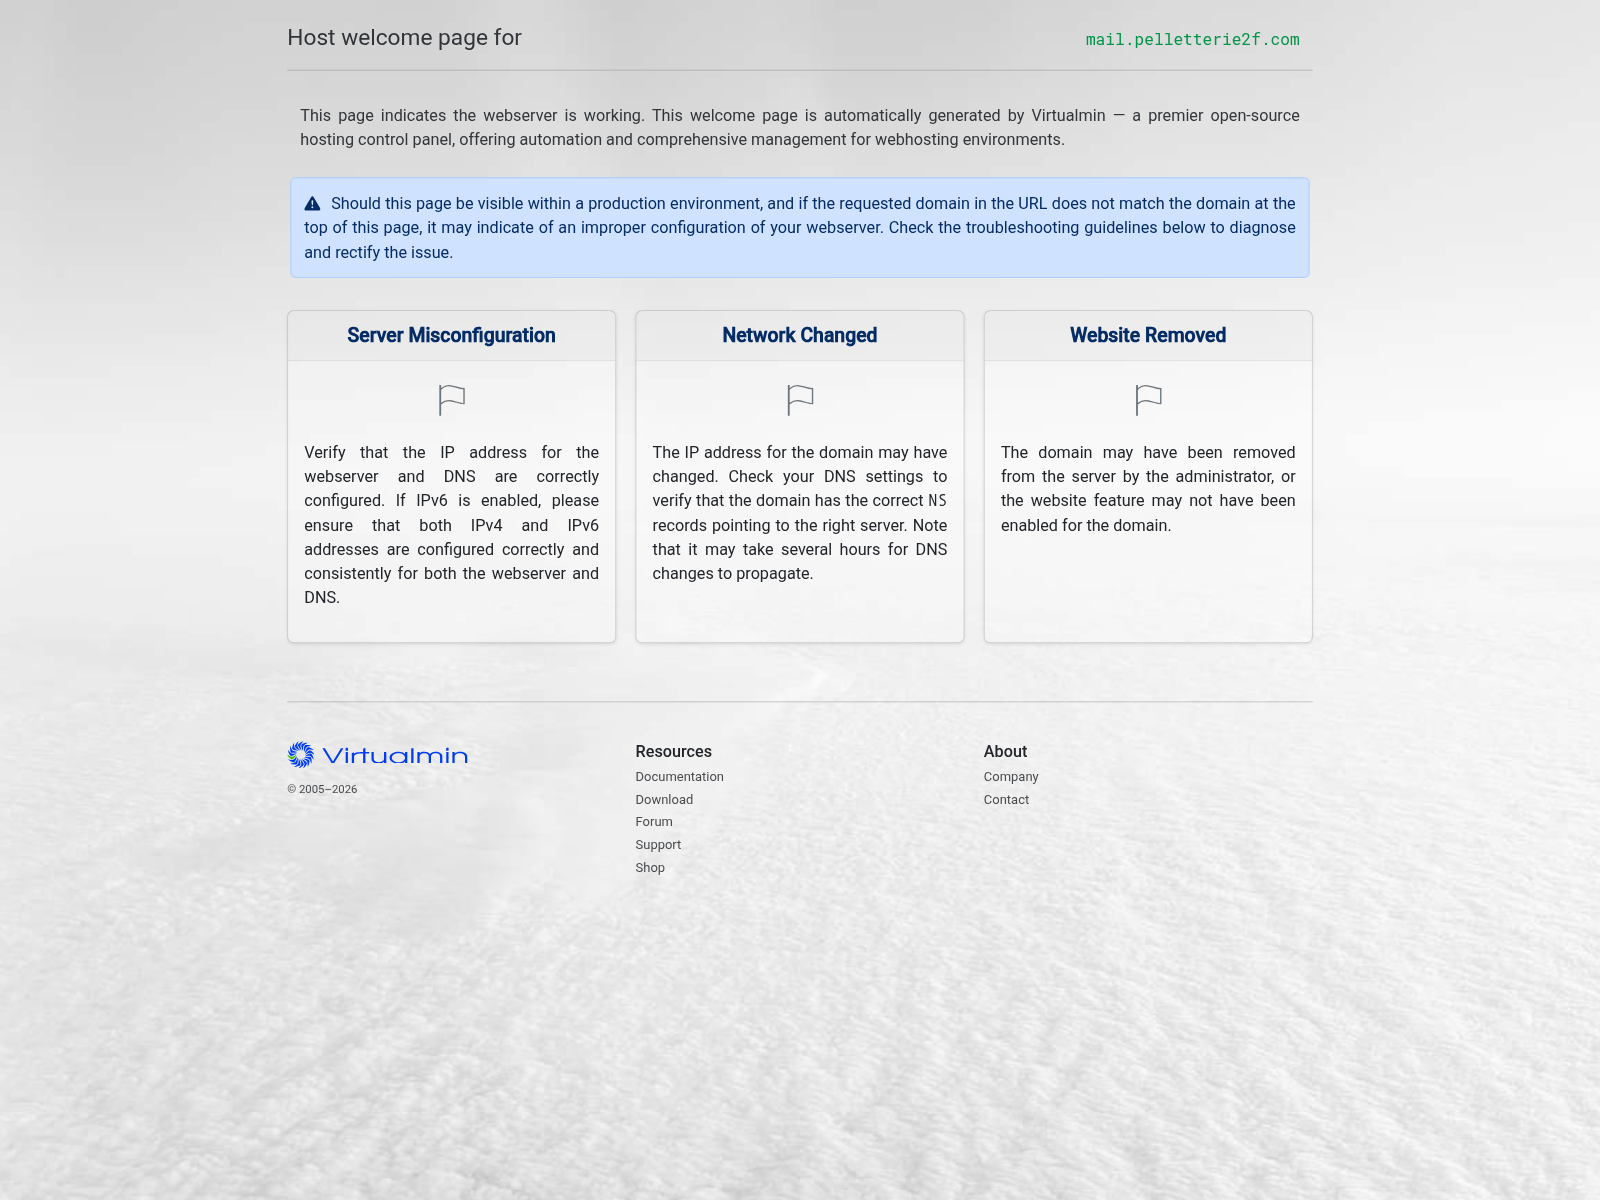
On 2026-11-10, webmail-authsecur.kukunochi.cfd displayed a Virtualmin-generated host welcome page. The page states that it indicates the webserver is working and was automatically generated by Virtualmin, described as a premier open-source hosting control panel. The header shows "Host welcome page for" alongside the domain mail.pelletterie2f.com. A notice warns that if the requested URL domain does not match the domain at the top of the page, it may indicate improper webserver configuration, and three troubleshooting cards titled Server Misconfiguration, Network Changed, and Website Removed offer diagnostic guidance.
URLScan截图 · 2026-11-10 17:59 UTC · SHA-256 dd22c58a…a46ea65
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-10, webmail-authsecur.kukunochi.cfd displayed a Virtualmin-generated host welcome page. The page states that it indicates the webserver is working and was automatically generated by Virtualmin, described as a premier open-source hosting control panel. The header shows "Host welcome page for" alongside the domain mail.pelletterie2f.com. A notice warns that if the requested URL domain does not match the domain at the top of the page, it may indicate improper webserver configuration, and three troubleshooting cards titled Server Misconfiguration, Network Changed, and Website Removed offer diagnostic guidance.
The stored VirusTotal domain result reports 18 detections out of 92 engines. DNS8 reported "suspicious"; ESET reported "phishing".
PhishDestroy records webmail-authsecur.kukunochi.cfd showing a Virtualmin-generated host welcome page with server troubleshooting guidance.
AI摘要
On 2026-11-10, webmail-authsecur.kukunochi.cfd displayed a Virtualmin-generated host welcome page. The page states that it indicates the webserver is working and was automatically generated by Virtualmin, described as a premier open-source hosting control panel. The header shows "Host welcome page for" alongside the domain mail.pelletterie2f.com. A notice warns that if the requested URL domain does not match the domain at the top of the page, it may indicate improper webserver configuration, and three troubleshooting cards titled Server Misconfiguration, Network Changed, and Website Removed offer diagnostic guidance. The stored VirusTotal domain result reports 18 detections out of 92 engines. DNS8 reported "suspicious"; ESET reported "phishing".
Stored registration data identifies NameSilo as the registrar. PhishDestroy maintains separate registrar investigations; that broader material is contextual and is not an independent detection for this domain.
The linked repository preserves daily zone observations across seven ShortDot-operated TLDs, including registration volume and abuse-related indicators. This registry context is supporting background and is not an independent detection for the domain in this report.
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:19 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:19 UTClast content: 2026-11-22 11:19 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.