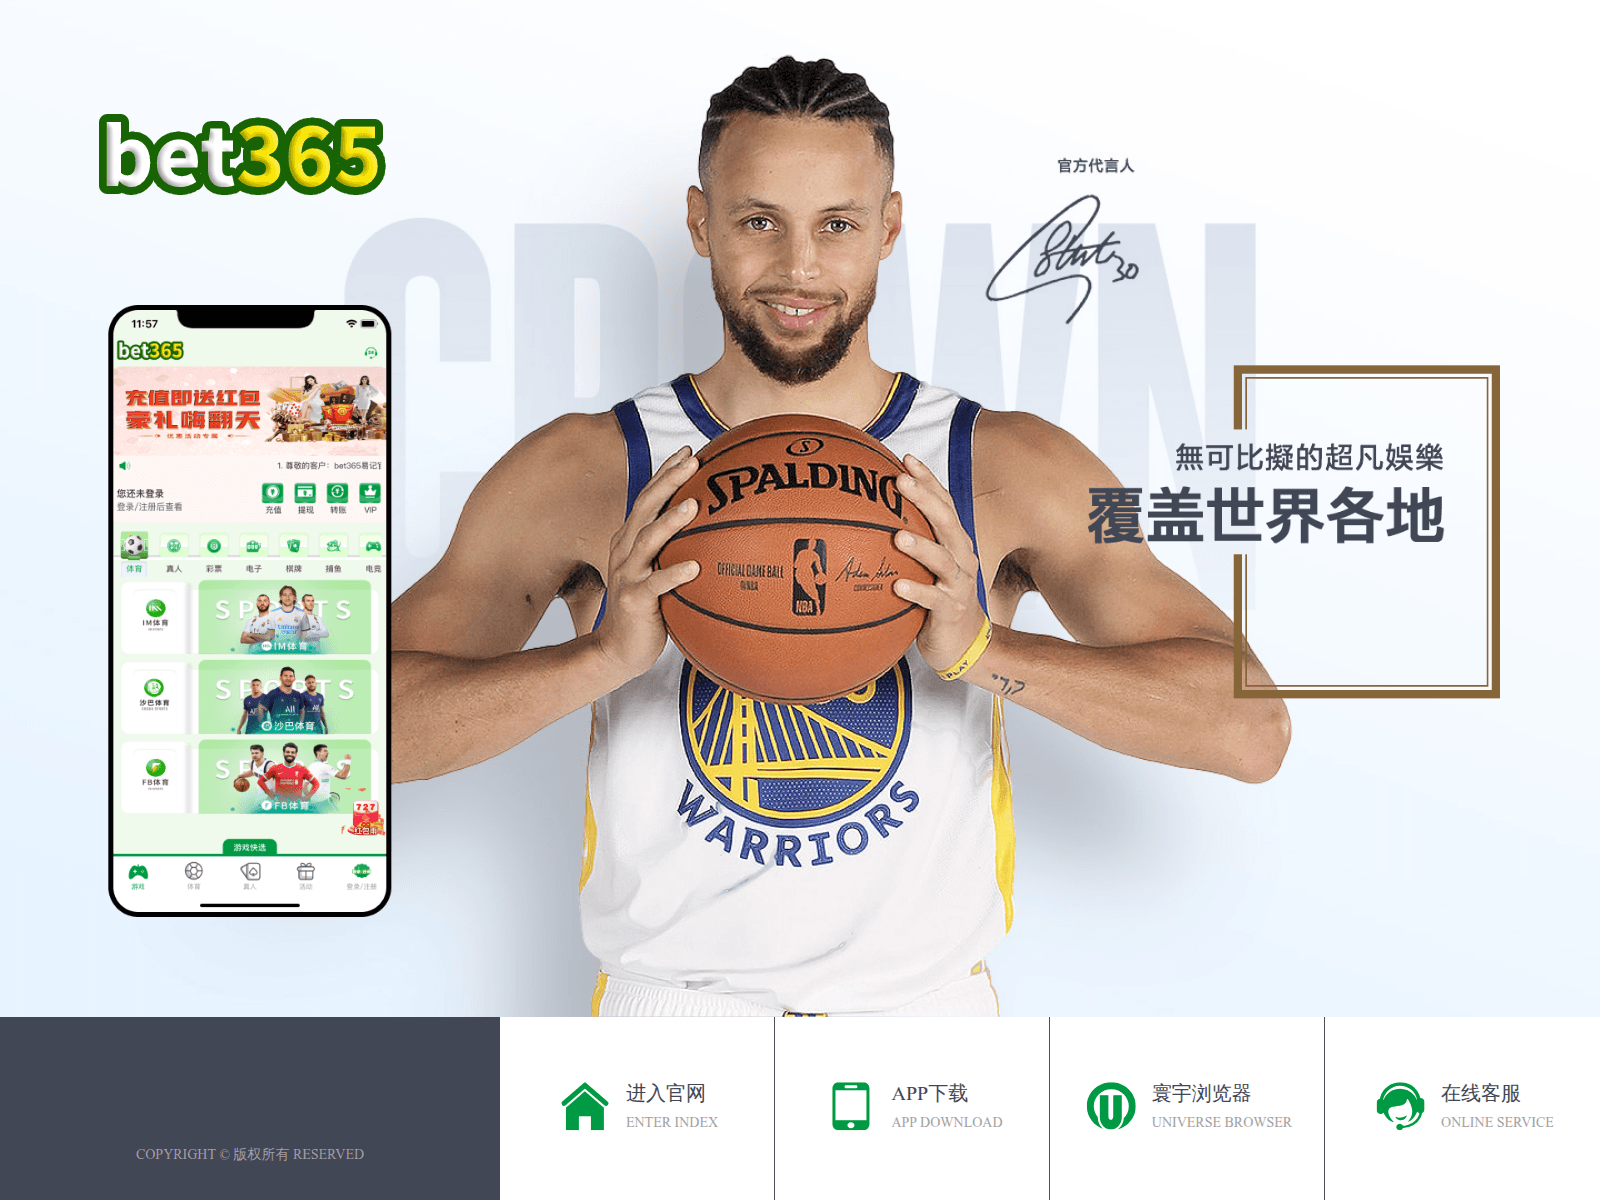
On 2026-11-07, 365972.top displayed a landing page carrying the bet365 logo and Chinese-language promotional text. The page features a large image of a basketball player in a Warriors jersey holding a ball, labeled as an official spokesperson, alongside a phone mockup showing a betting app interface with sports, lottery, and card game categories. Below the main image, four labeled buttons offer entry to the official site, app download, a browser link, and online customer service, with a copyright notice at the bottom.
URLScan截图 · 2026-11-07 05:32 UTC · SHA-256 f8358a02…5b848bd
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-07, 365972.top displayed a landing page carrying the bet365 logo and Chinese-language promotional text. The page features a large image of a basketball player in a Warriors jersey holding a ball, labeled as an official spokesperson, alongside a phone mockup showing a betting app interface with sports, lottery, and card game categories. Below the main image, four labeled buttons offer entry to the official site, app download, a browser link, and online customer service, with a copyright notice at the bottom.
The stored VirusTotal domain result reports 14 detections out of 92 engines. ESET reported "suspicious"; VIPRE reported "malware".
365972.top: Recorded bet365-branded sports betting landing page
AI 描述
PhishDestroy records 365972.top as a bet365-branded sports betting landing page with an app preview and customer service links.
AI摘要
On 2026-11-07, 365972.top displayed a landing page carrying the bet365 logo and Chinese-language promotional text. The page features a large image of a basketball player in a Warriors jersey holding a ball, labeled as an official spokesperson, alongside a phone mockup showing a betting app interface with sports, lottery, and card game categories. Below the main image, four labeled buttons offer entry to the official site, app download, a browser link, and online customer service, with a copyright notice at the bottom. The stored VirusTotal domain result reports 14 detections out of 92 engines. ESET reported "suspicious"; VIPRE reported "malware".
The owner of the website is using a service to hide their identity on WHOIS According to Tranco this site has a low rank Pulsedive reports elevated risk with this website. This website has been reported for Phishing by IPQS This website has been reported as Suspicious by IPQS
The SSL certificate is valid This website is safe according to DNSFilter
证据层Availability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP注册
观测时间线current episode first observed: 2026-11-08 10:22 UTCfirst terminal observation: 2026-11-08 10:22 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.