
Здійснюйте пошук серед відстежуваних доменів та переглядайте збережені докази, виявлені випадки та останні дані щодо доступності.
219,806
Загальна кількість відстежених
213,476
Виявлено VT
91,911
Останнє підключення: активний
127,895
Недоступний під час останньої перевірки
568
VT — у процесі розгляду
How This Attack Works
Fake Airdrop Scams exploit the burgeoning interest in cryptocurrencies by deceiving users into believing they are receiving free tokens.
STEP 1
Bait with Free Tokens
Scammers create fake websites promising free cryptocurrency airdrops to lure victims.
STEP 2
Collect Personal Data
Users are prompted to enter personal details or connect their crypto wallets to receive the airdrop.
STEP 3
Execute a Scam Transaction
Once connected, scammers initiate unauthorized transactions or steal sensitive data.
STEP 4
Disappear with the Loot
Scammers transfer stolen funds to anonymous accounts, disappearing without a trace.
Technical Analysis
Fake Airdrop Scams often involve sophisticated phishing techniques. Attackers use clone websites that mimic legitimate airdrop events. These sites are built using JavaScript and HTML to create convincing interfaces. Scammers may employ smart contract functions such as 'transfer' and 'approve' to gain unauthorized access to victims' wallets. Additionally, phishing emails and social media posts are used to drive traffic to these malicious websites. Infrastructure often involves домени, зареєстровані через top registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED, ensuring anonymity and making it challenging to track the perpetrators.
Real Cases
The Ethereum Classic Airdrop Scam (2024)
$3.5 million stolen
Scammers created a fake Ethereum Classic airdrop event, stealing millions from unsuspecting users.
Fake Uniswap Airdrop (2023)
$2 million stolen
A bogus Uniswap token airdrop fooled users into relinquishing control of their wallets.
The Polkadot Giveaway Fraud (2024)
$1 million stolen
A fake Polkadot giveaway led to substantial financial losses for crypto enthusiasts.
How to Detect
Unsolicited messages about free airdrops
Домени with unusual TLDs like .xyz and .top
Requests for private keys or wallet access
Poorly designed websites with typos
Терміново calls-to-action pressuring immediate response
How to Protect Yourself
1
Verify airdrop legitimacy through official channels
2
Avoid clicking on unsolicited links
3
Use hardware wallets for extra security
4
Enable two-factor authentication
5
Regularly update software and security protocols
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 6,437 domains tracked for this threat type
Fake Airdrop Scam 6,437 domains
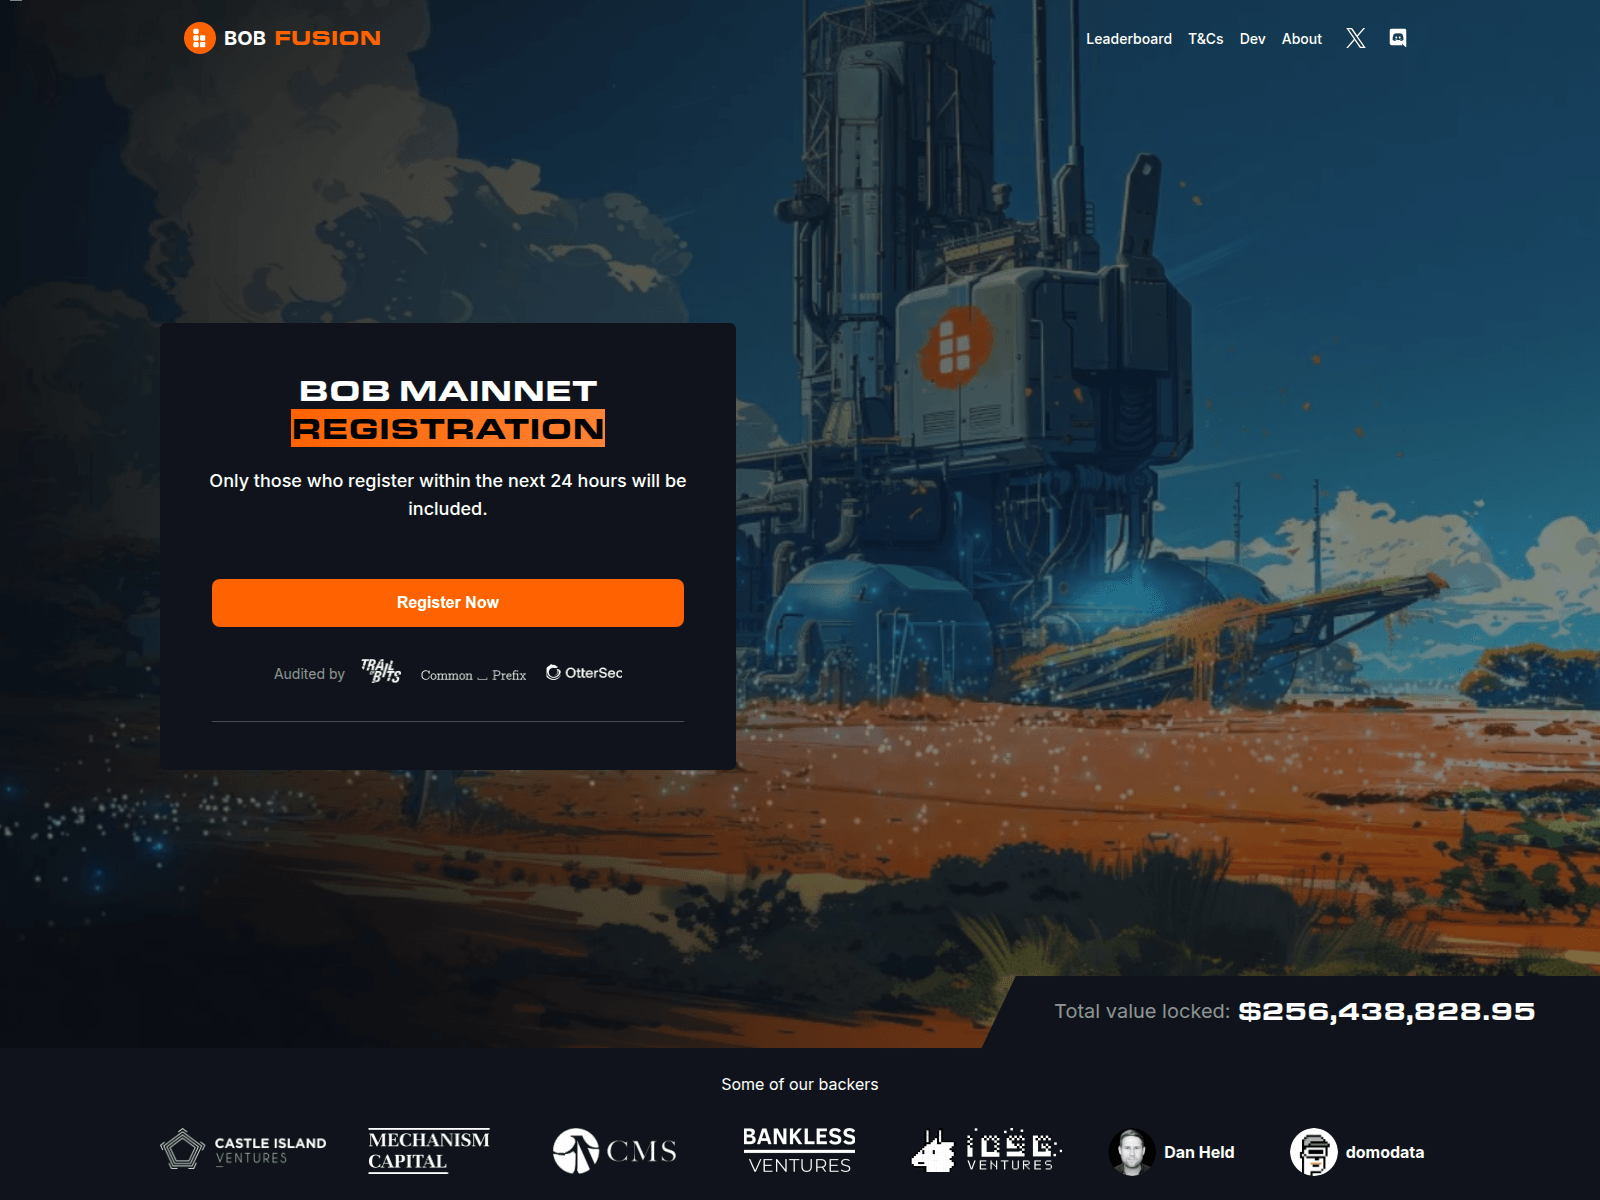
gobob.live

home-coinbase.com

iiweb-baseiinetmx.click

iiweb-baseiinetmx.onl

iiweb-baseiinetmx.sbs

imtokenapps.net

iwackfud.digital
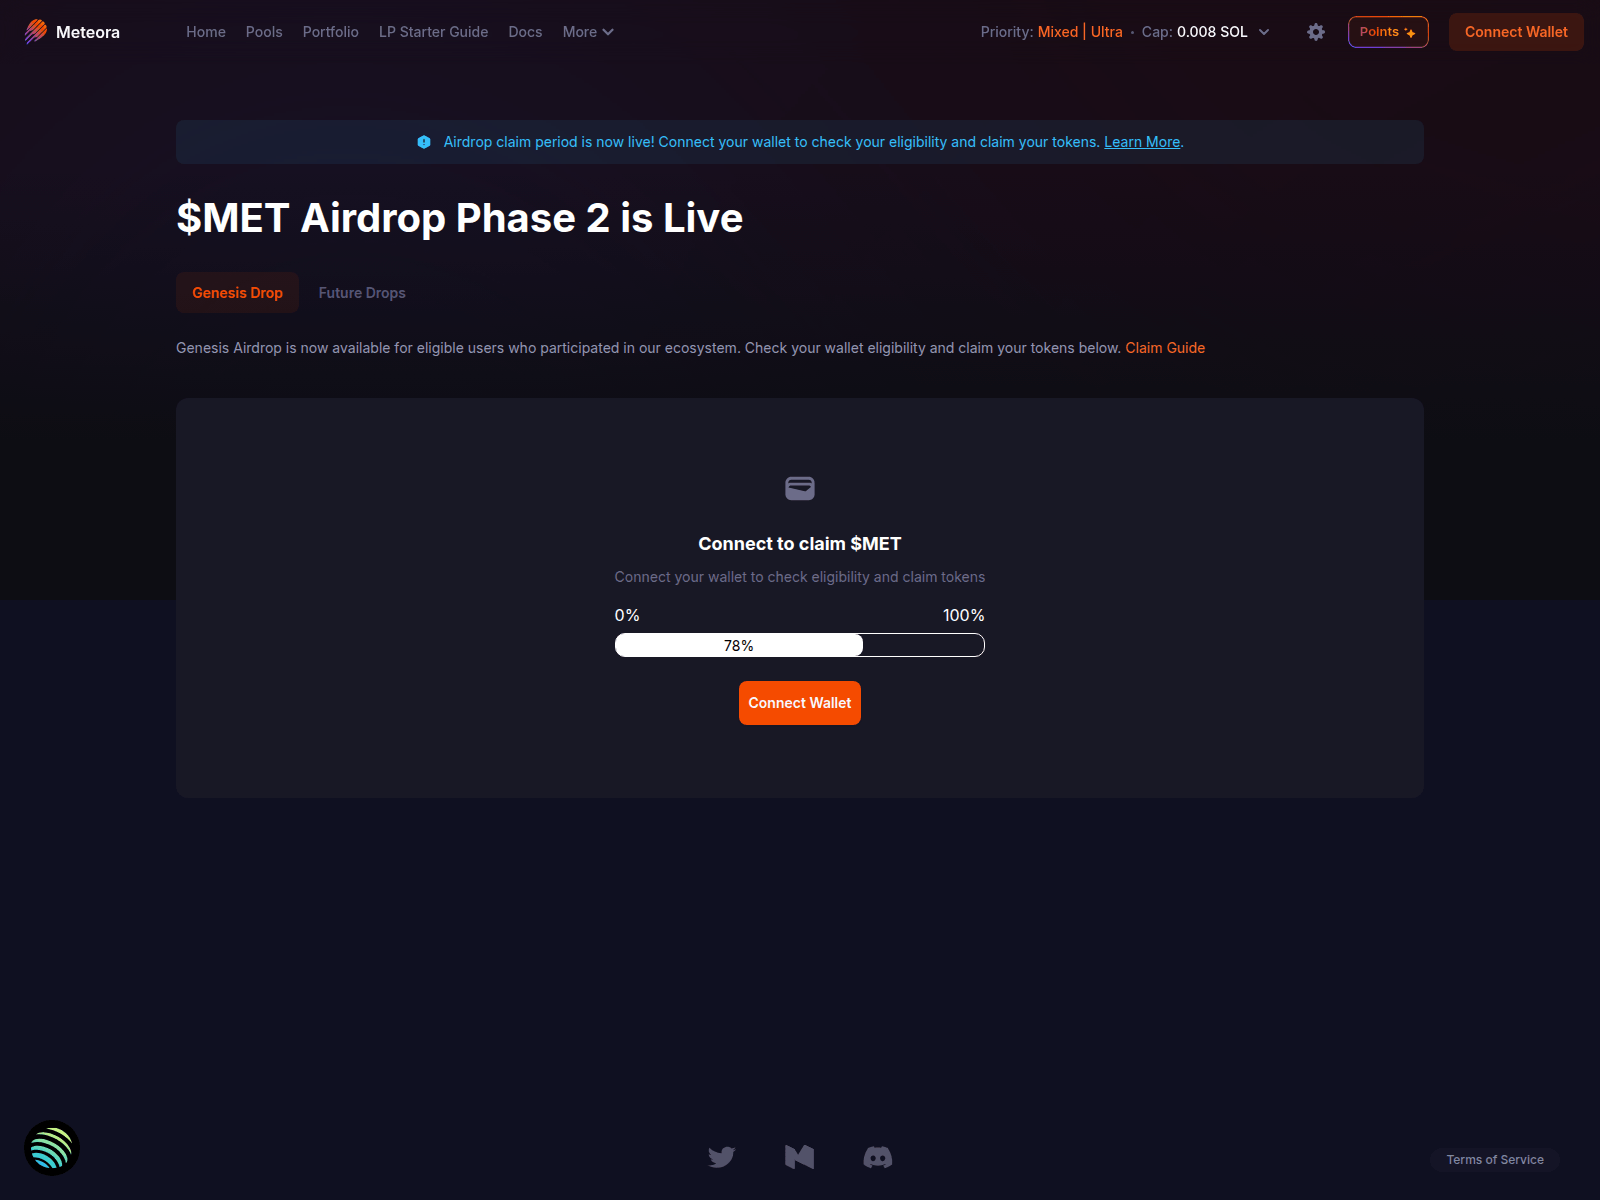
join-met.app
jup-exchange.top
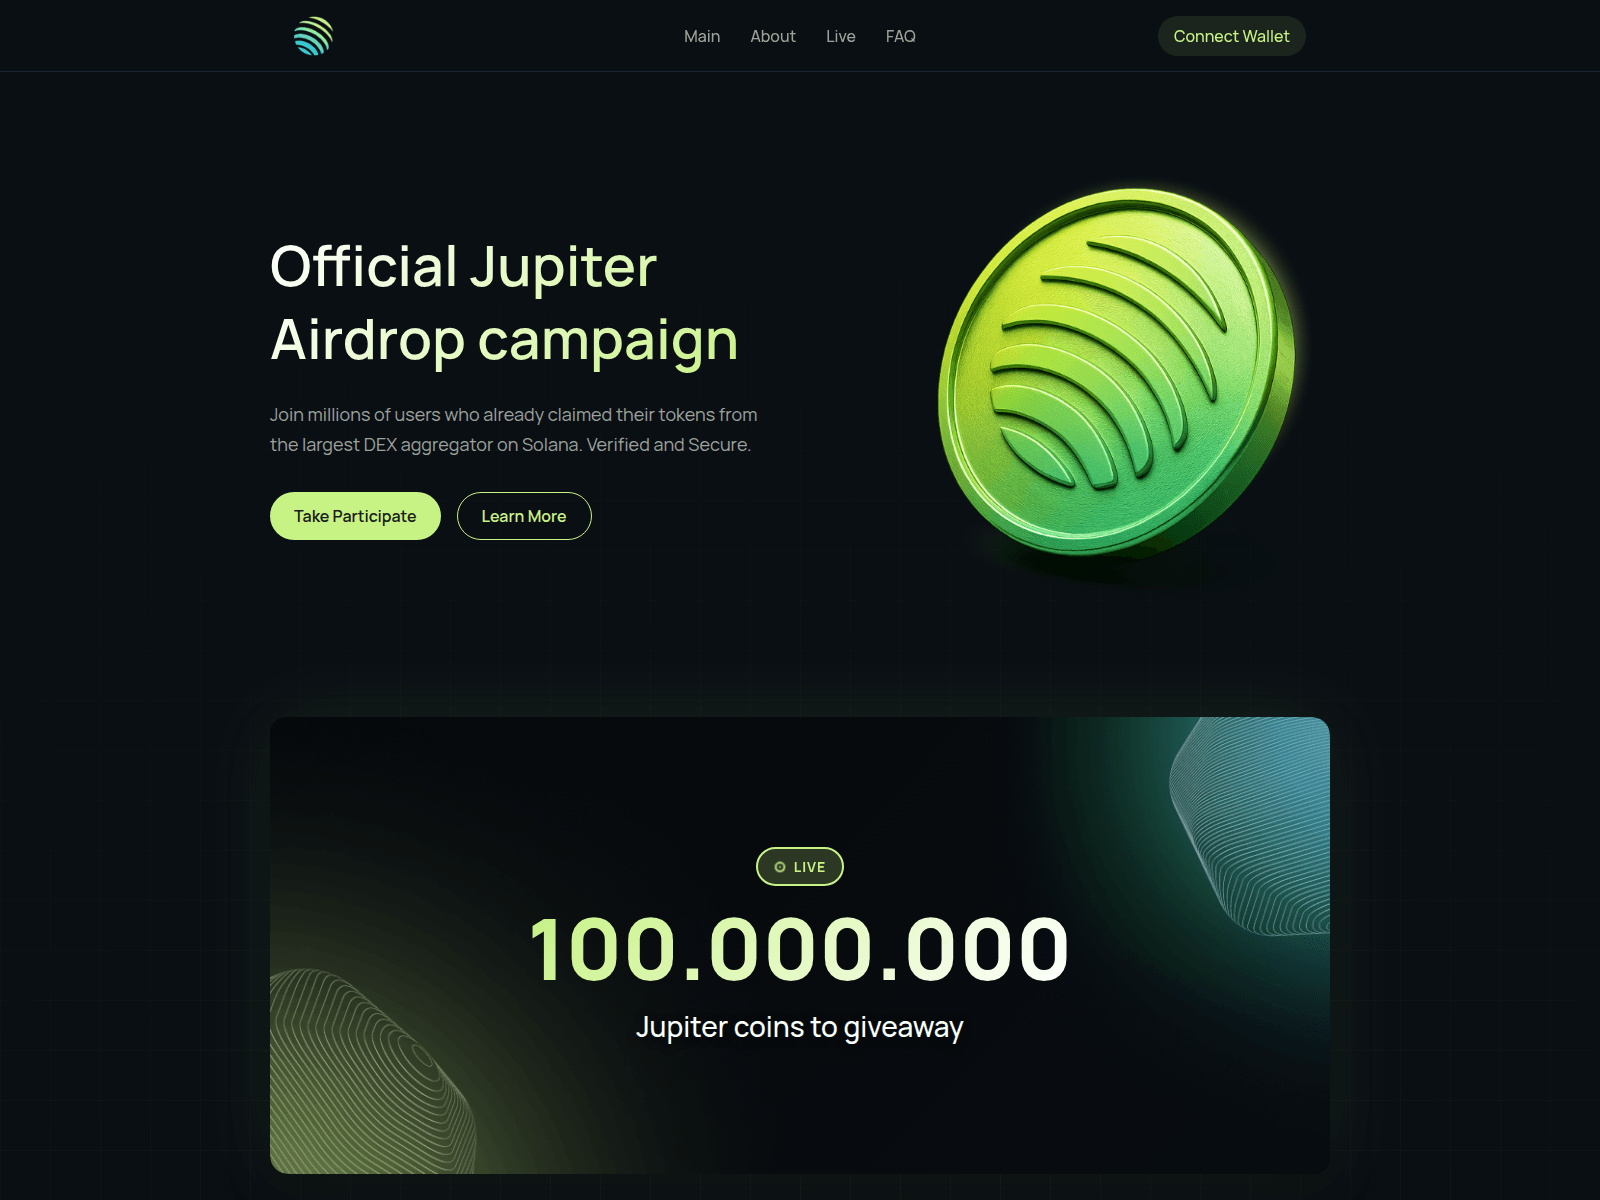
jup-yt.live
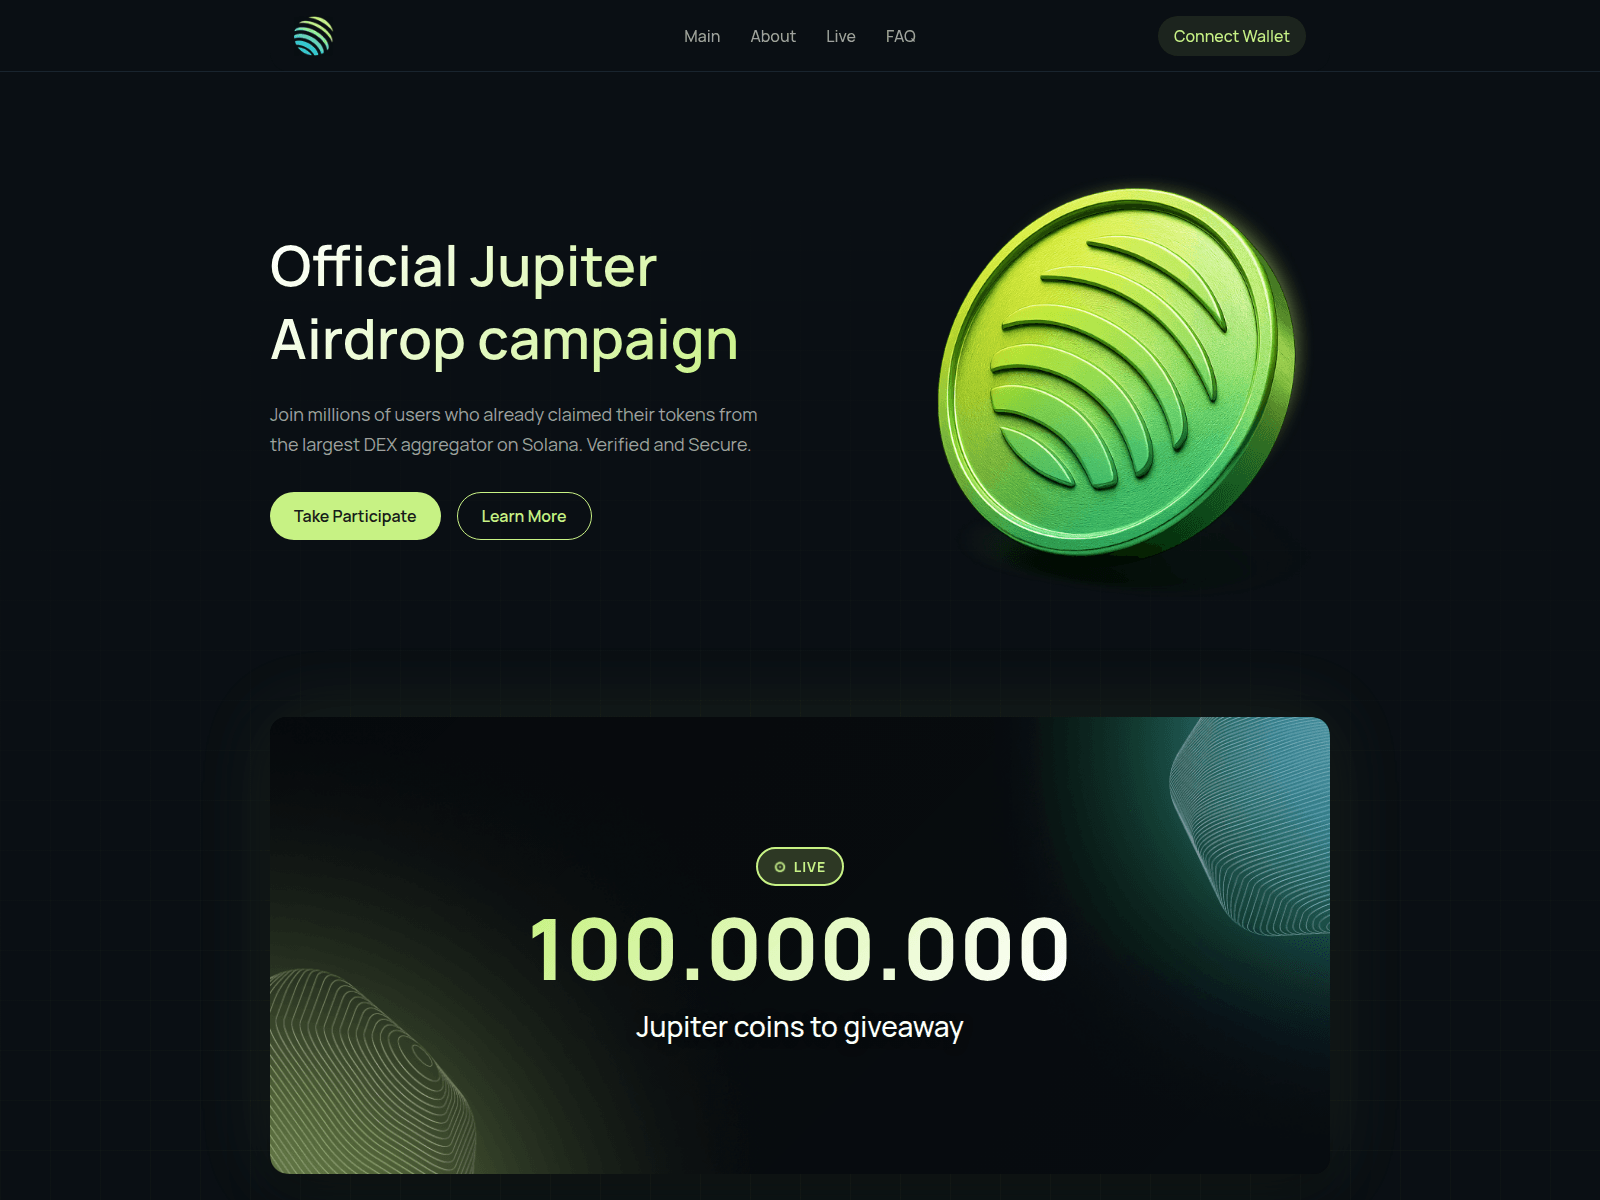
jupiterchecker.us

jupiterdrop.xyz

jweb-baseiinetmx.club

kawaii-airdrop.com

krakenapp.link
lineabuilderscheck.com

lineatoken.top
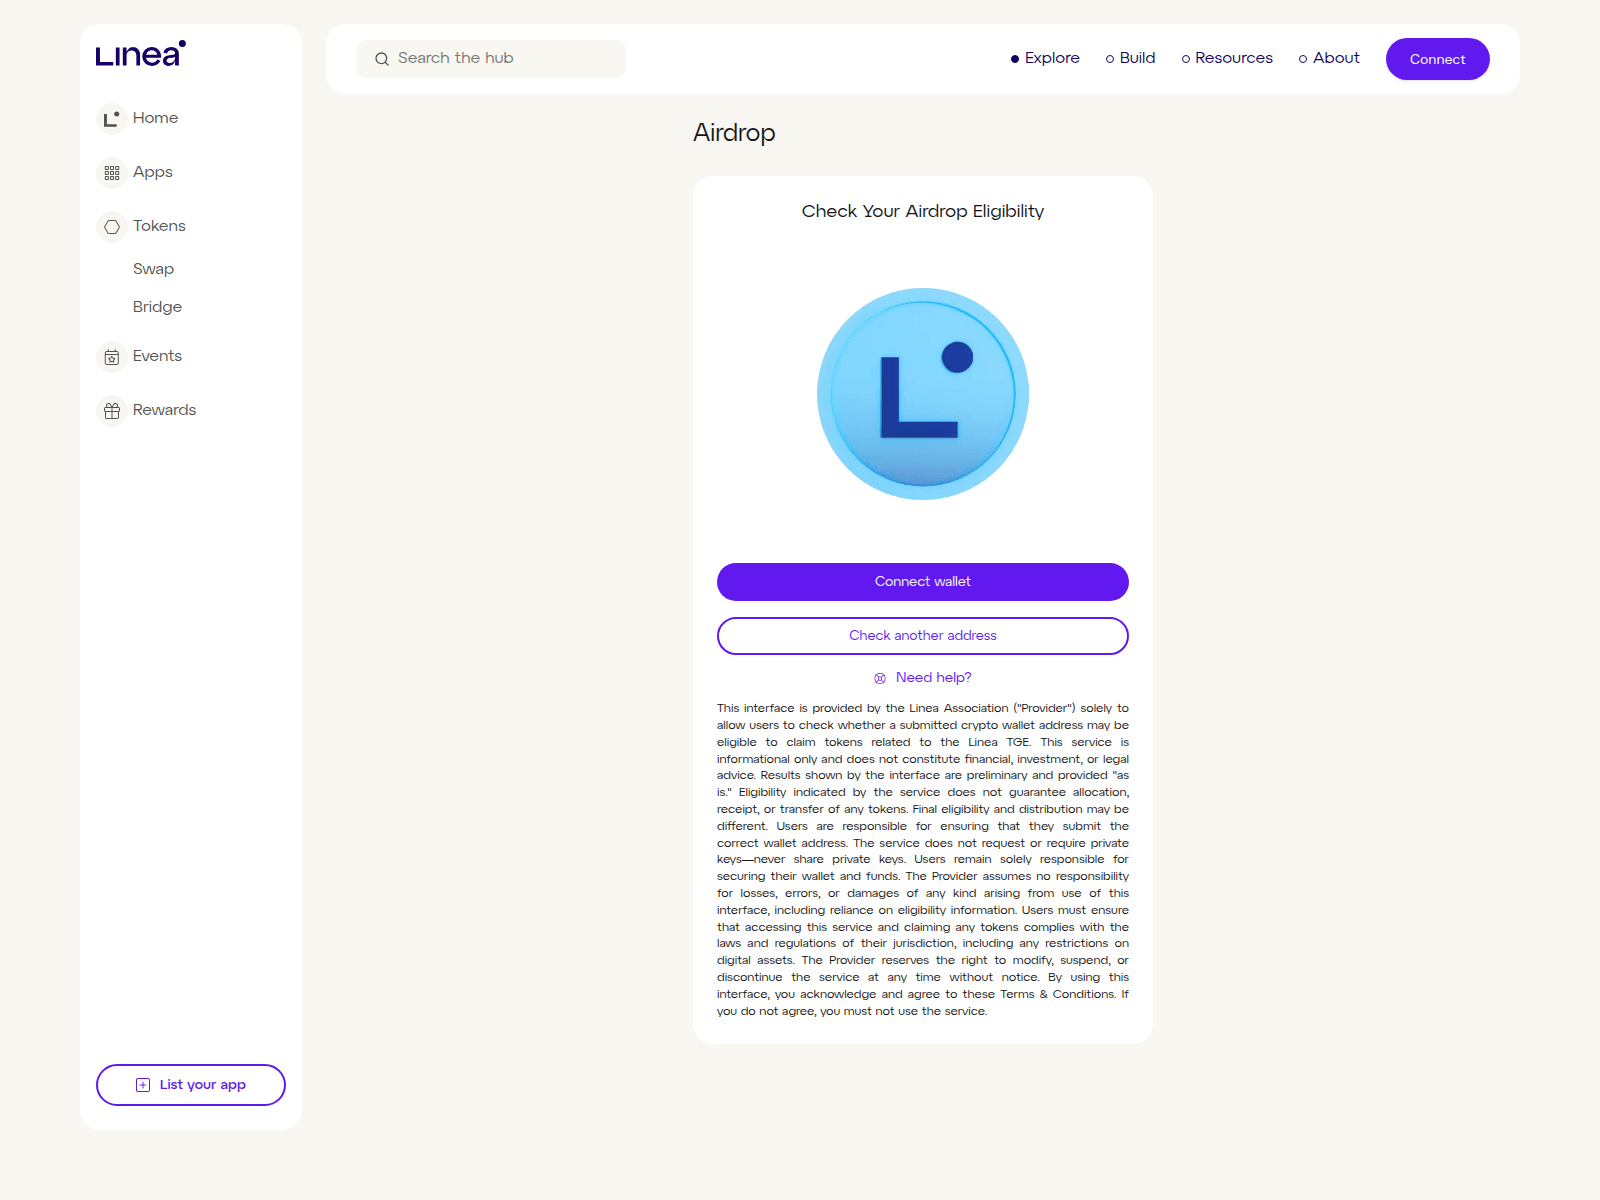
llnea-bluid.me

logatera.work

mask-airdrop.xyz
media.partner-agency-network.com


messenger-one-eta.vercel.app

metamask-dynamic-demo.vercel.app

metamaskpresale.com

mint-nftiff.com

moohshot.top

next-rent-app.vercel.app
nodefisolver.xyz
nodefoundation.airdropsalert.life

okxecn.com

opensea.airdropsalert.life

ouyi.support

playavalon.org
punchtoken.net

quantumsnek.xyz

rbianchi.info

reimagin8d.com
return.solcenter.cc
shares-cashcat.xyz

solana.appscan.pro

solax.cfd
solgoblin.world

ssuperformfoundation.org

stellar-neonode.sbs

supefrormfoundation.org
superfformfoundation.org
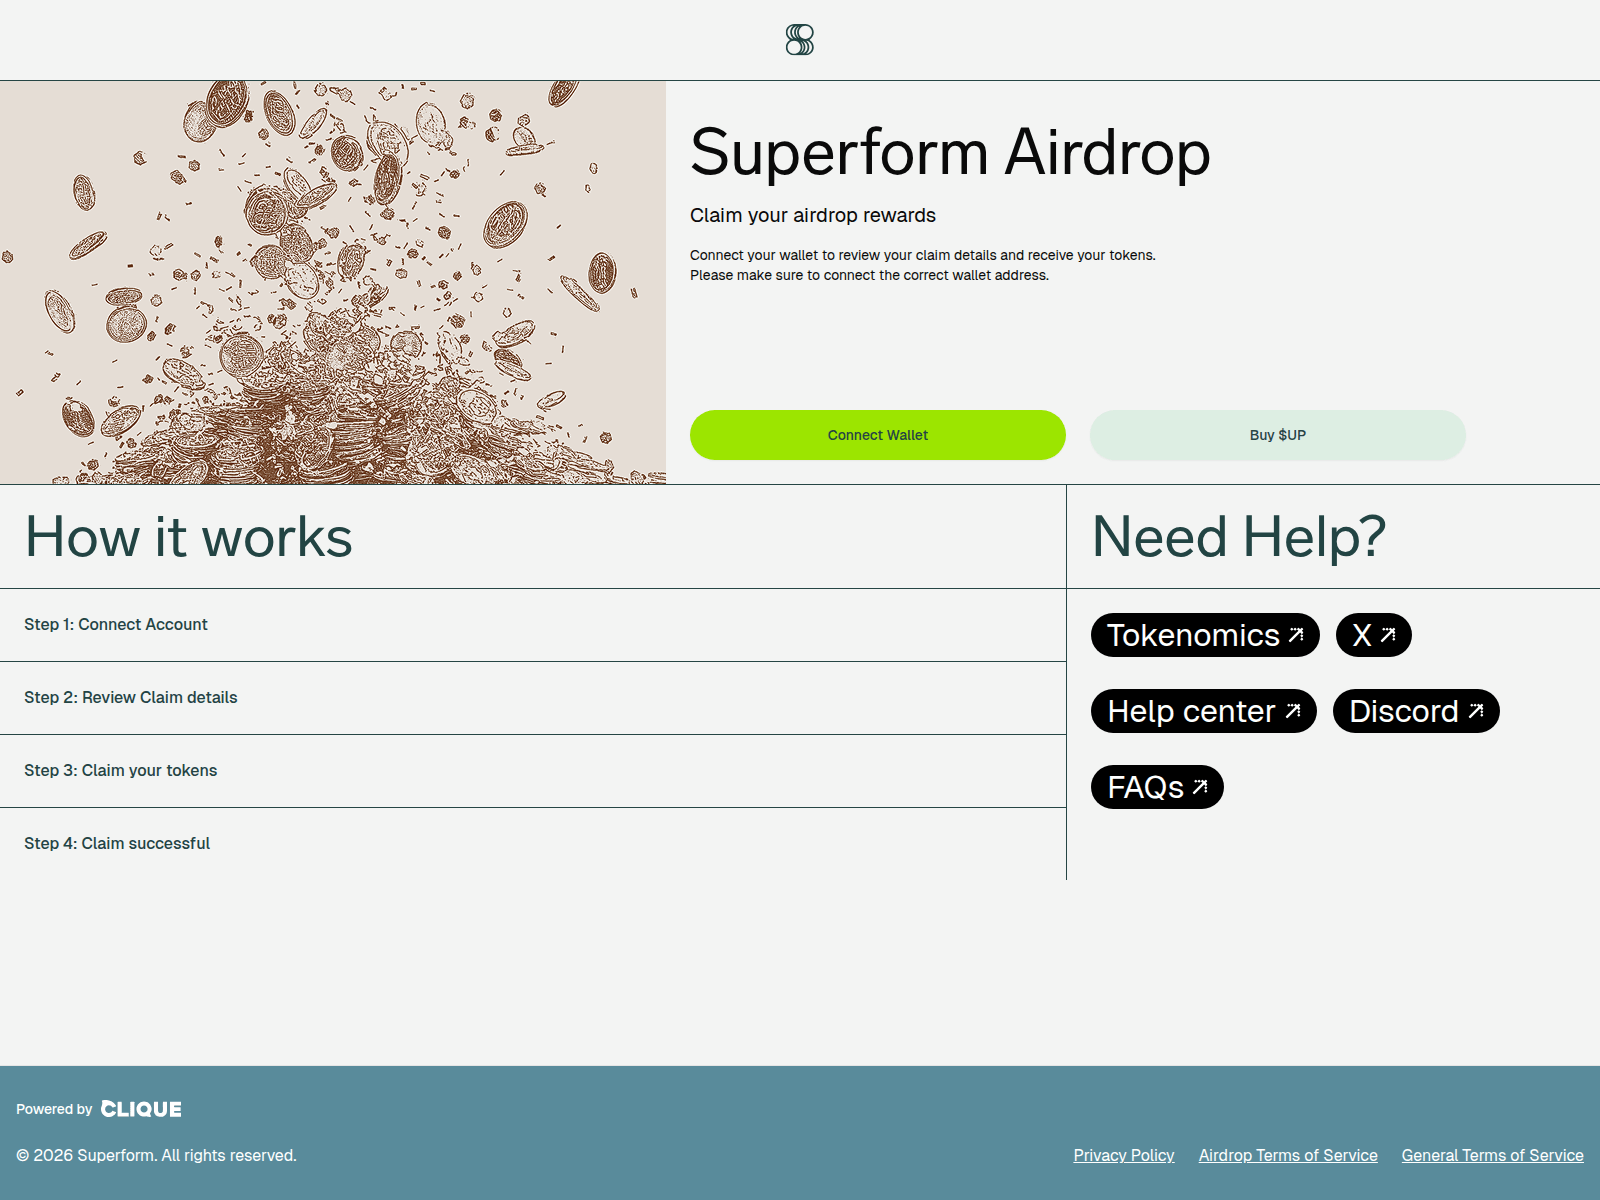
superfomrfoundation.org
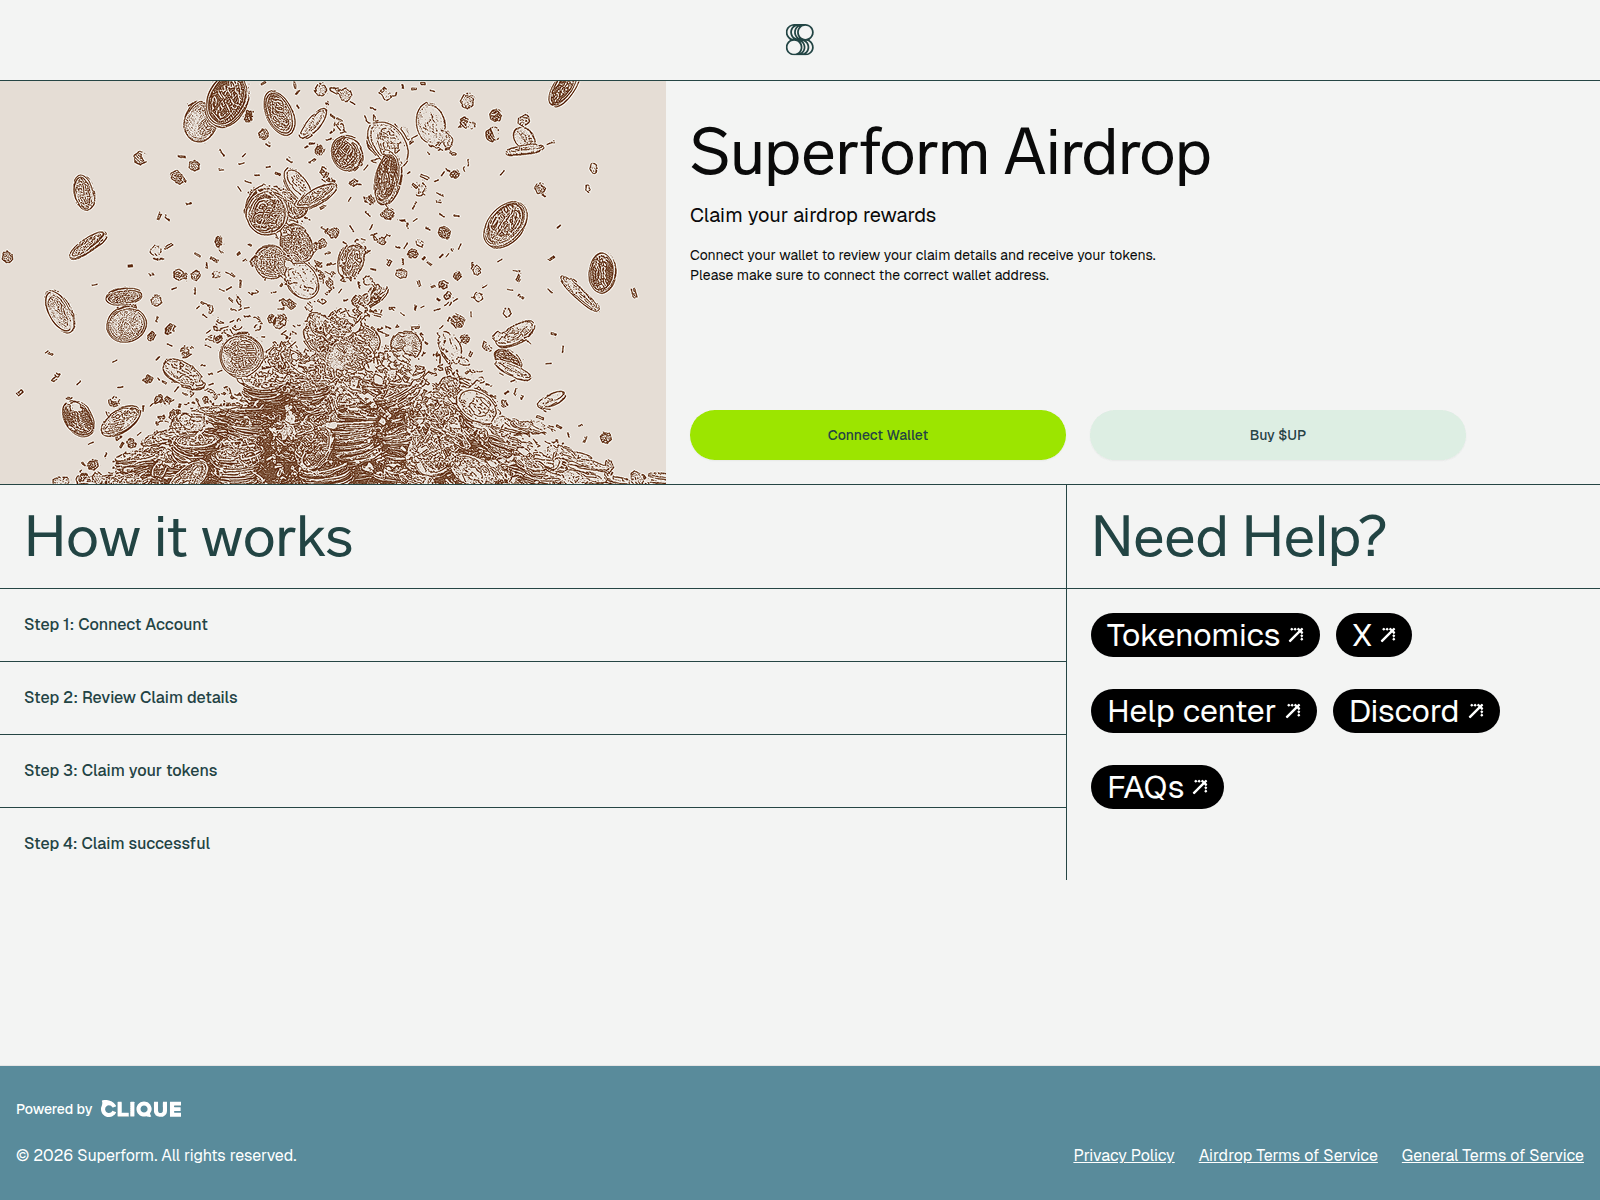
superformfoundatiion.org

superfromfoundation.org

support-coinbase-five.vercel.app

supreformfoundation.org

t-mobile.bocud.cc

t-mobile.csiem.cc

t-mobile.ncvpr.cc

t-mobile.qkfud.cc

tokencitrea.xyz

trustwallet-reward.com

trustwalletcard.app
turtlexyz.airdropsalert.life
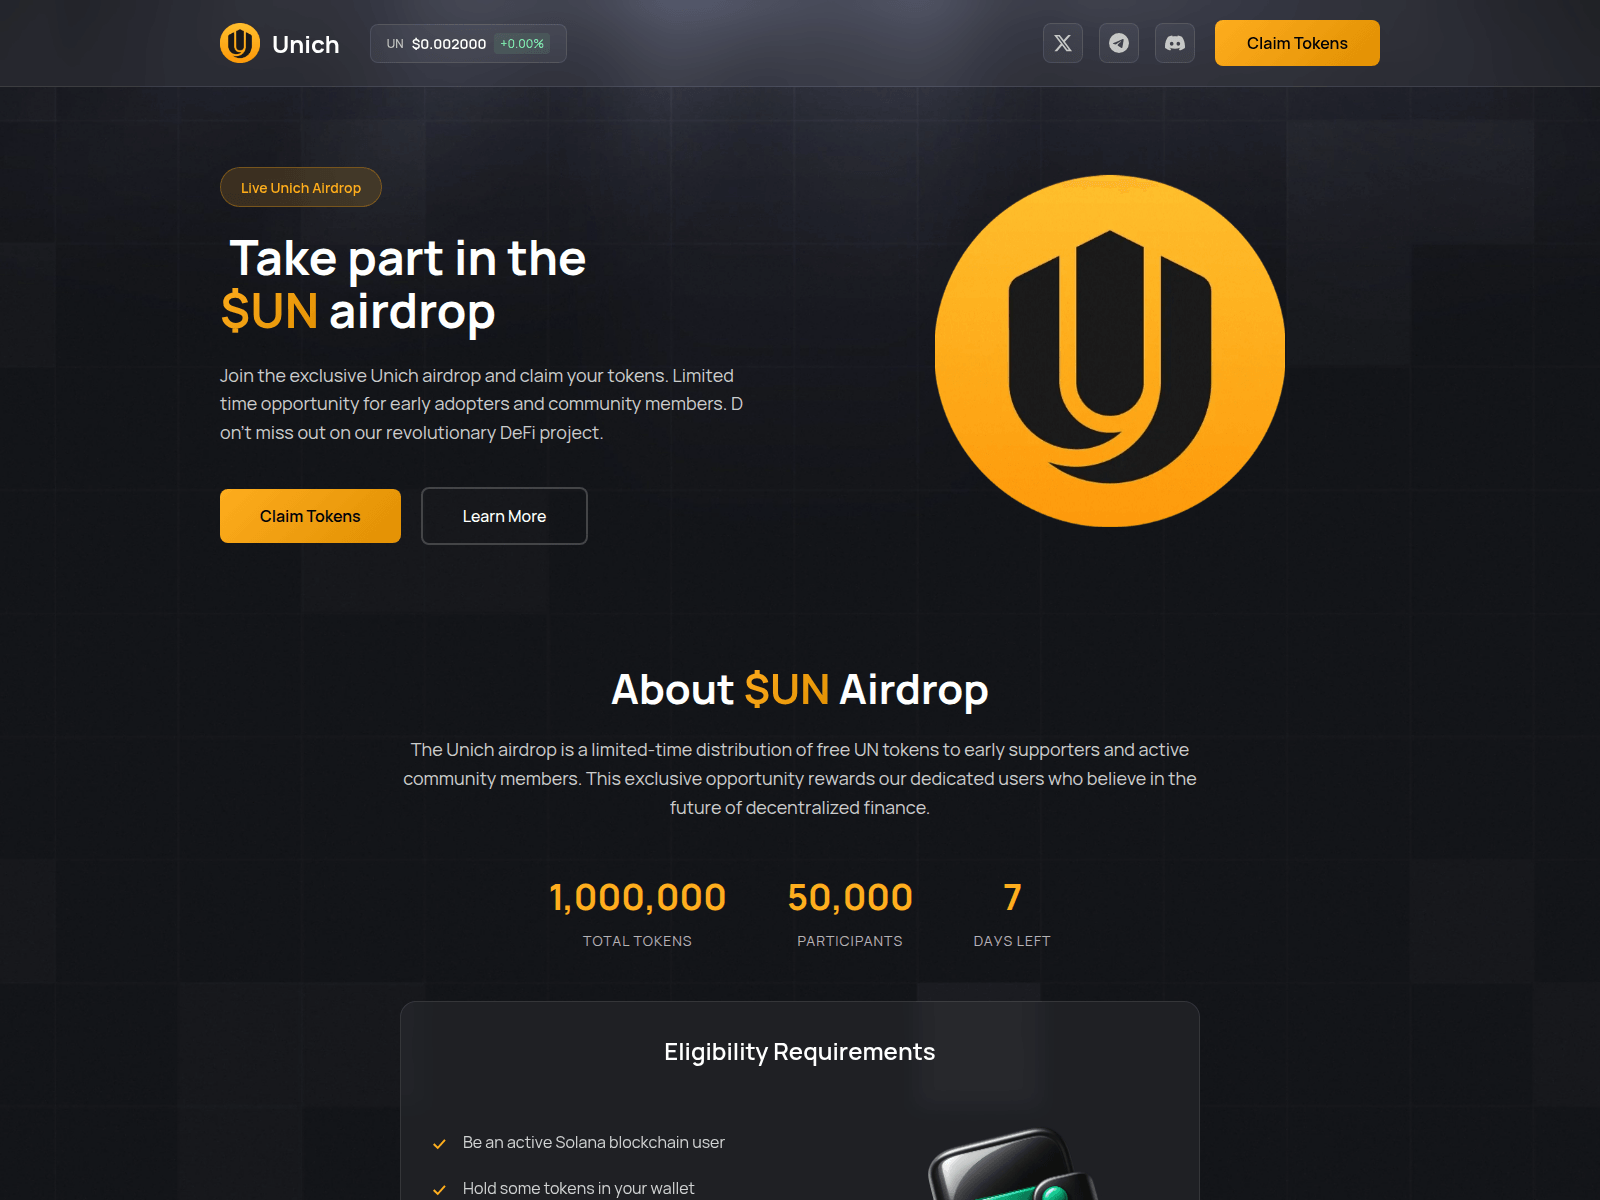
unich-gateway.click

unniswap.com
upholsterychoice.com

vame.be
vvv.airdropsalert.sbs
wallet-app.org

walletconnect.airdropsalert.life
walrus.life

we-tl-t-omj-s1b-qr-ci-sigma.vercel.app

wiseflareenterprise.sbs
wowcoin.bet

ww25.1873483-coinbase.com

ww25.715561-coinbase.com

ww25.876234-coinbase.com

ww25.cdn.195482-coinbase.com

ww25.demo.609410-coinbase.com

www3-vpass-jp.boyanzhixing.com

www3-vpass-jp.lydlnbearing.com

www3-vpass.wardka.com

xrpflarenet.com
yield.airdrpsalerts.click

yieldbasis.airdropsalert.life

zhgwexpouy.net

zircuit.airdropsalert.life
zofai.io.airdropsalert.life

0xpr.top

1drop.click

1drop.digital

abstractchain.airdropsalert.life
airdrop-asterdex.io

airdrop-coin.pages.dev

airdrop-debridge.live
Процес реагування на загрози Pipeline
Як перевіряється кожен домен у цьому хабі та як нейтралізуються підтверджені загрози. Повна візуалізація технологічного процесу →
Перевірки даних про загрози— кожен домен проходить сканування та перехресну перевірку щодо:
urlscan.ioЗнімок екрана · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ЗвітCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Безпека FiltersQuad9 · AdGuard · CleanBrowsingWeb-ПеревіритиFull surface scan
 crt.sh
Глобальна синхронізація постачальників— підтверджені випадки передаються 29 партнерам:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecОгляд сайтуAviraCloud detectionAvast / AVGWeb Shield«Касперський»OpenTIPDr.WebOnline scannerNetcraftЛіквідація APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ЗвітHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust