VirusTotal
11 / 89
Сообщить


“Verafy”
polymarket.verafy.us — Скрытый · достижимый (HTTP 200). Олицетворение бренда: Foundation; Тип мошенничества: Brand Impersonation. Сводка доказательств: VirusTotal 11/89 (BitDefender, CyRadar, ESET, Forcepoint ThreatSeeker, Fortinet); 1 external blocklist match (ScamSniffer); cloaking observed; PhishDestroy score 100/100. Регистратор: OwnRegistrar.
Подробный анализ PhishDestroy AI ниже оставлен на английском, чтобы сохранить исходную криминалистическую запись.

11 / 89
3/14
checked — no match recorded
no community references
Сообщитьprovider verdict: clean
Сообщитьсохраненный отчет
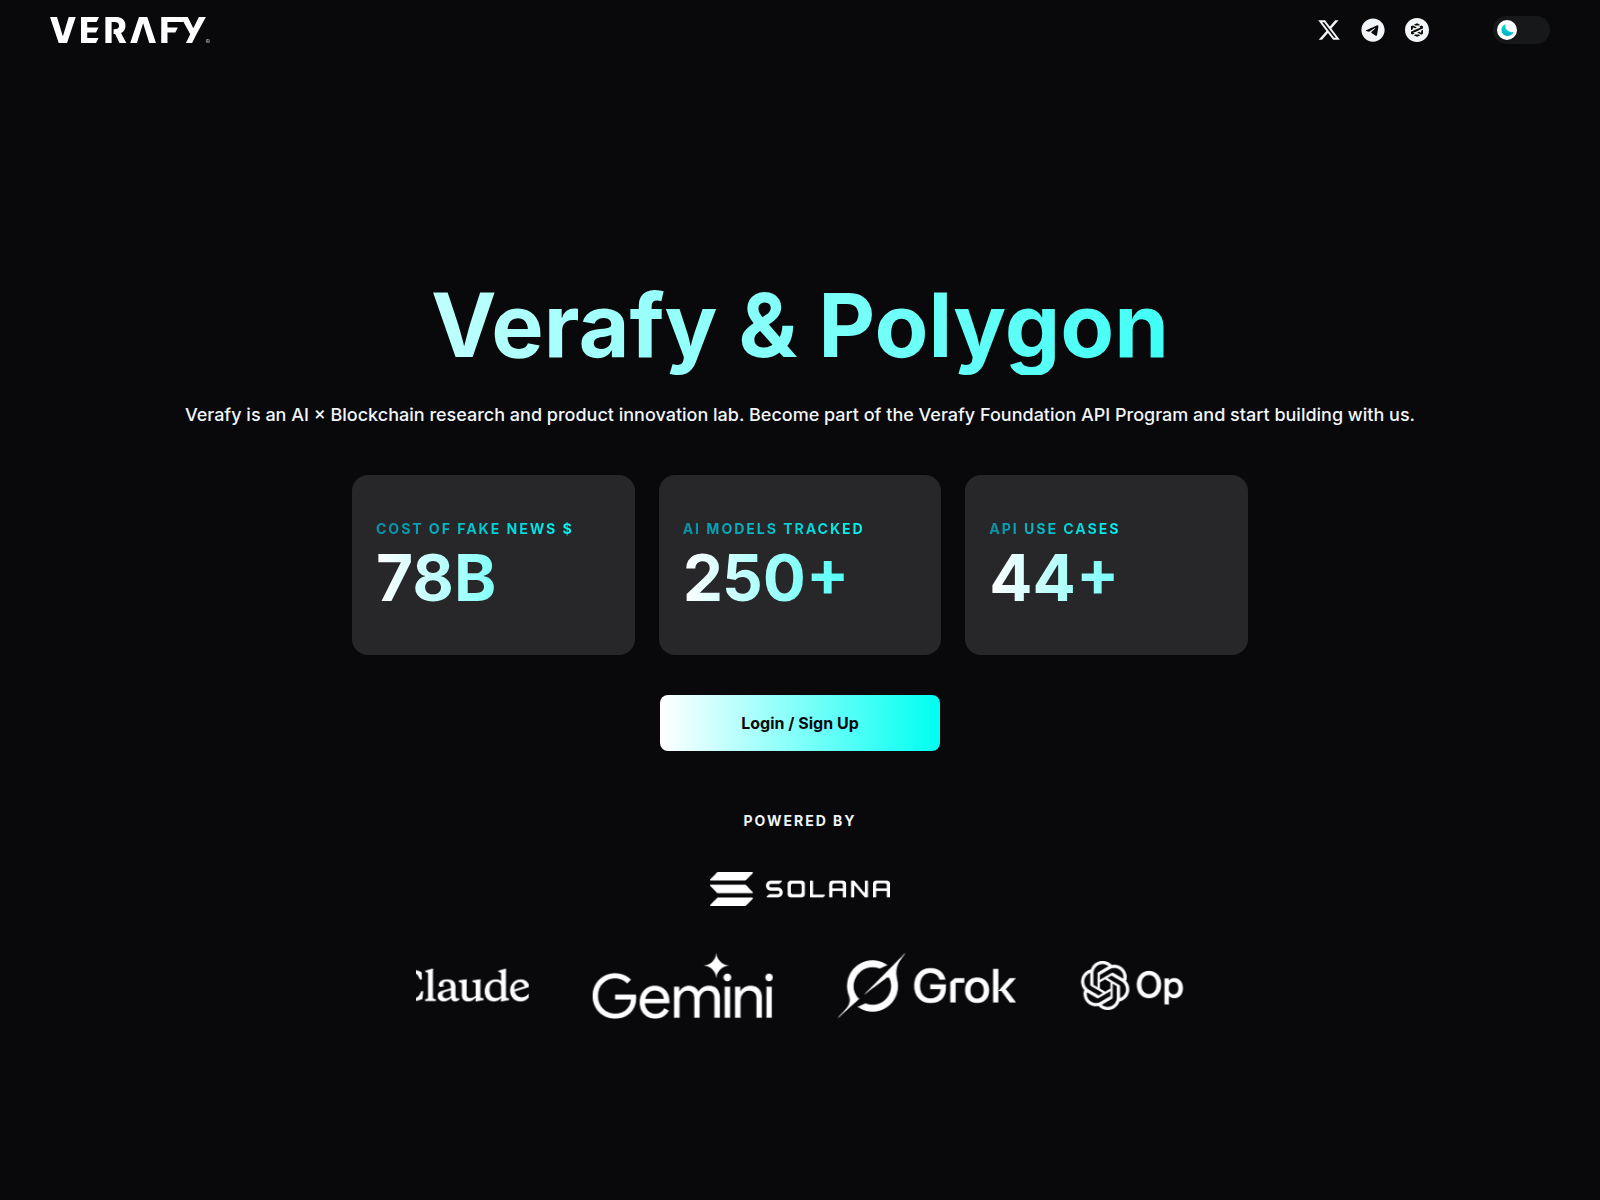 Сообщить
Анализ завершён
СообщитьChecked; no threat flag recorded
СообщитьThis domain is flagged as a high-risk generic phishing threat targeting users through a fraudulent verification portal impersonating Verafy. Analysis indicates the domain is designed to harvest credentials or sensitive information under the guise of a legitimate verification service, leveraging deceptive page titles and infrastructure to appear authentic. Infrastructure analysis reveals the domain polymarket.verafy.us resolves to IP address 188.114.97.3 and is registered through OwnRegistrar, Inc. It was created on May 20, 2026, an anomalous future date suggesting potential registration irregularities or obfuscation tactics. The domain is detected by 14 out of 95 security vendors on VirusTotal, holds a Gridinsoft trust score of 0/100, and appears on three security blocklists (PhishDestroy, ScamSniffer, OISD). Detected technologies include Node.js, Vue.js, Nuxt.js, Cloudflare Browser Insights, and Cloudflare CDN, with HTTP/3 support. The SSL certificate is issued by Let's Encrypt, a common choice for both legitimate and malicious domains. Mitigation steps specific to this threat type include immediate blocking of the domain and its resolving IP (188.114.97.3) at the network perimeter. Security teams should monitor for connections to this IP or domain in logs and proxy data, particularly from endpoints that handle sensitive authentication workflows. User awareness training should emphasize the risks of verification-themed phishing pages, especially those hosted on newly registered or low-reputation domains. Given the use of Cloudflare, analysts should inspect HTTP headers and TLS fingerprints for anomalous patterns. If credentials were entered, reset them immediately and enable multi-factor authentication on all critical accounts.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
https://t.me/verafyaiStored page referenceIoC extraction recorded 2026-07-29 02:02:12 UTC
Страница выдавала один ответ посетителю, действующему как браузер, и другой — поисковому роботу или сканеру безопасности. Маскировка используется исключительно для того, чтобы не допустить рецензентов к реальной целевой странице.
content_divergencecloudflareПримечание к сканированию: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare
 (US)
Репутация Edge-IP не связана с этим доменом.
ali.ns.cloudflare.comnullpiers.ns.cloudflare.comLocation describes the IP network.
f1ee65ded7ce72abeedf875ba3f5cb139c4904c160fb0a2f96944d1fb05e7588verafy.usSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of polymarket.verafy.us · checked Jun 26, 2026
12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Сообщил 1 участник сообщества; впервые замечено 25.05.2026
Если вы ввели учетные данные, личную или платежную информацию или загрузили файл с этого домена, примите немедленные меры. Ниже приведены ресурсы, которые помогут вам сообщить об инциденте и защитить себя.


Выберите свою страну, чтобы получить официальные контакты по киберпреступности или создать проект жалобы →.
Template-based draft · optional AI wording assistance requires separate consent
Каждая полоса — это одна из причин, по которой домен связан с этим хостом. Размер узла обозначает обнаружения VirusTotal, а пунктирные узлы уже находятся в автономном режиме. Полные списки приведены ниже.
Отдельный реестр доказательств для указанного выше домена, подлежащего регистрации: polymarket.verafy.us.
verafy.us 11 VTЭти отчеты относятся к одному и тому же общему граничному IP-адресу. Они помогают при обнаружении отчетов, но не подразумевают совместное владение или общий исходный сервер.
Эти домены также нацелены на пользователей сайта Foundation. Просмотреть все угрозы, связанные с «Foundation» →
Зарегистрированы через одного и того же регистратора. Регистратор обслуживает миллионы клиентов, не связанных друг с другом, поэтому данный факт скорее свидетельствует о сходстве данных, чем доказывает наличие связи.
Недавно добавленные отчёты об угрозах. Эти ссылки не означают общую инфраструктуру или одного владельца.
Анализ угроз с использованием сохраненного черного списка, WHOIS, DNS и общедоступных доказательств сканирования.
Сканировать сейчасДобавляйте подозрительные домены в нашу базу данных угроз — защищайте сообщество
СообщитьНедавние сообщения о фишинге и наблюдаемые изменения доступности
ОтслеживатьОтслеживайте актуальные угрозы или оспорьте эту запись, если считаете, что это ложное срабатывание








