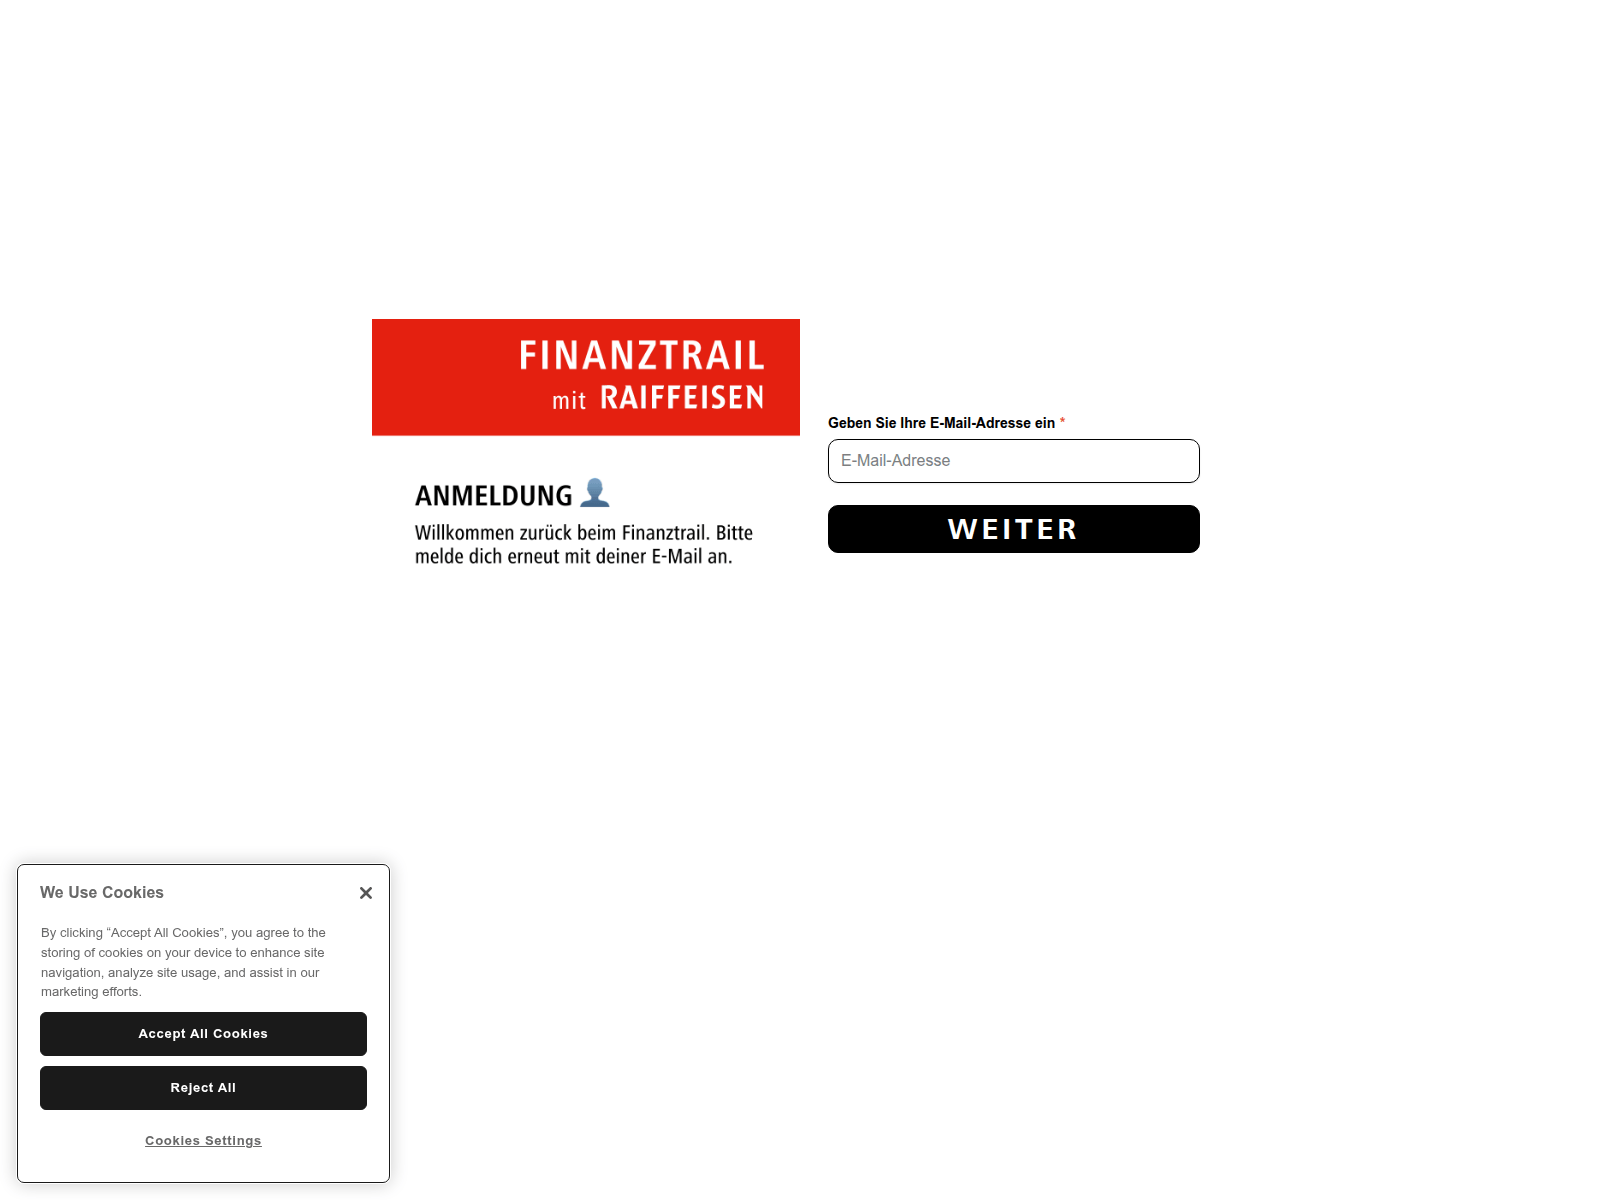
The page presents a "FINANZTRAIL mit RAIFFEISEN" login interface asking visitors to enter an email address before proceeding. Anyone who interacted with this form should immediately change credentials used elsewhere and check for unauthorized account access.
분석 내용은 영어로만 제공됩니다.
페이지 제목: “Viewer”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 15/92 엔진에서 경고했습니다. 악성: 14. 의심: 1. 분석 시간(저장된 표기): 2026-11-21 18:08 UTC. 조회 시간(저장된 표기): 2026-11-21 18:22 UTC. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
URLScan 캡처 · 2026-11-21 17:47 UTC · SHA-256 db2388c9…76087f3
PhishDestroy 분석, 검토 완료된 버전
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Finanztrail login portal layout and interface
The page displays a prominent red header box featuring the text "FINANZTRAIL mit RAIFFEISEN" in white capital letters. Below this header, a section titled "ANMELDUNG" appears alongside a user icon, accompanied by German text stating "Willkommen zurück beim Finanztrail. Bitte melde dich erneut mit deiner E-Mail an." On the right side, an input field is labeled "Geben Sie Ihre E-Mail-Adresse ein" with a placeholder for an email address, followed by a black button marked "WEITER". In the lower-left corner, a cookie consent banner displays options to "Accept All Cookies", "Reject All", and adjust "Cookies Settings". The page specifically asks visitors to input their email address to advance through the login workflow.
Security vendor telemetry and findings
The login form is designed to capture user credentials under the guise of a financial portal. urlscan classified the page as malicious, VirusTotal showed 15 of 92 engines flagging it on 21 Nov 2026, and OpenPhish blocks it, including Kaspersky, ESET and Fortinet. Its PhishDestroy evidence score is 75/100 (critical), so this domain operates as an active data-collection trap rather than a benign service.
Credential harvesting risks and precautions
Entering an email address into this unauthorized form exposes the visitor to follow-up phishing attempts or credential stuffing attacks. Because the address still answered requests on 21 Nov 2026 at 18:48 UTC, the capture mechanism remains live. Visitors who submitted details should treat their credentials as compromised, update passwords on related accounts, and monitor financial statements closely.
raiffeisenswitzerland.smartmediawallet.app hosted a fake Finanztrail login requesting email details, and is flagged by urlscan and 15 VirusTotal engines.
AI 요약
Finanztrail login portal layout and interface The page displays a prominent red header box featuring the text "FINANZTRAIL mit RAIFFEISEN" in white capital letters. Below this header, a section titled "ANMELDUNG" appears alongside a user icon, accompanied by German text stating "Willkommen zurück beim Finanztrail. Bitte melde dich erneut mit deiner E-Mail an." On the right side, an input field is labeled "Geben Sie Ihre E-Mail-Adresse ein" with a placeholder for an email address, followed by a black button marked "WEITER". In the lower-left corner, a cookie consent banner displays options to "Accept All Cookies", "Reject All", and adjust "Cookies Settings". The page specifically asks visitors to input their email address to advance through the login workflow. Security vendor telemetry and findings The login form is designed to capture user credentials under the guise of a financial portal. urlscan classified the page as malicious, VirusTotal showed 15 of 92 engines flagging it on 21 Nov 2026, and OpenPhish blocks it, including Kaspersky, ESET and Fortinet. Its PhishDestroy evidence score is 75/100 (critical), so this domain operates as an active data-collection trap rather than a benign service. Credential harvesting risks and precautions Entering an email address into this unauthorized form exposes the visitor to follow-up phishing attempts or credential stuffing attacks. Because the address still answered requests on 21 Nov 2026 at 18:48 UTC, the capture mechanism remains live. Visitors who submitted details should treat their credentials as compromised, update passwords on related accounts, and monitor financial statements closely.
Headers: Server: AmazonS3; Content type: text/html; Strict transport security: max-age=31536000; Content security policy: default-src 'self' ;img-src 'self' https://* data: blob: ;media-src 'self' https://* ;connect-src 'self' blob: data: https://api.vl.vatom.network wss://ws.vatomviewer.com https://*.smartmedialabs.io https://*.google-analytics.com https://*.mapbox.com https://*.8thwall.com https://geoip.blockv.io htt; X frame options: SAMEORIGIN; X content type options: nosniff; Referrer policy: strict-origin-when-cross-origin; Via: 1.1 b6be6ee8d445cfa291adcacd75a3fb12.cloudfront.net (CloudFront); X cache: RefreshHit from cloudfront
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
피싱 피싱 Security threats
raiffeisenswitzerland.smartmediawallet.app 관련 질문
raiffeisenswitzerland.smartmediawallet.app은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 raiffeisenswitzerland.smartmediawallet.app를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-11-21에 처음 기록되었습니다. 저장된 VirusTotal 결과: 15/92 엔진에서 경고했습니다. 악성: 14. 의심: 1. 분석 시간(저장된 표기): 2026-11-21 18:08 UTC. 조회 시간(저장된 표기): 2026-11-21 18:22 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.

 GoDaddy
 18.239.69.111


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT