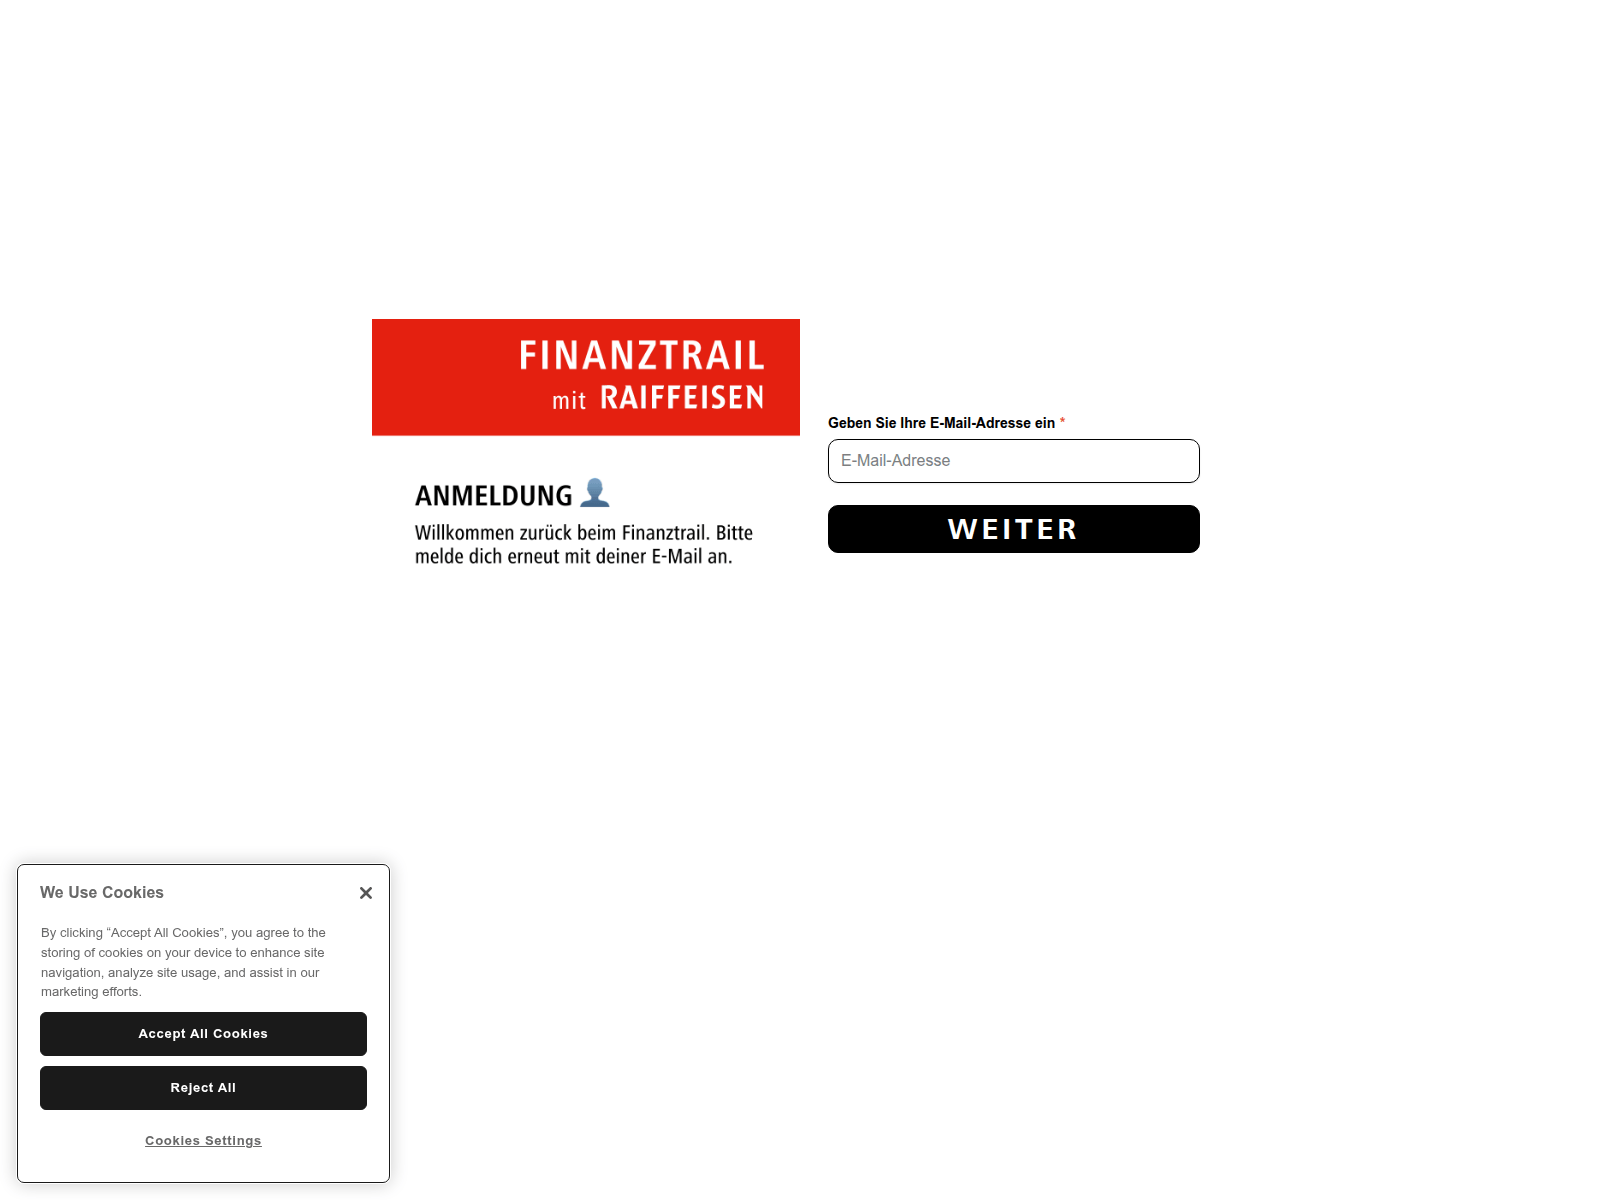
The page presents a "FINANZTRAIL mit RAIFFEISEN" login interface asking visitors to enter an email address before proceeding. Anyone who interacted with this form should immediately change credentials used elsewhere and check for unauthorized account access.
URLScan截图 · 2026-11-21 17:47 UTC · SHA-256 db2388c9…76087f3
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Finanztrail login portal layout and interface
The page displays a prominent red header box featuring the text "FINANZTRAIL mit RAIFFEISEN" in white capital letters. Below this header, a section titled "ANMELDUNG" appears alongside a user icon, accompanied by German text stating "Willkommen zurück beim Finanztrail. Bitte melde dich erneut mit deiner E-Mail an." On the right side, an input field is labeled "Geben Sie Ihre E-Mail-Adresse ein" with a placeholder for an email address, followed by a black button marked "WEITER". In the lower-left corner, a cookie consent banner displays options to "Accept All Cookies", "Reject All", and adjust "Cookies Settings". The page specifically asks visitors to input their email address to advance through the login workflow.
Security vendor telemetry and findings
The login form is designed to capture user credentials under the guise of a financial portal. urlscan classified the page as malicious, VirusTotal showed 15 of 92 engines flagging it on 21 Nov 2026, and OpenPhish blocks it, including Kaspersky, ESET and Fortinet. Its PhishDestroy evidence score is 75/100 (critical), so this domain operates as an active data-collection trap rather than a benign service.
Credential harvesting risks and precautions
Entering an email address into this unauthorized form exposes the visitor to follow-up phishing attempts or credential stuffing attacks. Because the address still answered requests on 21 Nov 2026 at 18:48 UTC, the capture mechanism remains live. Visitors who submitted details should treat their credentials as compromised, update passwords on related accounts, and monitor financial statements closely.
raiffeisenswitzerland.smartmediawallet.app hosted a fake Finanztrail login requesting email details, and is flagged by urlscan and 15 VirusTotal engines.
AI摘要
Finanztrail login portal layout and interface The page displays a prominent red header box featuring the text "FINANZTRAIL mit RAIFFEISEN" in white capital letters. Below this header, a section titled "ANMELDUNG" appears alongside a user icon, accompanied by German text stating "Willkommen zurück beim Finanztrail. Bitte melde dich erneut mit deiner E-Mail an." On the right side, an input field is labeled "Geben Sie Ihre E-Mail-Adresse ein" with a placeholder for an email address, followed by a black button marked "WEITER". In the lower-left corner, a cookie consent banner displays options to "Accept All Cookies", "Reject All", and adjust "Cookies Settings". The page specifically asks visitors to input their email address to advance through the login workflow. Security vendor telemetry and findings The login form is designed to capture user credentials under the guise of a financial portal. urlscan classified the page as malicious, VirusTotal showed 15 of 92 engines flagging it on 21 Nov 2026, and OpenPhish blocks it, including Kaspersky, ESET and Fortinet. Its PhishDestroy evidence score is 75/100 (critical), so this domain operates as an active data-collection trap rather than a benign service. Credential harvesting risks and precautions Entering an email address into this unauthorized form exposes the visitor to follow-up phishing attempts or credential stuffing attacks. Because the address still answered requests on 21 Nov 2026 at 18:48 UTC, the capture mechanism remains live. Visitors who submitted details should treat their credentials as compromised, update passwords on related accounts, and monitor financial statements closely.

 GoDaddy
 18.239.69.111


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT