보안 보고서로 이동
도메인 보안 및 위협 인텔리전스
catfee.energy favicon

catfee.energy

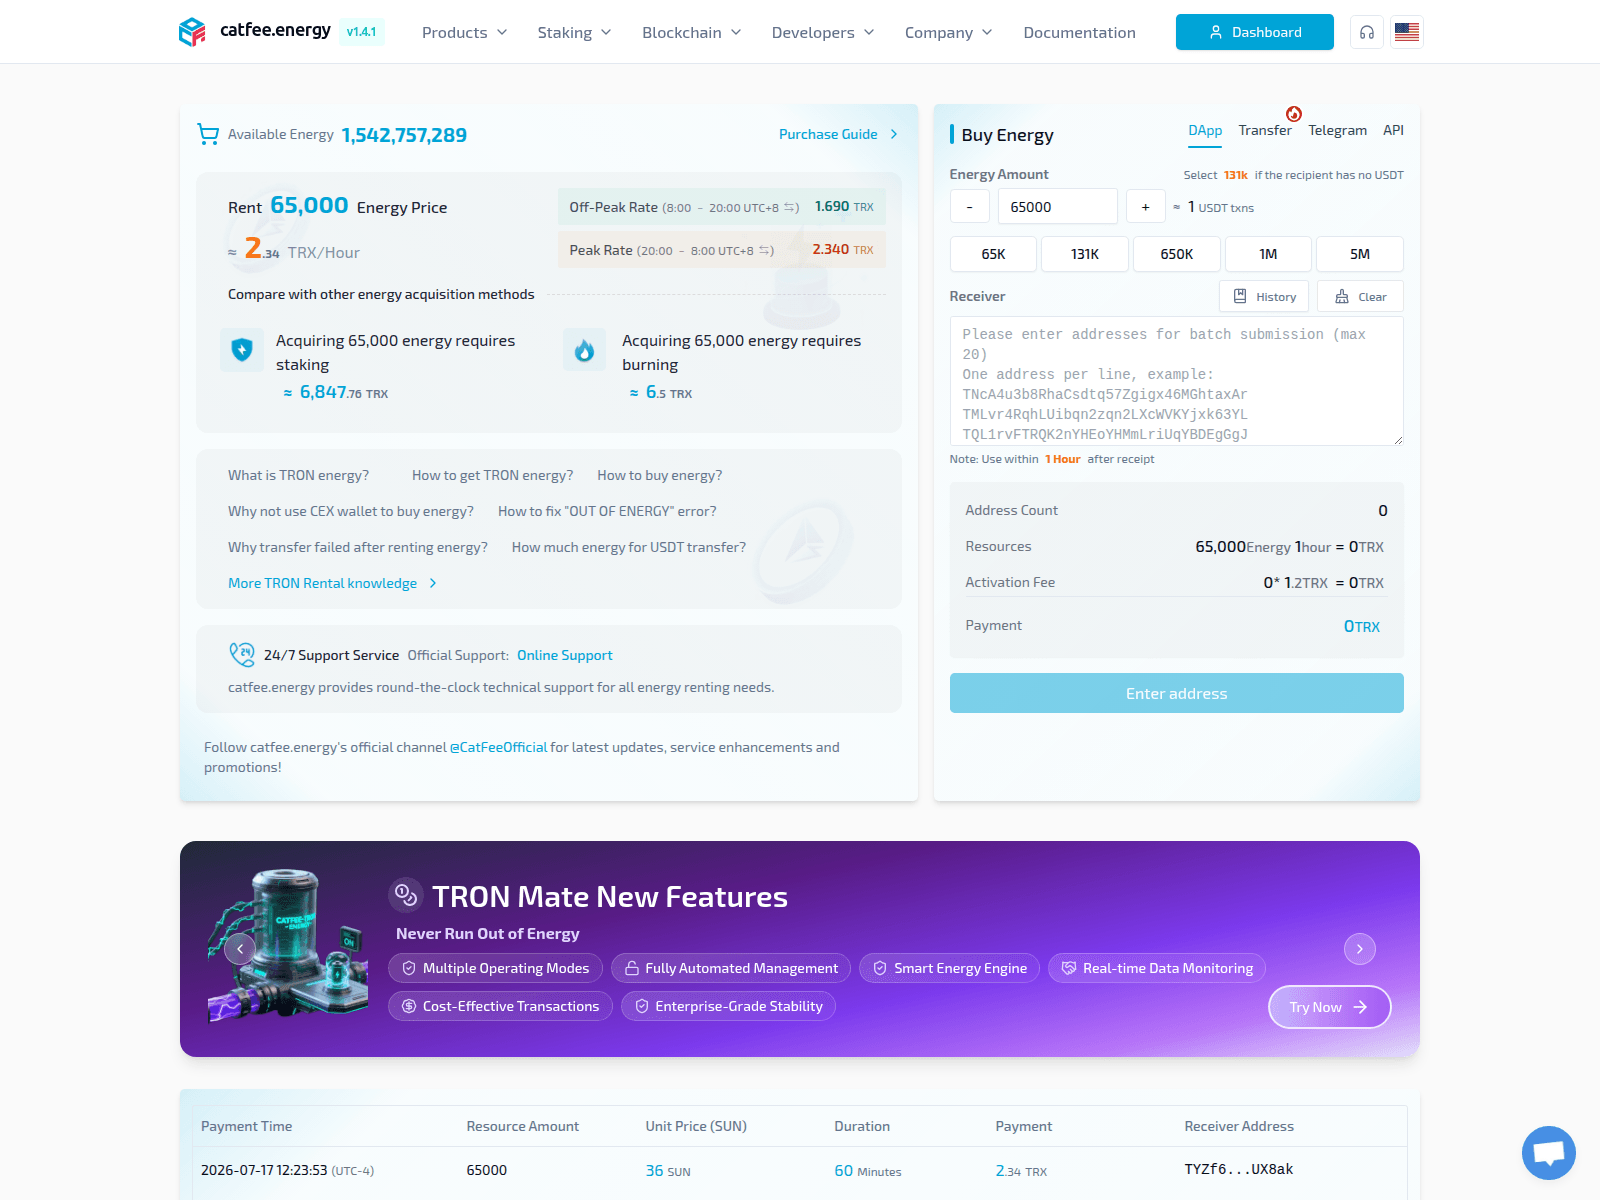
“Buy and Sell TRON Energy | Rent TRX Energy | CatFee”

등록기관
GNAME.COM
Resolved IP
186.2.175.25
Registered
2026년 7월 17일
위협 평결 심각
가용성 마지막으로 알려진 활성 최근에 저장된 도달 가능성 관찰 관측됨
Source: HTTP probe
VirusTotal 탐지: 11/89 Spamhaus DBL: DBL_PHISH 저장된 차단 목록 일치 항목: 2 브랜드 사칭: Binance
OTX: 4 refs 2026년 8월 4일 Binance 1 Report Sent
API
이 도메인은 악성 도메인으로 표시되었습니다.
탐지를 보고하는 보안 엔진: 11. 일치를 보고하는 공개 차단 목록: 2. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is complaint@gname.com. The latest stored availability evidence still shows the domain reachable; 2 months has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
2 months
Reports sent
1
Latest case ID
PD-20260804-8C56C5
Current status
HTTP 200 at latest stored check
보고서 요약

catfee.energy — 마지막으로 알려진 활성 (HTTP 200). 브랜드 사칭: Binance; 사기 유형: Crypto Drainer. 증거 요약: VirusTotal 11/89 (alphaMountain.ai, BitDefender, CRDF, CyRadar, Forcepoint ThreatSeeker); Spamhaus DBL_PHISH; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 100/100. 등록기관: GNAME.COM.

원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.

Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
11 det.
OTX references
URLScan
URLScan
ScamAdviser
Scamadviser
80/100Likely Safe
TLS 인증서
만료되었거나 검증되지 않음
연령
3 mo New
관측 상태
마지막으로 알려진 활성 200
PhishDestroy
DestroyList
등재됨
Reports Sent
1

Source evidence

9 sources

VirusTotal

11 / 89

보고서

Spamhaus DBL

DBL_PHISH

URLQuery

checked — no detections recorded

보고서

OTX

4 community references

보고서

CF 레이더

provider verdict: clean

보고서

URLScan capture

저장된 보고서

Stored URLScan capture preview
보고서

URLScan verdict

분석 완료

보고서

Google Safe Browsing

Checked; no threat flag recorded

보고서

증거 요약

심각
VirusTotal
11/89
OTX
4 community refs
URLScan
Stored capture

Analysis of the domain catfee.energy, observed on August 04 2026, shows limited public intelligence but several indicators of compromise. The domain was submitted to VirusTotal where 91 scanning engines examined the site; none reported a detection at the time of analysis. While a clean result might suggest an absence of known malware signatures, the lack of detections does not constitute evidence of legitimacy, especially given the domain’s appearance on a security blocklist. The blocklist entry is corroborated by PhishDestroy, which has actively blocked catfee.energy and classified it as a phishing resource.

No additional data such as registrar details, hosting IP, SSL certificate information, HTTP response codes, or page‑title metadata are currently available in the intelligence feed. Consequently, the infrastructure behind the domain remains opaque, and the specific brand or service being spoofed cannot be identified from the existing artifacts. Defenders should treat catfee.energy as a high‑confidence malicious indicator. Immediate mitigation steps include adding the domain to outbound and inbound deny lists across firewalls, proxy servers, and DNS filtering solutions.

Security information and event management (SIEM) rules should be updated to flag any DNS queries, HTTP requests, or email links containing the domain. Continuous monitoring of threat‑intel feeds for new indicators—such as IP address associations, SSL certificate changes, or emerging blocklist entries—will help refine detection capability. Because the domain has already been flagged by PhishDestroy, organizations employing that service will benefit from automatic blocking, but independent controls remain advisable. Until further forensic evidence is gathered, the recommendation is to maintain a strict deny‑list posture for catfee.energy and to educate end‑users about unsolicited communications that might reference the domain.

Extracted from stored page analysis

Observed indicators

3 wallet · 0 Telegram

Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.

TRX
TMLvr4RqhLUibqn2zqn2LXcWVKYjxk63YLFormat validated · Domain analysis
TRX
TNcA4u3b8RhaCsdtq57Zgigx46MGhtaxArFormat validated · Domain analysis
TRX
TQL1rvFTRQK2nYHEoYHMmLriUqYBDEgGgJFormat validated · Domain analysis

IoC extraction recorded 2026-08-04 04:00:12 UTC

탐지 회피 분석

클로킹 및 트래픽 분산 점검

아직 스캔되지 않았습니다 크롤러와 브라우저 간의 차이는 아직 보고된 바가 없습니다.

이 호스트에 대해 저장된 크롤러 대 브라우저 관측 데이터와, 케이타로 스타일의 트래픽 분배 시스템을 위한 실시간 지문 확인 정보.

저장된 은신 플래그
아직 스캔되지 않았습니다
마지막 은폐 스캔
스캐너가 감지한 서버 헤더
ddos-guard

스캐너 메모: alive_content: raw=ok; http=200; via=https_proxy; server=ddos-guard

TDS 지문 인식 실시간 확인
이 패널이 열려 있을 때 PhishDestroy 스캐너에서 실행되는 7개의 케이타로 지문과 크롤러 대 브라우저 비교 결과.
기다림

저장된 캡처 · 3 captures

페이지 제목
Buy and Sell TRON Energy | Rent TRX Energy | CatFee
Impersonates
Binance Bitget Bybit Ledger OKX Telegram Tron Trust Wallet +1
TLS 인증서
Hostname coverage not recorded · 발급자 Let's Encrypt · stored validity ends in 72 days

Domain details

도메인
URLScan Verdict 분석 완료 score 0 report ↗
IP 평판 abuse score 2/100 2 reports PhishingOpen ProxyVPN IP checked 2026년 10월 3일
OTX Tags 2026-08activeall-domainsblocklistcontentcrypto도메인drainerfraudlivemonthlyphishdestroyphishingscam
등록기관 GNAME.COM (Unknown)
악용 신고 연락처abuse@iqweb.io, complaint@gname.com
ICANN 레지스트리ICANN Lookup (RDAP) →
등록 정보생성됨 2026년 7월 17일 (86d · New) — Expires 2027년 7월 17일
HTTP 상태200
기술 세부 정보Provenance & timestamps
최초 발견2026년 8월 4일
DOM Analysisanalyzed 2026년 10월 9일score 100/1009 brand signals
IoC Extractionscanned 2026년 8월 4일3 wallet · 0 Telegram IoCs
Submitted URLhttps://catfee.energy/
Favicon Hash
사건 ID
ICANN OVERSIGHT

인증 및 RAA 상황

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft 어떤 내용도 자동으로 전송되지 않습니다.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
186.2.175.25
Network ASN
AS59692
Organization
Iqweb LLC
Observed location
Belmopan, BZ
Server header
ddos-guard

네임서버 2

  • a.share-dns.com
  • b.share-dns.net

Location describes the IP network.

TLS 인증서

Issuer
Let's Encrypt
Valid from
2026-10-08 15:22:34
Valid until
2027-01-06 15:22:33
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-10 16:03:02 UTC
Collection source
PhishDestroy collector
Certificate fingerprintb887175cdd01788690ceed65683a943054d116dae8e03871932cd8db376c073d

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 186.2.175.25rapiddns.io

Latest Classified Outcome 2026-10-11 10:30:39 UTC

Primary outcome 활성 콘텐츠 reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation 활성 콘텐츠 Ordinary HTTP content served 90% 2026-10-11 10:30:39 UTC
RDAP registration 알 수 없음
Observed timeline last reachable: 2026-10-11 10:30:39 UTC last content: 2026-10-11 10:30:39 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
기술 · 1 identified
Detected via Cloudflare Radar · Wappalyzer engine
이 도메인 신고하기 증거를 제출하고 다른 사람들을 보호하는 데 힘을 보태주세요

VirusTotal 분석

11 / 89 보안 공급업체가 이 도메인에 플래그를 지정했습니다.
View on VT
Last analyzed First positive detection Previous stored snapshot: 8 detections
alphaMountain.ai
BitDefender
CRDF
CyRadar
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
카스퍼스키
SOCRadar
소포스

보관된 증거

Wayback Machine Snapshot
증거 검토를 위해 과거 스냅샷을 사용할 수 있습니다.
View Archive

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-08-04 03:17:08 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 186.2.175.25.

위협 대응 Pipeline

발견
Analysis
Notifications
Monitoring

13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

위협 탐지됨
catfee.energy 탐지되어 전체 분석을 위해 대기열에 추가됨
2026년 8월 4일
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
2026년 10월 3일
URLScan.io Capture
저장됨 URLScan report with capture artifacts
2026년 8월 4일
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in 웨이백 머신 — historical evidence archived
2026년 8월 4일
VirusTotal
11/89 recorded on VirusTotal
2026년 9월 11일
차단 목록 탐지
출처: 2 blocklists: MetaMask, SEAL
2026년 10월 11일
OTX Community References
4 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
2026년 10월 5일
Brand Impersonation
Impersonation of Binance
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
2026년 8월 4일
Technical Analysis Recorded
보고서에는 저장된 기술 또는 포렌식 분석 결과가 포함됩니다.
2026년 10월 11일
Sent Report Recorded
Stored outgoing record associated with registrar GNAME.COM PTE. LTD., 2 abuse contacts
abuse@iqweb.iocomplaint@gname.com
2026년 8월 4일
DestroyList 게시됨
2026년 8월 4일
Monitoring Continues
도메인은 계속 연결 가능하거나 액세스가 제한되어 있습니다. 향후 점검을 통해 이 관찰 내용이 업데이트될 수 있습니다.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

웨이백 머신 Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

공개 차단 목록 상태

유사 도메인

저장된 유사 도메인 187개

모두 보기 (88)
binabce.com replacement binacne.com transposition binan.ce.com subdomain binancecom.com various binanci.com vowel-swap binanco.com vowel-swap binancr.com replacement binancs.com replacement binancw.com replacement binande.com replacement binanfe.com replacement binanve.com replacement binanxe.com replacement binnace.com transposition binonce.com vowel-swap binsnce.com replacement binunce.com vowel-swap binynce.com replacement binznce.com replacement bniance.com transposition bunance.com replacement ibnance.com transposition ninance.com replacement b-inance.com hyphenation b8inance.com insertion b8nance.com replacement b9nance.com replacement bbinance.com repetition bhinance.com insertion bi-nance.com hyphenation biance.com omission bibance.com replacement bibnance.com insertion bihance.com replacement bihnance.com insertion biinance.com repetition bijnance.com insertion biknance.com insertion bimance.com homoglyph bimnance.com insertion bin-ance.com hyphenation binaance.com repetition binabnce.com insertion binace.com omission binahce.com replacement binamnce.com insertion binan-ce.com hyphenation binanbce.com insertion binanc-e.com hyphenation binanc.com omission binanc3.com replacement binancce.com repetition binancve.com insertion binancxe.com insertion binancz.com replacement binandce.com insertion binane.com omission binanec.com homoglyph binanhce.com insertion binanmce.com insertion binannce.com homoglyph binanvce.com insertion binanxce.com insertion binarnce.com homoglyph binasnce.com insertion binawnce.com insertion binbance.com insertion binhance.com insertion binmance.com insertion binnance.com homoglyph binnce.com omission binqance.com insertion binsance.com insertion binwnce.com replacement binyance.com insertion bionance.com insertion birnance.com homoglyph biunance.com insertion bjnance.com replacement bnance.com omission bninance.com insertion boinance.com insertion bonance.com replacement buinance.com insertion bvinance.com insertion clinance.com homoglyph dinarce.com homoglyph ginance.com replacement

전체 187개 중 100개 표시

증거 및 외부 보고서

제출된 증거 스냅샷
Sent: Ledger records: 1 Case ID: PD-20260804-8C56C5 Recipient: complaint@gname.com
Page title stored with report: New Private Tab
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 576.8 KB
PDF notice generated Notice text archived (317 chars)
Abuse notice text as sent to the provider
Registrar: Gname.com Pte. Ltd. (Singapore)
Policy Violations: Illegal Activities section forbids phishing, fraud, fake sites, malware distribution; registrar investigates and may suspend or delete domain
Applicable Laws: Computer Misuse Act 1993 §§3+, Penal Code §§415–420 (cheating), Online Criminal Harms Act (OCHA)
심층 분석

이 사이트로 인해 영향을 받으셨나요?

7 evidence signal groups linked 1 reports recorded 마지막으로 알려진 활성
If credentials were compromised, report immediately. Do not engage with recovery scammers.

계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.

유로폴
EU 국가의 공식 신고 채널 찾기
National police directory
회복 사기꾼들을 조심하세요! 범죄자는 수사관, 변호사, 회복요원인 척 하면서 피해자에게 다시 연락할 수도 있습니다. 선불 비용을 지불하거나 자격 증명을 공유하지 마십시오. 회복 관련 사기에 대해 자세히 알아보기 →

지역 당국에 신고하십시오

공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.

97개국 디렉토리

Template-based draft · optional AI wording assistance requires separate consent

AI 지원 초안 - 사고 세부정보는 AI 제공업체에서 처리됩니다. · 직접 검토하고 제출하세요.

모든 도메인 확인

저장된 차단 목록, WHOIS, DNS 및 공개 스캔 증거를 사용한 위협 분석

지금 스캔하기

피싱 신고

의심스러운 도메인을 당사의 위협 데이터베이스에 신고해 주세요 — 커뮤니티를 보호해 주세요

보고서

실시간 위협 정보

최근 피싱 보고서 및 관찰된 가용성 변경 사항

모니터링

최신 정보를 확인하고, 안전을 지키세요

실시간 위협을 모니터링하거나, 오탐이라고 판단될 경우 이 목록에 이의를 제기하십시오.

실시간 위협 정보 이 목록에 이의 제기하기
HTML · IFRAME

이 보고서 삽입하기

이 위협 정보를 귀하의 웹사이트나 블로그에 공유하세요

embed.html
<iframe
  src="https://phishdestroy.io/ko/embed/domain/catfee.energy"
  title="PhishDestroy threat report for catfee.energy"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>