元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
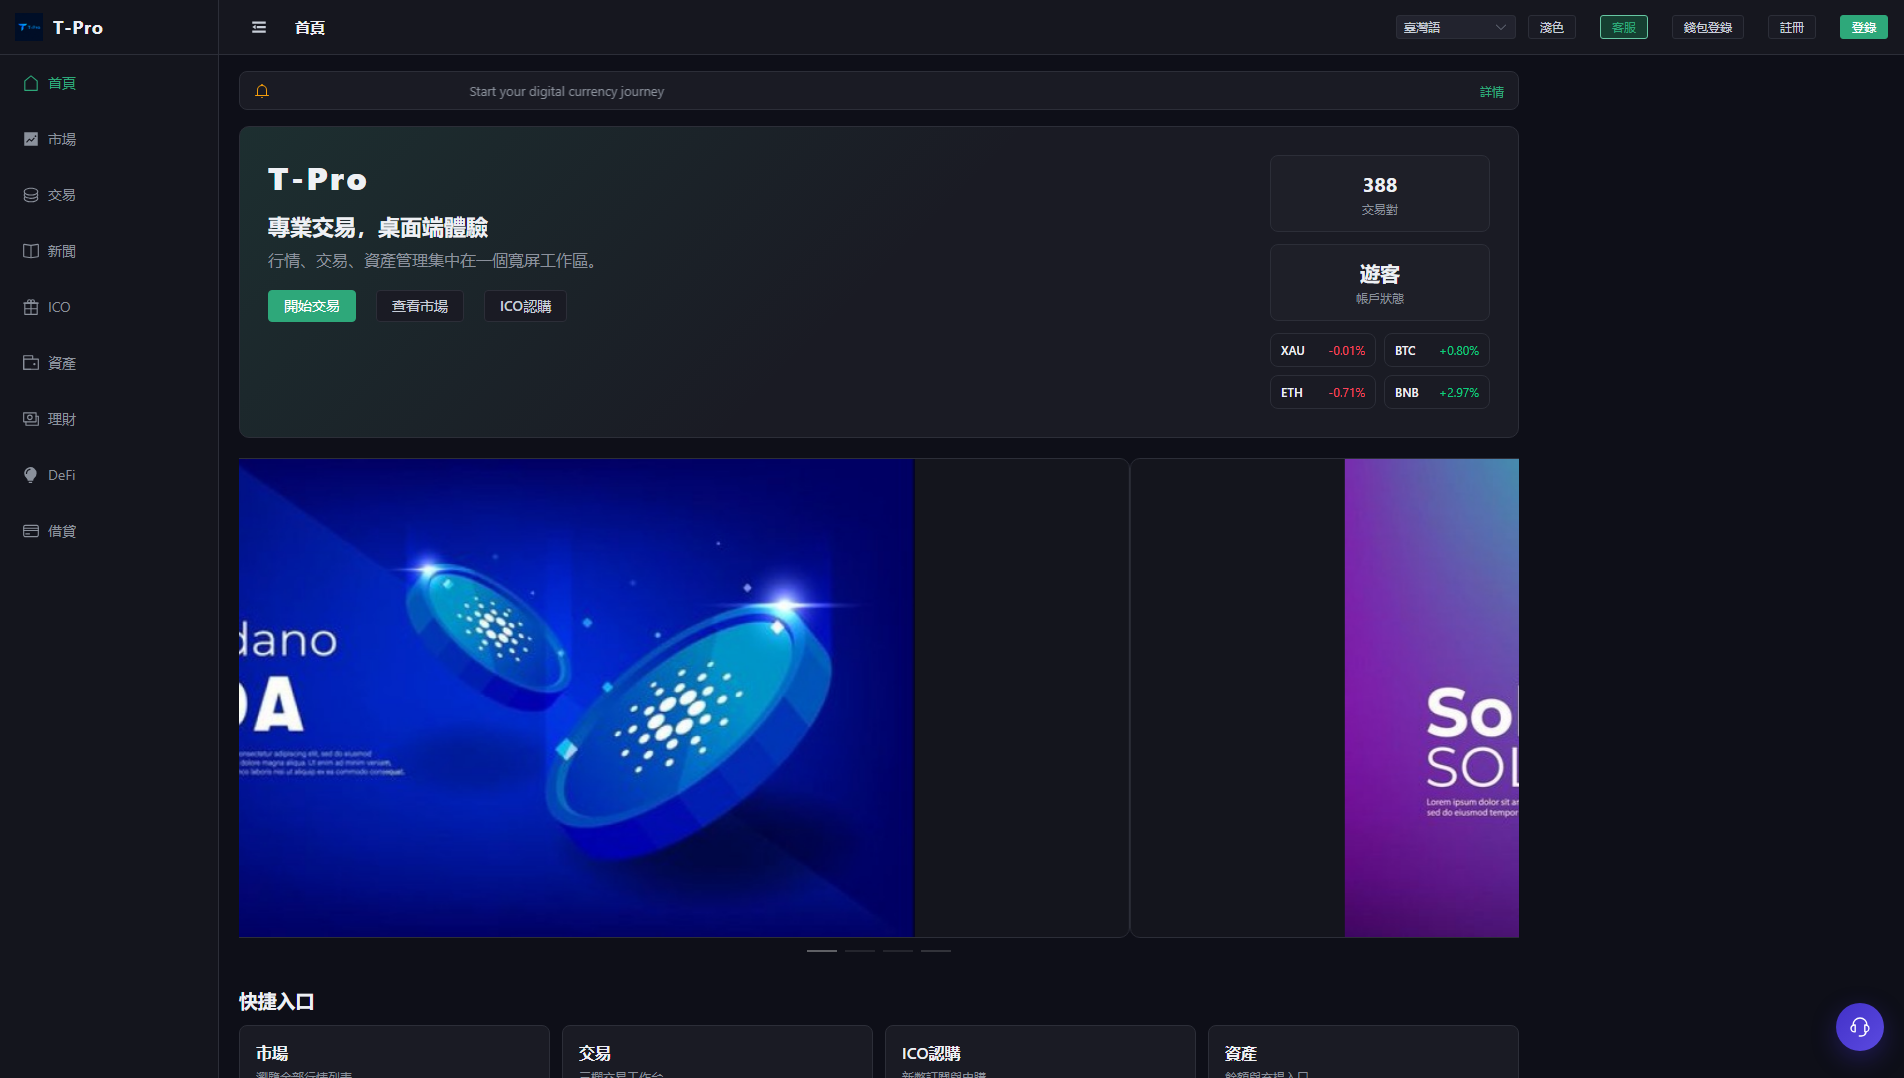
t-prokv.com is an impersonation phishing page that presented itself under the title "T-Pro". It borrowed that name to win the trust of crypto users. PhishDestroy first flagged it on 2026-09-04. The site has been offline since 2026-09-11, and as of 2026-10-19 its domain no longer resolves, so it is currently dead.
詐欺の手口
Impersonation pages copy the look and name of a service people already trust, here branded as "T-Pro". They then ask visitors to do something that only makes sense on the real service. In crypto-focused schemes that usually means logging in, entering a recovery phrase or private key, or connecting a wallet and signing a prompt. Anything typed or signed goes straight to the operator. The victim can lose account access, the contents of a wallet, or both. Listings by MetaMask and SEAL indicate the page was aimed at wallet users rather than a general audience.
証拠
On 2026-09-06, 9 of 90 VirusTotal engines marked the domain malicious, including Kaspersky, BitDefender, G-Data, Forcepoint ThreatSeeker, Gridinsoft, alphaMountain.ai, CRDF and SOCRadar. That count is modest, but it comes from unrelated vendors that reached the same verdict independently. MetaMask's own phishing list and the SEAL blocklist also carry the domain, alongside PhishDestroy. Five AlienVault OTX threat pulses reference it, showing other researchers tracked the same activity.
インフラ
The domain was registered on 2026-07-22 through Realtime Register B.V., about six weeks before PhishDestroy caught it. That gap is consistent with a domain registered in advance and put into use later. It sat behind Cloudflare, Inc. with a Canadian location, which hides the true origin server from visitors. The site went dark one week after first detection, a short lifespan typical of disposable phishing domains.
What to do
If you entered a password on this site, change it on the genuine service and on any account that shares it, then turn on app-based 2FA. If you typed a seed phrase or private key, treat that wallet as compromised and move any funds to a newly created wallet immediately. If you connected a wallet and signed anything, review and revoke token approvals with a trusted approval-checker. Defenders should block the domain and check logs for visits between 2026-07-22 and 2026-09-11. They should also watch for lookalike domains reusing the T-Pro branding.
t-prokv.com is an impersonation phishing page titled T-Pro, flagged by MetaMask and SEAL, targeting crypto users who trust the T-Pro name.
AIによる要約
Overview t-prokv.com is an impersonation phishing page that presented itself under the title "T-Pro". It borrowed that name to win the trust of crypto users. PhishDestroy first flagged it on 2026-09-04. The site has been offline since 2026-09-11, and as of 2026-10-19 its domain no longer resolves, so it is currently dead. How the scam works Impersonation pages copy the look and name of a service people already trust, here branded as "T-Pro". They then ask visitors to do something that only makes sense on the real service. In crypto-focused schemes that usually means logging in, entering a recovery phrase or private key, or connecting a wallet and signing a prompt. Anything typed or signed goes straight to the operator. The victim can lose account access, the contents of a wallet, or both. Listings by MetaMask and SEAL indicate the page was aimed at wallet users rather than a general audience. Evidence On 2026-09-06, 9 of 90 VirusTotal engines marked the domain malicious, including Kaspersky, BitDefender, G-Data, Forcepoint ThreatSeeker, Gridinsoft, alphaMountain.ai, CRDF and SOCRadar. That count is modest, but it comes from unrelated vendors that reached the same verdict independently. MetaMask's own phishing list and the SEAL blocklist also carry the domain, alongside PhishDestroy. Five AlienVault OTX threat pulses reference it, showing other researchers tracked the same activity. Infrastructure The domain was registered on 2026-07-22 through Realtime Register B.V., about six weeks before PhishDestroy caught it. That gap is consistent with a domain registered in advance and put into use later. It sat behind Cloudflare, Inc. with a Canadian location, which hides the true origin server from visitors. The site went dark one week after first detection, a short lifespan typical of disposable phishing domains. What to do If you entered a password on this site, change it on the genuine service and on any account that shares it, then turn on app-based 2FA. If you typed a seed phrase or private key, treat that wallet as compromised and move any funds to a newly created wallet immediately. If you connected a wallet and signed anything, review and revoke token approvals with a trusted approval-checker. Defenders should block the domain and check logs for visits between 2026-07-22 and 2026-09-11. They should also watch for lookalike domains reusing the T-Pro branding. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a06d39-3028-7729-823a-e2956ce1ab58/ VirusTotal report: https://www.virustotal.com/gui/domain/t-prokv.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=t-prokv.com Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP登録
観測されたタイムラインlast reachable: 2026-09-07 22:14 UTCcurrent episode first observed: 2026-09-30 16:14 UTCobserved RIP window: 2026-09-07 22:14 UTC → 2026-09-30 16:14 UTC · 546.00hmidpoint estimate ≈ 2026-09-19 07:14 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 172.67.150.54





 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT