元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
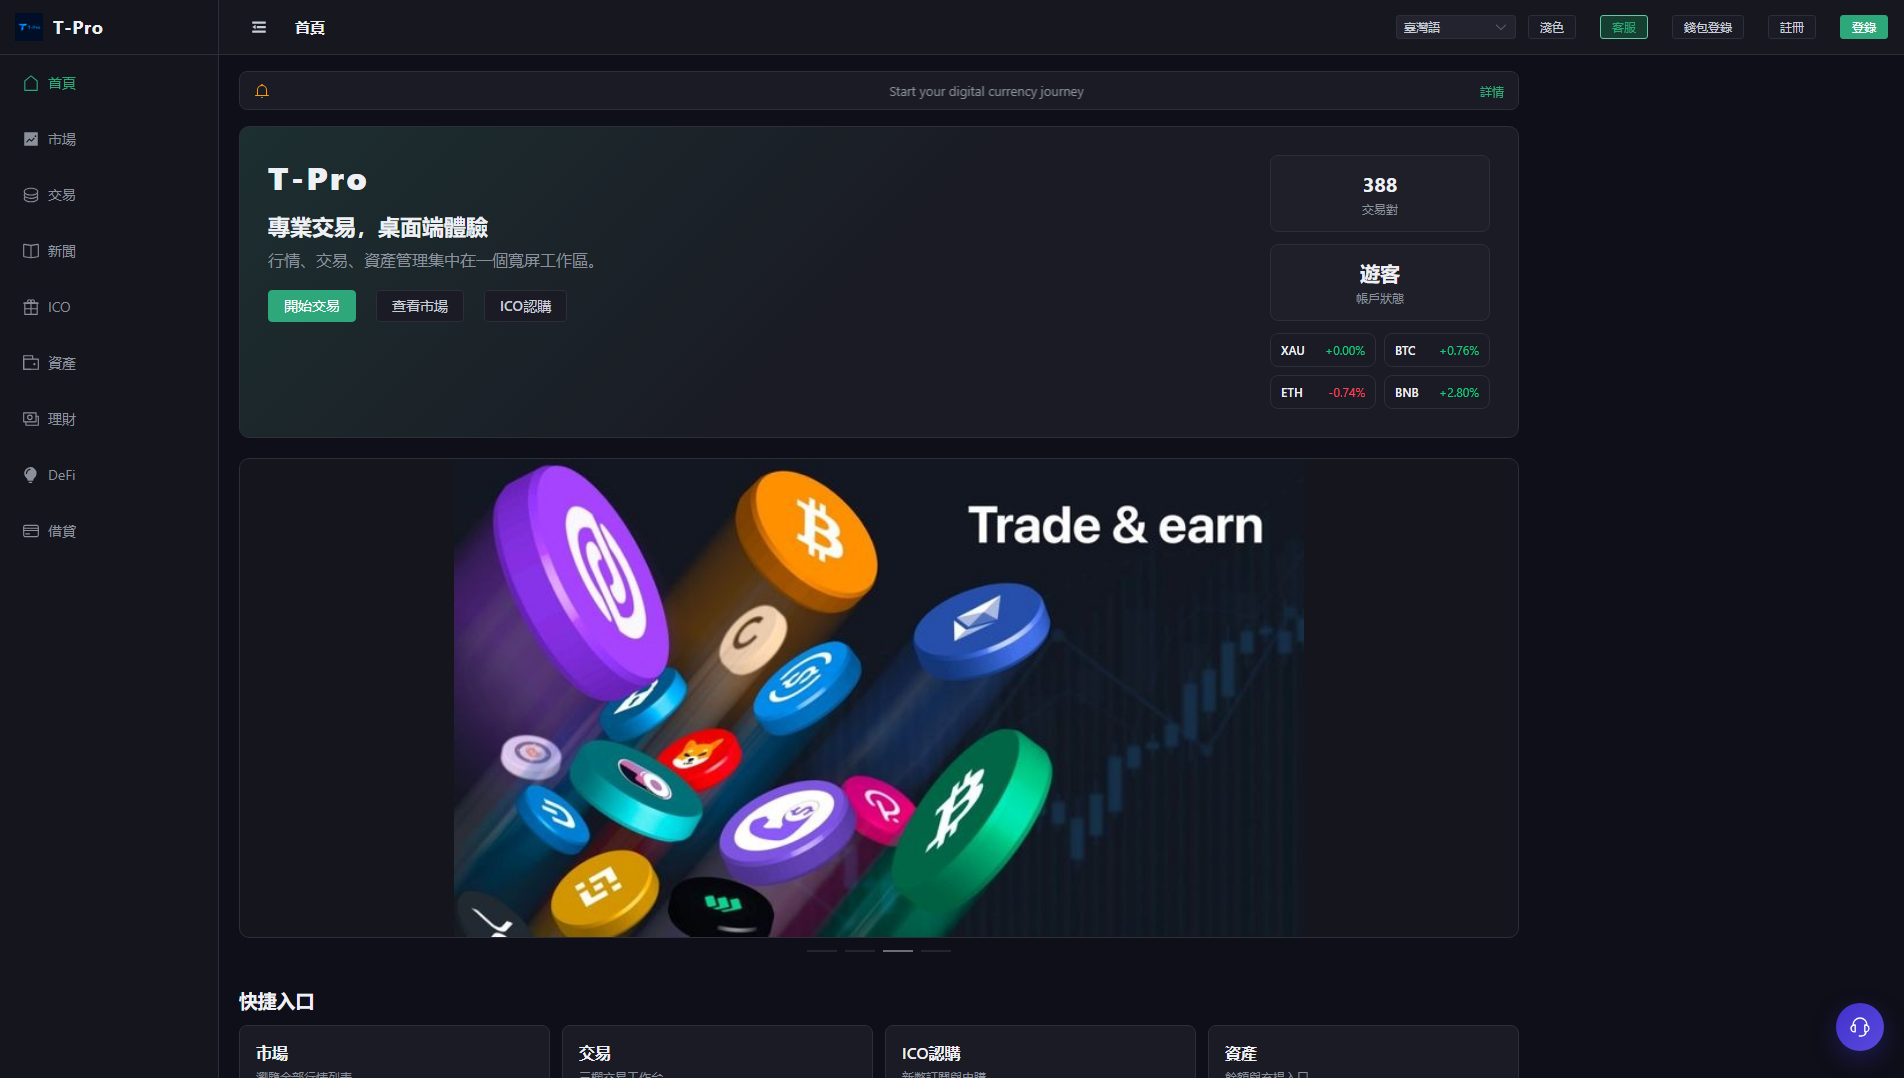
t-prokg.com ran a phishing page under the title "T-Pro", posing as a legitimate service to win the trust of crypto users. PhishDestroy first saw it on 2026-09-04 and classified it as impersonation. The site went offline on 2026-09-11. When we last checked on 2026-10-19, its DNS no longer resolved, so the domain was not reachable.
詐欺の手口
An impersonation page copies the name and look of a service the victim already uses, here presented as "T-Pro", so the visitor believes they are on the real site. It then asks for account credentials, recovery details or a wallet connection. Whatever is entered goes straight to the operators. Stolen logins let them take over accounts. A seed phrase or a signed wallet request can let them empty the wallet outright, and blockchain transfers cannot be reversed.
証拠
VirusTotal returned 9 detections out of 90 engines on 2026-09-06, two days after our first sighting. The flagging vendors included BitDefender, Kaspersky, Forcepoint ThreatSeeker, G-Data, Gridinsoft, alphaMountain.ai, CRDF and SOCRadar. That count is modest, but several major vendors reached the same verdict independently and quickly. MetaMask's and SEAL's crypto-focused blocklists also list the domain alongside PhishDestroy, and it appears in 3 AlienVault OTX threat pulses.
インフラ
The domain was registered on 2026-07-20 through Realtime Register B.V., roughly six weeks before PhishDestroy detected it. That gap is consistent with a domain set up in advance and then put into use. Traffic went through Cloudflare, Inc. (IP 188.114.96.3, located in CA), which hides the server actually hosting the content. The site stayed live for only about a week after detection before it went dark.
What to do
If you typed a password or email into this site, change that password on the genuine service and anywhere else you reused it. Then enable app-based 2FA. If you entered a seed phrase, treat that wallet as compromised and move any remaining funds to a new wallet created with a fresh phrase. If you connected a wallet or signed anything, review and revoke token approvals with a trusted approval-checking tool. Defenders should block t-prokg.com at DNS and proxy level and search logs for any visits to it after 2026-07-20.
t-prokg.com was an impersonation phishing site titled "T-Pro" that copied a trusted brand to steal logins and crypto from wallet users who trusted it.
AIによる要約
Overview t-prokg.com ran a phishing page under the title "T-Pro", posing as a legitimate service to win the trust of crypto users. PhishDestroy first saw it on 2026-09-04 and classified it as impersonation. The site went offline on 2026-09-11. When we last checked on 2026-10-19, its DNS no longer resolved, so the domain was not reachable. How the scam works An impersonation page copies the name and look of a service the victim already uses, here presented as "T-Pro", so the visitor believes they are on the real site. It then asks for account credentials, recovery details or a wallet connection. Whatever is entered goes straight to the operators. Stolen logins let them take over accounts. A seed phrase or a signed wallet request can let them empty the wallet outright, and blockchain transfers cannot be reversed. Evidence VirusTotal returned 9 detections out of 90 engines on 2026-09-06, two days after our first sighting. The flagging vendors included BitDefender, Kaspersky, Forcepoint ThreatSeeker, G-Data, Gridinsoft, alphaMountain.ai, CRDF and SOCRadar. That count is modest, but several major vendors reached the same verdict independently and quickly. MetaMask's and SEAL's crypto-focused blocklists also list the domain alongside PhishDestroy, and it appears in 3 AlienVault OTX threat pulses. Infrastructure The domain was registered on 2026-07-20 through Realtime Register B.V., roughly six weeks before PhishDestroy detected it. That gap is consistent with a domain set up in advance and then put into use. Traffic went through Cloudflare, Inc. (IP 188.114.96.3, located in CA), which hides the server actually hosting the content. The site stayed live for only about a week after detection before it went dark. What to do If you typed a password or email into this site, change that password on the genuine service and anywhere else you reused it. Then enable app-based 2FA. If you entered a seed phrase, treat that wallet as compromised and move any remaining funds to a new wallet created with a fresh phrase. If you connected a wallet or signed anything, review and revoke token approvals with a trusted approval-checking tool. Defenders should block t-prokg.com at DNS and proxy level and search logs for any visits to it after 2026-07-20. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a06d2c-12f5-726d-a5c7-54524850196e/ VirusTotal report: https://www.virustotal.com/gui/domain/t-prokg.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=t-prokg.com Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP登録
観測されたタイムラインlast reachable: 2026-09-07 22:14 UTCcurrent episode first observed: 2026-09-30 16:14 UTCobserved RIP window: 2026-09-07 22:14 UTC → 2026-09-30 16:14 UTC · 546.00hmidpoint estimate ≈ 2026-09-19 07:14 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 188.114.96.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT