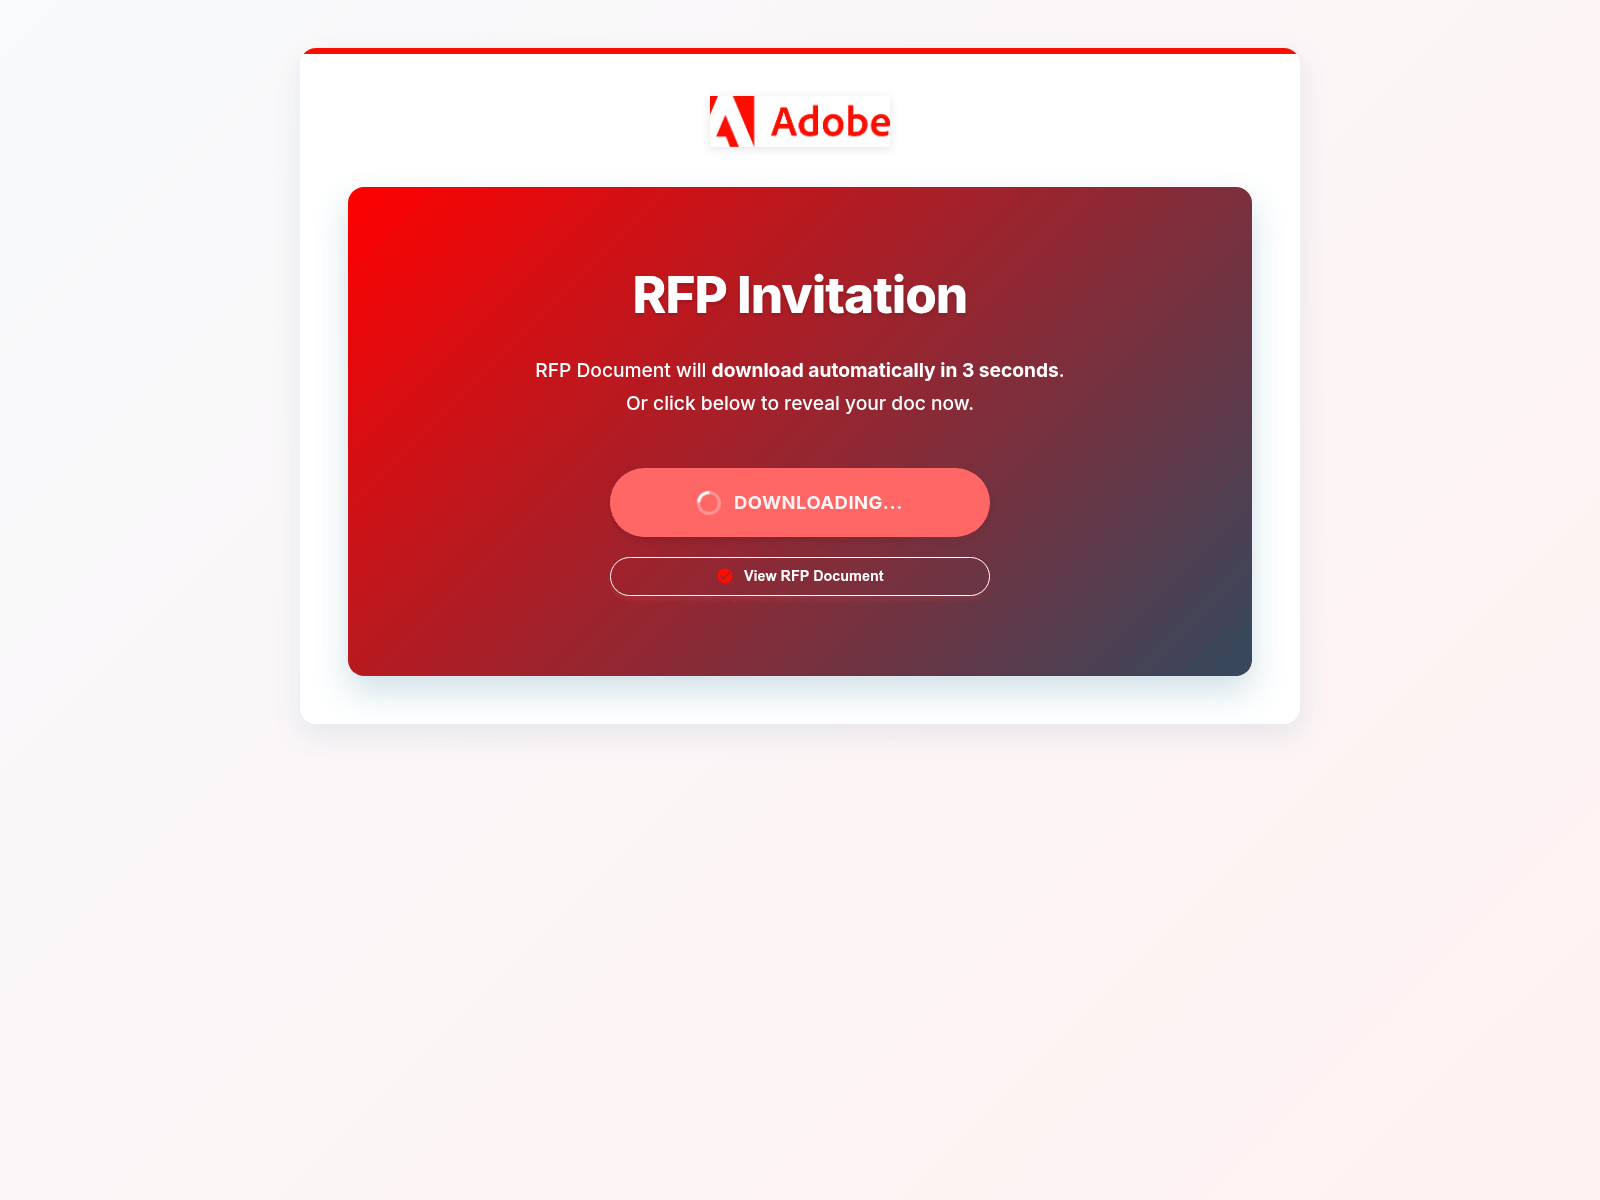
The qnomos.com page hosted an Adobe-branded RFP invitation that attempts to automatically download a malicious file, utilizing a domain completely unrelated to adobe.com. If you visited this page and downloaded a file, delete it immediately, disconnect your device, and run a thorough antivirus scan.
URLScanによるキャプチャ · 2026-11-21 17:45 UTC · SHA-256 06695a06…3918cfe
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Adobe RFP document download interface
The page hosted on qnomos.com prominently features the Adobe logo at the top and displays a large header reading "RFP Invitation". Below this heading, explanatory text states "RFP Document will download automatically in 3 seconds. Or click below to reveal your doc now." The interface includes a coral button labeled "DOWNLOADING..." containing a loading spinner icon, alongside an outlined button reading "View RFP Document". This entire setup mimics a corporate document delivery portal while operating on an arbitrary domain rather than adobe.com. Visitors are nudged to wait for an automated file payload or interact with the manual download triggers.
Independent security findings and risk analysis
urlscan classified the page as malicious, VirusTotal showed 2 of 92 engines flagging it on 21 Nov 2026, 3 AlienVault OTX community reports reference it, and OpenPhish blocks it, with security vendors like Gridinsoft and SOCRadar explicitly flagging the domain. PhishDestroy's evidence score for it is 50/100 (high). Pages mimicking corporate document portals often distribute trojans, infostealers, or malicious scripts disguised as routine office documents or RFPs, so visitors should avoid interacting with download prompts on qnomos.com and navigate directly to adobe.com for official communications.
Recommended actions for downloaded files
Run a full antivirus scan using a trusted security product to detect any installed infostealers or persistent background tasks. Check the system for unauthorized software installations and change critical account passwords from a clean, unaffected device.
qnomos.com hosted an Adobe RFP document download page, flagged by urlscan and 2 VirusTotal engines. Avoid executing any files downloaded from this address.
AIによる要約
Adobe RFP document download interface The page hosted on qnomos.com prominently features the Adobe logo at the top and displays a large header reading "RFP Invitation". Below this heading, explanatory text states "RFP Document will download automatically in 3 seconds. Or click below to reveal your doc now." The interface includes a coral button labeled "DOWNLOADING..." containing a loading spinner icon, alongside an outlined button reading "View RFP Document". This entire setup mimics a corporate document delivery portal while operating on an arbitrary domain rather than adobe.com. Visitors are nudged to wait for an automated file payload or interact with the manual download triggers. Independent security findings and risk analysis urlscan classified the page as malicious, VirusTotal showed 2 of 92 engines flagging it on 21 Nov 2026, 3 AlienVault OTX community reports reference it, and OpenPhish blocks it, with security vendors like Gridinsoft and SOCRadar explicitly flagging the domain. PhishDestroy's evidence score for it is 50/100 (high). Pages mimicking corporate document portals often distribute trojans, infostealers, or malicious scripts disguised as routine office documents or RFPs, so visitors should avoid interacting with download prompts on qnomos.com and navigate directly to adobe.com for official communications. Recommended actions for downloaded files Run a full antivirus scan using a trusted security product to detect any installed infostealers or persistent background tasks. Check the system for unauthorized software installations and change critical account passwords from a clean, unaffected device.
最新のHTTP観測結果RedirectingHTTP redirect observed80%2026-11-22 11:59 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 Tucows
 80.88.87.242


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT