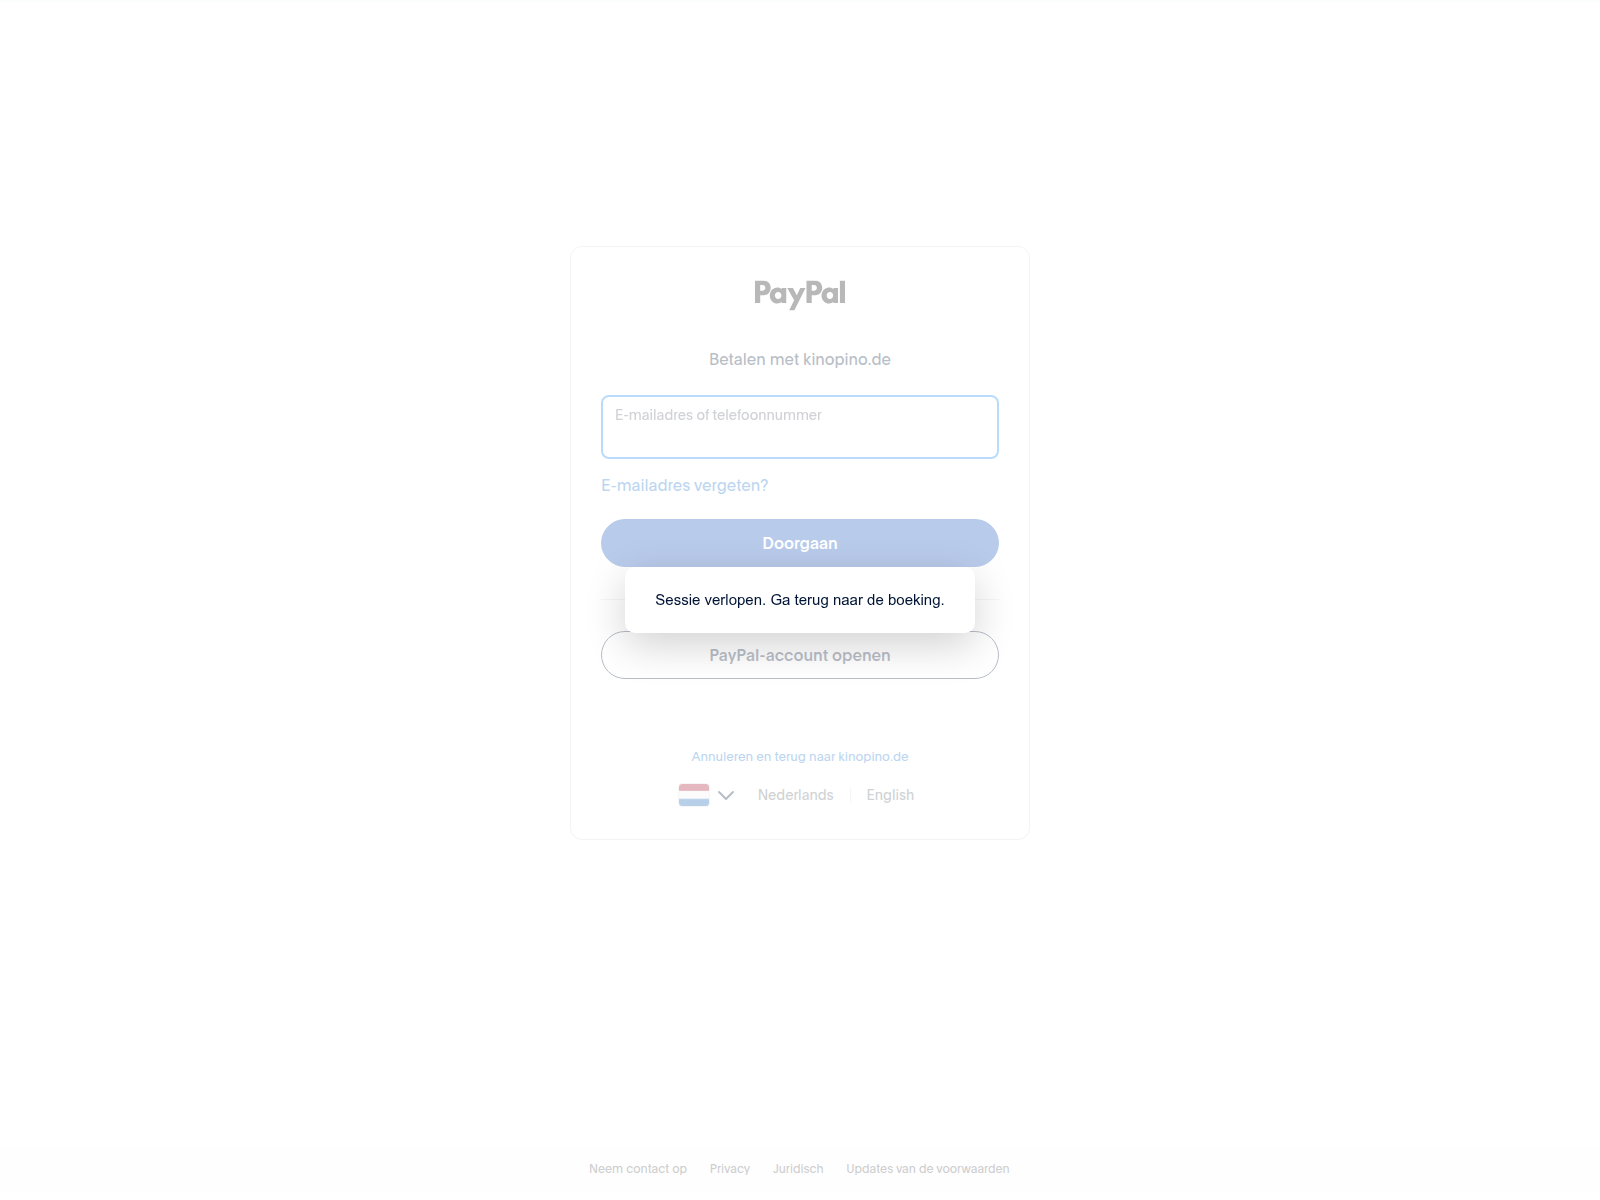
The domain paypal.kinopino.de hosted a phishing page mimicking the PayPal login interface in Dutch to harvest user credentials. Anyone who submitted their details should immediately update their actual PayPal password and check their account history.
URLScanによるキャプチャ · 2026-11-22 06:38 UTC · SHA-256 a5a59e47…8fe8024
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
PayPal login clone in Dutch
The page displayed on the site presents a credential harvesting interface mimicking PayPal. It displays the PayPal logo at the top followed by the text "Betalen met kinopino.de" and features an input field labelled "E-mailadres of telefoonnummer". Below this field sits a primary blue button marked "Doorgaan", accompanied by a smaller secondary button reading "PayPal-account openen". A floating notification overlay states "Sessie verlopen. Ga terug naar de boeking.", while footer links include "Neem contact op", "Privacy", "Juridisch" and "Updates van de voorwaarden".
Credential harvesting and security detections
By requesting email addresses or phone numbers followed by passwords, the form collects sensitive account credentials directly from visitors. This address is not the official site; PayPal operates exclusively on paypal.com rather than on third-party domains like kinopino.de. Spamhaus DBL lists it as phishing, and 9 of 92 VirusTotal engines flagged it on 13 Nov 2026, so this is a known threat rather than an isolated misconfiguration. PhishDestroy scores the evidence against it at 75/100 (critical), and vendors including ESET, Fortinet and Netcraft classify the URL as malicious or suspicious.
Shared server infrastructure
4 other reported domains resolve to the same IP address and 9 use the same nameserver pair. Among these neighbours are paypal.kinoberry.de, paypal.kinoloft.de and paypal.kinodora.de, which present identical login or brand-mimicking templates, pointing to a coordinated deployment of phishing pages hosted on the same infrastructure.
paypal.kinopino.de presented a fraudulent PayPal sign-in page in Dutch requesting account details, flagged by Spamhaus DBL and 9 VirusTotal engines.
AIによる要約
PayPal login clone in Dutch The page displayed on the site presents a credential harvesting interface mimicking PayPal. It displays the PayPal logo at the top followed by the text "Betalen met kinopino.de" and features an input field labelled "E-mailadres of telefoonnummer". Below this field sits a primary blue button marked "Doorgaan", accompanied by a smaller secondary button reading "PayPal-account openen". A floating notification overlay states "Sessie verlopen. Ga terug naar de boeking.", while footer links include "Neem contact op", "Privacy", "Juridisch" and "Updates van de voorwaarden". Credential harvesting and security detections By requesting email addresses or phone numbers followed by passwords, the form collects sensitive account credentials directly from visitors. This address is not the official site; PayPal operates exclusively on paypal.com rather than on third-party domains like kinopino.de. Spamhaus DBL lists it as phishing, and 9 of 92 VirusTotal engines flagged it on 13 Nov 2026, so this is a known threat rather than an isolated misconfiguration. PhishDestroy scores the evidence against it at 75/100 (critical), and vendors including ESET, Fortinet and Netcraft classify the URL as malicious or suspicious. Shared server infrastructure 4 other reported domains resolve to the same IP address and 9 use the same nameserver pair. Among these neighbours are paypal.kinoberry.de, paypal.kinoloft.de and paypal.kinodora.de, which present identical login or brand-mimicking templates, pointing to a coordinated deployment of phishing pages hosted on the same infrastructure.

 150.241.66.223


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT