元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
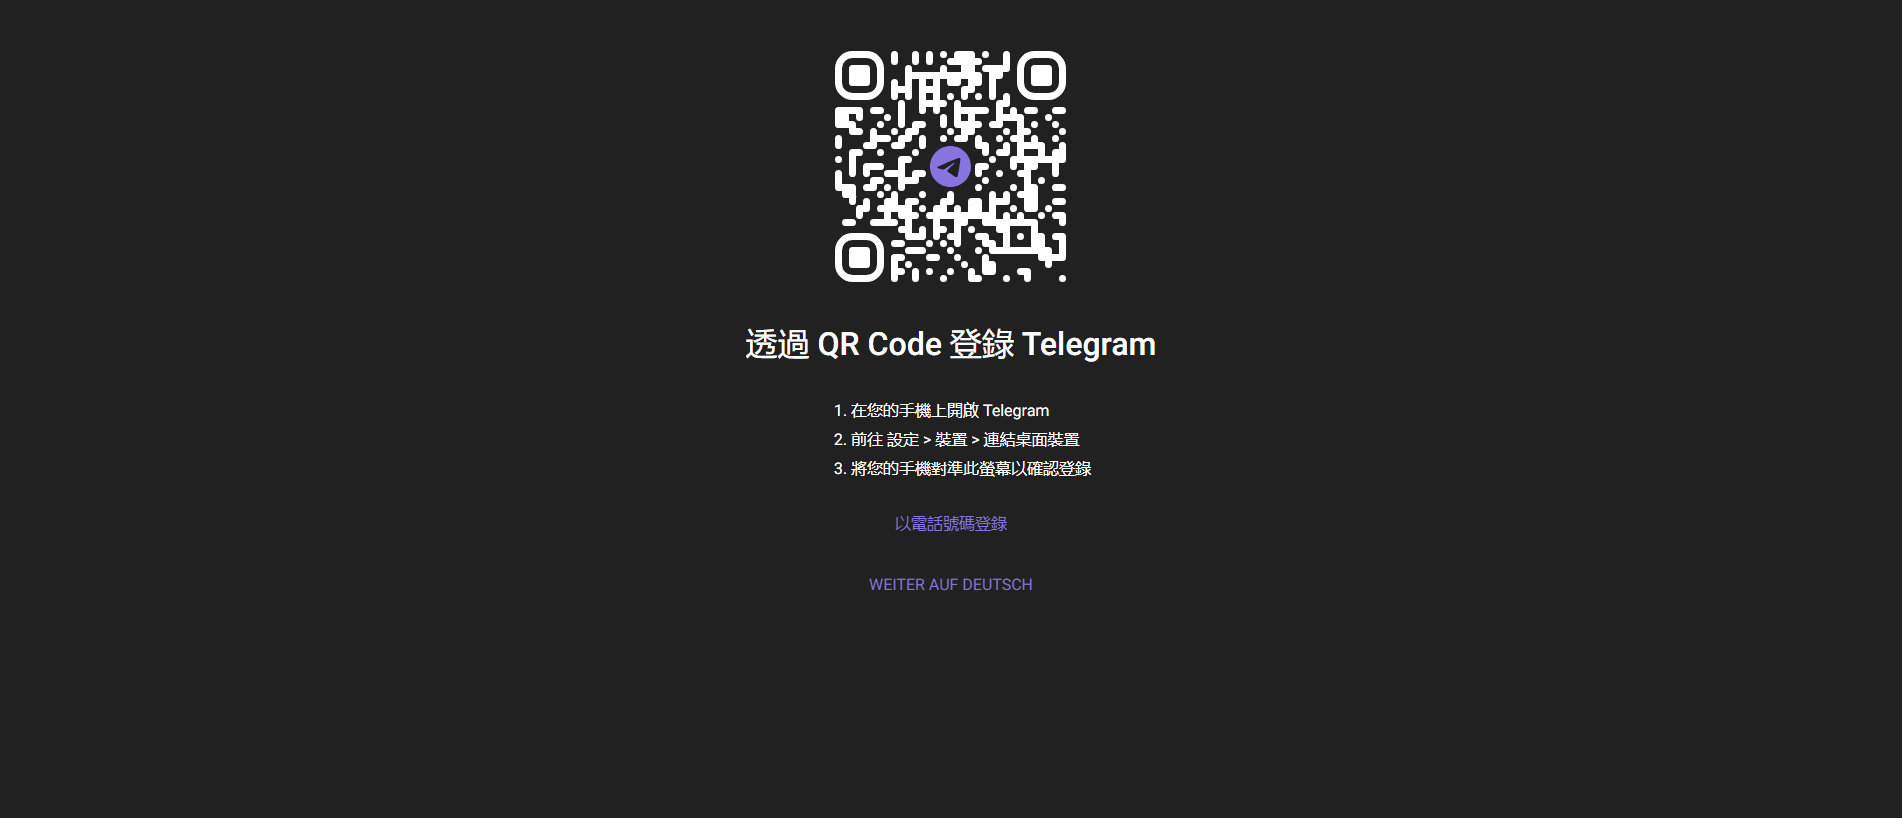
As observed on 2026-10-26, the captured screenshot shows a Chinese-language page with a QR code carrying the Telegram logo, a heading meaning sign in to Telegram via QR Code, three numbered device-linking steps and a link offering sign in with a phone number. PhishDestroy listed it under an automated Impersonation assessment, first seen by PhishDestroy on 2026-10-26, three days after the 2026-10-23 registration.
詐欺の手口
The page mimics the Telegram QR device-linking flow, so a visitor who scans the code or supplies a phone number could surrender session control or account credentials to the operator. As a category risk, this credential and session-harvesting pattern targets messaging accounts and can lead to account takeover.
証拠
The screenshot shows the QR code, Telegram logo, numbered login steps and phone-number login link. urlscan scored the engine verdict 99 and the overall verdict 100, categorised as phishing and tagged with the Telegram brand on 2026-10-26. VirusTotal flagged the domain as malicious, with Emsisoft and Fortinet applying phishing labels and Netcraft applying a malicious label. Google Safe Browsing, Spamhaus and external blocklists did not flag it on 2026-10-26, while OTX recorded 3 pulses and PhishDestroy's internal blocklist flags it; no cross-site redirect was observed. Inspection recorded no third-party trackers and 10 distinct script SHA256 hashes for campaign pivoting, the first starting a2382157448b, with page globals consistent with a Telegram Web style client.
インフラ
Notable weaknesses: no Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP or CORP headers; HSTS present with a max-age of 31536000; TLS 1.3 with AES-256-GCM, forward secrecy and ALPN h2; no SPF, DKIM or DMARC; CAA records present; DNSSEC unsigned. The domain was registered through GMO Internet Group, Inc. d/b/a Onamae.com on 2026-10-23, with hosting recorded only as a scan observation and no CDN or WAF identified in the signals.
What to do
If you entered a phone number or scanned the code on itelsgiae.com, change your Telegram password inside the genuine Telegram app, enable two-step verification, and end any active sessions you do not recognise, then stop reusing that password elsewhere. For defenders and filtering teams, block itelsgiae.com and pivot on the recorded script hashes.
PhishDestroy assesses itelsgiae.com as an impersonation phishing page presenting a fake Telegram QR code login form.
AIによる要約
Overview As observed on 2026-10-26, the captured screenshot shows a Chinese-language page with a QR code carrying the Telegram logo, a heading meaning sign in to Telegram via QR Code, three numbered device-linking steps and a link offering sign in with a phone number. PhishDestroy listed it under an automated Impersonation assessment, first seen by PhishDestroy on 2026-10-26, three days after the 2026-10-23 registration. How the scam works The page mimics the Telegram QR device-linking flow, so a visitor who scans the code or supplies a phone number could surrender session control or account credentials to the operator. As a category risk, this credential and session-harvesting pattern targets messaging accounts and can lead to account takeover. Evidence The screenshot shows the QR code, Telegram logo, numbered login steps and phone-number login link. urlscan scored the engine verdict 99 and the overall verdict 100, categorised as phishing and tagged with the Telegram brand on 2026-10-26. VirusTotal flagged the domain as malicious, with Emsisoft and Fortinet applying phishing labels and Netcraft applying a malicious label. Google Safe Browsing, Spamhaus and external blocklists did not flag it on 2026-10-26, while OTX recorded 3 pulses and PhishDestroy's internal blocklist flags it; no cross-site redirect was observed. Inspection recorded no third-party trackers and 10 distinct script SHA256 hashes for campaign pivoting, the first starting a2382157448b, with page globals consistent with a Telegram Web style client. Infrastructure Notable weaknesses: no Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP or CORP headers; HSTS present with a max-age of 31536000; TLS 1.3 with AES-256-GCM, forward secrecy and ALPN h2; no SPF, DKIM or DMARC; CAA records present; DNSSEC unsigned. The domain was registered through GMO Internet Group, Inc. d/b/a Onamae.com on 2026-10-23, with hosting recorded only as a scan observation and no CDN or WAF identified in the signals. What to do If you entered a phone number or scanned the code on itelsgiae.com, change your Telegram password inside the genuine Telegram app, enable two-step verification, and end any active sessions you do not recognise, then stop reusing that password elsewhere. For defenders and filtering teams, block itelsgiae.com and pivot on the recorded script hashes. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a177fd-d59d-7491-9178-b0b793adb1c4/ Cloudflare Radar report: https://radar.cloudflare.com/scan/541f9c5d-129e-46ec-87cc-56783409a2e5 URLQuery report: https://urlquery.net/report/d7806af5-8536-4d68-87e2-e479459a04ba Stored capture screenshot: https://i.ibb.co/nqBCYYpJ/72f5044daff1.png Cloudflare Radar screenshot (2026-10-26T11:34:42Z): https://screenshots.phishdestroy.io/cf/541f9c5d-129e-46ec-87cc-56783409a2e5.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/d7806af5-8536-4d68-87e2-e479459a04ba.png URLScan screenshot (2026-10-26T11:23:36Z): https://screenshots.phishdestroy.io/us/01a177f3-6cc7-7636-983b-02ebda01d42c.png URLScan capture report: https://urlscan.io/result/01a177f3-6cc7-7636-983b-02ebda01d42c/ URLScan screenshot (2026-10-26T11:38:00Z): https://screenshots.phishdestroy.io/us/01a17800-aeeb-71ac-b380-bc24794167a3.png URLScan capture report: https://urlscan.io/result/01a17800-aeeb-71ac-b380-bc24794167a3/ VirusTotal report: https://www.virustotal.com/gui/domain/itelsgiae.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=itelsgiae.com Archived copy: https://web.archive.org/web/20261026113414/https://itelsgiae.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Ogurl: https://web.telegram.org/k/; Title: Telegram Web; Ogtype: website; Ogimage: assets/img/android-chrome-192x192.png?v=jw3mK7G9Ry; Ogtitle: Telegram Web; Themecolor: #ffffff; Description: Telegram is a cloud-based mobile and desktop messaging app with a focus on security and speed.; Canonicalurl: https://web.telegram.org/; Ogdescription: Telegram is a cloud-based mobile and desktop messaging app with a focus on security and speed.

 43.133.87.107


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT