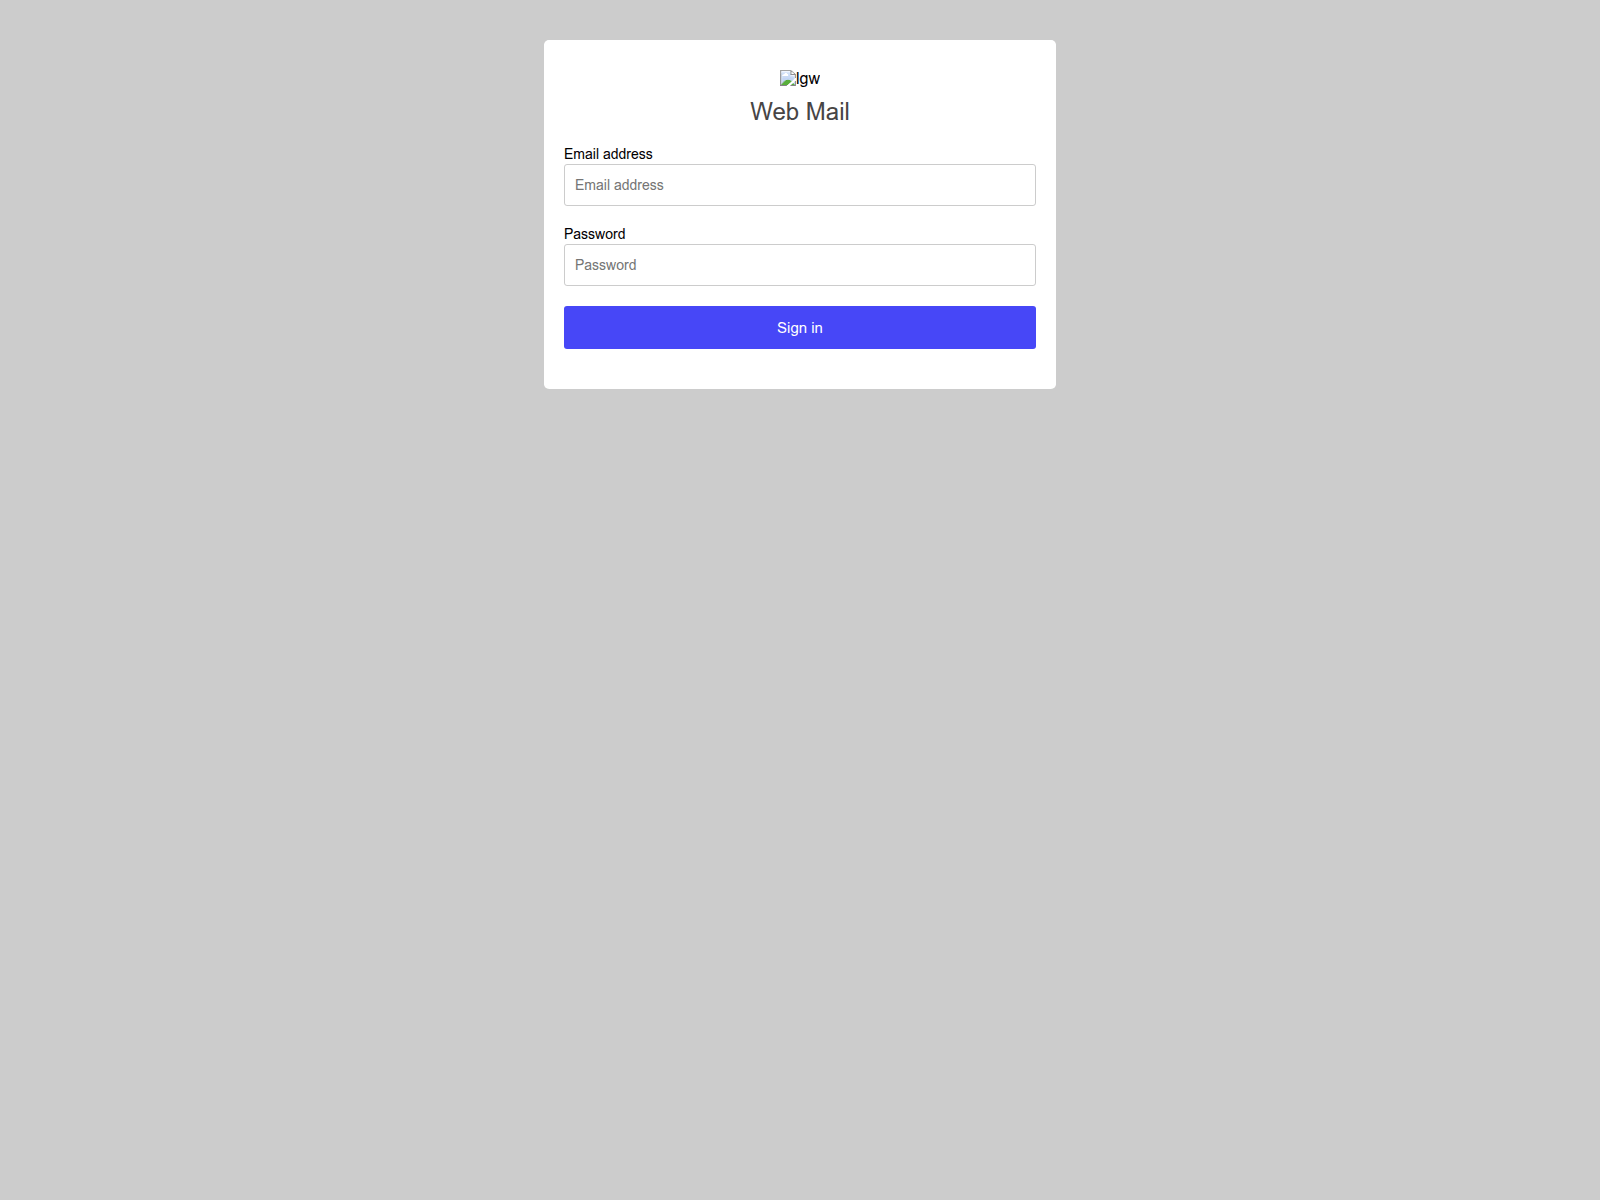
On 2026-11-12, googleurlnew.vercel.app was captured showing a centered white sign-in card on a gray background. The card displays a small broken image icon above the heading "Web Mail", followed by labeled fields for "Email address" and "Password" and a blue "Sign in" button. The page presents itself as a webmail login form, with placeholder text repeating "Email address" and "Password" inside the two input boxes.
URLScanによるキャプチャ · 2026-11-12 16:30 UTC · SHA-256 0857f15f…0d35609
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-11-12, googleurlnew.vercel.app was captured showing a centered white sign-in card on a gray background. The card displays a small broken image icon above the heading "Web Mail", followed by labeled fields for "Email address" and "Password" and a blue "Sign in" button. The page presents itself as a webmail login form, with placeholder text repeating "Email address" and "Password" inside the two input boxes.
The stored VirusTotal domain result reports 6 detections out of 92 engines. G-Data reported "phishing"; Sophos reported "phishing".
googleurlnew.vercel.app: Recorded Web Mail Sign-In Page
AIによる説明
PhishDestroy records the captured googleurlnew.vercel.app page as a Web Mail sign-in form with email address and password fields and a Sign in button.
AIによる要約
On 2026-11-12, googleurlnew.vercel.app was captured showing a centered white sign-in card on a gray background. The card displays a small broken image icon above the heading "Web Mail", followed by labeled fields for "Email address" and "Password" and a blue "Sign in" button. The page presents itself as a webmail login form, with placeholder text repeating "Email address" and "Password" inside the two input boxes. The stored VirusTotal domain result reports 6 detections out of 92 engines. G-Data reported "phishing"; Sophos reported "phishing".