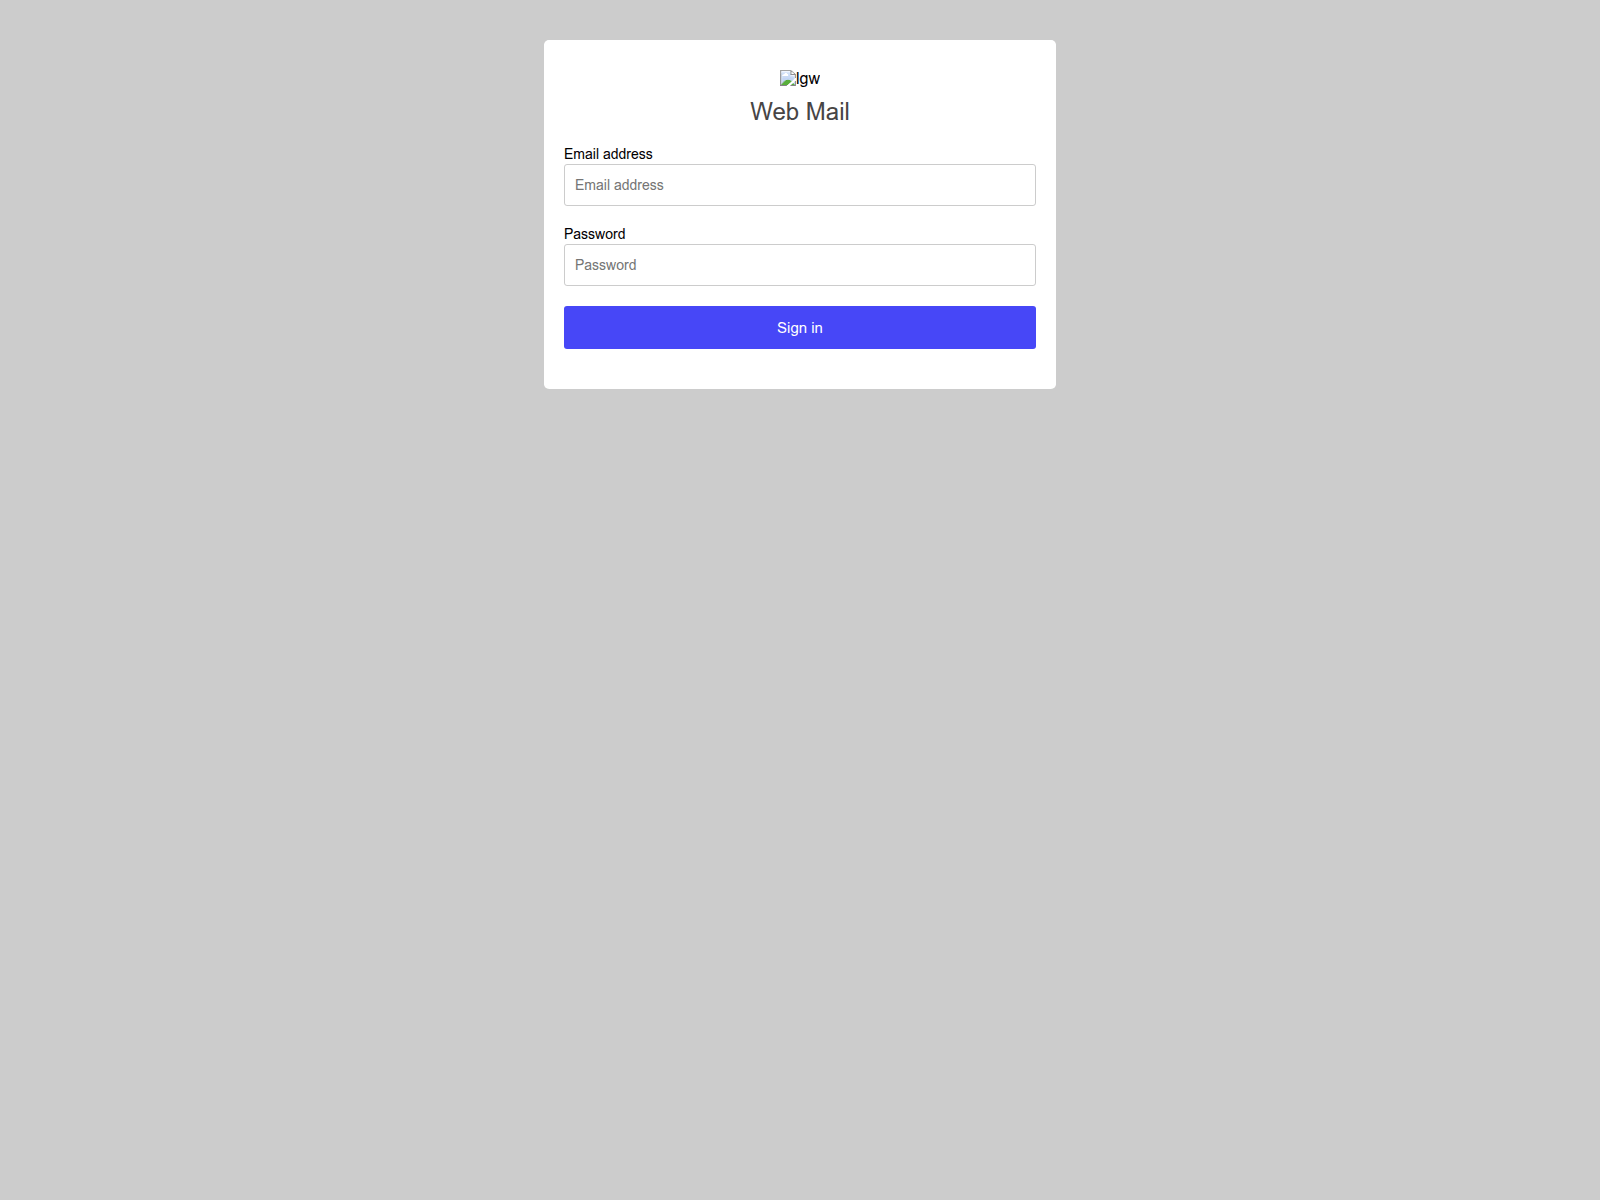
On 2026-11-12, googleurlnew.vercel.app was captured showing a centered white sign-in card on a gray background. The card displays a small broken image icon above the heading "Web Mail", followed by labeled fields for "Email address" and "Password" and a blue "Sign in" button. The page presents itself as a webmail login form, with placeholder text repeating "Email address" and "Password" inside the two input boxes.
URLScan截图 · 2026-11-12 16:30 UTC · SHA-256 0857f15f…0d35609
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-12, googleurlnew.vercel.app was captured showing a centered white sign-in card on a gray background. The card displays a small broken image icon above the heading "Web Mail", followed by labeled fields for "Email address" and "Password" and a blue "Sign in" button. The page presents itself as a webmail login form, with placeholder text repeating "Email address" and "Password" inside the two input boxes.
The stored VirusTotal domain result reports 6 detections out of 92 engines. G-Data reported "phishing"; Sophos reported "phishing".
googleurlnew.vercel.app: Recorded Web Mail Sign-In Page
AI 描述
PhishDestroy records the captured googleurlnew.vercel.app page as a Web Mail sign-in form with email address and password fields and a Sign in button.
AI摘要
On 2026-11-12, googleurlnew.vercel.app was captured showing a centered white sign-in card on a gray background. The card displays a small broken image icon above the heading "Web Mail", followed by labeled fields for "Email address" and "Password" and a blue "Sign in" button. The page presents itself as a webmail login form, with placeholder text repeating "Email address" and "Password" inside the two input boxes. The stored VirusTotal domain result reports 6 detections out of 92 engines. G-Data reported "phishing"; Sophos reported "phishing".

 216.198.79.67


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT