元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
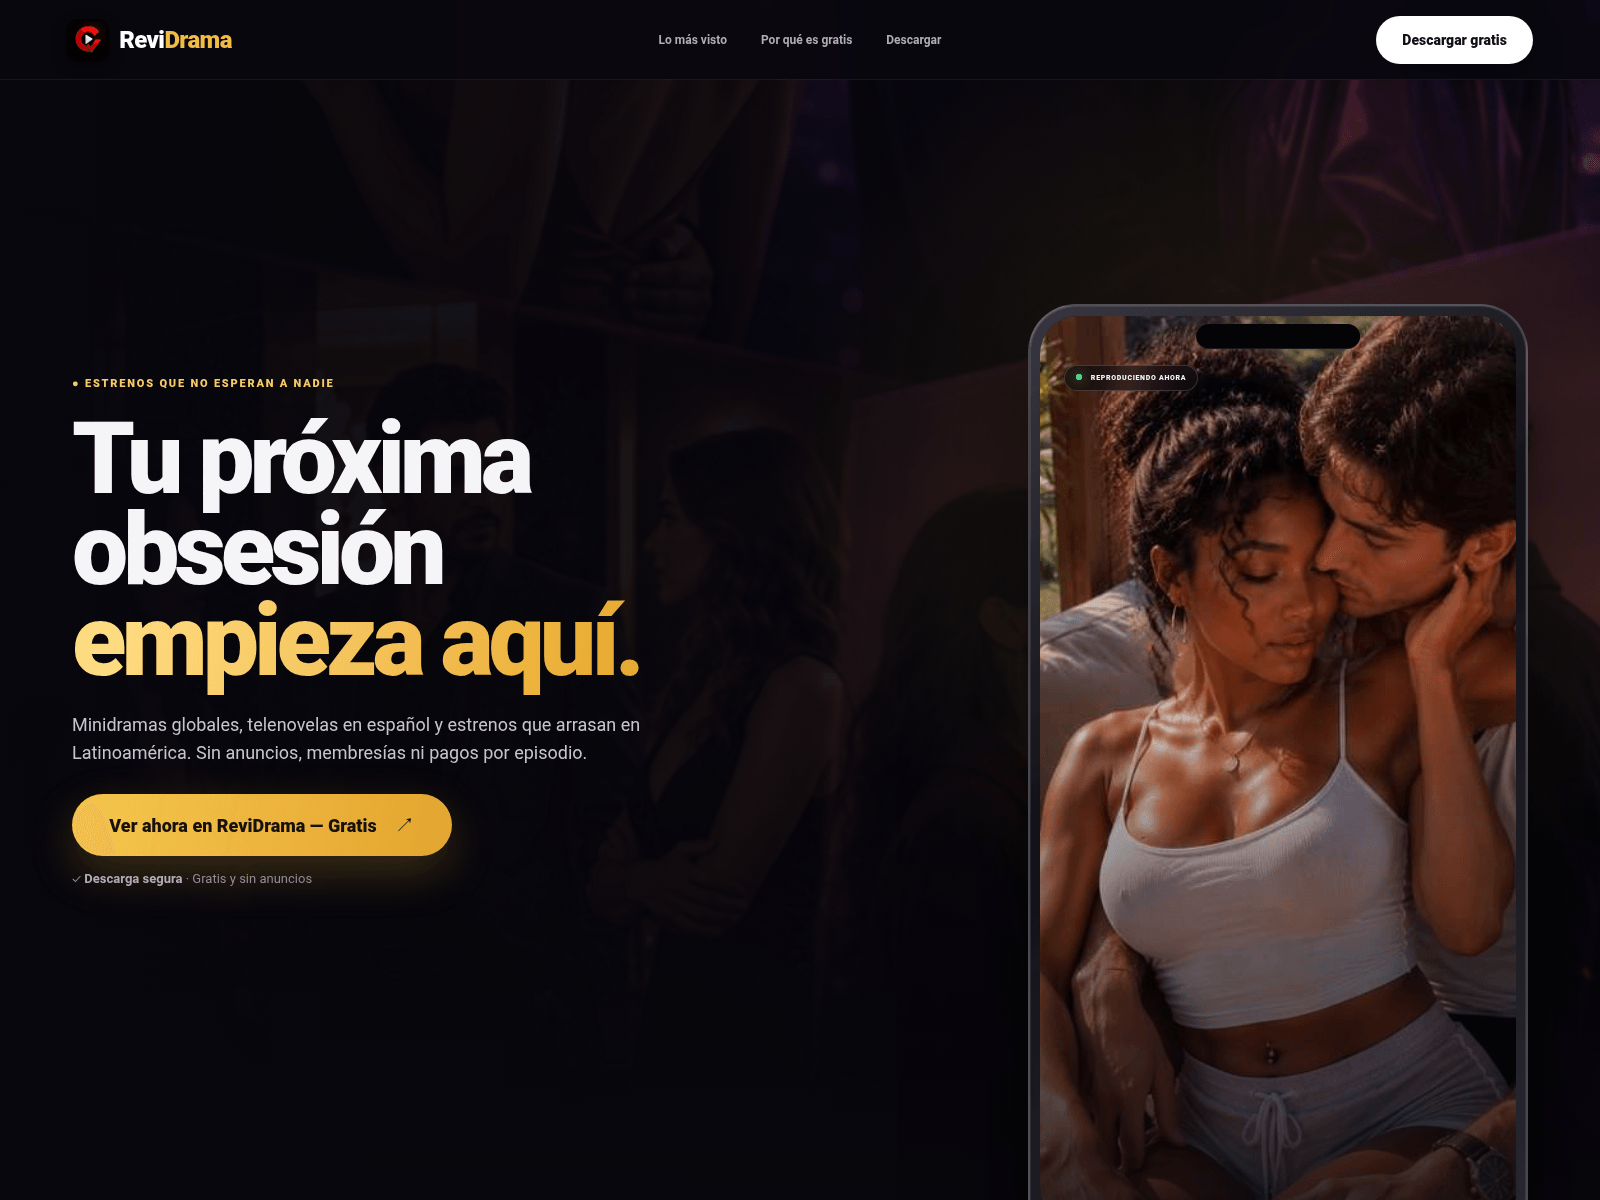
dd4gi.com is an impersonation phishing page that PhishDestroy first detected on 2026-09-03. It was listed by MetaMask's and SEAL's crypto-focused blocklists, which points to wallet users as the intended audience. The page carried the title "ReviDrama — Historias que se quedan contigo," a Spanish-language tagline that looks like a drama or story-review site, while our classification is impersonation phishing. The site has been offline since 2026-09-11, and on 2026-10-19 its DNS was still inactive.
詐欺の手口
Impersonation pages borrow the look or name of a trusted service so visitors lower their guard. They then ask for something valuable, such as login credentials, a wallet connection or a recovery phrase. The ReviDrama branding gives the domain a harmless, entertainment-style face. Anyone who follows the page's prompts risks handing over account access or, if a wallet is involved, signing away control of funds. Once a seed phrase or a signed approval is surrendered, the losses usually cannot be reversed.
証拠
Five of 90 VirusTotal engines flagged the domain as of 2026-09-05: CRDF, Forcepoint ThreatSeeker, Kaspersky, SOCRadar and VIPRE. That count is modest, but it comes from independent vendors and matches the listings on the PhishDestroy, MetaMask and SEAL blocklists. MetaMask and SEAL in particular track threats to crypto users. The domain also appears in four AlienVault OTX threat pulses, so other researchers had tied it to malicious activity as well.
インフラ
The domain was registered on 2026-08-12 through Realtime Register B.V. PhishDestroy detected it 22 days later, and it went offline eight days after that, a short lifespan typical of disposable phishing domains. It resolved to Cloudflare, Inc. address space geolocated to Canada. That means the IP reflects a proxy layer rather than the true origin server. Its TLS certificate came from Google Trust Services, which shows only that the padlock was free and automated, not that the site was legitimate.
What to do
If you entered a password on this site, change it everywhere you reused it and turn on app-based two-factor authentication. If you connected a wallet or signed anything, review and revoke token approvals with a trusted revocation tool. If you typed in a recovery phrase, treat that wallet as compromised and move your funds to a newly created wallet immediately. Defenders should keep dd4gi.com blocked at the DNS and proxy level and search their logs for visits between 2026-08-12 and 2026-09-11. They should also watch for lookalike pages reusing the ReviDrama title.
dd4gi.com was an impersonation phishing page flagged by MetaMask and SEAL, targeting crypto wallet users; offline since 2026-09-11.
AIによる要約
Overview dd4gi.com is an impersonation phishing page that PhishDestroy first detected on 2026-09-03. It was listed by MetaMask's and SEAL's crypto-focused blocklists, which points to wallet users as the intended audience. The page carried the title "ReviDrama — Historias que se quedan contigo," a Spanish-language tagline that looks like a drama or story-review site, while our classification is impersonation phishing. The site has been offline since 2026-09-11, and on 2026-10-19 its DNS was still inactive. How the scam works Impersonation pages borrow the look or name of a trusted service so visitors lower their guard. They then ask for something valuable, such as login credentials, a wallet connection or a recovery phrase. The ReviDrama branding gives the domain a harmless, entertainment-style face. Anyone who follows the page's prompts risks handing over account access or, if a wallet is involved, signing away control of funds. Once a seed phrase or a signed approval is surrendered, the losses usually cannot be reversed. Evidence Five of 90 VirusTotal engines flagged the domain as of 2026-09-05: CRDF, Forcepoint ThreatSeeker, Kaspersky, SOCRadar and VIPRE. That count is modest, but it comes from independent vendors and matches the listings on the PhishDestroy, MetaMask and SEAL blocklists. MetaMask and SEAL in particular track threats to crypto users. The domain also appears in four AlienVault OTX threat pulses, so other researchers had tied it to malicious activity as well. Infrastructure The domain was registered on 2026-08-12 through Realtime Register B.V. PhishDestroy detected it 22 days later, and it went offline eight days after that, a short lifespan typical of disposable phishing domains. It resolved to Cloudflare, Inc. address space geolocated to Canada. That means the IP reflects a proxy layer rather than the true origin server. Its TLS certificate came from Google Trust Services, which shows only that the padlock was free and automated, not that the site was legitimate. What to do If you entered a password on this site, change it everywhere you reused it and turn on app-based two-factor authentication. If you connected a wallet or signed anything, review and revoke token approvals with a trusted revocation tool. If you typed in a recovery phrase, treat that wallet as compromised and move your funds to a newly created wallet immediately. Defenders should keep dd4gi.com blocked at the DNS and proxy level and search their logs for visits between 2026-08-12 and 2026-09-11. They should also watch for lookalike pages reusing the ReviDrama title. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a06891-1638-71f0-80aa-67cbd8a6bdab/ VirusTotal report: https://www.virustotal.com/gui/domain/dd4gi.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=dd4gi.com Archived copy: https://web.archive.org/web/20260903185313/https://dd4gi.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP登録
観測されたタイムラインlast reachable: 2026-09-07 22:14 UTCcurrent episode first observed: 2026-09-30 16:14 UTCobserved RIP window: 2026-09-07 22:14 UTC → 2026-09-30 16:14 UTC · 546.01hmidpoint estimate ≈ 2026-09-19 07:14 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 172.67.219.153


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT