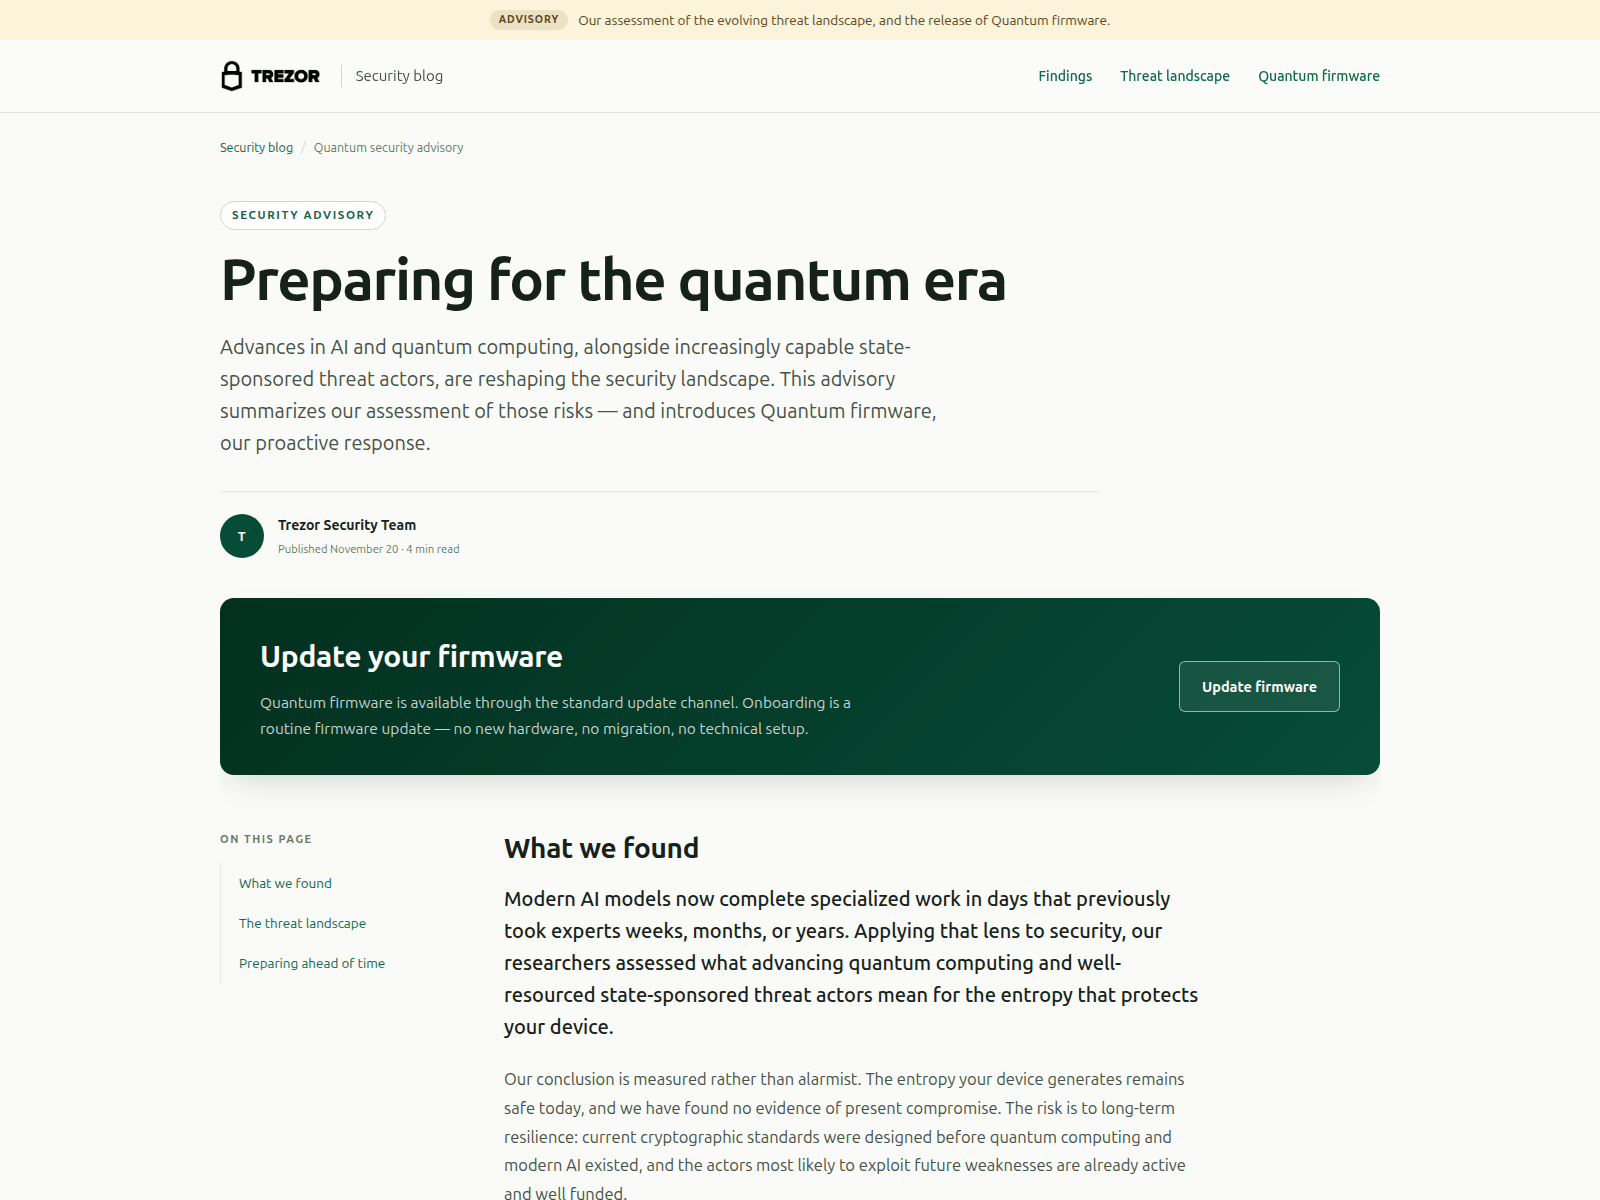
This site mimics the Trezor security blog, featuring an article titled "Preparing for the quantum era" alongside a prominent "Update firmware" button designed to entice visitors. Anyone who interacted with the update prompt should immediately disconnect their hardware wallet and ensure their recovery phrase remains private.
URLScanによるキャプチャ · 2026-11-21 01:06 UTC · SHA-256 78ee665f…ecdb748
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Fake Trezor security blog and firmware update prompt
The page opens with a banner reading "ADVISORY Our assessment of the evolving threat landscape, and the release of Quantum firmware." It mirrors the Trezor brand and presents a security blog titled "Preparing for the quantum era". The article discusses AI, quantum computing, and state-sponsored threat actors, complete with an author attribution to the "Trezor Security Team" and a publication date of November 20. A dark green box in the middle of the page urges visitors to "Update your firmware" with a button labelled "Update firmware". The sidebar and layout match typical corporate blog posts, while the top navigation links point to sections like "Findings", "Threat landscape", and "Quantum firmware".
Recent domain registration and security telemetry
Because it was registered on 20 Nov 2026 and reported the same day, the domain presents a sharp contrast to an established manufacturer like Trezor, whose official domain is trezor.io. Furthermore, urlscan classified the page as malicious, and 3 of 92 VirusTotal engines flagged it on 20 Nov 2026; PhishFort, Fortinet and alphaMountain.ai are among the engines flagging the site. Finally, it still answered requests on 21 Nov 2026 at 02:06 UTC.
Recommended precautions
Visitors should always navigate to the official domain, trezor.io, directly rather than following links from search results or external blogs. If you clicked the update button or entered sensitive details, check your device connections immediately and never input your seed phrase into any website.
blogsite-trezorsuite.com mimics a Trezor blog about quantum threats to prompt firmware updates, flagged by urlscan and 3 VirusTotal engines. Use trezor.io.
AIによる要約
Fake Trezor security blog and firmware update prompt The page opens with a banner reading "ADVISORY Our assessment of the evolving threat landscape, and the release of Quantum firmware." It mirrors the Trezor brand and presents a security blog titled "Preparing for the quantum era". The article discusses AI, quantum computing, and state-sponsored threat actors, complete with an author attribution to the "Trezor Security Team" and a publication date of November 20. A dark green box in the middle of the page urges visitors to "Update your firmware" with a button labelled "Update firmware". The sidebar and layout match typical corporate blog posts, while the top navigation links point to sections like "Findings", "Threat landscape", and "Quantum firmware". Recent domain registration and security telemetry Because it was registered on 20 Nov 2026 and reported the same day, the domain presents a sharp contrast to an established manufacturer like Trezor, whose official domain is trezor.io. Furthermore, urlscan classified the page as malicious, and 3 of 92 VirusTotal engines flagged it on 20 Nov 2026; PhishFort, Fortinet and alphaMountain.ai are among the engines flagging the site. Finally, it still answered requests on 21 Nov 2026 at 02:06 UTC. Recommended precautions Visitors should always navigate to the official domain, trezor.io, directly rather than following links from search results or external blogs. If you clicked the update button or entered sensitive details, check your device connections immediately and never input your seed phrase into any website.
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-21 11:13 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-21 11:13 UTClast content: 2026-11-21 11:13 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 Dominet (HK)
 172.67.190.116


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT