VirusTotal
16 / 89
Denunciar


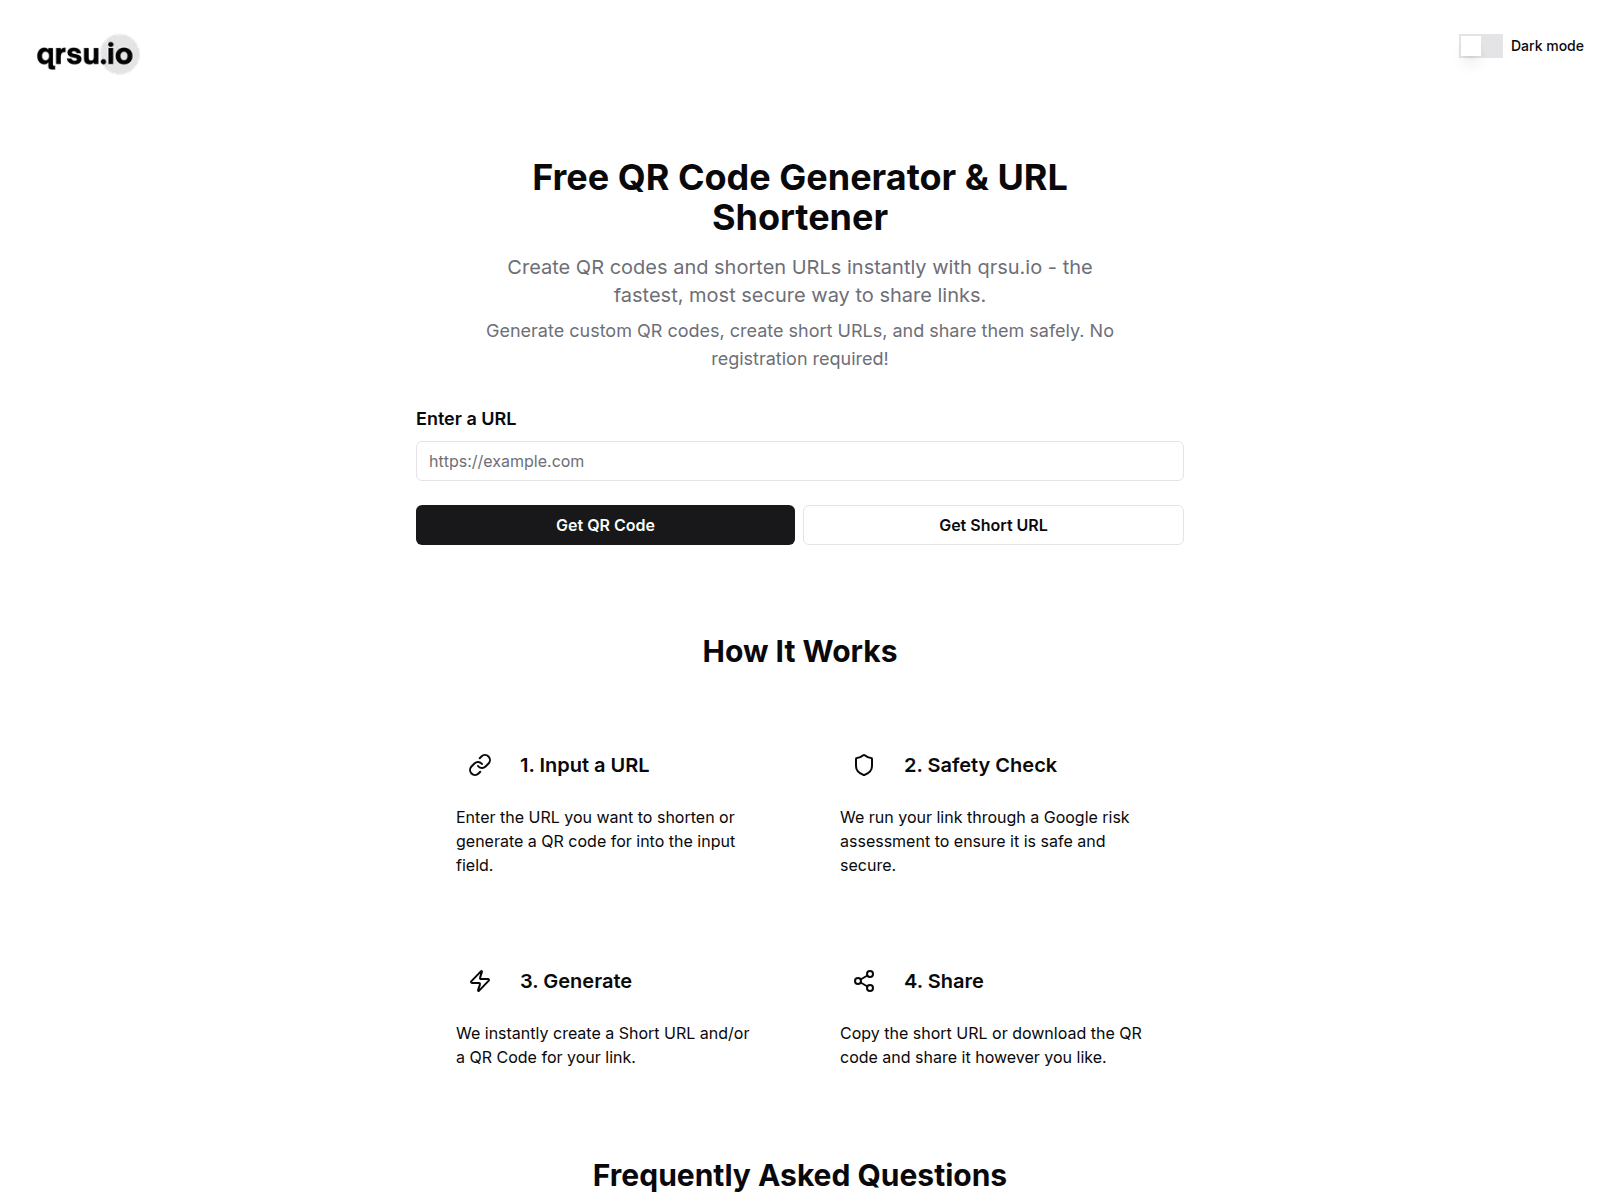
“qrsu.io - QR Code & URL Shortener”
qrsu.io — Último activo conocido (HTTP 200). Suplantación de marca: Google; Tipo de estafa: Credential Phishing. Resumen de las pruebas: VirusTotal 16/89 (ADMINUSLabs, Criminal IP, alphaMountain.ai, BitDefender, Chong Lua Dao); Spamhaus DBL_PHISH; PhishDestroy score 100/100. Registrador: GoDaddy.
El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

16 / 89
1/100
DBL_PHISH
50 community references
Denunciarprovider verdict: clean
Denunciarinforme almacenado
 Denunciar
Análisis finalizado
DenunciarChecked; no threat flag recorded
DenunciarOn 2026‑08‑04 the domain qrsu.io was observed flagged as part of an elevated‑risk generic phishing campaign. VirusTotal reports indicate that 16 of 91 scanning engines returned a malicious classification for the host, demonstrating a moderate consensus of detection across multiple vendors. The domain is listed on a single public security blocklist and is actively blocked by the PhishDestroy filtering service, confirming that at least one commercial anti‑phishing solution has incorporated it into its deny list.
No additional intelligence such as registrar details, registration date, hosting IP, autonomous system, SSL certificate information, or page title has been published in the current feed, so the underlying infrastructure remains opaque. The absence of these data points limits the ability to attribute the infrastructure to a specific operator or to map its network relationships. Nonetheless, the presence on VirusTotal and a known blocklist, combined with the elevated risk rating, suggests that qrsu.io is being used to harvest credentials or otherwise deceive users.
Defenders should add qrsu.io to local deny lists, enforce URL filtering rules that block the domain, and monitor outbound DNS queries for any attempts to resolve it. Network traffic to the domain should be logged and, where possible, redirected to a sandbox for deeper analysis. Continuous re‑evaluation is advised, as additional indicators such as hosting IPs, certificate fingerprints, or page content may emerge in future threat‑intel updates.
Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.
VercelNota del escáner: alive_content: raw=ok; http=200; via=https_proxy; server=Vercel
 (US)
La reputación de Edge-IP no se atribuye a este dominio.
ns72.domaincontrol.comLocation describes the IP network.
7432a8e126ad4da568b9fd0b69a7a1b919972a714818659dd184e39e6d44f58cSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of qrsu.io · checked Aug 4, 2026
16 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.


Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.
Template-based draft · optional AI wording assistance requires separate consent
Cada línea representa un motivo por el que un dominio está vinculado a este servidor. El tamaño de los nodos indica las detecciones de VirusTotal y los nodos con línea discontinua ya están fuera de línea. A continuación se incluyen las listas completas.
Estos informes se resuelven en la misma IP perimetral compartida. Ayudan a descubrir informes, pero no implican una propiedad común ni un servidor de origen compartido.
Estos dominios también se dirigen a los usuarios de Google. Ver todas las amenazas de «Google» →
Registrados a través del mismo proveedor de registro. Un proveedor de registro presta servicio a millones de clientes que no tienen relación entre sí, por lo que este dato solo agrupa los registros, en lugar de demostrar que exista un vínculo.
Informes agregados recientemente de la base de datos PhishDestroy. Estos enlaces de descubrimiento no implican infraestructura ni propiedad compartida.
Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público
Escanear ahoraEnvía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad
DenunciarInformes de phishing recientes y cambios de disponibilidad observados
MonitorizarSupervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.







