Ir al informe de seguridad
Seguridad de dominio e inteligencia sobre amenazas
ouyi.systems favicon

ouyi.systems

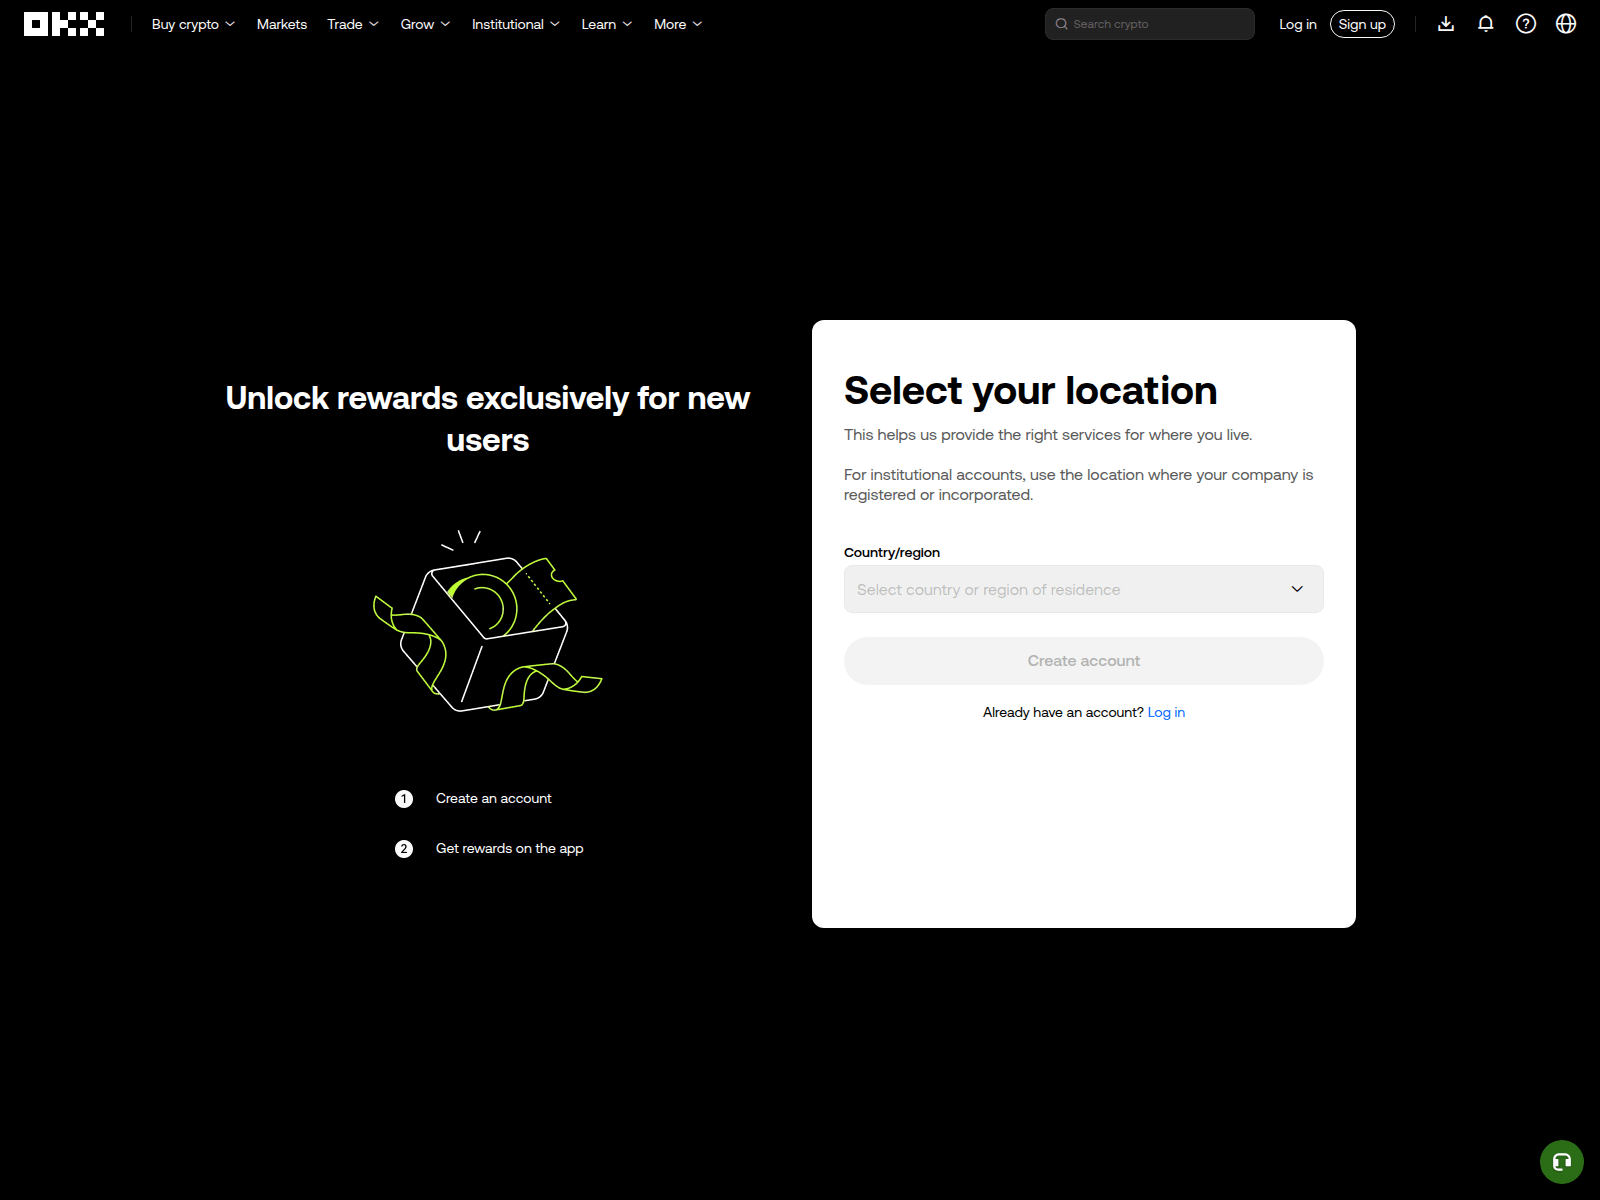
“Earn rewards when you get started on OKX | My referral code: 92497733 | OKX United States”

Registrador
Dynadot
Resolved IP
54.215.31.113
Registered
02/10/2025
Veredicto de amenaza Crítico
Disponibilidad Último activo conocido Última observación de accesibilidad almacenada Observado
Source: HTTP probe
VirusTotal detecciones: 15/89 URLQuery threat systems: 3 alerts Suplantación de marca: OKX
OTX: 23 refs 31/03/2026 OKX 1 Report Sent
API
Este dominio ha sido señalado como malicioso
Motores de seguridad que informan una detección: 15. Tenga extrema precaución: no ingrese credenciales o información personal.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@dynadot.com. The latest stored availability evidence still shows the domain reachable; 6 months has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
6 months
Reports sent
1
Latest case ID
PD-20260331-77232F
Current status
HTTP 302 at latest stored check
Resumen del informe

ouyi.systems — Último activo conocido (HTTP 302). Suplantación de marca: OKX; Tipo de estafa: Brand Impersonation. Resumen de las pruebas: VirusTotal 15/89 (alphaMountain.ai, BitDefender, Chong Lua Dao, ESET, Emsisoft); URLQuery 3 alerts; PhishDestroy score 100/100. Registrador: Dynadot.

El análisis detallado de PhishDestroy AI se mantiene en inglés para conservar el registro forense original.

VirusTotal
VirusTotal
15 det.
URLQuery
URLQuery
3 threat alerts
OTX references
URLScan
URLScan
Certificado TLS
Caducado o no verificado 29d
Edad
1 yr
Estado observado
Último activo conocido 302
PhishDestroy
DestroyList
Incluido
Reports Sent
1

Source evidence

8 sources

VirusTotal

15 / 89

Denunciar

URLQuery

3 threat-system alerts

Denunciar

PhishStats

checked — no match recorded

OTX

23 community references

Denunciar

URLScan capture

informe almacenado

Stored URLScan capture preview
Denunciar

Bloqueos de DNS

12 comprobado — sin bloqueos

Google Safe Browsing

Checked; no threat flag recorded

Denunciar
Inteligencia de seguridad de red
Threat Detection Systems 3 alerts
Detection System Indicator Verdict Alert
Private YARA rules static.okx.com/cdn/assets/okfe/util/ont/5.8.45/ont.js audit Hunting_JS_WebAssembly
Hagezi Threat Feed www.zhgwexpouy.net malicious Sinkholed
DNS4EU www.zhgwexpouy.net malicious Sinkholed

Resumen de las pruebas

Crítico
VirusTotal
15/89
OTX
23 community refs
URLScan
Stored capture

PhishDestroy identifies ouyi.systems as an active crypto drainer domain, posing a high risk to users' cryptocurrency assets. This domain is under investigation for phishing activities specifically targeting crypto wallet credentials and transaction approvals. The site leverages deceptive tactics to trick users into connecting wallets or signing malicious transactions, leading to irreversible fund losses. Technical analysis confirms the domain is operational and distributing malicious payloads, with no current detections on VirusTotal as of the latest scan.

This domain was flagged by PhishDestroy due to its suspicious behavior and lack of legitimate indicators. ouyi.systems resolves to IP 54.215.31.113, registered through Dynadot Inc on October 02, 2025. The domain uses a Let's Encrypt SSL certificate to appear legitimate, though this is a common tactic among malicious actors. As of now, VirusTotal reports 3/95 detections, indicating it has evaded initial detection by antivirus engines. The domain's recent creation date and hosting infrastructure further contribute to its high-risk classification. Trust scores and blocklist entries are pending further investigation, but preliminary data suggests a strong likelihood of malicious intent.

To mitigate risks associated with this crypto drainer, users must avoid interacting with ouyi.systems entirely. If you've already visited the site, disconnect your wallet immediately and revoke any connected permissions via your wallet's settings. Scan your device for malware using reputable security tools like Malwarebytes or Windows Defender. Report the domain to PhishDestroy and your browser's safe browsing program to help block future access. Always verify URLs manually and use hardware wallets for transactions to minimize exposure to drainer scripts. Stay vigilant—crypto drainers often mimic legitimate platforms to exploit user trust.

Análisis de detección y evasión

Comprobación del enmascaramiento y la distribución del tráfico

No se ha observado No se ha observado ningún enmascaramiento en la exploración almacenada.

Observaciones almacenadas de rastreadores frente a navegadores para este servidor, además de una comprobación en tiempo real de la huella digital para sistemas de distribución de tráfico al estilo Keitaro.

Indicador de camuflaje almacenado
No se ha observado
Puntuación de encubrimiento
0/6
Último escaneo de camuflaje
Encabezado del servidor detectado por el escáner
Apache

Nota del escáner: redirect: raw=redirect_302; http=302; via=https_proxy; location=https://yfdabv8.com/?dn=ouyi.systems&accid=710956738&spfwd=1&spmsg=nschttp%3A504; server=Apache

Comprobación de huellas dactilares en directo en TDS
Siete huellas de Keitaro, además de una comparación entre el rastreador y el navegador, que se ejecutan desde el escáner PhishDestroy cuando este panel está abierto.
Esperando

Captura guardada · 3 captures

Título de la página
Earn rewards when you get started on OKX | My referral code: 92497733 | OKX United States
Impersonates
Argent Mastercard OKX Visa
Certificado TLS
Certificate hostname mismatch · Emitido por Let's Encrypt · stored validity ends in 29 days

Domain details

Dominio
Reputación de IP abuse score 7/100 6 reports Fraud OrdersPhishingOpen ProxyPort Scan checked 12/09/2026
OTX Tags 2026-04activeall-domainsblocklistcontentcryptodominiosdrainerfraudlivemonthlyphishdestroyphishingscam
Registrador Dynadot (Unknown)
Contacto de abusoabuse@dynadot.com
Registro de la ICANNICANN Lookup (RDAP) →
RegistroCreado 02/10/2025 — Expires 02/10/2026
Estado HTTP302 Found (Temporary)
Detalles técnicosProvenance & timestamps
Primera detección31/03/2026
DOM Analysisanalyzed 09/10/2026score 98/1004 brand signals
Submitted URLhttp://ouyi.systems/
Favicon Hash
ID del caso
ICANN OVERSIGHT

Acreditación y contexto RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft No se envía nada automáticamente.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
54.215.31.113
Network ASN
AS16509
Organization
AWS EC2 (us-west-1)
Observed location
San Jose, US
Server header
Apache

Servidores de nombres 2

  • ns1.dyna-ns.net
  • ns2.dyna-ns.net

Location describes the IP network.

Certificado TLS

Issuer
Let's Encrypt
Valid from
2026-10-03 15:17:54
Valid until
2027-01-01 15:17:53
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-10-09 19:03:36 UTC
Collection source
PhishDestroy collector
Certificate fingerprint47fc3a02595757109f2e4df79e817853f067618746cca50bee281c4e968b4ecd
Certificate names · 11 SANs
  • 33593.cc
  • 937913.com
  • abbasitvhd.com
  • animze.net
  • arunainfoco.com
  • desi49.biz
  • hondamc2011.com
  • lfav95.cc
  • smileuniverse.online
  • speedone.com.bd
  • thekella.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 54.215.31.113rapiddns.io

Latest Classified Outcome 2026-10-11 10:07:44 UTC

Primary outcome Redirecting reason: HTTP redirect observed 80% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Redirecting Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Redirecting HTTP redirect observed 80% 2026-10-11 10:07:44 UTC
RDAP registration Desconocido
Observed timeline last reachable: 2026-10-11 10:07:44 UTC last content: 2026-10-10 22:07:30 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Tecnologías · 6 identified
O
OneTrust
N
Naver Analytics
Detected via Cloudflare Radar · Wappalyzer engine
Denunciar este dominio Envía pruebas y ayuda a proteger a los demás

Análisis de VirusTotal

15 / Los proveedores de seguridad de 89 marcaron este dominio
View on VT
Last analyzed Previous stored snapshot: 17 detections
alphaMountain.ai
BitDefender
Chong Lua Dao
ESET
Emsisoft
Fortinet
G-Data
Gridinsoft
Kaspersky
Lionic
Netcraft
SOCRadar
Sophos
VIPRE
Webroot

Evidencias archivadas

Wayback Machine Snapshot
Una instantánea histórica está disponible para revisión de evidencia.
View Archive
Análisis del rendimiento del sitio

Google PageSpeed Insights — mobile performance audit of ouyi.systems · checked Mar 31, 2026

30
Poor
Performance
FCP
3.83s
First Contentful Paint
LCP
17.41s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
2984ms
Total Blocking Time
SI
8.45s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-10-09 01:47:23 UTC
    Domain state transitioned from dead to alive.
  2. Domain Status Transition 2026-10-03 02:30:05 UTC
    Domain state transitioned from alive to dead.

Proceso de respuesta ante amenazas Pipeline

Descubrimiento
Analysis
Notifications
Monitoring

13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Amenaza detectada
ouyi.systems detectados y puestos en cola para su análisis completo
31/03/2026
URLScan.io Capture
Almacenado URLScan report with capture artifacts
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
01/04/2026
VirusTotal
15/89 recorded on VirusTotal
11/09/2026
OTX Community References
23 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
01/10/2026
Brand Impersonation
Impersonation of OKX
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
Technical Analysis Recorded
El informe contiene tecnología almacenada o resultados de análisis forenses.
11/10/2026
Site Came Back Online
Domain is responding again — monitoring resumed
09/10/2026
Content Observed Unavailable
El monitoreo registró una respuesta no disponible (HTTP 200); la causa no se estableció de forma independiente.
03/10/2026
Sent Report Recorded
Stored outgoing record associated with registrar Dynadot Inc, 1 abuse contact
abuse@dynadot.com
31/03/2026
Lista de destrucción publicada
31/03/2026
Monitoring Continues
El dominio sigue siendo accesible o tiene acceso restringido; controles futuros pueden actualizar esta observación.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Dominios similares

89 dominios similares almacenados

0kx.com homoglyph 0okx.com insertion 9kx.com replacement 9okx.com insertion akx.com vowel-swap ekx.com vowel-swap gkx.com bitsquatting ikx.com replacement iokx.com insertion kkx.com bitsquatting kokx.com insertion kox.com transposition
Mostrar todo (77)
kx.com omission lkx.com replacement lokx.com insertion mkx.com bitsquatting nkx.com bitsquatting o0kx.com insertion ocx.com bitsquatting oicx.com homoglyph oikx.com insertion oix.com bitsquatting ojkx.com insertion ojx.com bitsquatting ok-x.com hyphenation ok.com omission ok8.com bitsquatting okc.com replacement okd.com replacement okh.com bitsquatting okix.com insertion okjx.com insertion okkx.com insertion oklx.com insertion okmx.com insertion okox.com insertion okp.com bitsquatting oks.com replacement okw.com replacement okx0.com addition okx4.com addition okx5.com addition okxcom.com various okxj.com addition okxr.com addition oky.com bitsquatting okz.com bitsquatting olcx.com homoglyph olex.com homoglyph olkx.com insertion olx.com replacement omkx.com insertion omx.com replacement oox.com bitsquatting opkx.com insertion ox.com omission oxk.com transposition pkx.com replacement ukx.com vowel-swap xn--j1ahw.com cyrillic xn--kx-4ja.com homoglyph okx1.com addition okx2.com addition okx3.com addition okx6.com addition okx8.com addition okx9.com addition okxa.com addition okxb.com addition okxc.com addition okxd.com addition okxf.com addition okxg.com addition okxh.com addition okxi.com addition okxk.com addition okxl.com addition okxm.com addition okxn.com addition okxo.com addition okxp.com addition okxq.com addition okxs.com addition okxt.com addition okxv.com addition okxw.com addition okxx.com addition okxy.com addition okxz.com addition

Reportes de la comunidad

Reportado por 1 miembro de la comunidad; visto por primera vez el 31/03/2026

Reportes almacenados
1
URL únicas reportadas
1
Aceptado1

Datos y informes externos

Instantánea de evidencia enviada
Sent: Ledger records: 1 Case ID: PD-20260331-77232F Recipient: abuse@dynadot.com
Page title stored with report: Earn rewards when you get started on OKX | My referral code: 92497733 | OKX Europe
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 89.1 KB
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Análisis en profundidad

¿Te ha afectado esta página web?

6 evidence signal groups linked 1 reports recorded Último activo conocido
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Si ingresó credenciales de cuenta, información personal o de pago, o descargó un archivo de este dominio, tome medidas inmediatas. A continuación encontrará recursos que le ayudarán a informar el incidente y protegerse.

Europol
Encuentre el canal de denuncia oficial para su país de la UE
National police directory
¡Cuidado con los estafadores que se hacen pasar por empresas de recuperación de datos! Los delincuentes pueden volver a contactar a las víctimas haciéndose pasar por investigadores, abogados o agentes de recuperación. No pague tarifas por adelantado ni comparta credenciales. Más información sobre el fraude en las ayudas de recuperación →

Informa a las autoridades locales

Seleccione su país para obtener contactos oficiales de cibercrimen o crear un borrador de queja →.

directorio de 97 países

Template-based draft · optional AI wording assistance requires separate consent

Borrador asistido por IA: el proveedor de IA procesa los detalles del incidente · Revíselo y envíelo usted mismo

Comprobar cualquier dominio

Análisis de amenazas utilizando listas de bloqueo almacenadas, WHOIS, DNS y evidencia de escaneo público

Escanear ahora

Denunciar un intento de phishing

Envía los dominios sospechosos a nuestra base de datos de amenazas: protege a la comunidad

Denunciar

Flujo de amenazas en tiempo real

Informes de phishing recientes y cambios de disponibilidad observados

Monitorizar

Mantente informado, mantente a salvo

Supervisa las amenazas en tiempo real o impugna esta entrada si crees que se trata de un falso positivo.


Flujo de amenazas en tiempo real Reclamar este anuncio
HTML · IFRAME

Incrustar este informe

Comparte esta información sobre amenazas en tu página web o blog

embed.html
<iframe
  src="https://phishdestroy.io/es/embed/domain/ouyi.systems"
  title="PhishDestroy threat report for ouyi.systems"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>