VirusTotal
19 / 91
Report

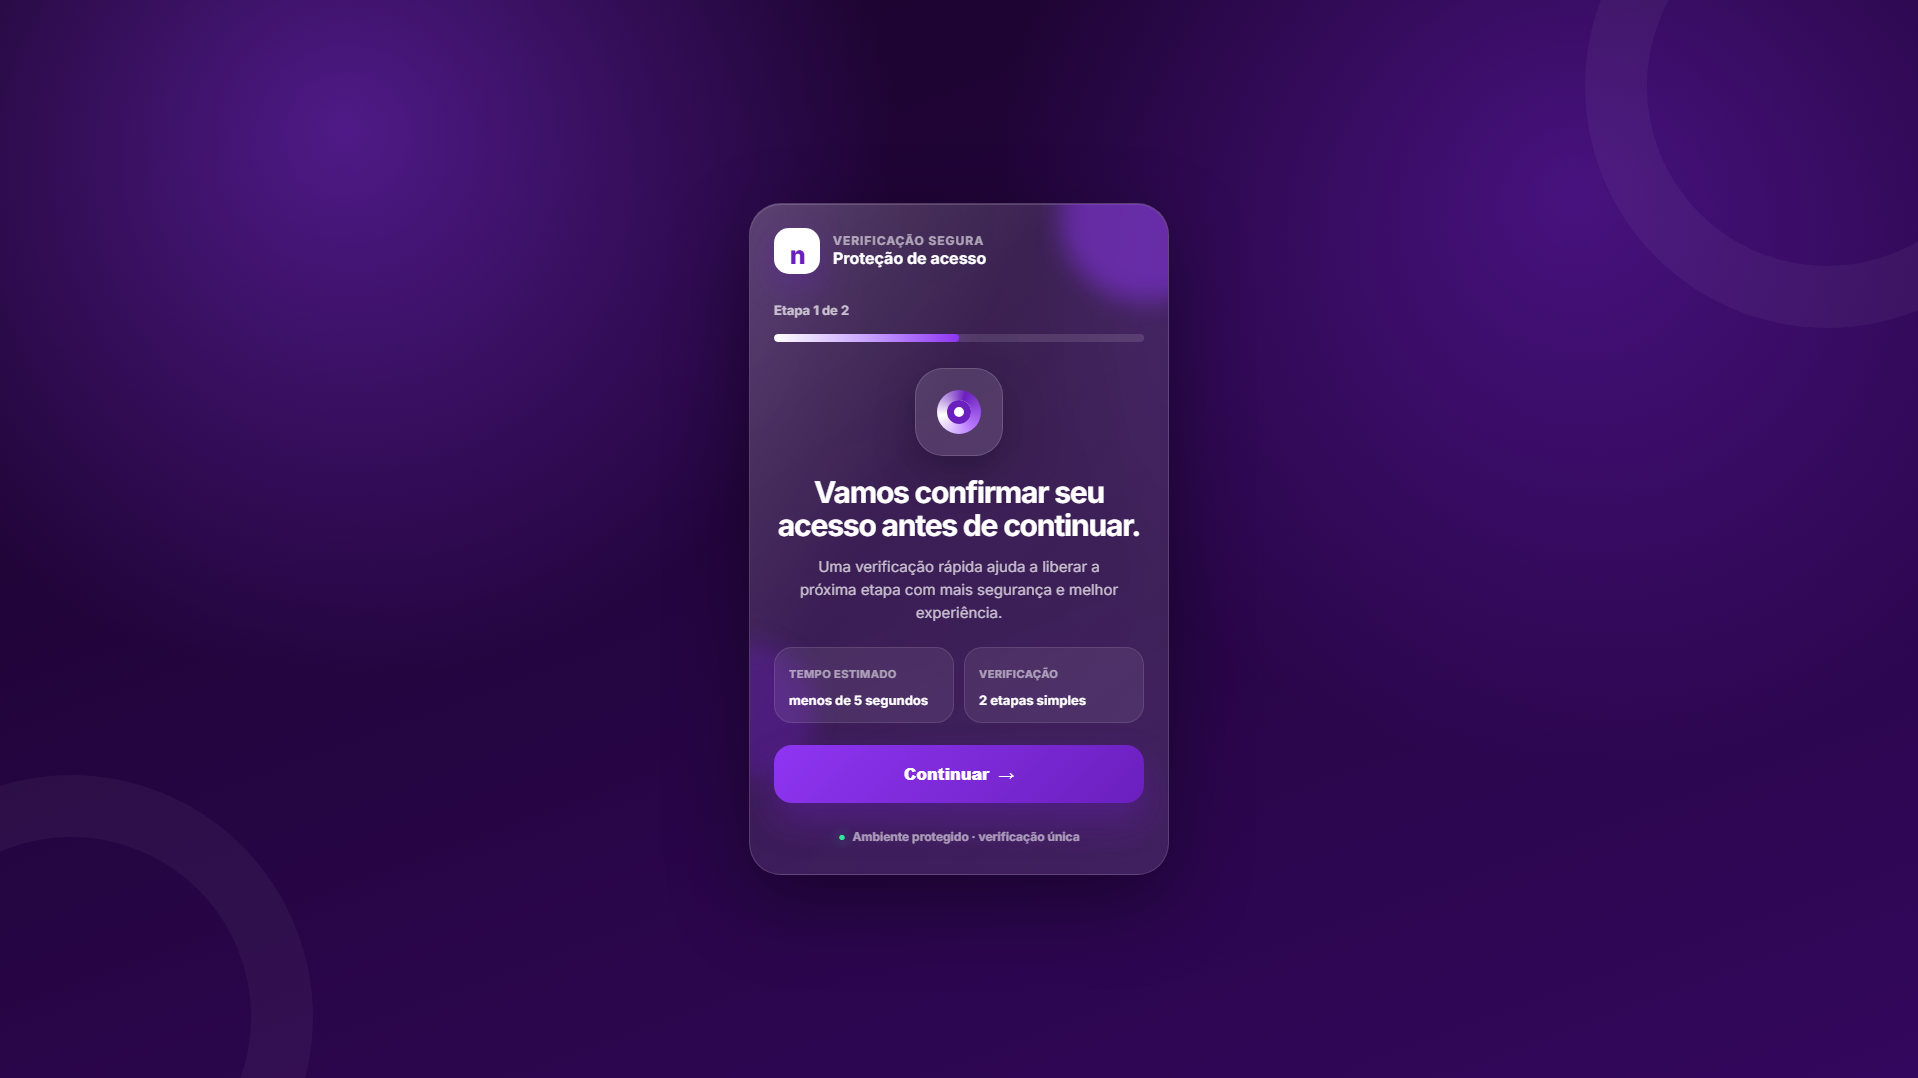
“Verificação de Conta”
portalcredito.online is identified as a high-risk phishing domain currently active and designed to deceive users into submitting sensitive information. The domain is associated with generic phishing attacks, which may involve creating fraudulent login forms or mimicry of legitimate services to harvest user credentials. User engagement with this domain could lead to severe security breaches, including identity theft and financial fraud.
Evidence shows that portalcredito.online was registered through NicNames, Inc, and the domain was created on June 26, 2026. Security evaluations indicate that the domain is flagged by 8 out of 95 security vendors on VirusTotal, suggesting a significant reputation risk. Furthermore, the associated IP address 69.49.241.79 has the potential for malicious activity, warranting additional investigation and monitoring. The domain's presence in multiple security blocklists emphasizes its harmful intent and high-risk status within the cybersecurity landscape.
Users who have interacted with portalcredito.online are advised to take immediate action. It is recommended to change any credentials that may have been submitted and to monitor financial accounts for suspicious activity. Users should also consider running security scans on their devices to detect any potential threats, which could include malware downloaded inadvertently during visits to this site. Educating oneself about phishing tactics can greatly reduce the likelihood of future compromises.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
Scanner note: transient_502: raw=transient_502; http=502; via=http_proxy
 (SE)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
ns10.uadns.comns11.uadns.comns12.uadns.comLocation describes the IP network.
c175b0e184dfdb4c0f96e94da9ec1545ba8ebf08133ee5d1424ce66bf6ec0ce8acessonext.online.marcossantos1781381403023.0791640.meusitehostgator.com.brflowcentral.online.marcossantos1781381403023.0791640.meusitehostgator.com.brgestaoplus.online.marcossantos1781381403023.0791640.meusitehostgator.com.brhubfinance.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnexoclientes.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnexofinance.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnuguia.onlinenuguia.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnuonlinevip.onlinenuonlinevip.online.marcossantos1781381403023.0791640.meusitehostgator.com.brportalcredito.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.acessonext.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.flowcentral.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.gestaoplus.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.hubfinance.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nexoclientes.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nexofinance.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nuguia.onlinewww.nuguia.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nuonlinevip.onlinewww.nuonlinevip.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.portalcredito.onlinewww.portalcredito.online.marcossantos1781381403023.0791640.meusitehostgator.com.brSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
7 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
Multiple reports share this IP.
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive