VirusTotal
16 / 91
Report

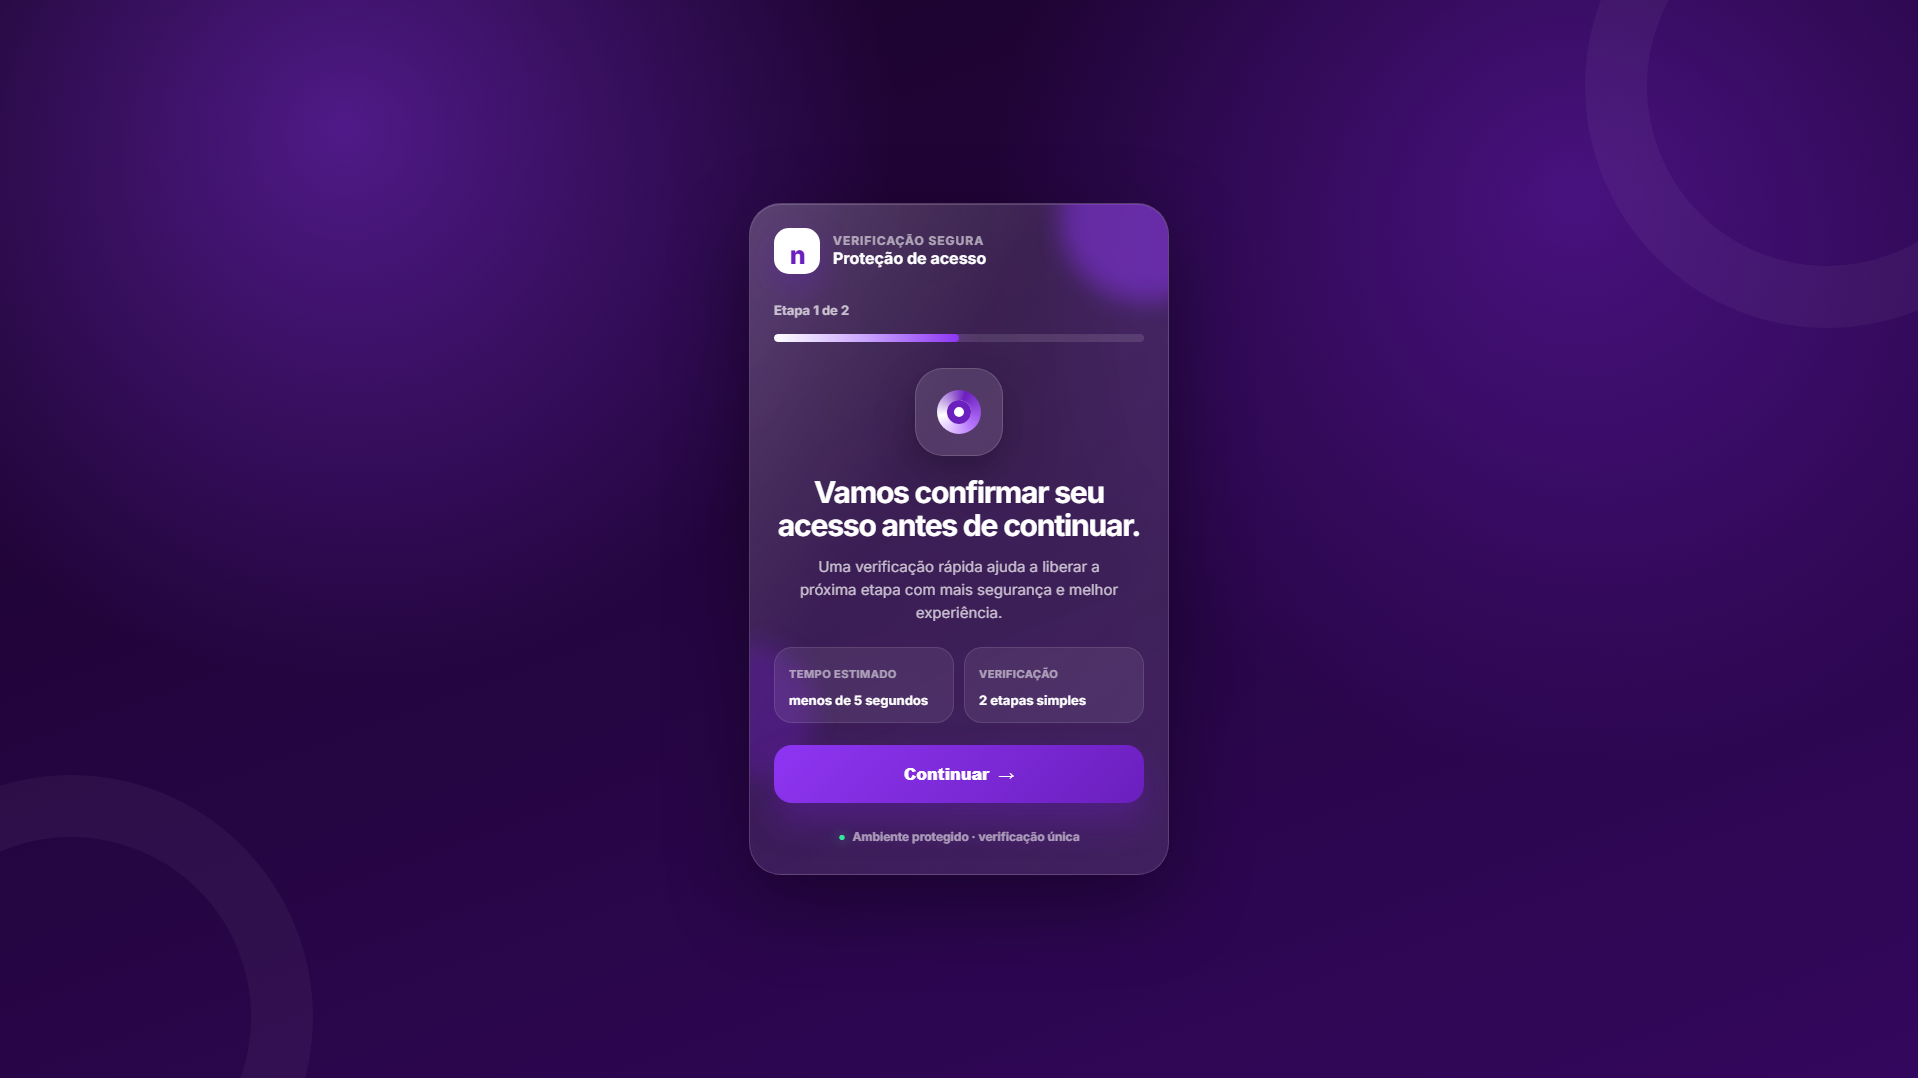
“Verificação de Conta”
The domain nuorigin.online is currently classified as a high-risk generic phishing threat, with active phishing activities detected. As of the latest intelligence, the domain continues to operate and poses significant risks to internet users by potentially impersonating well-known brands or entities to steal sensitive information.
Data analysis reveals that nuorigin.online is flagged by 15 out of 95 security vendors on VirusTotal, indicating the presence of harmful phishing activities. The domain was registered through Dynadot Inc and currently resolves to the IP address 69.49.241.79. It was created on June 27, 2026, which suggests it is relatively new but actively engaging in malicious activities. Additionally, the domain is listed on one security blocklist, further affirming its threat status.
Given the domain's active status and high-risk level, it is crucial for users and organizations to implement security measures to protect against potential phishing attacks associated with nuorigin.online. Recommendations include monitoring network traffic for connections to the IP 69.49.241.79, using email filtering tools to block any communications from this domain, and educating users about identifying phishing attempts. Continual vigilance and proactive threat intelligence updates are advised to mitigate risks effectively.
The page served one response to a browser-like visitor and another to a crawler or security scanner. Cloaking exists only to keep reviewers away from the real landing page.
content_divergenceScanner note: transient_502: raw=transient_502; http=502; via=http_proxy
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
ns1.dyna-ns.netns2.dyna-ns.netLocation describes the IP network.
deb75b28b86bcca674fa98fe55ac4516e01c5db0338b43b244c05cb4409aa1f9nufusion.onlinenufusion.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnumatrix.onlinenumatrix.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnuorbit.onlinenuorbit.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnuorigin.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnuproxima.onlinenuproxima.online.marcossantos1781381403023.0791640.meusitehostgator.com.brnuviahub.onlinenuviahub.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nufusion.onlinewww.nufusion.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.numatrix.onlinewww.numatrix.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nuorbit.onlinewww.nuorbit.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nuorigin.onlinewww.nuorigin.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nuproxima.onlinewww.nuproxima.online.marcossantos1781381403023.0791640.meusitehostgator.com.brwww.nuviahub.onlinewww.nuviahub.online.marcossantos1781381403023.0791640.meusitehostgator.com.brSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
9 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
Same favicon hash or the same page title as this host.
Multiple reports share this IP.
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive