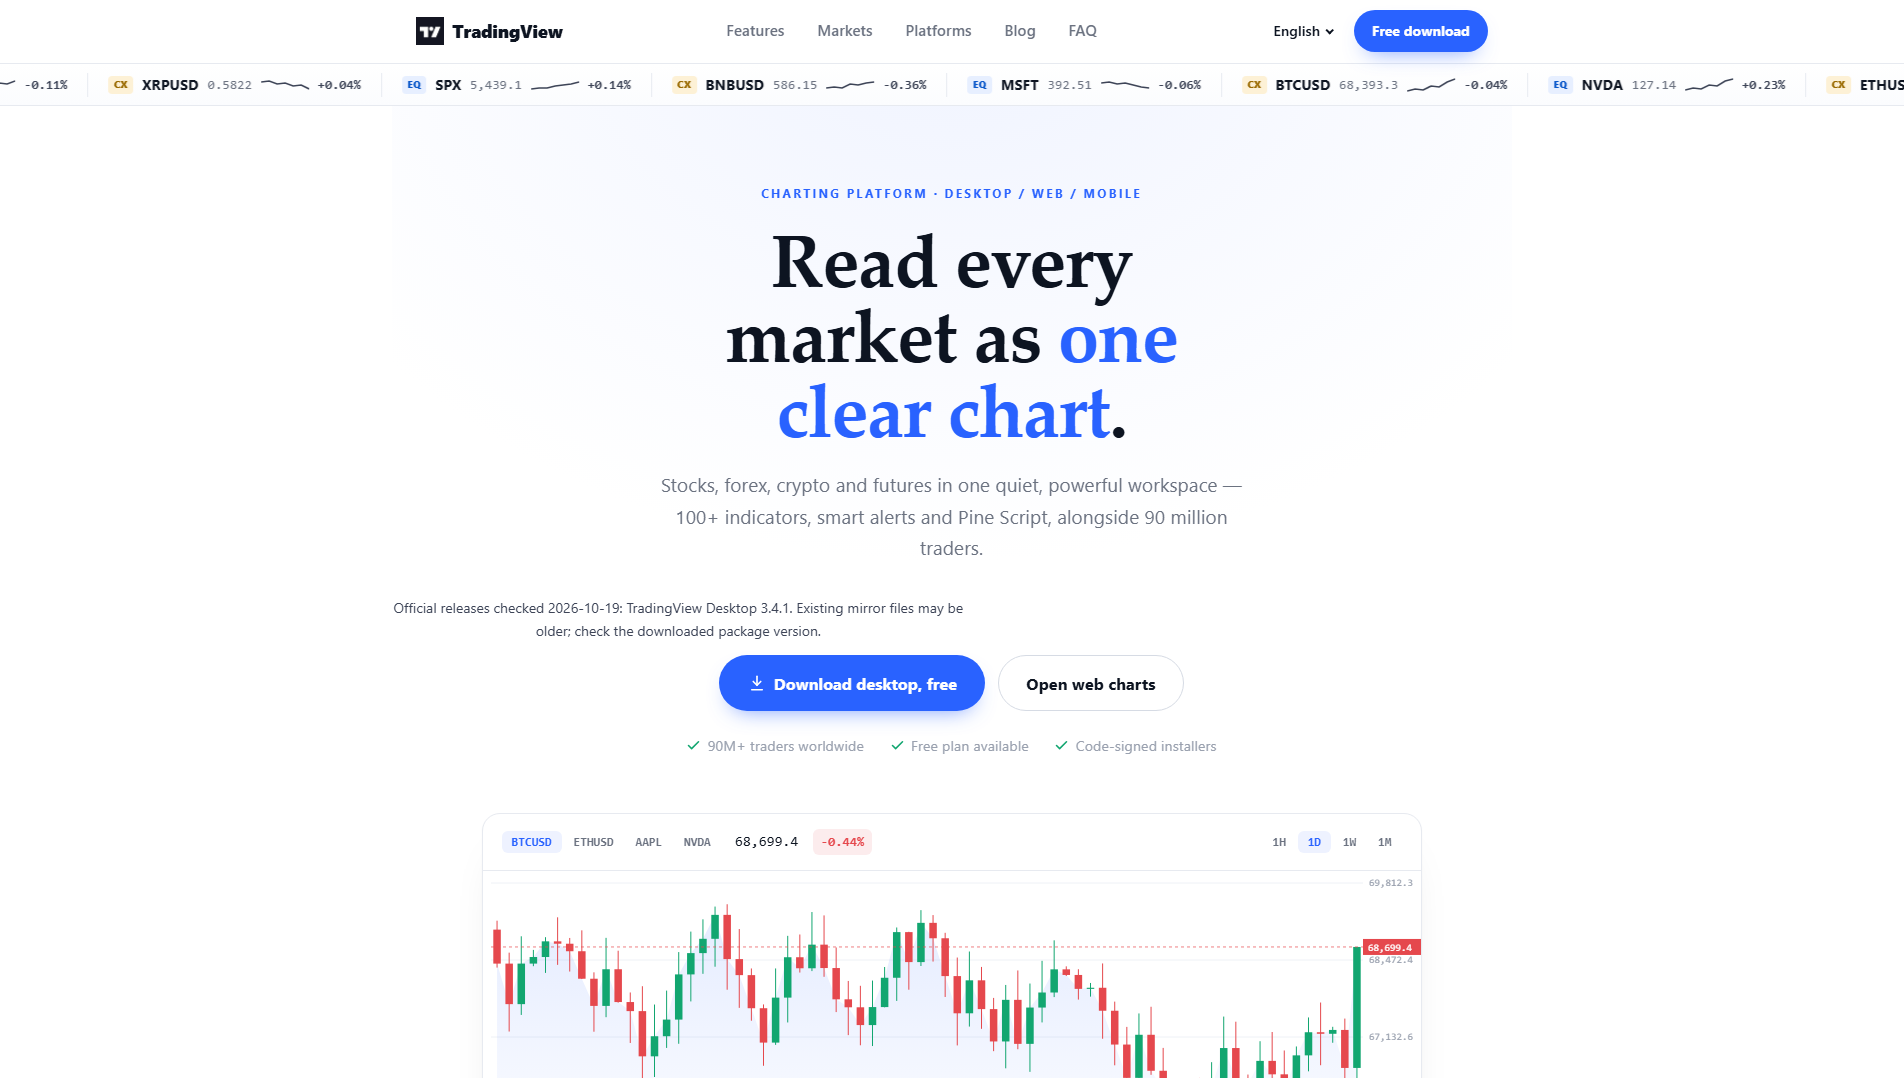
PhishDestroy first recorded btc-tradingview.st on 2026-10-23. Stored VirusTotal result: 10/92 engines flagged. Malicious: 8. Suspicious: 2. Analysis time (as stored): 2026-10-22 12:03 UTC. Retrieved (as stored): 2026-10-23 01:41 UTC. Listed by external blocklists: MetaMask, SEAL.
Page title: “TradingView | Choose a language”
More about the sources
Recorded security signals
Stored VirusTotal result: 10/92 engines flagged. Malicious: 8. Suspicious: 2. Analysis time (as stored): 2026-10-22 12:03 UTC. Retrieved (as stored): 2026-10-23 01:41 UTC. Listed by external blocklists: MetaMask, SEAL. Use caution — do not enter credentials or personal information.
Expert view has every section: DNS, TLS, network requests, hashes and the raw JSON.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@avenacloud.com. The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
1 month
Reports sent
1
Latest case ID
PD-20261023-891938
Current status
HTTP 200 at latest stored check
Analysis
Domain summary
PhishDestroy first recorded btc-tradingview.st on 2026-10-23. Stored VirusTotal result: 10/92 engines flagged. Malicious: 8. Suspicious: 2. Analysis time (as stored): 2026-10-22 12:03 UTC. Retrieved (as stored): 2026-10-23 01:41 UTC. Listed by external blocklists: MetaMask, SEAL. Risk: critical (evidence score 100/100). Registrar: IncogNET. Status: Last known active. Hosting: S.C. INFOTECH-GRUP S.R.L. PhishDestroy sent 1 abuse report. Do not enter credentials or connect a wallet.
PhishDestroy added btc-tradingview.st to its internal blocklist because Google Safe Browsing reported it as a social‑engineering threat. The recorded page title is “TradingView | Choose a language”. The domain was first seen by PhishDestroy on 2026-10-23 and returned an HTTP 200 response at that time.
How the scam works
The classification indicates the site could be used for social‑engineering attacks that aim to trick visitors into revealing credentials or personal data. No specific malicious functionality was observed on the page beyond a language‑selection interface, so the risk is inferred from external warnings rather than concrete behavior.
Evidence
Google Safe Browsing flagged the domain as SOCIAL_ENGINEERING on 2026-10-23. VirusTotal scanned the domain on 2026-10-22 and reported 8 malicious and 2 suspicious detections out of 92 engines, with vendors such as BitDefender, G‑Data, AlphaMountain.ai and Google Safe Browsing labeling it phishing. urlscan.io captured the site on 2026-10-20; its engine score was 96 with a malicious tag, but the overall verdict was clean. PhishDestroy’s internal blocklist marks the domain as blocked, while external blocklists returned zero hits on 2026-10-22, and OTX listed no pulses on 2026-10-23.
Infrastructure
The domain was registered with IncogNET on 2026-07-24, giving it an age of about 86 days at the time of observation. The recorded IP address is 132.243.164.53, belonging to S.C. INFOTECH‑GRUP S.R.L. in Moldova. The TLS certificate is issued by Let’s Encrypt, valid until 2027-01-20, and the server header identified Nginx with HSTS enabled; DNS records listed four ISP‑provided name servers.
What to do
Do not enter any credentials or personal information on this site. If you have already submitted login details, change the associated passwords immediately and monitor the accounts for unauthorized activity. Defenders should block connections to btc-tradingview.st, log any attempts to the recorded IP, and continue monitoring threat feeds for new indicators.
This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.
Open report Title, description and generation record
The narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.
AI title
btc-tradingview.st — Suspicious Domain
AI description
PhishDestroy flagged btc-tradingview.st as suspicious after Google Safe Browsing marked it a social site; the page shows a TradingView language selector.
AI summary
Overview PhishDestroy added btc-tradingview.st to its internal blocklist because Google Safe Browsing reported it as a social‑engineering threat. The recorded page title is “TradingView | Choose a language”. The domain was first seen by PhishDestroy on 2026-10-23 and returned an HTTP 200 response at that time. How the scam works The classification indicates the site could be used for social‑engineering attacks that aim to trick visitors into revealing credentials or personal data. No specific malicious functionality was observed on the page beyond a language‑selection interface, so the risk is inferred from external warnings rather than concrete behavior. Evidence Google Safe Browsing flagged the domain as SOCIAL_ENGINEERING on 2026-10-23. VirusTotal scanned the domain on 2026-10-22 and reported 8 malicious and 2 suspicious detections out of 92 engines, with vendors such as BitDefender, G‑Data, AlphaMountain.ai and Google Safe Browsing labeling it phishing. urlscan.io captured the site on 2026-10-20; its engine score was 96 with a malicious tag, but the overall verdict was clean. PhishDestroy’s internal blocklist marks the domain as blocked, while external blocklists returned zero hits on 2026-10-22, and OTX listed no pulses on 2026-10-23. Infrastructure The domain was registered with IncogNET on 2026-07-24, giving it an age of about 86 days at the time of observation. The recorded IP address is 132.243.164.53, belonging to S.C. INFOTECH‑GRUP S.R.L. in Moldova. The TLS certificate is issued by Let’s Encrypt, valid until 2027-01-20, and the server header identified Nginx with HSTS enabled; DNS records listed four ISP‑provided name servers. What to do Do not enter any credentials or personal information on this site. If you have already submitted login details, change the associated passwords immediately and monitor the accounts for unauthorized activity. Defenders should block connections to btc-tradingview.st, log any attempts to the recorded IP, and continue monitoring threat feeds for new indicators. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a15821-06de-7292-9cf9-ebac987088ac/ Cloudflare Radar report: https://radar.cloudflare.com/scan/b0436c25-d621-438f-8bbb-93b3a9d87651 Stored capture screenshot: https://urlscan.io/screenshots/01a15821-06de-7292-9cf9-ebac987088ac.png Cloudflare Radar screenshot (2026-10-23T01:42:42Z): https://screenshots.phishdestroy.io/cf/b0436c25-d621-438f-8bbb-93b3a9d87651.png URLScan screenshot (2026-08-02T03:18:15Z): https://screenshots.phishdestroy.io/us/019fc07a-86ad-737b-bc92-9657346e49fb.png URLScan capture report: https://urlscan.io/result/019fc07a-86ad-737b-bc92-9657346e49fb/ URLScan screenshot (2026-08-12T03:19:25Z): https://screenshots.phishdestroy.io/us/019ff3fb-4155-72dc-859a-45925b8f106f.png URLScan capture report: https://urlscan.io/result/019ff3fb-4155-72dc-859a-45925b8f106f/ URLScan screenshot (2026-08-26T03:02:55Z): https://screenshots.phishdestroy.io/us/01a03c05-34d9-7132-a1e1-687ec1e17dd4.png URLScan capture report: https://urlscan.io/result/01a03c05-34d9-7132-a1e1-687ec1e17dd4/ URLScan screenshot (2026-09-29T13:13:57Z): https://screenshots.phishdestroy.io/us/01a0ed4c-c39d-74e3-9570-7f060dcaf8c3.png URLScan capture report: https://urlscan.io/result/01a0ed4c-c39d-74e3-9570-7f060dcaf8c3/ URLScan screenshot (2026-10-02T01:30:26Z): https://screenshots.phishdestroy.io/us/01a0fa3b-d07d-727a-b58d-f6034c7c3c5a.png URLScan capture report: https://urlscan.io/result/01a0fa3b-d07d-727a-b58d-f6034c7c3c5a/ URLScan screenshot (2026-10-16T07:01:32Z): https://screenshots.phishdestroy.io/us/01a14383-e818-71b0-b0ac-b231db45dd09.png URLScan capture report: https://urlscan.io/result/01a14383-e818-71b0-b0ac-b231db45dd09/ VirusTotal report: https://www.virustotal.com/gui/domain/btc-tradingview.st Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=btc-tradingview.st Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Ogurl: https://btc-tradingview.st/; Title: TradingView | Choose a language; Ogtype: website; Robots: index,follow; Ogimage: https://btc-tradingview.st/logo.png; Ogtitle: TradingView | Choose a language; Ogsitename: TradingView 图表指南; Themecolor: #ffffff; Description: Choose 简体中文, 繁體中文 or English to open TradingView.; Twittercard: Summary large image; Canonicalurl: https://btc-tradingview.st/; Ogdescription: Choose 简体中文, 繁體中文 or English to open TradingView.
No sri: https://a.dffg524.cn/tracker.php, https://static.cloudflareinsights.com/beacon.min.js, https://dl.kuaipan.cyou/daily-links.v1.js; Third party scripts: 3
Headers: Server: nginx; Content type: text/html; Strict transport security: max-age=31536000
Questions about btc-tradingview.st
Is btc-tradingview.st legit?
PhishDestroy rates btc-tradingview.st as critical risk (evidence score 100/100) from the recorded evidence; it was first recorded on 2026-10-23. Stored VirusTotal result: 10/92 engines flagged. Malicious: 8. Suspicious: 2. Analysis time (as stored): 2026-10-22 12:03 UTC. Retrieved (as stored): 2026-10-23 01:41 UTC. Listed by external blocklists: MetaMask, SEAL. The local score and a listing do not prove fraud. Check each source’s date and the exact URL.
Is btc-tradingview.st safe to connect a wallet?
Because of the risk signals above, do not connect a wallet, sign messages or approve token permissions on btc-tradingview.st. A confirmed blockchain transaction cannot be reversed.
What should I do if I used btc-tradingview.st?
Entered a password — change it on that service and on every other site where you used the same password
Turn on two-factor authentication — where the service offers it; an authenticator app is stronger than SMS codes
Paid or entered card or bank details — contact your bank or payment service through the contacts on your card or its official website
Connected a wallet but signed nothing — disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds
Approved token spending (approve / permit) — revoke that approval with a token-approval checker
Shared a seed phrase or private key — move the remaining funds to a new wallet with a new seed phrase; the exposed wallet is no longer safe
Downloaded a file — do not open it and scan the device with security software
Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority. A report does not guarantee that money is returned. Step-by-step help: emergency guide.
IP Reputation132.243.164.530/100abuse score · abuse reports about this server's IP address, not about the domain; higher = worseThis IP address has a low abuse score, but the domain itself is recognized as phishing.0 reportschecked 2026-11-22last reported · outside the counted period
DOM Analysisanalyzed 2026-10-23score 95/1003 brand signals
Submitted URLhttp://btc-tradingview.st/
Favicon Hash
Case ID
Observed page title
TradingView | Choose a language
Automated brand references
AcrossAppleCurve
TLS Certificate
Issued by Let's Encrypt / YR1· stored validity ends in 58 days
Network & certificates
Stored technical evidence
Network & DNS
Resolved IP
132.243.164.53
Network ASN
AS201670
Organization
S.C. INFOTECH-GRUP S.R.L.
Observed location
Chisinau, MD
Server header
nginx
Nameservers 4
ns.isp.fo
ns.isp.gd
ns.isp.st
ns.isp.vg
SOA
nsname: ns.isp.st
hostmaster: hostmaster.btc-tradingview.st
serial: 2026102201
refresh: 3600
retry: 900
expire: 604800
minttl: 86400
Location describes the IP network.
TLS certificate
Issuer
Let's Encrypt / YR1
Valid from
2026-10-22 09:20:12
Valid until
2027-01-20 09:20:11
Hostname match
Yes
Validity
Within stored validity dates
Collection source
PhishDestroy collector
Certificate fingerprint2e31924d701aa7f47a6521935927df5f253f01c864530666f186b56ee52bd51aCertificate names · 1 SAN
btc-tradingview.st
Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Evidence layersAvailability: Content servingContent: Content served at rootDNS: Resolved
Latest HTTP observationLive contentOrdinary HTTP content served90%2026-11-22 11:45 UTC
RDAP registration
Observed timelinelast reachable: 2026-11-22 11:45 UTClast content: 2026-11-22 11:45 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Network requests that the URLScan browser recorded while loading the page. URLScan does not provide a hash for every request. PhishDestroy retrieved this list on 2026-10-29 02:00 UTC.
Recorded events: 13. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
The domain remains reachable or access-restricted; future checks may update this observation.
ongoing
Recorded activity
6 entries
Lifecycle
Domain registered
VirusTotal analysis with detections+90 d 12 h
Added to PhishDestroy+13 h 37 min
First abuse report sent+40 min
Reported 91 d 2 h after registration
AlienVault OTX
1 community references
+30 d 3 h
Abuse report sent
PD-20261023-891938 · Receipt 81623
abuse@avenacloud.com
+2 min
URLScan
Page captured
+28 min
Wayback Machine
Page archived
+9 min
Added to PhishDestroy
btc-tradingview.st
+13 h 37 min
VirusTotal
10/92 engine detections
How we investigate & report
Public scans, evidence and abuse channels
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
01Public scans & evidence collection10 sources and tool groups
Inspect the public DNS, TLS, HTTP and technology surface.
02Abuse reports & follow-upRegistrar, hosting and security channels
Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
Send the report. Keep outgoing report records and recipient information when available.
Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Names that imitate the brand, found by dnstwist. A similar name alone does not prove the same owner.
Report all
A similar name alone does not prove fraud. Send the list to services that check each address themselves. Report a domain as phishing only if you saw a fake page on it.
Nothing matches. Clear the search or choose another filter.
burve.fiBit flipVariant of curve.fiA 76.76.21.21NS ns01.trademarkarea.comcruve.fiSwapped charactersVariant of curve.fiA 176.65.144.109NS 1-you.njalla.nocur.ve.fiSplit into subdomainVariant of curve.fiA 64.190.63.222MX localhostNS ns1.sedoparking.comcure.fiMissing characterVariant of curve.fiA 64.190.63.222MX localhostNS ns1.sedoparking.comcurve-fi.comVariantVariant of curve.fiA 195.201.128.179NS ns1.dns-redirect.comcurvefi.comVariantVariant of curve.fiA 172.65.185.109NS sp1.gname-dns.comcurvi.fiVowel swapVariant of curve.fiA 88.99.26.106MX mail.curvi.fiNS ns1.polar55.comcurvo.fiVowel swapVariant of curve.fiA 185.53.179.145NS ns1.eurodns.comcuvre.fiSwapped charactersVariant of curve.fiA 176.65.144.109NS 1-you.njalla.no
Related Infrastructure & Reports
Stored relationships are grouped by the exact matching attribute. A shared provider or registrar alone does not prove common ownership.
Same registrar: IncogNET6
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
You are not alone and there is nothing to be ashamed of. Scammers are sophisticated criminals who exploit trust. Reporting your experience is the most powerful weapon against fraud — your report can prevent others from becoming victims and help law enforcement take action. Secure your accounts and funds first, then report. If credentials were compromised, report immediately. Do not engage with recovery scammers.
Act on what you actually did. Entered a password: change it, and wherever you reused it. Paid or gave card details: contact your bank or payment service. Downloaded a file: scan the device. Then report the incident.
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
What should I do immediately?
Urgent
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Entered a password — change it on that service and on every other site where you used the same password
Turn on two-factor authentication — where the service offers it; an authenticator app is stronger than SMS codes
Paid or entered card or bank details — contact your bank or payment service through the contacts on your card or its official website
Downloaded a file — do not open it and scan the device with security software
Shared a seed phrase or private key — move the remaining funds to a new wallet with a new seed phrase; the exposed wallet is no longer safe
Connected a wallet but signed nothing — disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds
Approved token spending (approve / permit) — revoke that approval with a token-approval checker (revoke.cash)
Sent crypto — save the transaction hash, your address and the receiving address; blockchain transactions cannot be reversed
What information should I collect for my report?
FBI guidelines
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
Exact dates & times — of each transaction and first contact with scammer
Screenshots — scam website, chat messages, emails, wallet transactions, social media
All URLs & domains used by the scammer (including btc-tradingview.st)
Communications — emails, texts, phone numbers, usernames the scammer used
Even if you don't have all details — file a report anyway. Partial information still helps investigations.
Where should I report the scam?
FBI IC3 — Internet Crime Complaint Center (US federal reporting)
Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
Local police — creates an official record, even if they can't act immediately
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
How do phishing scams typically work?
Fake websites — pixel-perfect clones of legitimate sites with slightly altered domains
Pig butchering — trust built over weeks via Telegram/WhatsApp/dating apps, then money stolen
Recovery scams — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
AI-powered scams — deepfakes, automated phishing, and AI-generated sites making fraud harder to detect
How can I protect myself in the future?
Bookmark official sites — never click links from emails, DMs, or ads
Verify domains — check on PhishDestroy before interacting. Check HTTPS, spelling, domain age
"Too good to be true" = scam — guaranteed returns, celebrity endorsements, urgent deadlines
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials.Learn more about recovery fraud →
About this reportSources, observation dates and corrections
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

 132.243.164.53


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT