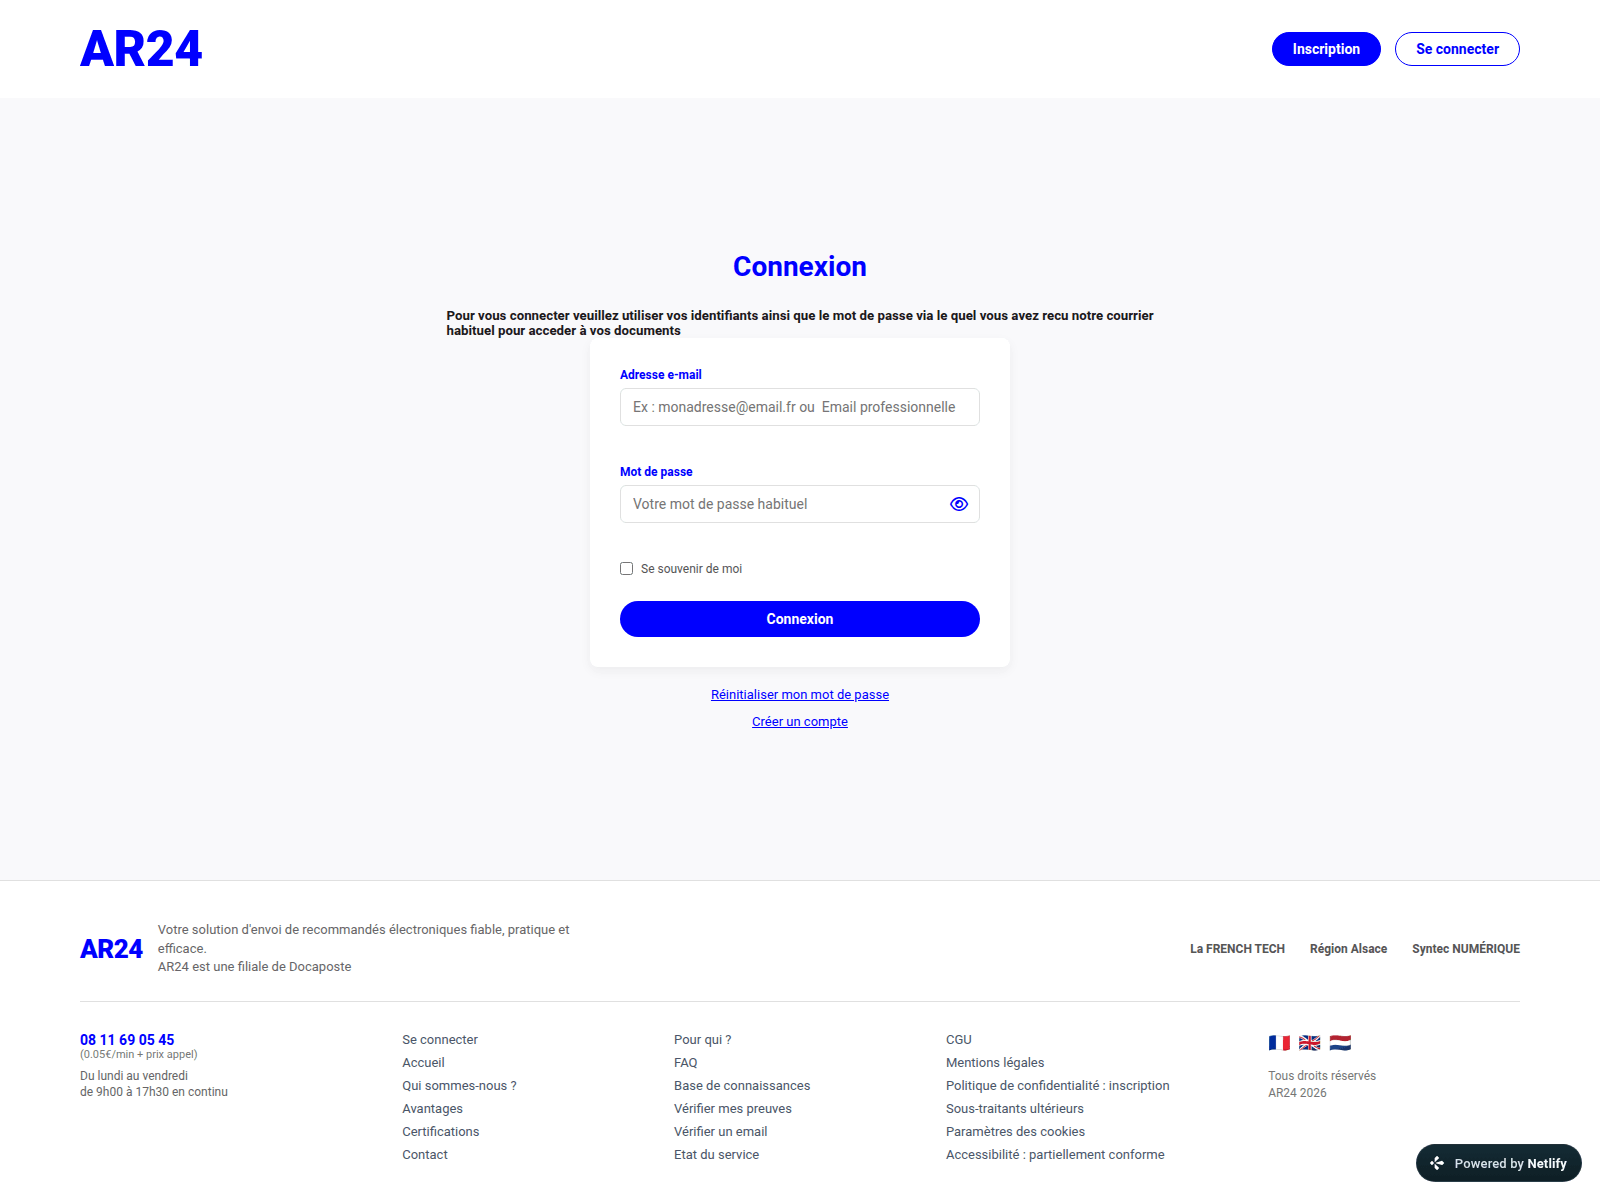
The page at ar24courrielfr10.netlify.app presents a fake Ar24 login portal designed to capture email addresses and account passwords. If you entered your credentials here, change your password immediately on the official service and review your account activity.
Page title: “Connexion - AR24 PRO”
More about the sources
Recorded security signals
Stored VirusTotal result: 19/92 engines flagged. Malicious: 18. Suspicious: 1. Analysis time (as stored): 2026-11-21 00:08 UTC. Retrieved (as stored): 2026-11-21 17:50 UTC. Listed by external blocklists: PhishFeed. Use caution — do not enter credentials or personal information.
Expert view has every section: DNS, TLS, network requests, hashes and the raw JSON.
Analysis
Domain summary
PhishDestroy first recorded ar24courrielfr10.netlify.app on 2026-11-21. Stored VirusTotal result: 19/92 engines flagged. Malicious: 18. Suspicious: 1. Analysis time (as stored): 2026-11-21 00:08 UTC. Retrieved (as stored): 2026-11-21 17:50 UTC. Listed by external blocklists: PhishFeed. Risk: critical (evidence score 100/100). Status: Last known active. Hosting: Amazon.com, Inc. Do not enter credentials or connect a wallet.
The page displays the blue Ar24 brand logo at the top left alongside top-bar buttons for inscription and connection. In the centre, a prominent heading reads "Connexion" with descriptive French text instructing users to enter their usual credentials and password "via le quel vous avez reçu notre courrier habituel pour acceder à vos documents". The white login card contains input fields for an email address labeled "Adresse e-mail" with an example format, and a password field labeled "Mot de passe" accompanied by a show-password icon. Below these fields sits a "Se souvenir de moi" checkbox, a blue "Connexion" submission button, and recovery links for resetting passwords or creating an account. The footer includes support phone numbers, French compliance badges, and branding indicating use of the netlify.app platform.
Credential harvesting risk and telemetry
By providing email and password inputs inside the form, visitors risk handing over their active authentication data directly to unauthorised operators. urlscan classified the page as malicious, 19 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and PhishFeed blocks it, with Kaspersky, ESET and BitDefender among them, so this is a known data-collection page rather than a one-off false alarm. Its PhishDestroy evidence score is 75/100 (critical).
Recommended actions for affected users
Visitors who typed their credentials into the form must immediately update their password on genuine accounts and review active sessions for suspicious activity. Report the hosting abuse to netlify.app and avoid entering personal details on unsolicited subdomains.
Source evidenceVirusTotal 19 / 925 sources
SourceResultRecorded · UTCOpen
VirusTotal
19 / 92 engine detections
Analysis:
Open report VirusTotalOriginal source recordObserved: 15 fields
This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.
Open report Page code check by a separate monitor · 10 / 100 · 2026-11-21 19:20 UTC
This dated monitor analysis is separate from the primary PhishDestroy analysis above. A heuristic score is not a measured probability.
Heuristic score
10
Analyzed at
2026-11-21T19:20:10Z
Source timestamp
2026-11-21 20:20:10
Technical metadata
PhishDestroy narrative
Narrative generation metadata
Open report Title, description and generation record
The narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.
AI title
ar24courrielfr10.netlify.app — Ar24 login clone on Netlify
AI description
ar24courrielfr10.netlify.app mimics the Ar24 sign-in interface to steal passwords, flagged by urlscan and 19 VirusTotal engines. Protect your account.
AI summary
Ar24 login page clone layout The page displays the blue Ar24 brand logo at the top left alongside top-bar buttons for inscription and connection. In the centre, a prominent heading reads "Connexion" with descriptive French text instructing users to enter their usual credentials and password "via le quel vous avez reçu notre courrier habituel pour acceder à vos documents". The white login card contains input fields for an email address labeled "Adresse e-mail" with an example format, and a password field labeled "Mot de passe" accompanied by a show-password icon. Below these fields sits a "Se souvenir de moi" checkbox, a blue "Connexion" submission button, and recovery links for resetting passwords or creating an account. The footer includes support phone numbers, French compliance badges, and branding indicating use of the netlify.app platform. Credential harvesting risk and telemetry By providing email and password inputs inside the form, visitors risk handing over their active authentication data directly to unauthorised operators. urlscan classified the page as malicious, 19 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and PhishFeed blocks it, with Kaspersky, ESET and BitDefender among them, so this is a known data-collection page rather than a one-off false alarm. Its PhishDestroy evidence score is 75/100 (critical). Recommended actions for affected users Visitors who typed their credentials into the form must immediately update their password on genuine accounts and review active sessions for suspicious activity. Report the hosting abuse to netlify.app and avoid entering personal details on unsolicited subdomains.
Is ar24courrielfr10.netlify.app a legitimate Ar24 website?
No, it is hosted on netlify.app rather than official infrastructure. urlscan classified the page as malicious, 19 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and PhishFeed blocks it.
What happens if I entered my password on ar24courrielfr10.netlify.app?
The operators behind the page instantly capture your submitted credentials and can attempt to access your real accounts. You should immediately change your password on the legitimate Ar24 service and enable multi-factor authentication.
Why does the page ask for my email and password?
The page uses the Ar24 brand styling and the "Connexion" form to deceive users into surrendering their login details. No actual document retrieval takes place through this form.
DOM Analysisanalyzed 2026-11-21score 10/1001 brand signal
Submitted URLhttp://ar24courrielfr10.netlify.app/
Favicon Hash
Observed page title
Connexion - AR24 PRO
Automated brand references
Base
TLS Certificate
Issued by DigiCert Global G2 TLS RSA SHA256 2020 CA1· stored validity ends in 117 days
Network & certificates
Stored technical evidence
Network & DNS
Shared CDN edge
Resolved IP
63.176.8.218
Network ASN
AS16509
AS name
AMAZON-02 - Amazon.com, Inc., US
Organization
AWS EC2 (eu-central-1)
Observed location
Frankfurt, DE
Server header
Netlify
Edge-IP reputation is not attributed to this domain.
Nameservers 4
dns1.p01.nsone.net
dns2.p01.nsone.net
dns3.p01.nsone.net
dns4.p01.nsone.net
Location describes the IP network.
TLS certificate
Issuer
DigiCert Global G2 TLS RSA SHA256 2020 CA1
Valid from
2026-02-16 00:00:00
Valid until
2027-03-19 23:59:59
Hostname match
Yes
Validity
Within stored validity dates
Collection source
PhishDestroy collector
Certificate fingerprintbc3a8134c21a842e64ea34d488826dd2ba50f59a3bcbaed1e6b71a4242de1478Certificate names · 2 SANs
*.netlify.app
netlify.app
Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Evidence layersAvailability: Content servingContent: Content served at rootDNS: Stale
Latest HTTP observationLive contentOrdinary HTTP content served90%2026-11-22 11:59 UTC
RDAP registration
Observed timelinelast reachable: 2026-11-22 11:59 UTClast content: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Technologies · 2 identified
N
Netlify
PaaSCDN
Netlify providers hosting and server-less backend services for web applications and static websites.
Network requests that the URLScan browser recorded while loading the page. URLScan does not provide a hash for every request. PhishDestroy retrieved this list on 2026-11-21 17:46 UTC.
Loads saved data; the suspicious site is not opened.
Captured network requests
#
Network request
HTTP method · status
Type
Uncompressed size
Response body SHA-256
Stored observation history2
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Availability monitor · Recorded state
Serving page content
page content returned
Domain monitor · First collection record
Reachable
All retained availability observations3
Source: availability monitor. Every retained observation remains separate, including records with the same date or evidence hash but different sources or DNS states. An unknown state is not proof that the site is offline.
Recorded events: 11. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
The domain remains reachable or access-restricted; future checks may update this observation.
ongoing
Recorded activity
4 entries
Lifecycle
Domain registered
VirusTotal analysis with detections+3118 d 1 h
Added to PhishDestroy+17 h 32 min
Cloudflare Radar
Phishing
+9 min
Added to PhishDestroy
ar24courrielfr10.netlify.app
same minute
URLScan
Page captured
+17 h 32 min
VirusTotal
19/92 engine detections
How we investigate & report
Public scans, evidence and abuse channels
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
01Public scans & evidence collection10 sources and tool groups
Inspect the public DNS, TLS, HTTP and technology surface.
02Abuse reports & follow-upRegistrar, hosting and security channels
Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
Send the report. Keep outgoing report records and recipient information when available.
Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Supporting signal — Shares a page feature, infrastructure or a collector label; not proof of one operator.
Each spoke is one reason a domain is linked to this report. Node size marks VirusTotal detections, dashed nodes are already offline, and the full lists follow below. Full list of related reports
Content matches3
Same favicon file hash, or a recorded page title that starts with the same 20 characters. A content match does not establish a shared phishing kit or owner.
You are not alone and there is nothing to be ashamed of. Scammers are sophisticated criminals who exploit trust. Reporting your experience is the most powerful weapon against fraud — your report can prevent others from becoming victims and help law enforcement take action. Secure your accounts and funds first, then report. If credentials were compromised, report immediately. Do not engage with recovery scammers.
Act on what you actually did. Entered a password: change it, and wherever you reused it. Paid or gave card details: contact your bank or payment service. Downloaded a file: scan the device. Then report the incident.
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
What should I do immediately?
Urgent
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Entered a password — change it on that service and on every other site where you used the same password
Turn on two-factor authentication — where the service offers it; an authenticator app is stronger than SMS codes
Paid or entered card or bank details — contact your bank or payment service through the contacts on your card or its official website
Downloaded a file — do not open it and scan the device with security software
Shared a seed phrase or private key — move the remaining funds to a new wallet with a new seed phrase; the exposed wallet is no longer safe
Connected a wallet but signed nothing — disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds
Approved token spending (approve / permit) — revoke that approval with a token-approval checker (revoke.cash)
Sent crypto — save the transaction hash, your address and the receiving address; blockchain transactions cannot be reversed
What information should I collect for my report?
FBI guidelines
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
Exact dates & times — of each transaction and first contact with scammer
Screenshots — scam website, chat messages, emails, wallet transactions, social media
All URLs & domains used by the scammer (including ar24courrielfr10.netlify.app)
Communications — emails, texts, phone numbers, usernames the scammer used
Even if you don't have all details — file a report anyway. Partial information still helps investigations.
Where should I report the scam?
FBI IC3 — Internet Crime Complaint Center (US federal reporting)
Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
Local police — creates an official record, even if they can't act immediately
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
How do phishing scams typically work?
Fake websites — pixel-perfect clones of legitimate sites with slightly altered domains
Pig butchering — trust built over weeks via Telegram/WhatsApp/dating apps, then money stolen
Recovery scams — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
AI-powered scams — deepfakes, automated phishing, and AI-generated sites making fraud harder to detect
How can I protect myself in the future?
Bookmark official sites — never click links from emails, DMs, or ads
Verify domains — check on PhishDestroy before interacting. Check HTTPS, spelling, domain age
"Too good to be true" = scam — guaranteed returns, celebrity endorsements, urgent deadlines
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials.Learn more about recovery fraud →
About this reportSources, observation dates and corrections
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.


 63.176.8.218


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT