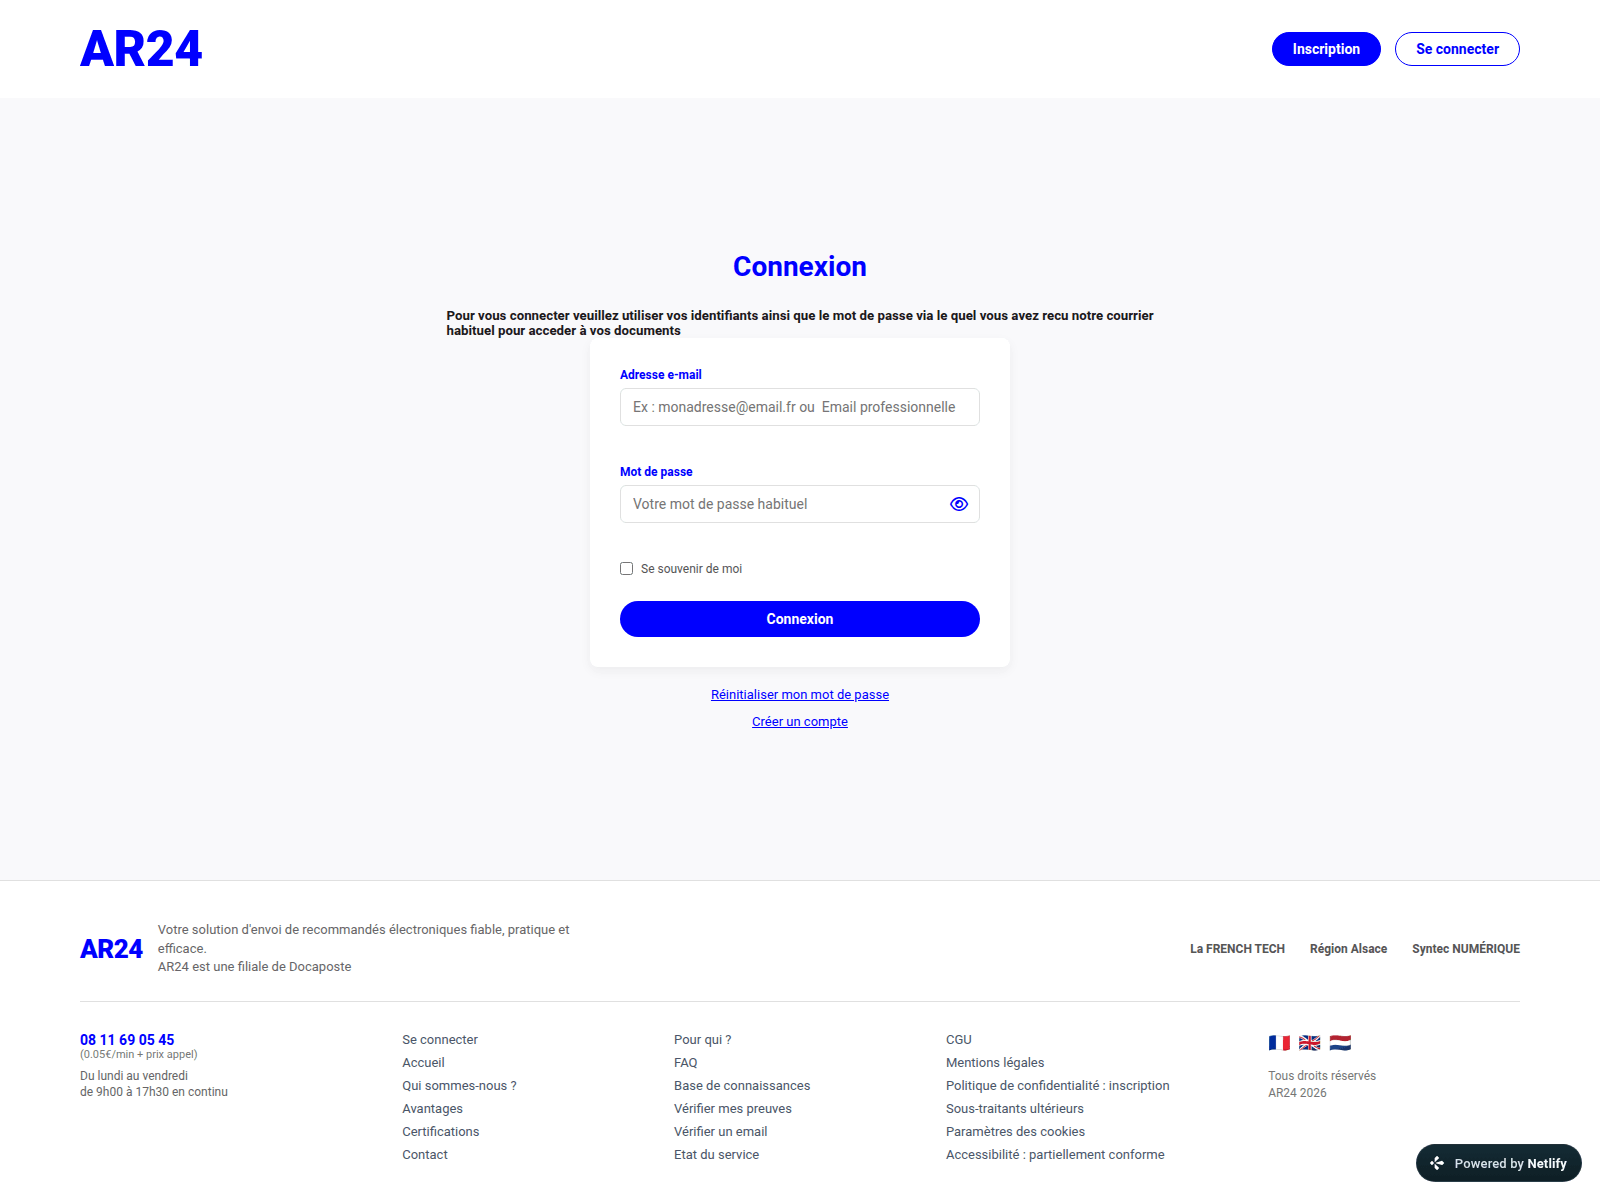
The page at ar24courrielfr10.netlify.app presents a fake Ar24 login portal designed to capture email addresses and account passwords. If you entered your credentials here, change your password immediately on the official service and review your account activity.
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Ar24 login page clone layout
The page displays the blue Ar24 brand logo at the top left alongside top-bar buttons for inscription and connection. In the centre, a prominent heading reads "Connexion" with descriptive French text instructing users to enter their usual credentials and password "via le quel vous avez reçu notre courrier habituel pour acceder à vos documents". The white login card contains input fields for an email address labeled "Adresse e-mail" with an example format, and a password field labeled "Mot de passe" accompanied by a show-password icon. Below these fields sits a "Se souvenir de moi" checkbox, a blue "Connexion" submission button, and recovery links for resetting passwords or creating an account. The footer includes support phone numbers, French compliance badges, and branding indicating use of the netlify.app platform.
Credential harvesting risk and telemetry
By providing email and password inputs inside the form, visitors risk handing over their active authentication data directly to unauthorised operators. urlscan classified the page as malicious, 19 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and PhishFeed blocks it, with Kaspersky, ESET and BitDefender among them, so this is a known data-collection page rather than a one-off false alarm. Its PhishDestroy evidence score is 75/100 (critical).
Recommended actions for affected users
Visitors who typed their credentials into the form must immediately update their password on genuine accounts and review active sessions for suspicious activity. Report the hosting abuse to netlify.app and avoid entering personal details on unsolicited subdomains.
ar24courrielfr10.netlify.app — Ar24 login clone on Netlify
AIによる説明
ar24courrielfr10.netlify.app mimics the Ar24 sign-in interface to steal passwords, flagged by urlscan and 19 VirusTotal engines. Protect your account.
AIによる要約
Ar24 login page clone layout The page displays the blue Ar24 brand logo at the top left alongside top-bar buttons for inscription and connection. In the centre, a prominent heading reads "Connexion" with descriptive French text instructing users to enter their usual credentials and password "via le quel vous avez reçu notre courrier habituel pour acceder à vos documents". The white login card contains input fields for an email address labeled "Adresse e-mail" with an example format, and a password field labeled "Mot de passe" accompanied by a show-password icon. Below these fields sits a "Se souvenir de moi" checkbox, a blue "Connexion" submission button, and recovery links for resetting passwords or creating an account. The footer includes support phone numbers, French compliance badges, and branding indicating use of the netlify.app platform. Credential harvesting risk and telemetry By providing email and password inputs inside the form, visitors risk handing over their active authentication data directly to unauthorised operators. urlscan classified the page as malicious, 19 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and PhishFeed blocks it, with Kaspersky, ESET and BitDefender among them, so this is a known data-collection page rather than a one-off false alarm. Its PhishDestroy evidence score is 75/100 (critical). Recommended actions for affected users Visitors who typed their credentials into the form must immediately update their password on genuine accounts and review active sessions for suspicious activity. Report the hosting abuse to netlify.app and avoid entering personal details on unsolicited subdomains.
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Stale
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:59 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:59 UTClast content: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 2 identified
N
Netlify
PaaSCDN
Netlify providers hosting and server-less backend services for web applications and static websites.


 63.176.8.218


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT