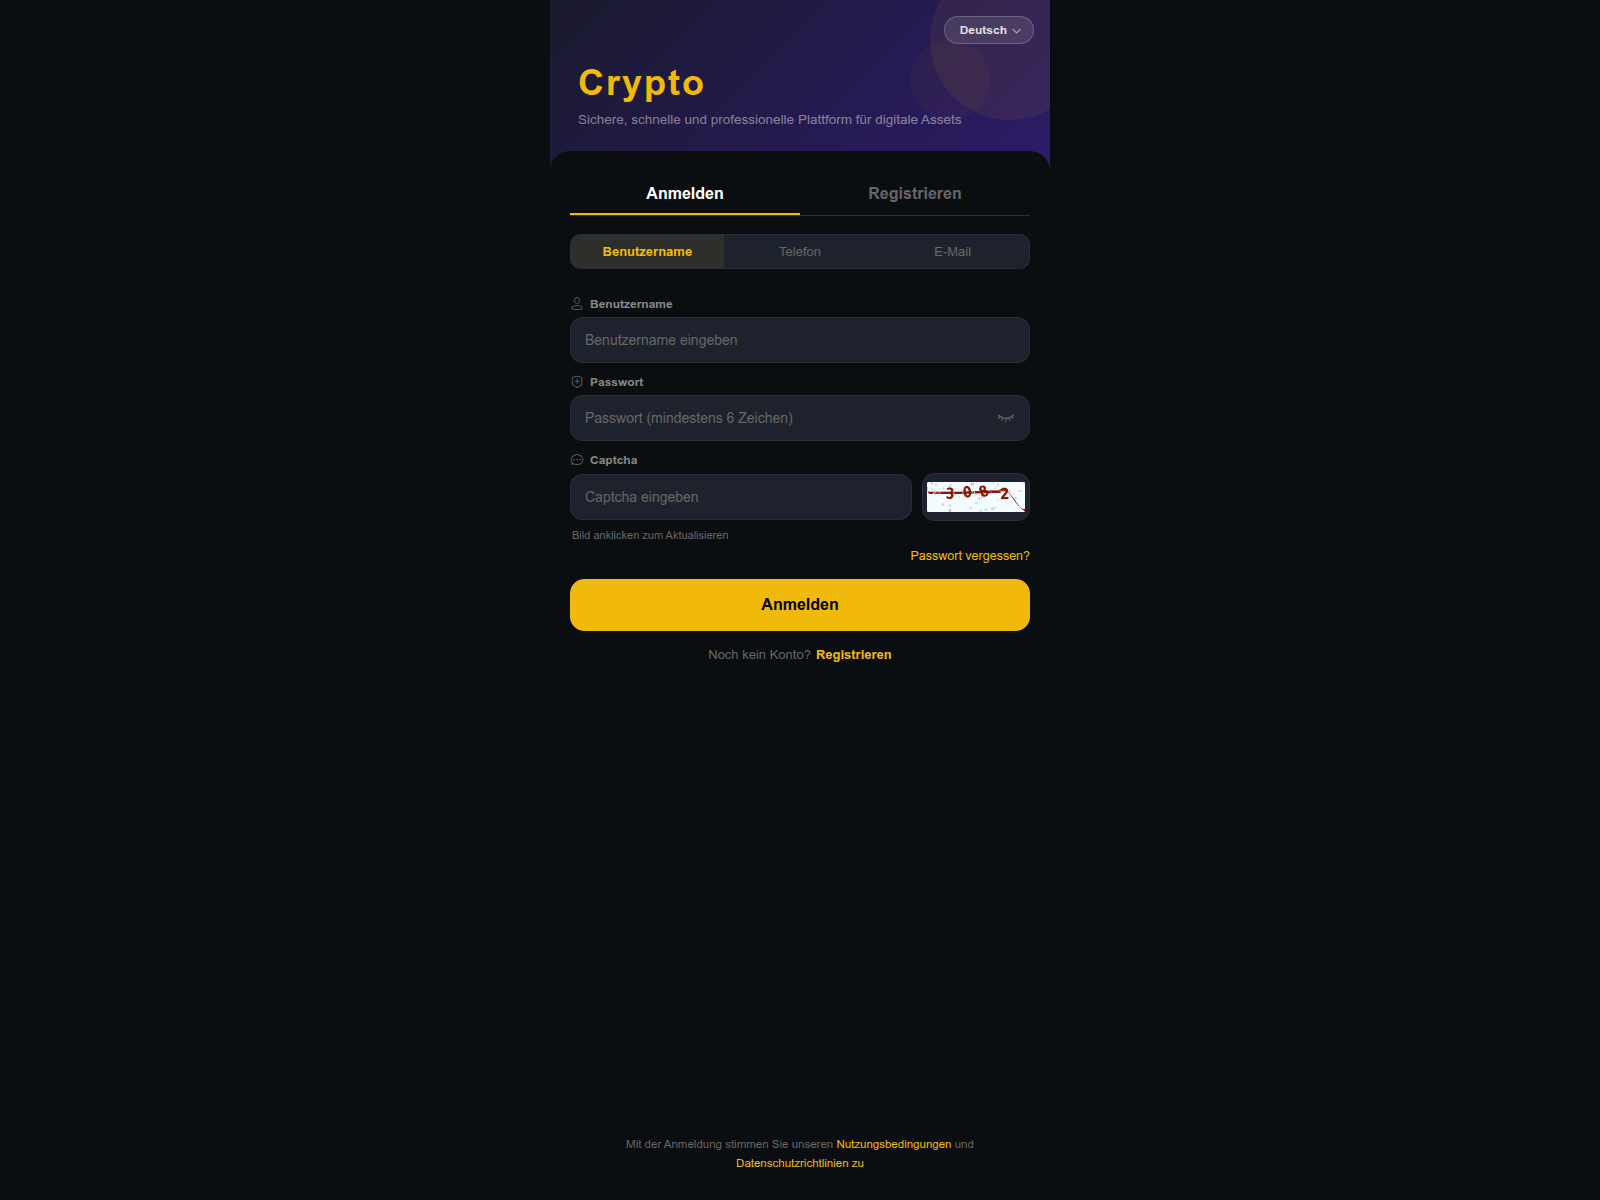
PhishDestroy added xiuoi.com to its internal blocklist on 2026-10-25 after an intake review flagged the domain as suspicious. The intake reason cited six malicious vendors on VirusTotal. No page title was recorded, and the site returned HTTP 200 on the same date, but the recorded response does not prove current availability.
诈骗手法解析
The available detections suggest a potential phishing risk, where a site might be used to harvest credentials or personal data, but no specific phishing form or credential‑stealing behavior was observed on this domain. Consequently, the exact malicious mechanism cannot be confirmed from the current evidence.
证据
VirusTotal reported eight detections from 92 engines on 2026-10-25, with six vendors marking the domain as malicious and two as suspicious. Google Safe Browsing checked the domain on 2026-10-25 and did not flag it. URLScan captured the site on 2026-10-24, gave an overall clean verdict but its engine score labeled it malicious; the scan also listed related domains in the TLS certificate. OTX listed one pulse referencing xiuoi.com, and external blocklists returned zero hits on the check date. PhishDestroy’s internal list includes the domain.
基础设施
The domain was registered on 2026-07-09 through July Name Limited and was 105 days old at the time of observation. The recorded IP address 35.241.101.141 belongs to Google LLC and is geolocated to Hong Kong; the TLS certificate issued by Let’s Encrypt is valid from 2026-09-26 to 2026-12-25 and lists cuioi.com, jiemili.com, miuxci.com and xiuoi.com as SANs. Nameservers are ns1.julydns.com and ns2.julydns.com, DNSSEC is not enabled, and the server presented an HSTS header with a max‑age of one year.
What to do
Visitors should avoid entering any credentials on this site; if credentials were submitted, change the affected passwords and monitor accounts for unauthorized activity. Defenders can block xiuoi.com at network perimeters, review logs for connections to its IP address, and continue monitoring security feeds for any updated classification.
PhishDestroy lists xiuoi.com as a suspicious domain after VirusTotal flagged it with multiple malicious detections on 2026-10-25.
AI摘要
Overview PhishDestroy added xiuoi.com to its internal blocklist on 2026-10-25 after an intake review flagged the domain as suspicious. The intake reason cited six malicious vendors on VirusTotal. No page title was recorded, and the site returned HTTP 200 on the same date, but the recorded response does not prove current availability. How the scam works The available detections suggest a potential phishing risk, where a site might be used to harvest credentials or personal data, but no specific phishing form or credential‑stealing behavior was observed on this domain. Consequently, the exact malicious mechanism cannot be confirmed from the current evidence. Evidence VirusTotal reported eight detections from 92 engines on 2026-10-25, with six vendors marking the domain as malicious and two as suspicious. Google Safe Browsing checked the domain on 2026-10-25 and did not flag it. URLScan captured the site on 2026-10-24, gave an overall clean verdict but its engine score labeled it malicious; the scan also listed related domains in the TLS certificate. OTX listed one pulse referencing xiuoi.com, and external blocklists returned zero hits on the check date. PhishDestroy’s internal list includes the domain. Infrastructure The domain was registered on 2026-07-09 through July Name Limited and was 105 days old at the time of observation. The recorded IP address 35.241.101.141 belongs to Google LLC and is geolocated to Hong Kong; the TLS certificate issued by Let’s Encrypt is valid from 2026-09-26 to 2026-12-25 and lists cuioi.com, jiemili.com, miuxci.com and xiuoi.com as SANs. Nameservers are ns1.julydns.com and ns2.julydns.com, DNSSEC is not enabled, and the server presented an HSTS header with a max‑age of one year. What to do Visitors should avoid entering any credentials on this site; if credentials were submitted, change the affected passwords and monitor accounts for unauthorized activity. Defenders can block xiuoi.com at network perimeters, review logs for connections to its IP address, and continue monitoring security feeds for any updated classification. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a16c59-b643-71cd-846b-7c8f9d43dd30/ Cloudflare Radar report: https://radar.cloudflare.com/scan/8f1b2143-0951-49f3-8dd4-2b1c19fab377 Stored capture screenshot: https://urlscan.io/screenshots/01a16c59-b643-71cd-846b-7c8f9d43dd30.png Cloudflare Radar screenshot (2026-10-25T02:05:27Z): https://screenshots.phishdestroy.io/cf/8f1b2143-0951-49f3-8dd4-2b1c19fab377.png URLScan screenshot (2026-07-30T14:13:04Z): https://screenshots.phishdestroy.io/us/019fb35e-eeb2-7568-adcc-2b986e8ff69f.png URLScan capture report: https://urlscan.io/result/019fb35e-eeb2-7568-adcc-2b986e8ff69f/ URLScan screenshot (2026-07-30T15:06:41Z): https://screenshots.phishdestroy.io/us/019fb390-19a2-71d2-8e57-4da7b6fc8932.png URLScan capture report: https://urlscan.io/result/019fb390-19a2-71d2-8e57-4da7b6fc8932/ URLScan screenshot (2026-08-01T16:37:49Z): https://screenshots.phishdestroy.io/us/019fbe30-4537-70ef-b4e2-0cf773561b16.png URLScan capture report: https://urlscan.io/result/019fbe30-4537-70ef-b4e2-0cf773561b16/ URLScan screenshot (2026-10-25T02:01:23Z): https://screenshots.phishdestroy.io/us/01a170ca-5ce7-717f-b017-dc2a64ac8fa1.png URLScan capture report: https://urlscan.io/result/01a170ca-5ce7-717f-b017-dc2a64ac8fa1/ URLScan screenshot (2026-10-25T02:02:31Z): https://screenshots.phishdestroy.io/us/01a170cb-6e48-734d-bac2-634ad18bbd45.png URLScan capture report: https://urlscan.io/result/01a170cb-6e48-734d-bac2-634ad18bbd45/ VirusTotal report: https://www.virustotal.com/gui/domain/xiuoi.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=xiuoi.com Archived copy: https://web.archive.org/web/20261025015953/https://xiuoi.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Registrar: July Name Limited; Created: 2026-07-09T07:47:27Z; Updated: 2026-09-12T13:40:42Z; Expires: 2028-07-09T07:47:27Z; Status: clientTransferProhibited https://icann.org/epp; Nameservers: ns1.julydns.com, ns2.julydns.com
HTTP 头
Headers: Server: nginx; Content type: text/html; Strict transport security: max-age=31536000
安全信号
Scamadviser 警告20/100
The website's owner is hiding his identity on WHOIS using a paid service This website does not have many visitors We found many low rated websites on the same server This website has only been registered recently. Pulsedive reports elevated risk with this website.
According to the SSL check the certificate is valid The owner of the site has claimed the domain name for a long time DNSFilter considers this website safe
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:48 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:48 UTClast content: 2026-11-22 11:48 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 July Name
 35.241.101.141


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT