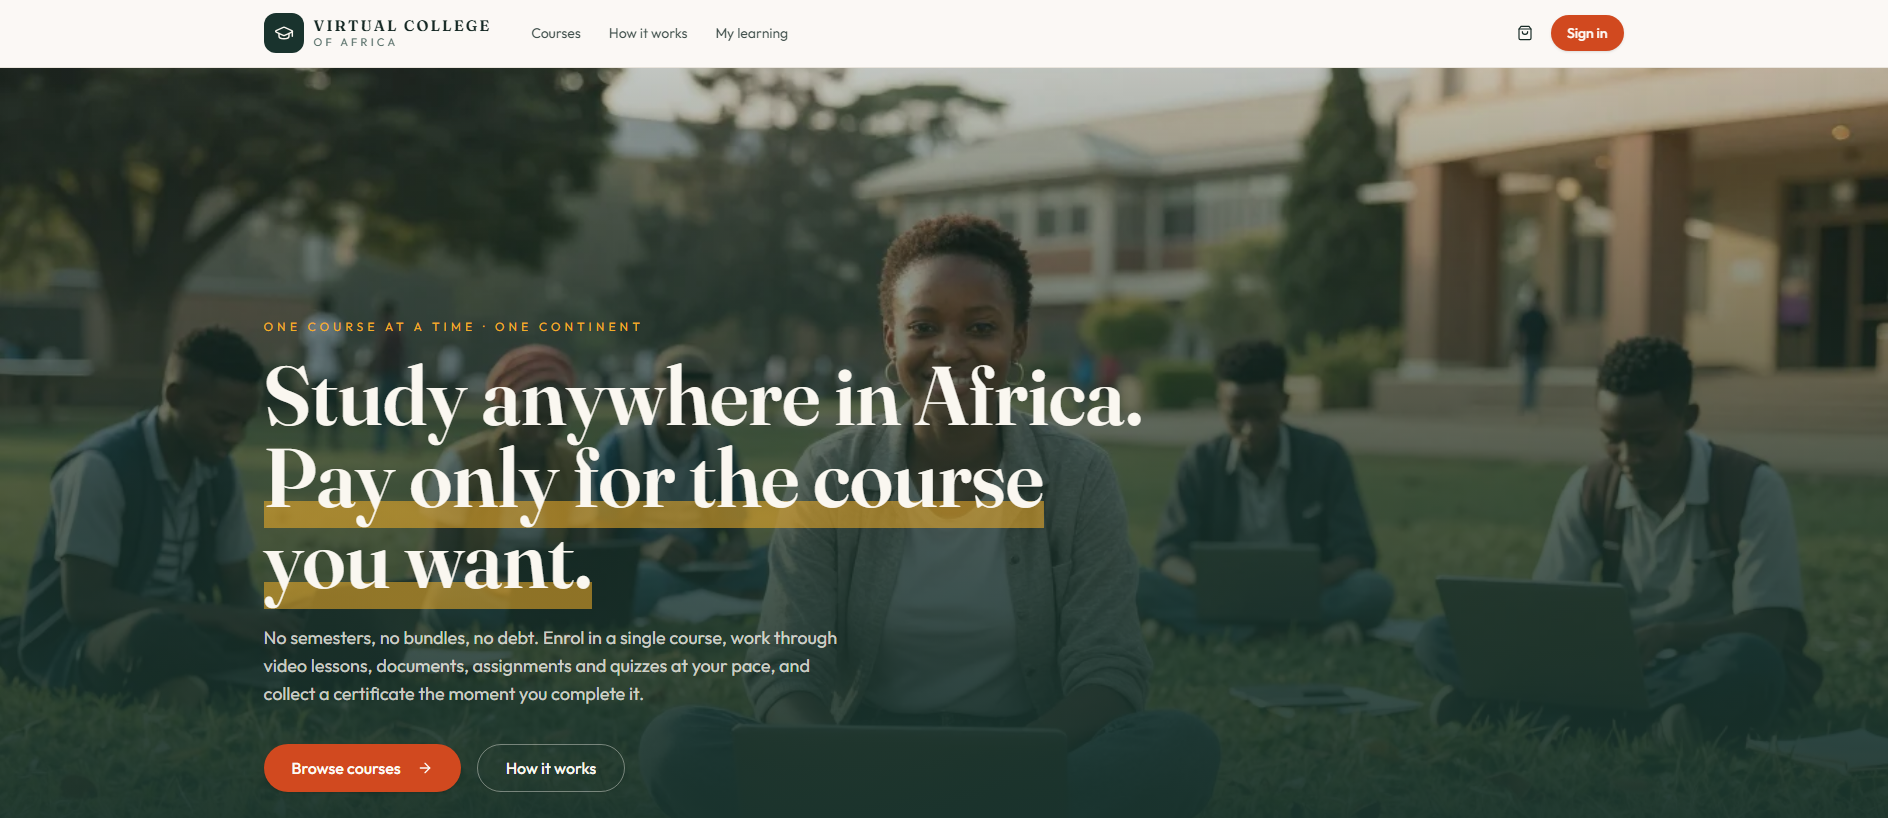
virtualcollege.africa presents itself as "Virtual College of Africa — Pay-per-course online learning across Africa", a storefront aimed at students and professionals across the continent who want to buy individual courses. PhishDestroy classifies it as an impersonation phishing page and first flagged it on 2026-09-22. On 2026-10-19 the site was still online and serving content, so it remains a live risk to anyone who lands on it.
诈骗手法解析
The page shows a pay-per-course education service, while our classification is impersonation phishing. Impersonation pages borrow the look and promise of a legitimate-seeming service so visitors trust them with what they would normally give a real provider. Here, a course catalogue with paid enrolment invites learners to create accounts and pay per course. That puts login credentials, personal details and payment card information in the operator's hands, along with any fees paid for courses that never materialise.
证据
The classification has strong outside support. On 2026-10-01, 18 of 91 VirusTotal engines flagged the domain, including ESET, BitDefender, Fortinet, Forcepoint ThreatSeeker, alphaMountain.ai, CRDF, CyRadar and the Vietnamese anti-scam group Chong Lua Dao. Agreement across vendors this varied rules out a single engine's false positive. The domain also appears in 5 AlienVault OTX threat pulses, which shows other researchers are tracking it.
基础设施
The domain was registered through Namecheap, Inc. on 2023-07-31, more than three years before PhishDestroy detected it. That long, quiet history lends the site a seasoned appearance that newly registered phishing domains lack. It is hosted on Hostinger International Limited's network in Lithuania and uses a free Let's Encrypt certificate. The padlock in the browser only means the connection is encrypted, not that the college is genuine.
What to do
If you paid for a course on this site, contact your bank or card issuer now to dispute the charge and ask about reissuing the card. If you created an account, change that password everywhere you reused it and turn on two-factor authentication for your email. Expect follow-up phishing that uses the name, email or phone number you supplied, and do not send further "enrolment" or "certificate" fees. Defenders should block the domain at DNS and proxy level, search logs for visits and form submissions, and report it to the hosting provider and registrar for takedown.
virtualcollege.africa is an impersonation phishing page posing as a pay-per-course African online college, targeting learners paying for courses.
AI摘要
Overview virtualcollege.africa presents itself as "Virtual College of Africa — Pay-per-course online learning across Africa", a storefront aimed at students and professionals across the continent who want to buy individual courses. PhishDestroy classifies it as an impersonation phishing page and first flagged it on 2026-09-22. On 2026-10-19 the site was still online and serving content, so it remains a live risk to anyone who lands on it. How the scam works The page shows a pay-per-course education service, while our classification is impersonation phishing. Impersonation pages borrow the look and promise of a legitimate-seeming service so visitors trust them with what they would normally give a real provider. Here, a course catalogue with paid enrolment invites learners to create accounts and pay per course. That puts login credentials, personal details and payment card information in the operator's hands, along with any fees paid for courses that never materialise. Evidence The classification has strong outside support. On 2026-10-01, 18 of 91 VirusTotal engines flagged the domain, including ESET, BitDefender, Fortinet, Forcepoint ThreatSeeker, alphaMountain.ai, CRDF, CyRadar and the Vietnamese anti-scam group Chong Lua Dao. Agreement across vendors this varied rules out a single engine's false positive. The domain also appears in 5 AlienVault OTX threat pulses, which shows other researchers are tracking it. Infrastructure The domain was registered through Namecheap, Inc. on 2023-07-31, more than three years before PhishDestroy detected it. That long, quiet history lends the site a seasoned appearance that newly registered phishing domains lack. It is hosted on Hostinger International Limited's network in Lithuania and uses a free Let's Encrypt certificate. The padlock in the browser only means the connection is encrypted, not that the college is genuine. What to do If you paid for a course on this site, contact your bank or card issuer now to dispute the charge and ask about reissuing the card. If you created an account, change that password everywhere you reused it and turn on two-factor authentication for your email. Expect follow-up phishing that uses the name, email or phone number you supplied, and do not send further "enrolment" or "certificate" fees. Defenders should block the domain at DNS and proxy level, search logs for visits and form submissions, and report it to the hosting provider and registrar for takedown. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a0c872-466e-72cc-b0d6-52ebd34c0bb1/ VirusTotal report: https://www.virustotal.com/gui/domain/virtualcollege.africa Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=virtualcollege.africa Archived copy: https://web.archive.org/web/20260922092828/https://virtualcollege.africa/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:41 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:41 UTClast content: 2026-11-22 11:41 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 Namecheap
 84.32.84.73


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT