The thebeginning.trade website hosts a fake Solana token cashback claim designed to trick visitors into linking their crypto wallets and draining funds. Disconnect any wallet that interacted with the site and revoke token approvals immediately.
URLScan截图 · 2026-11-20 20:32 UTC · SHA-256 1ea17bd0…6638ddc
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
The Beginning token cashback page layout
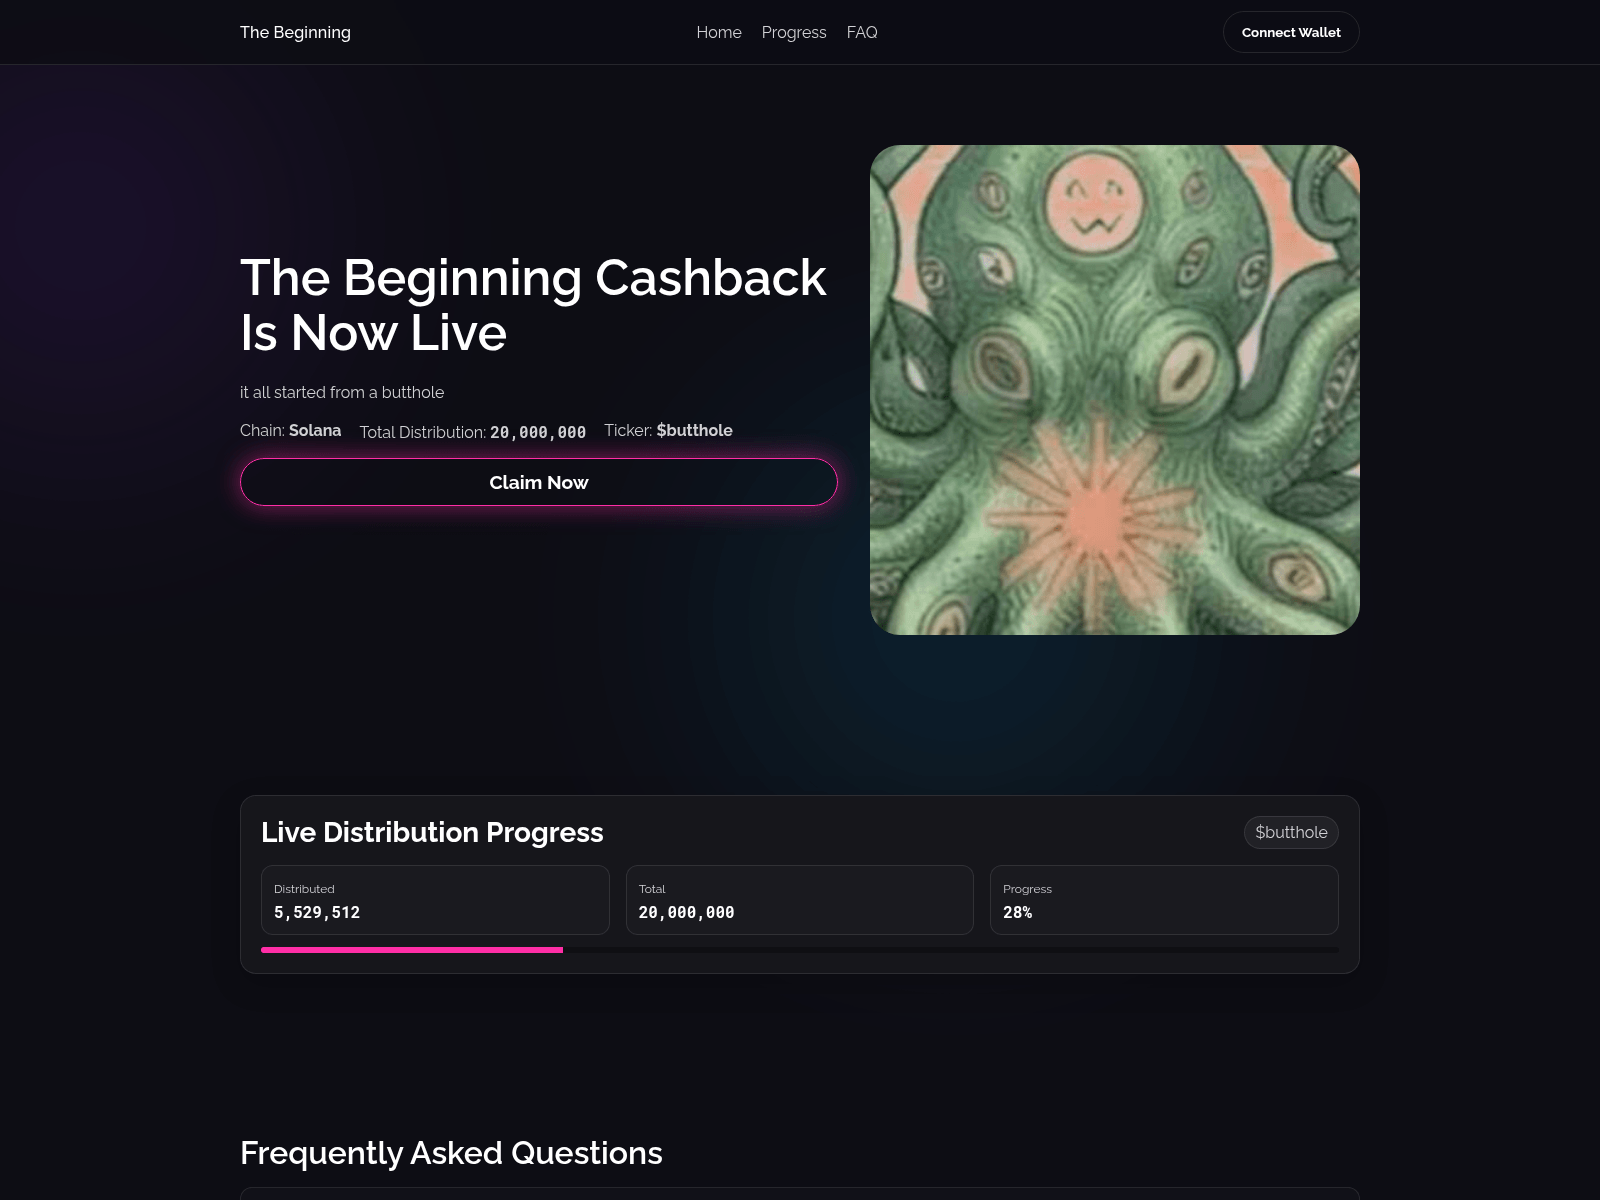
The dark-themed website presents itself as "The Beginning" with a top navigation bar offering links to "Home", "Progress", and "FAQ", alongside a "Connect Wallet" button. The main hero section displays the headline "The Beginning Cashback Is Now Live" with the subtext "it all started from a butthole", specifying the chain as "Solana", a total distribution of "20,000,000", and a ticker of "$buttholes". Next to this text sits an illustration of a multi-eyed green creature, accompanied by a glowing purple button reading "Claim Now". Below the fold, a "Live Distribution Progress" box shows a distributed amount of "5,529,512" out of a total "20,000,000", indicating a "28%" progress bar. The overall layout mimics a legitimate token distribution portal designed to lure users into linking their Web3 wallets. 16 of 92 engines on VirusTotal flagged it on 17 Nov 2026, and MetaMask and SEAL block it, with Kaspersky, ESET and Sophos among them. Furthermore, its PhishDestroy evidence score is 80/100 (critical).
Wallet connection and asset risk
Interacting with the claim button or linking a crypto wallet on this page typically triggers malicious smart contract requests designed to drain tokens. Sites of this nature use deceptive distribution claims to trick visitors into granting unlimited spending approvals or signing unauthorized transfer transactions. Once a wallet is connected, attackers can rapidly sweep native and token assets without further user prompts.
Recommended actions for visitors
Anyone who visited the site and connected a wallet should immediately use a block explorer tool or a security utility like Revoke.cash to inspect and revoke all active token allowances. Users should also disconnect their wallet from the site interface and move remaining funds to a newly generated, secure address. Reporting the domain to hosting providers and browser extensions helps protect other potential victims.
thebeginning.trade presents a fake Solana token cashback claim for $buttholes tokens, flagged by 16 VirusTotal engines. Do not connect your wallet.
AI摘要
The Beginning token cashback page layout The dark-themed website presents itself as "The Beginning" with a top navigation bar offering links to "Home", "Progress", and "FAQ", alongside a "Connect Wallet" button. The main hero section displays the headline "The Beginning Cashback Is Now Live" with the subtext "it all started from a butthole", specifying the chain as "Solana", a total distribution of "20,000,000", and a ticker of "$buttholes". Next to this text sits an illustration of a multi-eyed green creature, accompanied by a glowing purple button reading "Claim Now". Below the fold, a "Live Distribution Progress" box shows a distributed amount of "5,529,512" out of a total "20,000,000", indicating a "28%" progress bar. The overall layout mimics a legitimate token distribution portal designed to lure users into linking their Web3 wallets. 16 of 92 engines on VirusTotal flagged it on 17 Nov 2026, and MetaMask and SEAL block it, with Kaspersky, ESET and Sophos among them. Furthermore, its PhishDestroy evidence score is 80/100 (critical). Wallet connection and asset risk Interacting with the claim button or linking a crypto wallet on this page typically triggers malicious smart contract requests designed to drain tokens. Sites of this nature use deceptive distribution claims to trick visitors into granting unlimited spending approvals or signing unauthorized transfer transactions. Once a wallet is connected, attackers can rapidly sweep native and token assets without further user prompts. Recommended actions for visitors Anyone who visited the site and connected a wallet should immediately use a block explorer tool or a security utility like Revoke.cash to inspect and revoke all active token allowances. Users should also disconnect their wallet from the site interface and move remaining funds to a newly generated, secure address. Reporting the domain to hosting providers and browser extensions helps protect other potential victims.
Headers: Server: cloudflare; Content type: text/html; Strict transport security: max-age=63072000; includeSubDomains; preload; Content security policy: frame-ancestors http: https:; X content type options: nosniff
安全信号
Scamadviser 警告1/100
The website's owner is hiding his identity on WHOIS using a paid service This website does not have many visitors This website has only been registered recently. DNSFilter reported this website as malicious in the last 30 days IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
According to the SSL check the certificate is valid
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:12 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:12 UTClast content: 2026-11-22 11:12 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 Global Domain Group
 172.67.140.19


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT