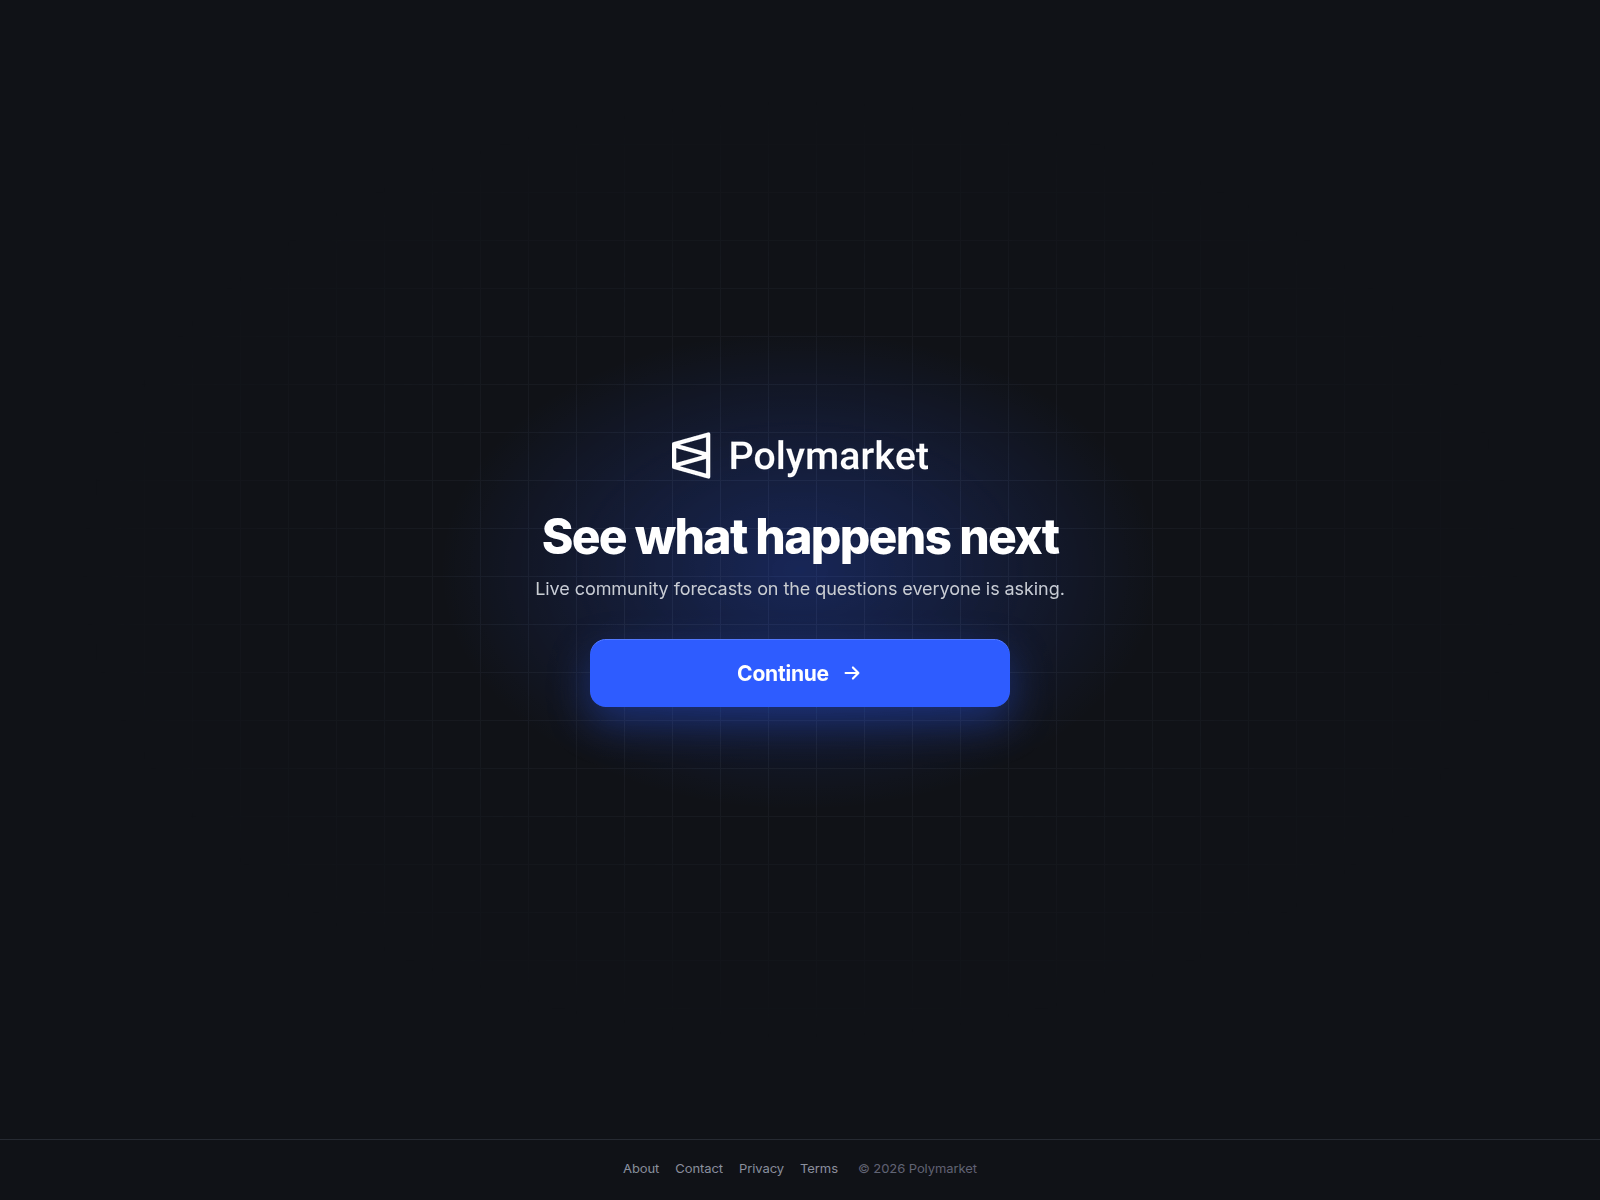
The pollymarket.info domain presents a fake Polymarket forecast portal designed to harvest user interactions under the guise of the prediction market. If you visited this site, do not click continue or connect any digital wallets.
It was registered on 19 Nov 2026, 1 day before it was first reported, presenting a significant mismatch for an established platform brand that relies on long-term user trust. urlscan classified the page as malicious, 5 of 92 engines on VirusTotal flagged it on 20 Nov 2026, and MetaMask and SEAL block it, with Forcepoint ThreatSeeker, Gridinsoft and ChainPatrol among them. Its PhishDestroy evidence score is 70/100 (critical), which aligns with the deceptive nature of the portal. The shared infrastructure also includes kalshii.org which used a similar Polymarket page title, showing a pattern of fraudulent prediction market clones.
Risks of prediction portal clones
Pages mimicking popular forecasting platforms like Polymarket typically lead visitors toward malicious wallet connection prompts or credential harvesting scripts. Because the official domain is polymarket.com, an address like pollymarket.info exists solely to deceive users into giving up control of their accounts or funds.
Recommended precautions and actions
Always verify that you are visiting polymarket.com before engaging with any community forecasts or connecting a wallet. If you already interacted with pollymarket.info or clicked the continue button, immediately revoke any unfamiliar token approvals using a trusted blockchain explorer and disconnect your wallet.
Headers: Server: openresty/1.31.1.1; Content type: text/html; Content security policy: script-src 'nonce-egm92+seNeST82+NVfBAAg=='; style-src 'nonce-egm92+seNeST82+NVfBAAg=='; frame-ancestors 'self'; X frame options: SAMEORIGIN; X content type options: nosniff; Referrer policy: strict-origin-when-cross-origin
安全信号
Scamadviser 警告54/100
According to Tranco this site has a low rank High number of suspicious websites on this server
The SSL certificate is valid This website is safe according to DNSFilter
网络安全情报 注册商背景
注册商背景NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
证据层Availability: Content servingContent: Content served at rootDNS: ResolvedRegistration: Active
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 12:07 UTC
RDAP注册有效NICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765RDAP HTTP 200source: Rdap Status CollectorAddperiodclientDeleteProhibitedclientTransferProhibitedexpires 2027-11-19 16:34 UTC已检查 2026-11-21 08:37 UTC
观测时间线last reachable: 2026-11-22 12:07 UTClast content: 2026-11-22 12:07 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 NiceNIC
 5.61.209.225


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT