跳转到安全报告
polexbot.pro 的网站图标
域安全和威胁情报

polexbot.pro

我被骗了——请帮我写报案材料
分享/下载报告
发布到X 通过Telegram发送 通过API进行核查
简要

PhishDestroy 于 2026-10-25 首次记录了 polexbot.pro。被外部黑名单列入:MetaMask, SEAL。

页面标题: “Polexbot: Automated Polymarket Bot for 5-Minute Crypto Rounds”

更多关于数据来源的信息
已保存的安全信号

被外部黑名单列入:MetaMask, SEAL。 请格外小心——不要输入凭据或个人信息。

Spamhaus DBL: 垃圾邮件域名 存储的阻止列表匹配项:2
注册商
俄罗斯NiceNIC
IP 地址
德国108.138.26.63Amazon.com, Inc.
首次由PhishDestroy发现
2026-10-25
URLQuery
次检测
OTX
社区参考资料
页面快照
打开图库
已发送举报
查看时间线
OTX: 4 条引用 2026-10-25 1 份举报已发送

风险评分,数值越高,情况越糟 · 该评分的计算原理

现在该怎么做

选择实际发生的情况,并随着操作进程逐项勾选相应步骤。勾选记录仅保存在当前浏览器中。

输入了密码0/3
已支付或已输入的银行卡或银行信息0/2
下载了文件0/2
分享了助记词或私钥0/3
批准代币支出 (approve / permit)0/3
已连接钱包,但未签署任何内容0/2
发送了加密货币0/3
向警方报案

专家视图包含所有部分:DNS、TLS、网络请求、哈希值以及原始 JSON 数据。

ABUSE NOTICE · 7D+ OPEN 外发滥用报告均被记录;存储的最新可用性证据仍显示该域名可访问。
通知与当前状态证据

已发送报告日志记录了首份外发报告的时间为 。记录的收件人是 abuse@identitydigital.com. 最新的存储可用性证据仍显示该域名可访问; 28 days 自首份外发报告发布以来,已过去……

ICANN RAA §3.18 描述了域名注册商的滥用联系渠道及处理义务。本节记录了发送时间戳、收件人列表、案件标识符以及后续的可用性。本节内容本身并不构成对收件、确认、调查、整改或合同违约的证明。

自首次报告以来的时间
28 days
已发送举报
1
最新案例 ID
PD-20261025-0A50AD
当前状态
HTTP 301 最新存储的检查结果
报告概览

PhishDestroy 保存了 polexbot.pro 的记录。各来源的观测有各自的日期;缺少检查并不代表安全。

为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。

分析

域名概览

PhishDestroy 于 2026-10-25 首次记录了 polexbot.pro。被外部黑名单列入:MetaMask, SEAL。风险:严重(证据评分 100/100)。注册商:NiceNIC。状态:最后一次已知在线状态。托管:Amazon.com, Inc。PhishDestroy 已发送1 份滥用举报。请勿输入登录凭据,也不要连接钱包。

严重
状态
最后一次已知在线状态
黑名单匹配项
2个外部 + PhishDestroy列表
诈骗类型(自动标记)
仿冒
托管
德国108.138.26.63Amazon.com, Inc.
注册商
俄罗斯NiceNIC
OTX
4 community refs
页面快照
6

PhishDestroy分析,早期未经审核的版本

为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。

Overview

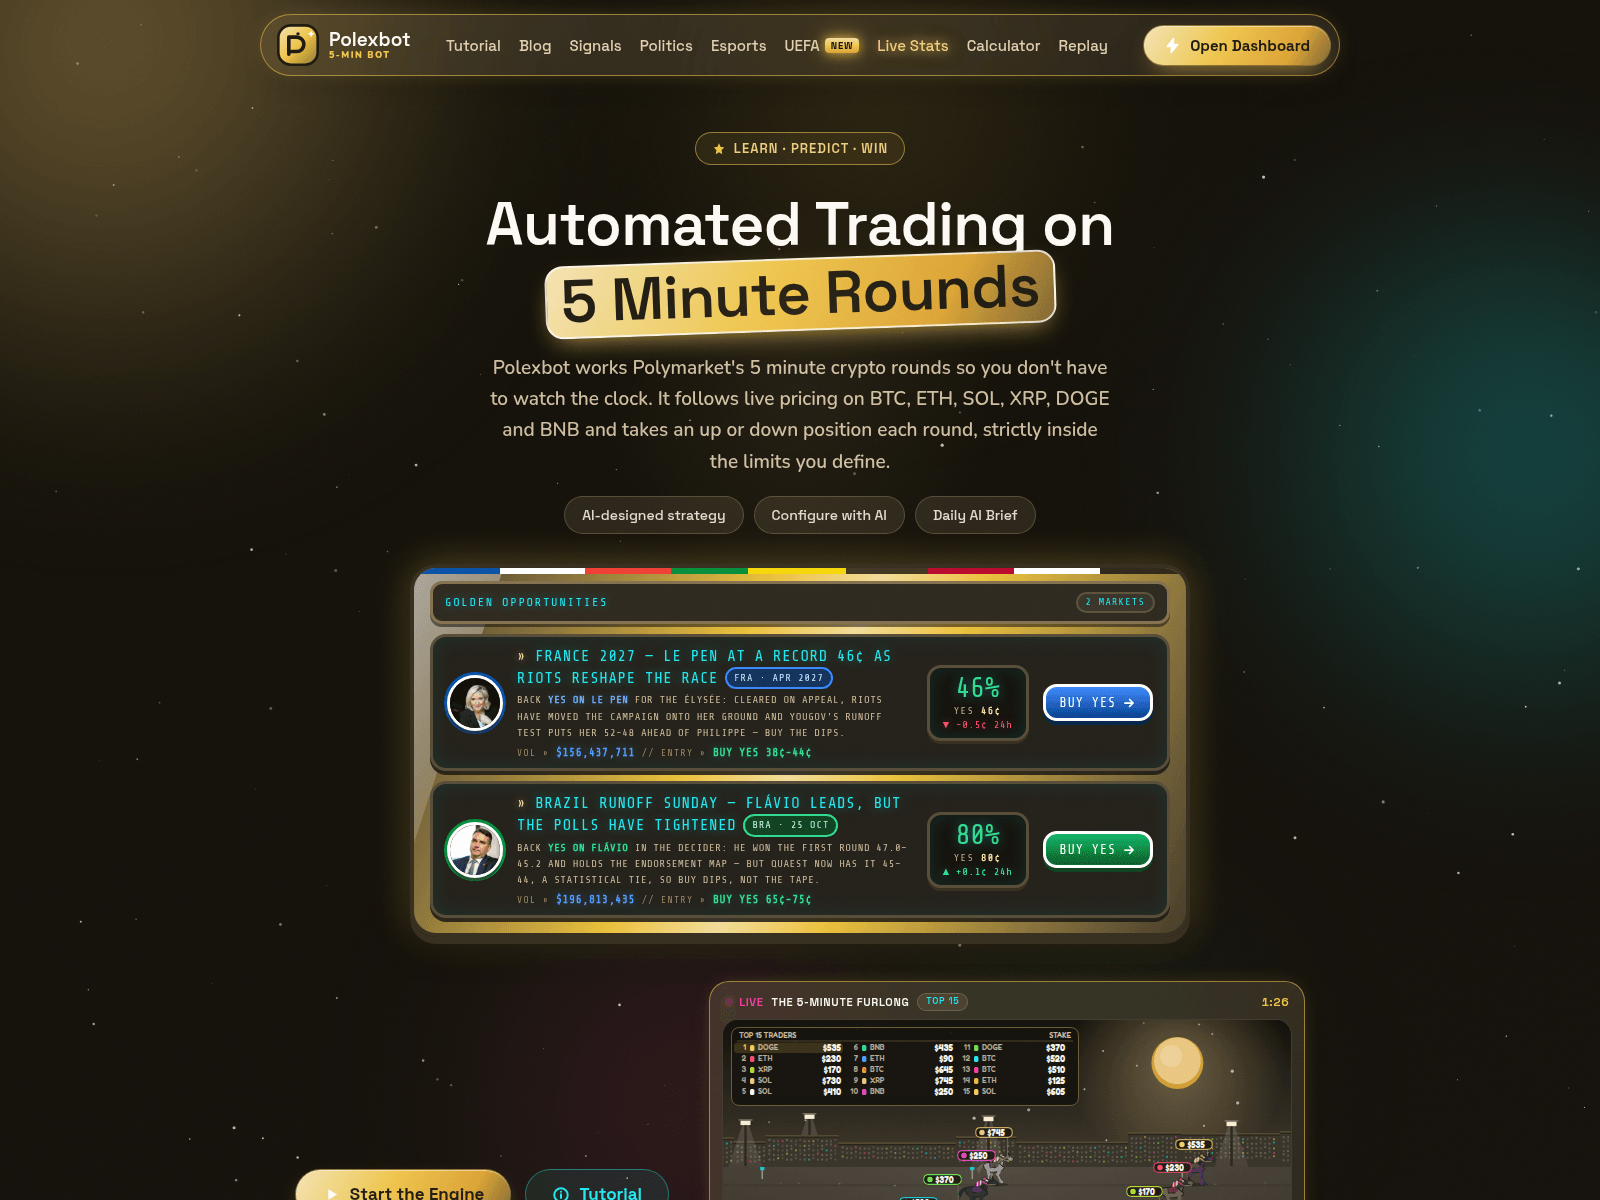
The captured screenshot from 2026-10-25 shows a dark gold landing page headed Automated Trading on 5 Minute Rounds, offering an AI bot for Polymarket's five-minute crypto rounds, with an Open Dashboard button, AI configuration chips and market cards with BUY YES prompts. Metadata described an automated Polymarket bot covering BTC, ETH, SOL, XRP, DOGE and BNB. PhishDestroy listed the page for impersonation because it trades on the Polymarket brand on a domain registered the day before. First seen by PhishDestroy on 2026-10-25.

诈骗手法解析

The page routes visitors to a dashboard behind an automation pitch, a pattern in which a copycat collects account credentials or payment details from people who believe they are using the genuine Polymarket service. The lure is a bot claiming to place an up or down position each round inside visitor-set limits. Treat the offer as unverified impersonation rather than an authorized Polymarket tool.

证据

The screenshot shows branded navigation, AI strategy chips and market cards borrowing Polymarket's name. urlscan's machine-learning engine scored the capture malicious at 97 on 2026-10-25 while its overall verdict stayed clean. VirusTotal did not flag the domain. Spamhaus listed it under the spam category on 2026-10-25; the MetaMask and SEAL blocklists plus PhishDestroy's internal list flagged it on 2026-10-26; OTX carried 4 pulses on 2026-10-25; Google Safe Browsing was not flagged on 2026-10-26. A same-domain redirect chain led to the captured page, whose scripts showed an Express on nginx stack with Google Tag Manager and Google Analytics, no React, Vue or Next globals, and a document hash starting 4f3ae770ccf7.

基础设施

The domain was registered 2026-10-24 through NICENIC INTERNATIONAL GROUP CO., LIMITED and the capture was served from Amazon CloudFront behind nginx with Express headers; no firewall vendor was shown. Notable weaknesses: DNSSEC unsigned, no DKIM recorded, COOP, COEP and CORP absent, and one check reported no HSTS header. Otherwise TLS 1.3 with TLS-AES-128-GCM-SHA256, forward secrecy and ALPN h2; CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy present; SPF and DMARC present; CAA record present.

What to do

If you entered a password or payment details on polexbot.pro, change that password on the genuine Polymarket service and enable two-factor authentication. Defenders should block polexbot.pro at DNS, proxy and mail gateways and hunt for it in web logs and referral data. PhishDestroy's impersonation listing stands regardless of clean verdicts from other feeds.

来源证据OTX 4 参考文献 8 个来源

Scamadviser

1/100

可信度评分,数值越低,情况越糟

打开报告

Spamhaus DBL

垃圾邮件域名

URLScan

页面快照

打开报告
URLScan来源原始记录观测时间: 23 个字段
单独的监视器记录

单独存储的监控快照;不会替换主报告记录,也不会确定当前的可用性。

UUID
01a16d36-6919-779d-8caa-5f2b65ebe9b6
数据增强时间
2026-10-25T09:11:41Z
源数据时间戳
Urlscan enriched at: 2026-10-25 10:11:41

PhishDestroy DOM

90 / 100 · 启发式得分 · 7 个品牌引用 · 1 个分类

仅为内容启发式评分;并非最终评分

打开报告
技术元数据

PhishDestroy的分析说明

叙事生成元数据

打开报告
标题、描述和生成记录

叙述生成日期与观测日期不同。这些是保留的出版字段,并非额外的独立检测结果。

AI 标题
polexbot.pro — Polymarket impersonation bot scam
AI 描述
PhishDestroy assesses polexbot.pro as an impersonation phishing page posing as an automated Polymarket trading bot.
AI摘要
Overview The captured screenshot from 2026-10-25 shows a dark gold landing page headed Automated Trading on 5 Minute Rounds, offering an AI bot for Polymarket's five-minute crypto rounds, with an Open Dashboard button, AI configuration chips and market cards with BUY YES prompts. Metadata described an automated Polymarket bot covering BTC, ETH, SOL, XRP, DOGE and BNB. PhishDestroy listed the page for impersonation because it trades on the Polymarket brand on a domain registered the day before. First seen by PhishDestroy on 2026-10-25. How the scam works The page routes visitors to a dashboard behind an automation pitch, a pattern in which a copycat collects account credentials or payment details from people who believe they are using the genuine Polymarket service. The lure is a bot claiming to place an up or down position each round inside visitor-set limits. Treat the offer as unverified impersonation rather than an authorized Polymarket tool. Evidence The screenshot shows branded navigation, AI strategy chips and market cards borrowing Polymarket's name. urlscan's machine-learning engine scored the capture malicious at 97 on 2026-10-25 while its overall verdict stayed clean. VirusTotal did not flag the domain. Spamhaus listed it under the spam category on 2026-10-25; the MetaMask and SEAL blocklists plus PhishDestroy's internal list flagged it on 2026-10-26; OTX carried 4 pulses on 2026-10-25; Google Safe Browsing was not flagged on 2026-10-26. A same-domain redirect chain led to the captured page, whose scripts showed an Express on nginx stack with Google Tag Manager and Google Analytics, no React, Vue or Next globals, and a document hash starting 4f3ae770ccf7. Infrastructure The domain was registered 2026-10-24 through NICENIC INTERNATIONAL GROUP CO., LIMITED and the capture was served from Amazon CloudFront behind nginx with Express headers; no firewall vendor was shown. Notable weaknesses: DNSSEC unsigned, no DKIM recorded, COOP, COEP and CORP absent, and one check reported no HSTS header. Otherwise TLS 1.3 with TLS-AES-128-GCM-SHA256, forward secrecy and ALPN h2; CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy present; SPF and DMARC present; CAA record present. What to do If you entered a password or payment details on polexbot.pro, change that password on the genuine Polymarket service and enable two-factor authentication. Defenders should block polexbot.pro at DNS, proxy and mail gateways and hunt for it in web logs and referral data. PhishDestroy's impersonation listing stands regardless of clean verdicts from other feeds. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1715a-4da1-718d-9999-b133425d7cd7/ Cloudflare Radar report: https://radar.cloudflare.com/scan/394a5704-0d49-4790-8a84-898d14a297e3 URLQuery report: https://urlquery.net/report/78ae276c-abc7-4352-adee-5f221fc08b7b Stored capture screenshot: https://urlscan.io/screenshots/01a1715a-4da1-718d-9999-b133425d7cd7.png Cloudflare Radar screenshot (2026-10-25T04:38:17Z): https://screenshots.phishdestroy.io/cf/394a5704-0d49-4790-8a84-898d14a297e3.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/78ae276c-abc7-4352-adee-5f221fc08b7b.png URLScan screenshot (2026-10-24T09:21:13Z): https://screenshots.phishdestroy.io/us/01a16d36-6919-779d-8caa-5f2b65ebe9b6.png URLScan capture report: https://urlscan.io/result/01a16d36-6919-779d-8caa-5f2b65ebe9b6/ URLScan screenshot (2026-10-25T04:54:11Z): https://screenshots.phishdestroy.io/us/01a17168-9fe8-7695-92e8-9ea565a1feb5.png URLScan capture report: https://urlscan.io/result/01a17168-9fe8-7695-92e8-9ea565a1feb5/ VirusTotal report: https://www.virustotal.com/gui/domain/polexbot.pro Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=polexbot.pro Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
撰写本文的AI模型
mimo-flash
AI文本的生成时间
2026-10-26T21:27:53Z
Revision
6a35fa011d1055926a89caa5f992e5b1210adc9a390a259830afdeb135b88560
模式
stored
Interpretation
先前存储的分析结果,未经审核;文本生成时间与源观察日期不同。

结果反映各来源的采集时间。零检出不代表安全。OTX 引用为社区发布的内容。

已采集的来源详情

已存档的页面、网络和扫描器观测结果,按来源和观测时间分组。

所有已保存字段及其来源和日期
VirusTotal来源原始记录观测时间: 8 个字段
打开完整记录
网站检查来源原始记录检索到: 25 个字段

邮件配置

SPF 记录
v=spf1 -all
DMARC
是
SPF 查询次数
0

CAA 记录

域名
polexbot.pro

DNS防护结果

已检查的解析器
12
拦截的解析器
0

爬行器规则

用户代理
  • *
存在
是
站点地图 URL
  • https://www.polexbot.pro/sitemap.xml

站点地图

存在
是
URL 数量
31

安全联系文件(security.txt)

存在
是
发现位置
/.well-known/security.txt

页面标题与元数据

Open Graph URL
https://www.polexbot.pro/
页面标题
Polexbot: Automated Polymarket Bot for 5-Minute Crypto Rounds
作者
Polexbot
Open Graph 类型
website
索引指令
index,follow
Open Graph 图片
https://www.polexbot.pro/og-image.jpg
Open Graph 标题
Polexbot: Automated Polymarket Bot for 5-Minute Crypto Rounds
关键词
Polexbot, Polymarket bot, automated trading bot, 5 minute crypto rounds, prediction market bot, BTC ETH SOL XRP DOGE BNB, up or down bot
Open Graph 网站名称
Polexbot
描述
Polexbot automates Polymarket's 5-minute crypto up/down rounds. It covers BTC, ETH, SOL, XRP, DOGE and BNB, taking a position every round strictly within the limits you set.
Twitter 卡片
summary_large_image
规范 URL
https://www.polexbot.pro/
Open Graph 描述
Polexbot works Polymarket's 5 minute crypto rounds for you, taking an up or down position each round inside the limits you set.

追踪器

请求
22
检测到的服务
  • 名称
    Google Tag
    公司
    Google
    国家/地区
    US
    类别
    Advertising
    请求
    1
  • 名称
    Amazon Web Services
    公司
    Amazon
    国家/地区
    US
    类别
    托管
    请求
    2
  • 名称
    Google Fonts
    公司
    Google
    国家/地区
    US
    类别
    托管
    请求
    1
  • 名称
    Google Static
    公司
    Google
    国家/地区
    US
    类别
    托管
    请求
    3
  • 名称
    Google Analytics
    公司
    Google
    国家/地区
    US
    类别
    Site Analytics
    请求
    1

表单与混合内容

无 SRI 的脚本
  • https://www.googletagmanager.com/gtag/js
第三方脚本
1

HTTP 响应

可访问
是
HTTP状态码
301
请求耗时(毫秒)
DNS
29
TLS
12
等待
15
连接
14
下载
0
响应时间(毫秒)
70

TLS连接

ALPN
h2
加密套件
TLS_AES_128_GCM_SHA256
协议
TLSv1.3
支持的版本
  • TLSv1.2
  • TLSv1.3
证书已验证
是
前向保密
是

端口

开放端口
  • 80
  • 443

碳排放估算

字节
208908
CO₂(克)
0.0076
比其他页面更环保的比例(%)
6

DNS 服务器

域名服务器
  • IP 地址
    205.251.192.95
    主机
    ns-95.awsdns-11.com
  • IP 地址
    205.251.196.240
    主机
    ns-1264.awsdns-30.org
  • IP 地址
    205.251.199.244
    主机
    ns-2036.awsdns-62.co.uk
  • IP 地址
    205.251.194.210
    主机
    ns-722.awsdns-26.net
DNS 区域
polexbot.pro

Cookie

Cookie
  • 名称
    _ga_CC1B5QY8E3
  • 名称
    _ga

位置

IP 地址
108.138.26.63
ASN
16509
组织
Amazon.com, Inc.
城市
Frankfurt am Main
国家/地区
DE

TLS 证书

签发者
Amazon / Amazon RSA 2048 M01
使用者(Subject)
polexbot.pro

DNS 记录

A
  • 108.138.26.125
  • 108.138.26.63
  • 108.138.26.95
  • 108.138.26.23
NS
  • ns-95.awsdns-11.com
  • ns-2036.awsdns-62.co.uk
  • ns-722.awsdns-26.net
  • ns-1264.awsdns-30.org
SOA
主域名服务器
ns-1264.awsdns-30.org
Hostmaster
awsdns-hostmaster.amazon.com
序列号
1
刷新(秒)
7200
重试(秒)
900
过期(秒)
1209600
最小 TTL(秒)
86400
TXT
  • v=spf1 -all

DNSSEC

DS 记录
否
RRSIG
否
DNSKEY
否

HSTS

观测结果
Site does not serve any HSTS headers.

HTTP 安全策略

X-Frame-Options
SAMEORIGIN
Referrer-Policy
strict-origin-when-cross-origin
X-XSS-Protection
否
Permissions-Policy
camera=(), microphone=(), geolocation=(), payment=()
X-Content-Type-Options
nosniff
Content-Security-Policy
default-src 'self' https: data: blob:; script-src 'self' 'unsafe-inline' 'unsafe-eval' https:; style-src 'self' 'unsafe-
Strict-Transport-Security
max-age=31536000; includeSubDomains
Cross-Origin-Opener-Policy
否
Cross-Origin-Embedder-Policy
否
Cross-Origin-Resource-Policy
否

IP 查询

IP 地址
108.138.26.95
IP 版本
4

重定向

重定向链
  • https://polexbot.pro
  • https://www.polexbot.pro/
数量
1

页面链接

外部链接地址
  • https://polymarket.com/event/next-french-presidential-election
  • https://polymarket.com/event/brazil-presidential-election
外部链接
2
内部链接
17

HTTP 头

响应头
服务器
nginx
Content-Type
text/html; charset=UTF-8
X-Powered-By
Express
Strict-Transport-Security
max-age=31536000; includeSubDomains
Content-Security-Policy
default-src 'self' https: data: blob:; script-src 'self' 'unsafe-inline' 'unsafe-eval' https:; style-src 'self' 'unsafe-inline' https:; img-src 'self' data: blob: https:; font-src 'self' data: https:; connect-src 'self' https: wss:; frame-ancestors 'self'
X-Frame-Options
SAMEORIGIN
X-Content-Type-Options
nosniff
Referrer-Policy
strict-origin-when-cross-origin
Permissions-Policy
camera=(), microphone=(), geolocation=(), payment=()
Via
1.1 8109fadbc132b410ecc2c3df250d6144.cloudfront.net (CloudFront)
X-Cache
Miss from cloudfront
来源原始字段 · JSON
邮件配置
Spf: v=spf1 -all; Dmarc: ✓; Spf lookups: 0
CAA 记录
Domain: polexbot.pro
DNS防护结果
Resolvers: 12; Blocked count: 0
爬行器规则
Agents: *; Present: ✓; Sitemaps: https://www.polexbot.pro/sitemap.xml
站点地图
Present: ✓; URL count: 31
Security contact file
Present: ✓; Found in: /.well-known/security.txt
页面标题与元数据
Ogurl: https://www.polexbot.pro/; Title: Polexbot: Automated Polymarket Bot for 5-Minute Crypto Rounds; Author: Polexbot; Ogtype: website; Robots: index,follow; Ogimage: https://www.polexbot.pro/og-image.jpg; Ogtitle: Polexbot: Automated Polymarket Bot for 5-Minute Crypto Rounds; Keywords: Polexbot, Polymarket bot, automated trading bot, 5 minute crypto rounds, prediction market bot, BTC ETH SOL XRP DOGE BNB, up or down bot; Ogsitename: Polexbot; Description: Polexbot automates Polymarket's 5-minute crypto up/down rounds. It covers BTC, ETH, SOL, XRP, DOGE and BNB, taking a position every round strictly within the limits you set.; Twittercard: Summary large image; Canonicalurl: https://www.polexbot.pro/; Ogdescription: Polexbot works Polymarket's 5 minute crypto rounds for you, taking an up or down position each round inside the limits you set.
追踪器
Requests: 22; Trackers: (Name: Google Tag; Company: Google; Country: US; Category: Advertising; Requests: 1), (Name: Amazon Web Services; Company: Amazon; Country: US; Category: Hosting; Requests: 2), (Name: Google Fonts; Company: Google; Country: US; Category: Hosting; Requests: 1), (Name: Google Static; Company: Google; Country: US; Category: Hosting; Requests: 3), (Name: Google Analytics; Company: Google; Country: US; Category: Site Analytics; Requests: 1)
表单与混合内容
No sri: https://www.googletagmanager.com/gtag/js; Third party scripts: 1
状态
Up: ✓; Code: 301; Timings: DNS: 29; TLS: 12; Wait: 15; Connect: 14; Download: 0; Response ms: 70
TLS连接
Alpn: h2; Cipher: TLS_AES_128_GCM_SHA256; Protocol: TLSv1.3; Versions: TLSv1.2, TLSv1.3; Authorized: ✓; Forward secrecy: ✓
端口
Open: 80, 443
Carbon
Bytes: 208908; Co2 grams: 0.0076; Cleaner than: 6
DNS server
NS: (IP: 205.251.192.95; Host: ns-95.awsdns-11.com), (IP: 205.251.196.240; Host: ns-1264.awsdns-30.org), (IP: 205.251.199.244; Host: ns-2036.awsdns-62.co.uk), (IP: 205.251.194.210; Host: ns-722.awsdns-26.net); Zone: polexbot.pro
Cookie
Cookies: (Name: _ga_CC1B5QY8E3), (Name: _ga)
位置
IP: 108.138.26.63; ASN: 16509; Org: Amazon.com, Inc.; City: Frankfurt am Main; Country: DE
SSL
Issuer: Amazon / Amazon RSA 2048 M01; Subject: polexbot.pro
DNS 记录
A: 108.138.26.125, 108.138.26.63, 108.138.26.95, 108.138.26.23; NS: ns-95.awsdns-11.com, ns-2036.awsdns-62.co.uk, ns-722.awsdns-26.net, ns-1264.awsdns-30.org; Soa: Nsname: ns-1264.awsdns-30.org; Hostmaster: awsdns-hostmaster.amazon.com; Serial: 1; Refresh: 7200; Retry: 900; Expire: 1209600; Minttl: 86400; Txt: v=spf1 -all
DNSsec
Ds: ✗; Rrsig: ✗; Dnskey: ✗
Hsts
Message: Site does not serve any HSTS headers.
HTTP 安全策略
Xframeoptions: SAMEORIGIN; Referrerpolicy: strict-origin-when-cross-origin; Xxssprotection: ✗; Permissionspolicy: camera=(), microphone=(), geolocation=(), payment=(); Xcontenttypeoptions: nosniff; Contentsecuritypolicy: default-src 'self' https: data: blob:; script-src 'self' 'unsafe-inline' 'unsafe-eval' https:; style-src 'self' 'unsafe-; Stricttransportpolicy: max-age=31536000; includeSubDomains; Crossoriginopenerpolicy: ✗; Crossoriginembedderpolicy: ✗; Crossoriginresourcepolicy: ✗
Get IP
IP: 108.138.26.95; Family: 4
重定向
Chain: https://polexbot.pro, https://www.polexbot.pro/; Count: 1
页面链接
External: https://polymarket.com/event/next-french-presidential-election, https://polymarket.com/event/brazil-presidential-election; External count: 2; Internal count: 17
HTTP 头
Headers: Server: nginx; Content type: text/html; charset=UTF-8; X powered by: Express; Strict transport security: max-age=31536000; includeSubDomains; Content security policy: default-src 'self' https: data: blob:; script-src 'self' 'unsafe-inline' 'unsafe-eval' https:; style-src 'self' 'unsafe-inline' https:; img-src 'self' data: blob: https:; font-src 'self' data: https:; connect-src 'self' https: wss:; frame-ancestors 'self'; X frame options: SAMEORIGIN; X content type options: nosniff; Referrer policy: strict-origin-when-cross-origin; Permissions policy: camera=(), microphone=(), geolocation=(), payment=(); Via: 1.1 8109fadbc132b410ecc2c3df250d6144.cloudfront.net (CloudFront); X cache: Miss from cloudfront
安全信号
SA Scamadviser 警告 1/100
This website does not have many visitors We detected cryptocurrency services which can be high risk We could not find a valid SSL certificate while the site offers financial services
DNSFilter considers this website safe
网络安全情报 注册商背景
注册商背景 NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
NiceNIC裁决 全面调查

关于 polexbot.pro 的问题

polexbot.pro 是正规网站吗?

根据记录在案的证据,PhishDestroy将polexbot.pro评定为严重风险等级(证据评分 100/100);该记录首次出现于2026-10-25。被外部黑名单列入:MetaMask, SEAL。本站评分和名单收录本身不能证明欺诈。请核对每个来源的日期和具体网址。

在 polexbot.pro 连接钱包安全吗?

鉴于上述风险信号,请勿在此处连接钱包、签署消息或approve代币权限。已确认的区块链交易无法撤销。

如果我使用过 polexbot.pro,该怎么办?

  • 输入了密码 — 请在该服务以及您使用过相同密码的其他所有网站上修改该密码
  • 开启双因素认证 — 在提供该服务的地区,身份验证应用比短信验证码更安全
  • 已支付或已输入的银行卡或银行信息 — 请通过卡片上的联系方式或其官方网站联系您的银行或支付服务商
  • 已连接钱包,但未签署任何内容 — 在钱包中断开该站点的连接并拒绝待处理的请求;仅建立连接本身并不会转移资金
  • 批准代币支出 (approve / permit) — 使用代币授权检查器撤销该授权
  • 分享了助记词或私钥 — 将剩余资金转移到一个带有新助记词的新钱包中;该已泄露的钱包已不再安全
  • 下载了文件 — 请勿打开该文件,并使用安全软件对设备进行扫描

请保留地址、日期、付款或交易详情以及相关信息,以便向警方或其他主管机关报案。 报案并不保证能追回款项。 分步帮助指南:紧急处理指南。

延伸阅读

摘自存储页面分析

观察到的指标

10 wallet · 0 Telegram

完整的提取值、其区块链及采集来源。在页面内容中发现的地址并不能证明谁控制该地址。

ETH
0x06dc51826bc524d9a83770e7de9dd7e005b04524Format validated · Domain analysis
ETH
0x66ad4221d66358ab9867f6d8cae73ede08e5cc4eFormat validated · Domain analysis
ETH
0x6916cc00aa1c3e75ecf4081df7cae7d2f3592fd4Format validated · Domain analysis
ETH
0x76d90685ded3907b5bba8af633812aceca00205aFormat validated · Domain analysis
ETH
0x76eca4109d0dfe8649d5e3861dfccac67ae7d630Format validated · Domain analysis
ETH
0x8b4bca1d794779e66e023d44391b2a86c5ab541bFormat validated · Domain analysis
ETH
0x9bbf8abf929eddbb4da10535cf4c02db33f4c59fFormat validated · Domain analysis
ETH
0xa19cbababc312f9df185e49d7004c249ed1ade6bFormat validated · Domain analysis
ETH
0xa9c94c974a34abd275b7d576f14bf955bad543d2Format validated · Domain analysis
ETH
0xb392b0234600393289f7a5a0dc32af604ea0fc73Format validated · Domain analysis

已记录IoC提取结果 2026-10-25 05:00 UTC

黑名单匹配项2个外部 + PhishDestroy列表 · MetaMask · PhishDestroy · SEAL 2
MetaMask 已列入 查看来源
PhishDestroy PhishDestroy列表 查看来源
SEAL 已列入 查看来源

最近检查

页面快照 (6)

所有捕获链接和哈希值 (6)
polexbot.pro: Crypto scam — Blocked by MetaMask, flagged by SEAL, Spamhaus DBL, 6/92 VirusTotal engines. PhishDestroy risk score 100/100 (critical).
社交媒体预览卡片 polexbot.pro: Crypto scam — Blocked by MetaMask, flagged by SEAL, Spamhaus DBL, 6/92 VirusTotal engines. PhishDestroy risk score 100/100 (critical). v eff4050aa871

域名详情

域名
URLScan 判定 分析完成 评分 0 引擎判定:恶意 · 评分 97 报告 ↗
IP 信誉 德国108.138.26.63 0/100滥用评分 · 针对该服务器IP地址的滥用报告,而非针对该域名的报告;分数越高,情况越严重 该IP地址尚未被上报至滥用数据库,但该域名本身已被识别为钓鱼网站。 0 条举报 已检查 2026-10-25
OTX 标签 2026-10activeall-domainsblocklistcontentcryptodomainsdrainerfraudlivemonthlyphishdestroyphishingscam
注册商 NiceNIC RU(RU) PhishDestroy调查
滥用举报联系方式abuse@nicenic.net
ICANN 注册管理机构ICANN Lookup (RDAP) →
注册信息有效期至 2027-10-24
HTTP 状态码301 Moved Permanently
技术详情来源与时间戳
首次发现2026-10-25
DOM 分析已分析 2026-10-25评分 90/1007 个品牌信号
IoC Extractionscanned 2026-10-2510 wallet · 0 Telegram IoCs
提交的网址http://polexbot.pro/
网站图标哈希值
案件 ID
观察到的页面标题
Polexbot: Automated Polymarket Bot for 5-Minute Crypto Rounds
自动生成的品牌引用
Across Ankr Celer MetaMask Near Signal Ups
TLS 证书
颁发者 Amazon / Amazon RSA 2048 M01 · 存储的有效期将在 168 天后结束

网络 & 证书

已存档技术证据

网络 & DNS

IP 地址
德国108.138.26.63
网络 ASN
AS16509
AS名称
AMAZON-02 - Amazon.com, Inc., US
组织
Amazon.com, Inc.
观测地点
德国Frankfurt am Main, DE
服务器标头
nginx

域名服务器 4

  • ns-1264.awsdns-30.org
  • ns-2036.awsdns-62.co.uk
  • ns-722.awsdns-26.net
  • ns-95.awsdns-11.com

SOA

  • nsname: ns-1264.awsdns-30.org
  • hostmaster: awsdns-hostmaster.amazon.com
  • serial: 1
  • refresh: 7200
  • retry: 900
  • expire: 1209600
  • minttl: 86400

位置信息描述的是 IP 网络。

TLS 证书

签发者
Amazon / Amazon RSA 2048 M01
生效时间
2026-10-24 00:00:00
到期时间
2027-05-09 23:59:59
主机名匹配
是
有效期
在存档的有效期内
采集来源
PhishDestroy collector
证书指纹c9ac600b3e61e970e6fb829868181c596c92bb2bb8e6f4964d64c0cbdc8137ed
证书名称 · 2 个 SAN
  • polexbot.pro
  • www.polexbot.pro

已保存的证书元数据。未带时区的证书日期按存档原样显示。传输加密并不能证明该网站值得信任。

最新分类结果 2026-11-22 11:59 UTC

最近一次检查时,该网站正在将访问者重定向到其他地址。

技术细节
主要结局指标 Redirecting reason: HTTP redirect observed 80% confidence
来源 source: Current Http Probe
证据层 Availability: Redirecting DNS: Resolved Registration: Active
最新的 HTTP 观察结果 Redirecting HTTP redirect observed 80% 2026-11-22 11:59 UTC
RDAP注册 有效 NICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765 RDAP HTTP 200 source: Rdap Status Collector AddperiodclientDeleteProhibitedclientTransferProhibited expires 2027-10-24 05:59 UTC 已检查 2026-10-26 05:36 UTC
观测时间线 last reachable: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
已注册的子域名2

保存在域名记录或证书透明度缓存中的主机名。仅凭主机名本身无法确定当前是否可用或存在恶意活动。

  • origin.polexbot.pro域名记录
  • www.polexbot.pro域名记录
技术 · 9 identified
打开完整记录
注册与观摩详情9

注册证据

RDAP状态
addperiod · clientdeleteprohibited · clienttransferprohibited
RDAP响应
200
注册证据中的注册商
NICENIC INTERNATIONAL GROUP CO., LIMITED
注册商 IANA ID
3765
RDAP 记录的到期时间
注册观测记录
注册信息来源
rdap_status_collector

可用性观测数据

最近一次可访问观测
估算依据
当前可访问

估算时间描述的是一个观测时间窗口。它并不能证明注册商采取了措施,也不代表网站变为不可访问的确切时刻。

所有存储的数据122
打开完整记录

捕获的网络请求

网络请求: 34 SHA-256 哈希值: 29 URLScan扫描:

URLScan在加载页面时记录的网络请求。URLScan并非为每个请求都提供哈希值。 PhishDestroy 于 2026-10-29 01:58 UTC 检索到了此列表。

在 URLScan 上打开此扫描 01a1715a-4da1-718d-9999-b133425d7cd7 ↗

伪装检测

比较浏览器与爬虫各自收到的内容,并检查是否存在 Keitaro 流量分发。

页面标题不同

我们的扫描器无法完成此项检查。

浏览器
Polexbot: Automated Polymarket Bot for 5-Minute Crypto Rounds
爬虫
301 Moved Permanently
polexbot.pro
已存档的观测历史25
打开完整记录
所有保留的可用性观测数据134
打开完整记录

威胁响应流程

  1. 发现 · 已记录
  2. 分析 · 已记录
  3. 通知 · 已记录
  4. 监控 · 进行中

已记录事件:13。这些记录描述了收集到的证据、外发通知及黑名单发布情况;它们并不意味着调查已完全结束或该网站已被下线。

主动发现与数据摄入威胁已收录 已记录
  • 威胁已收录
    检测到 polexbot.pro,并已排入队列等待全面分析
威胁情报核查Spamhaus DBL · URLScan.io捕获 · URLScan评估结果 · Cloudflare Radar报告 · 黑名单检测 · OTX社区引用 · 注册商背景:NiceNIC · 自动品牌标签:Polymarket · 已收集的取证证据 · 已记录的技术分析 已记录
通知记录已记录报告发送 已记录
  • 已记录报告发送
    关于该域名的滥用报告存档记录;当时的注册商:Identitydigital。 滥用举报联系人:1。
    • abuse@identitydigital.com
发布与可用性已发布至 DestroyList · 监控仍在进行中 正在进行中
  • 已发布至 DestroyList
    该信息已收录于公共仓库 PhishDestroy/DestroyList 中
  • 监控仍在进行中
    该域名目前仍可访问或访问受限;后续检查可能会更新此观察结果。
    正在进行中

已记录的活动

4 条记录

生命周期

  1. 已添加至 PhishDestroy
  2. 已发送首份滥用报告+28分钟
  1. AlienVault OTX

    4 社区参考资料

    +15分钟
  2. 已发送滥用报告

    PD-20261025-0A50AD · 收据 82841

    abuse@identitydigital.com
    +19分钟
  3. URLScan

    页面已捕获

    +9分钟
  4. 已添加至 PhishDestroy

    polexbot.pro

我们的调查与报告流程

公开扫描、证据及滥用举报渠道

我们扫描可疑网址,审查公开检测结果,并通过相应的滥用举报渠道提交证据。上方的带日期事件记录了该域名的相关记录。下方的目录说明了更全面的工作流程。

01公开扫描与证据收集10个来源和工具组
urlscan.io 屏幕截图 · DOM · HTTP

捕获渲染后的页面、请求以及可见的基础设施。

VirusTotal 多引擎判定结果

比较各引擎的检测结果,并保留分析时间戳。

Cloudflare Radar DNS · 证书 · 分类

查看公开扫描结果及其记录的网络和分类数据。

AlienVault OTX 威胁情报快讯

查找相关指标参考及相关社区情报。

crt.sh 证书透明度

检查证书记录及相关主机名。

DNS安全过滤器 Quad9 · AdGuard · CleanBrowsing

比较安全解析器的响应,并记录观察到的拦截情况。

Web-Check 表面检查

检查公共DNS、TLS、HTTP及技术暴露面。

02滥用报告与后续处理域名注册商、主机服务商及安全渠道
  1. 确定相关服务提供商。 将注册和托管记录与相应的滥用联系人进行匹配。
  2. 准备证据包。 内容应包含网址、公开扫描记录、截图以及记录的观察结果。
  3. 发送报告。 在条件允许的情况下,请保留外发报告记录及收件人信息。
  4. 重新检查并发布更新。 后续可追踪扫描结果、服务商回复及网站可用性。

用于扫描、信誉检查和报告的安全服务列于下方。某项服务被列出并不意味着该服务已收到、接受或针对该特定域名采取了行动。已记录的提交内容显示在上方通知历史记录中。

按来源分类的所有存储记录

按来源浏览该域名的完整历史记录。下载内容包含所选来源的每条记录。日期将保留其原始字段标签。

将所有记录下载为 JSON 格式

证据与外部报告

已提交证据快照
发送时间: 台账记录: 1 案例 ID: PD-20261025-0A50AD 收件人: abuse@identitydigital.com
随举报存档的页面标题: Polexbot: Automated Polymarket Bot for 5-Minute Crypto Rounds
生成的 PDF 通知
深度分析

您是否受到该网站的影响?

你并不孤单,这也没有什么可羞耻的。 骗子是利用信任作案的老练罪犯。报告你的遭遇是对抗欺诈最有力的武器:你的报告可以防止他人受害,并帮助执法部门采取行动。 请先确保您的账户和资金安全,然后再进行举报。 如果凭据已泄露,请立即报告。 切勿理会声称可追回资金的诈骗者。

根据您实际采取的行动采取相应措施。如果输入了密码:请立即更改密码,并检查是否在其他地方重复使用过该密码。如果支付过款项或提供过银行卡信息:请联系您的银行或支付服务商。如果下载了文件:请对设备进行病毒扫描。然后报告该事件。

向哪里报案

该草稿仅供您个人保留。

首先确保资金安全:致电您的银行或撤销钱包授权。 当务之急 →

更多:国际及加密货币频道

正式报告渠道

更多官方举报渠道
SEAL 911 全球

当您的加密货币钱包正在被清空时,安全研究人员将提供紧急帮助。

FTC ReportFraud 美国

向美国联邦贸易委员会举报诈骗和欺诈行为。举报信息将录入执法部门使用的数据库。

IdentityTheft.gov 美国

附带分步恢复计划的官方身份盗用举报指南。

CISA 美国

向美国网络安全与基础设施安全局报告网络安全事件和网络钓鱼行为。

CSIRTs Network 欧洲联盟

欧盟各国计算机安全事件响应团队(CSIRT)名录。查找您所在国家的响应团队。

FIRST 全球

全球事件响应团队目录,可按国家和行业进行搜索。

ReportCyber 澳大利亚

请向澳大利亚网络安全中心和警方举报网络犯罪。

Scamwatch 澳大利亚

向由澳大利亚竞争与消费者委员会(ACCC)运营的国家反诈骗中心举报诈骗行为。

发生一起网络钓鱼事件后

针对受害者的建议与指导

请根据您提供过的信息选择相应的步骤。请将本报告的副本与您自己的记录一并保存。

我应该立即采取什么措施?

紧急

停止使用可疑网站。请通过官方应用或您已信任的网址访问真正的服务。

  • 输入了密码 — 请在该服务以及您使用过相同密码的其他所有网站上修改该密码
  • 开启双因素认证 — 在提供该服务的地区,身份验证应用比短信验证码更安全
  • 已支付或已输入的银行卡或银行信息 — 请通过卡片上的联系方式或其官方网站联系您的银行或支付服务商
  • 下载了文件 — 请勿打开该文件,并使用安全软件对设备进行扫描
  • 分享了助记词或私钥 — 将剩余资金转移到一个带有新助记词的新钱包中;该已泄露的钱包已不再安全
  • 已连接钱包,但未签署任何内容 — 在钱包中断开该站点的连接并拒绝待处理的请求;仅建立连接本身并不会转移资金
  • 批准代币支出 (approve / permit) — 使用代币授权检查器撤销该授权 (revoke.cash)
  • 发送了加密货币 — 请保存交易哈希值、您的地址和收款地址;区块链交易无法撤销

我应该收集哪些信息用于报案?

联邦调查局(FBI)指南

请将原始邮件、收据、消息和截图保存在安全的地方。基于事实的时间线有助于受理机构了解事件经过。 IC3 证据指南 ↗

  • 付款记录 — 如果您已付款,请保留收据,并记录好金额、日期、支付方和收款方的详细信息。
  • 确切日期和时间 — 每笔交易的详情以及与诈骗者的首次接触
  • 屏幕截图 — 诈骗网站、聊天消息、电子邮件、钱包交易、社交媒体
  • 所有网址和域名 诈骗者使用的(包括 polexbot.pro)
  • 通信 — 诈骗者使用的电子邮件、短信、电话号码、用户名

即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。

我应该向哪里举报这起诈骗?

  • 联邦调查局(FBI)IC3 — 互联网犯罪投诉中心(美国联邦举报渠道)
  • 欧洲刑警组织 — 欧洲网络犯罪报告(欧盟)
  • 您的银行或支付服务提供商 — 如果资金或卡片信息泄露,请立即通过官方联系方式联系其反欺诈团队。
  • 当地警方 — 即使无法立即采取行动,也能留下正式记录

举报并不能保证追回损失或启动调查,但及时、准确的交易数据可以帮助执法机构和服务提供商追踪事件。

网络钓鱼诈骗通常是如何运作的?

  • 虚假网站 — 与正规网站完全一致的克隆网站,仅域名略有改动
  • 杀猪盘 — 通过Telegram/WhatsApp/交友软件花数周时间建立信任,随后钱被骗走
  • 退款诈骗 — 诈骗者冒充资金追回机构并索要预付费用。在独立核实服务方之前,切勿分享助记词或付款
  • 利用人工智能实施的诈骗 — 深度伪造、自动化网络钓鱼以及人工智能生成的网站,使得欺诈行为更难被察觉

将来我该如何保护自己?

  • 将官方网站添加到书签 — 切勿点击来自电子邮件、私信或广告中的链接
  • 验证域名 — 查看 PhishDestroy 在进行互动之前,请检查HTTPS、拼写和域名注册时间。
  • “好得令人难以置信”=骗局 — 保证收益、名人代言、紧迫的截止日期

进一步的指导: NIST · 应对网络钓鱼FBI IC3 · 举报与证据联邦贸易委员会(FTC)· 资金追回诈骗

随时掌握最新信息,确保安全

请实时监控威胁,或者如果您认为这是误报,请对该条目提出异议

警惕“数据恢复”诈骗! 犯罪分子可能会冒充调查员、律师或追债员再次联系受害者。 请勿支付预付费用或共享凭证。 了解有关资金追回诈骗的更多信息 →
关于本报告来源、观测日期与更正

本报告汇总了已保存的页面快照、注册与网络记录、扫描器结果以及 PhishDestroy 举报历史。每个来源均保留各自的观测日期。打开来源报告即可查看原始结果。

AI 辅助分析的撰写时间: . 该内容描述了当时可获得的证据;后续的来源核查可能会导致情况发生变化。

快照记录的是当时显示的内容。扫描器结果记录的是该服务商在检查时的评估。有效证书或零检出结果都不能保证安全。

嵌入此报告附带证据链接的紧凑型小组件
HTML · IFRAME

嵌入此报告

在您的网站或博客上分享此威胁情报

embed.html
<iframe
  src="https://phishdestroy.io/zh/embed/domain/polexbot.pro"
  title="PhishDestroy threat report for polexbot.pro"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>