域安全和威胁情报

olsu.appwrite.network
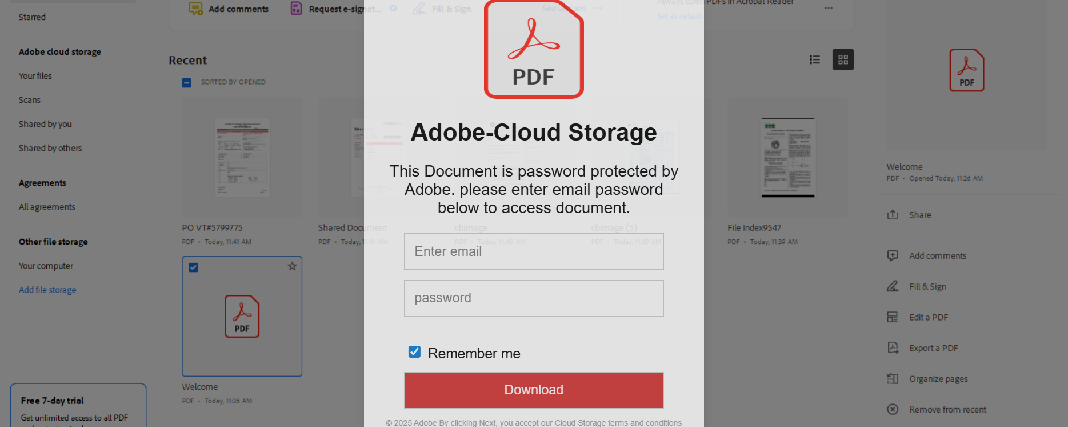
“Sign~in to view”
威胁判定
关键
100/100 证据评分
可用性
可达 · 访问受限
可达响应;页面内容未经验证
风险信号
病毒检测总数:8/89
URLQuery threat systems: 5 alerts
品牌冒充:Unknown
最后已知的活跃状态
Actions
API
ABUSE NOTICE · 7D+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@fastly.com.
The latest stored availability evidence still shows the domain reachable; 6 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
6 months
Reports sent
1
Latest case ID
PD-20260311-7EA0AC
Current status
HTTP 403 at latest stored check
报告概览
olsu.appwrite.network — 可达 · 访问受限 (HTTP 403). 品牌冒充:Unknown; 诈骗类型:Credential Phishing. 证据摘要: VirusTotal 8/89 (ADMINUSLabs, alphaMountain.ai, Chong Lua Dao, ESET, Forcepoint ThreatSeeker); URLQuery 5 alerts; CF Radar malicious; PhishDestroy score 100/100. 注册商: Fastly.
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
证据摘要
重要
This domain, olsu.appwrite.network, is flagged as a high-risk phishing resource targeting user credentials through a fabricated login interface. Analysis indicates the page title 'Sign~in to view' is designed to deceive users into submitting authentication details, likely mimicking a legitimate service. The domain was registered on March 11, 2026, and remains active as of July 12, 2026, resolving to the IP address 151.101.131.52. Infrastructure analysis reveals the use of Cloudflare, Varnish, and Fastly, which may obscure the true origin of the malicious activity and complicate takedown efforts. Technical indicators show the domain employs common web technologies such as Bootstrap, jQuery, HSTS, and Google Hosted Libraries, which are consistent with legitimate sites but are frequently leveraged in phishing campaigns to appear credible. The SSL certificate is issued by Certainly, providing encrypted connections that may further mislead users. The domain currently appears on one security blocklist and is detected by 12 out of 95 security vendors on VirusTotal, confirming its malicious classification. However, the specific phishing kit or targeted brand remains unidentified, limiting attribution. Defenders should prioritize blocking this domain at the DNS and web proxy levels to prevent user access. The IP address 151.101.131.52 should be monitored for additional malicious domains, as it may host further phishing resources. Given the domain's recent registration and active status, it is likely part of an ongoing campaign, and security teams should review logs for connections to this domain or IP within the past four months. No evidence suggests this domain is part of a broader malware distribution or command-and-control infrastructure, but continuous monitoring is recommended due to its persistence.
VirusTotal
8 det.
URLQuery
5 threat alerts
DNS Security
6/14
CF雷达
恶意
URLScan
TLS 证书
Certainly 26d
年龄
6 mo
观测状态
可达 · 访问受限 403

DestroyList
已列入
Reports Sent
1
数据覆盖范围
VirusTotal
8 / 89
URLQuery
5 threat-system alerts
PhishStats
checked — no match recorded
OTX
no community references
CF雷达
provider verdict: malicious
URLScan capture
存储的报告
URLScan verdict
分析完成
DNS 阻断
6/14
TLS
valid certificate, 26d
WHOIS
6 mo old
屏幕截图
3 captures · 3 sources
网络安全情报
DNS Provider Blocks
6 / 14
Threat Detection Systems
5 alerts
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | olsu.appwrite.network |
malicious | Sinkholed |
| DNS4EU | olsu.appwrite.network |
malicious | Sinkholed |
| DigiCert UltraDNS | olsu.appwrite.network |
malicious | Sinkholed |
| Quad9 DNS | olsu.appwrite.network |
malicious | Sinkholed |
| DigiCert UltraDNS | assets.appwrite.io |
malicious | Sinkholed |
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
VirusTotal Detections Update Jul 12, 2026 · 18:35 UTCVirusTotal scanner detections updated from 17 to 12. Added scanner alerts: ESET, Gridinsoft, Lionic, Sophos, VIPRE. Resolved alerts: CRDF, Emsisoft, Netcraft, Trustwave.
-
VirusTotal Detections Update Mar 11, 2026 · 03:35 UTCVirusTotal scanner detections updated from 0 to 13. Added scanner alerts: ADMINUSLabs, CRDF, Chong Lua Dao, CyRadar, DNS8, Emsisoft, Forcepoint ThreatSeeker, Fortinet, Netcraft, Trustwave, URLQuery, Webroot, alphaMountain.ai.
威胁响应 Pipeline
发现
Checks
Reports
可用性
15/16
Sent Report Recorded
Stored sent-report record for registrar Fastly, hosting provider, 1 abuse contact
abuse@fastly.com
公共封禁名单状态
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not observed
- 伪装评分
- 0/6
- Last cloaking scan
- Server header seen by scanner
swoole-http-server
Scanner note: alive_content: raw=short_403; http=403; via=https_proxy; server=swoole-http-server
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
已保存的截图 · 3 sources
域名情报
域名
URLScan Verdict
分析完成
score 0 report ↗
服务器 / ASN
swoole-http-server · AS54113 Fastly, Inc.
IP Context
Fastly shared edge
origin IP hidden
Edge-IP 声誉不属于此域。
Registrar (base domain)
Fastly
IP 地址
151.101.131.52
CDN
地理位置 San Francisco, US
网络AS54113 · Fastly, Inc.
源 IP 隐藏在 CDN 代理后面。边缘地址的反向 IP 结果包含不相关的租户;查找源头需要被动 DNS 或证书透明数据。
Registration (base domain)appwrite.network · 创建 2026年3月11日 (194d)
HTTP 状态码403 Forbidden
技术详情DNS、SSL SAN、时间戳
首次发现2026年3月11日
DOM Analysis
IoC Extraction
Submitted URLhttp://olsu.appwrite.network/
TLS Fingerprint
TLS Observation
TLS SAN Domainsappwrite.networkimagine.diy
案件 ID
ICANN OVERSIGHT
Registration: appwrite.network
认证和 RAA 背景
认证和 RAA 背景
Registrar accreditation and DNS abuse obligations
For the registrable domain appwrite.network behind this subdomain, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
技术 · 8 identified
Varnish
Bootstrap
UI frameworks
Cloudflare
CDN
jQuery
JavaScript libraries
HSTS
安全
Google Hosted Libraries
cdnjs
Popper
Detected via Cloudflare Radar · Wappalyzer engine
举报此域名
提交证据,帮助保护他人
VirusTotal 分析
8 / 89 安全供应商标记了该域
View on VT
Last analyzed Previous stored snapshot: 11 detections
ADMINUSLabs
alphaMountain.ai
Chong Lua Dao
ESET
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
Webroot
网站性能分析
Google PageSpeed Insights — mobile performance audit of olsu.appwrite.network · checked Jul 12, 2026
100
Good
Performance
FCP
0.77s
First Contentful Paint
LCP
0.77s
Largest Contentful Paint
CLS
0.01
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
0.77s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
社区报告
由 1 名社区成员报告;首次发现于 2026年3月11日
- 已存储报告
- 1
- 已报告的唯一 URL
- 1
已接受1
证据与外部报告
证券分析
已提交证据快照
Sent: Ledger records: 1
Case ID:
PD-20260311-7EA0AC Recipient: abuse@fastly.com Page title stored with report: Deployment blocked
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
OSINT与情报分析
DNS 与网络
SEO 与域名
您是否受到本网站的影响?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。


PhishDestroy listing review 不是执法报告
域名申诉
如果您拥有该域名并认为该列表不正确,请请求审核
警惕“数据恢复”诈骗! 犯罪分子可能会冒充调查员、律师或追债员再次联系受害者。 请勿支付预付费用或共享凭证。 了解有关康复欺诈的更多信息 →
相关基础设施与报告
Infrastructure map · olsu.appwrite.network
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 1
关于共享 Fastly 边缘的其他报告 6
这些报告解析为相同的共享边缘 IP。它们有助于报告发现,但并不意味着共同所有权或共享源服务器。
同一注册商: Fastly 6
Unknown impersonation 8
These domains also target 未知 users. View all Unknown threats →
Unknown kit 8
Part of the 未知 phishing campaign. View all campaign domains →
最近的威胁报告 6
最近添加了来自 PhishDestroy 数据库的报告。这些发现链接并不意味着共享基础设施或所有权。
 primarkpolska.pl
 yeniyerler.com
 ziajasklep.club