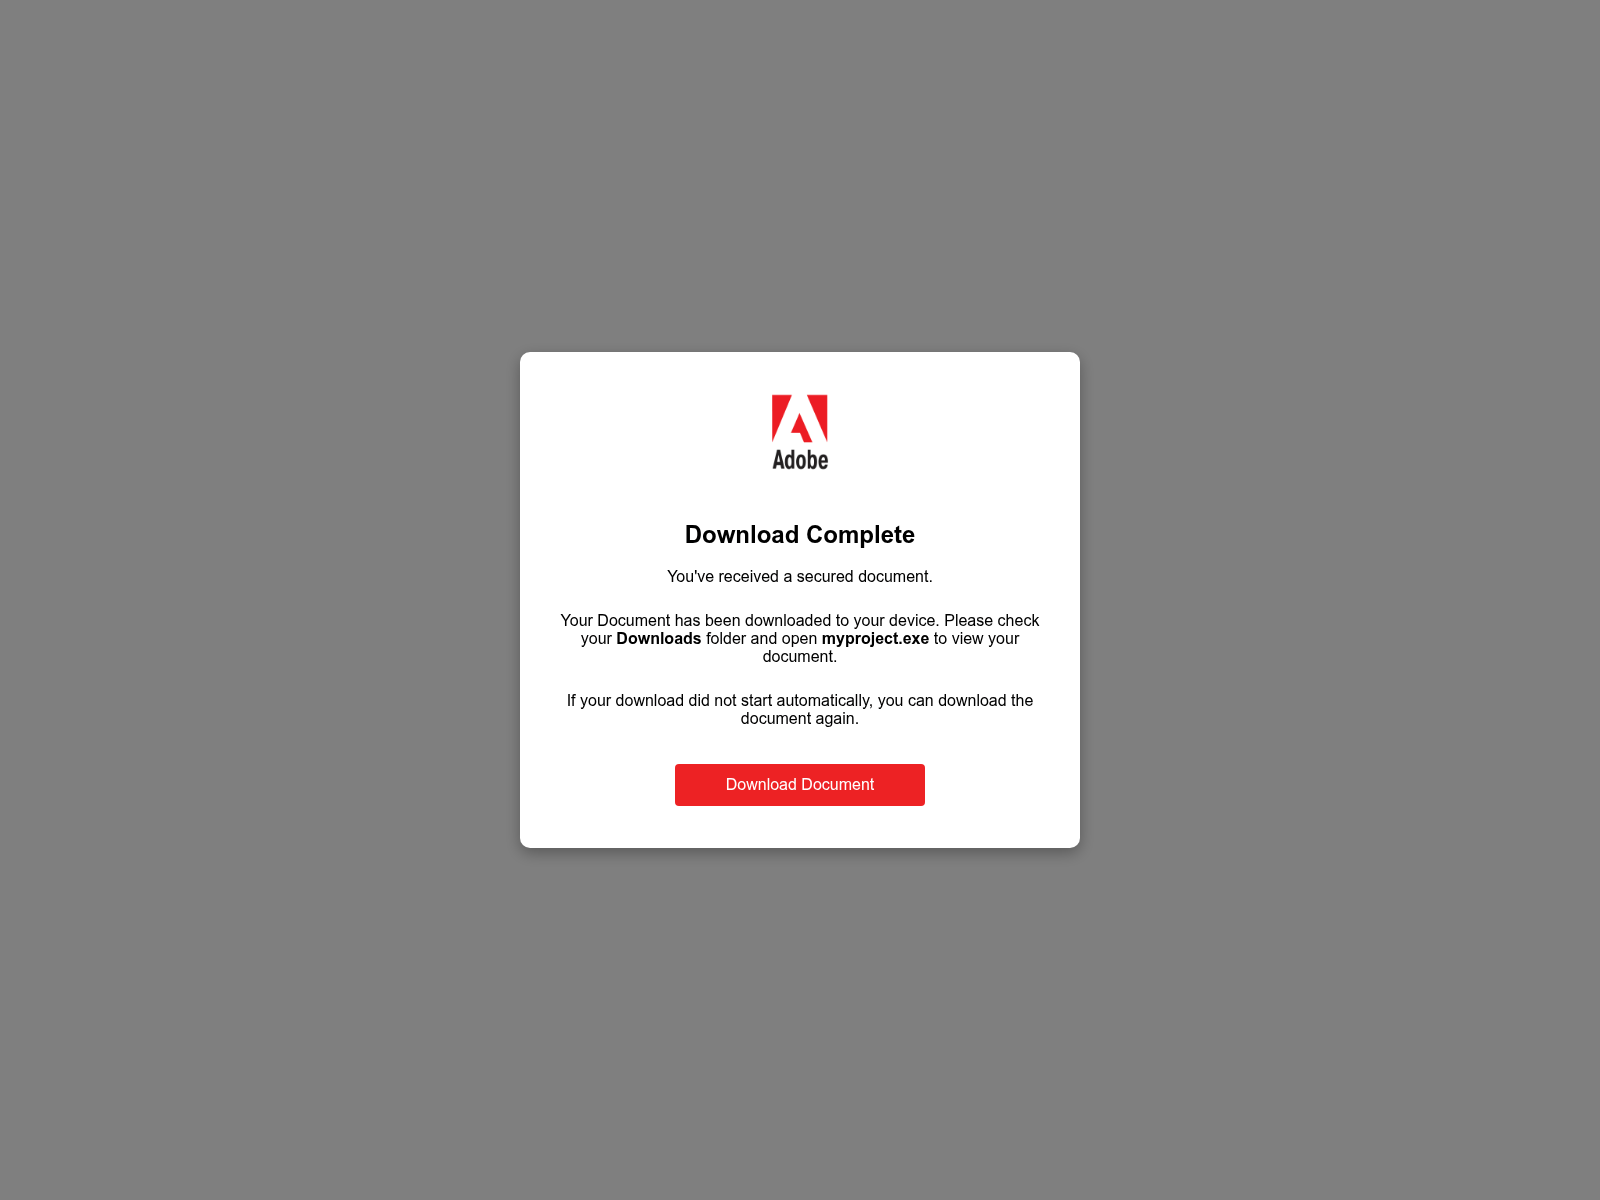
The site myprojectdocument.pw mimics an Adobe document download portal to trick visitors into executing a suspicious file named myproject.exe. If you downloaded and ran this executable, immediately disconnect your device from the network and scan for malware.
URLScan截图 · 2026-11-21 17:39 UTC · SHA-256 f18bba03…3832553
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Adobe document download interface
The page displays a centered white dialog box featuring the Adobe logo and brand name at the top. Large bold text reads "Download Complete" followed by the subheadline "You've received a secured document." The body text instructs the user: "Your Document has been downloaded to your device. Please check your Downloads folder and open myproject.exe to view your document." A smaller note states, "If your download did not start automatically, you can download the document again." At the bottom sits a prominent red button labeled "Download Document." The background is a solid neutral grey, focusing attention entirely on the fake delivery prompt designed to trick users into executing an arbitrary program.
Security detections and executable delivery
urlscan classified the page as malicious, 24 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and 1 AlienVault OTX community report references it, with vendors like Kaspersky, ESET and BitDefender identifying it as malicious. This confirms the page is actively used to distribute unauthorized files rather than legitimate documents from the official adobe.com site. Its PhishDestroy evidence score is 60/100 (high).
Recommended actions for visitors
If you arrived at myprojectdocument.pw expecting a standard file, do not click the red download button or open any downloaded executables. Visitors who already ran myproject.exe should inspect their systems for unauthorized changes, run a thorough antivirus scan, and change critical account credentials. Always obtain documents and software through official channels like adobe.com rather than unverified third-party addresses.
myprojectdocument.pw presents an Adobe document download page and prompts visitors to run myproject.exe, flagged by urlscan and 24 VirusTotal engines.
AI摘要
Adobe document download interface The page displays a centered white dialog box featuring the Adobe logo and brand name at the top. Large bold text reads "Download Complete" followed by the subheadline "You've received a secured document." The body text instructs the user: "Your Document has been downloaded to your device. Please check your Downloads folder and open myproject.exe to view your document." A smaller note states, "If your download did not start automatically, you can download the document again." At the bottom sits a prominent red button labeled "Download Document." The background is a solid neutral grey, focusing attention entirely on the fake delivery prompt designed to trick users into executing an arbitrary program. Security detections and executable delivery urlscan classified the page as malicious, 24 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and 1 AlienVault OTX community report references it, with vendors like Kaspersky, ESET and BitDefender identifying it as malicious. This confirms the page is actively used to distribute unauthorized files rather than legitimate documents from the official adobe.com site. Its PhishDestroy evidence score is 60/100 (high). Recommended actions for visitors If you arrived at myprojectdocument.pw expecting a standard file, do not click the red download button or open any downloaded executables. Visitors who already ran myproject.exe should inspect their systems for unauthorized changes, run a thorough antivirus scan, and change critical account credentials. Always obtain documents and software through official channels like adobe.com rather than unverified third-party addresses.
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:59 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:59 UTClast content: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
已注册的子域名1
保存在域名记录或证书透明度缓存中的主机名。仅凭主机名本身无法确定当前是否可用或存在恶意活动。
www.myprojectdocument.pw域名记录
技术 · 1 identified
A
Apache HTTP Server
Web服务器
Apache is a free and open-source cross-platform web server software.

 WBeen
 91.92.41.104


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT