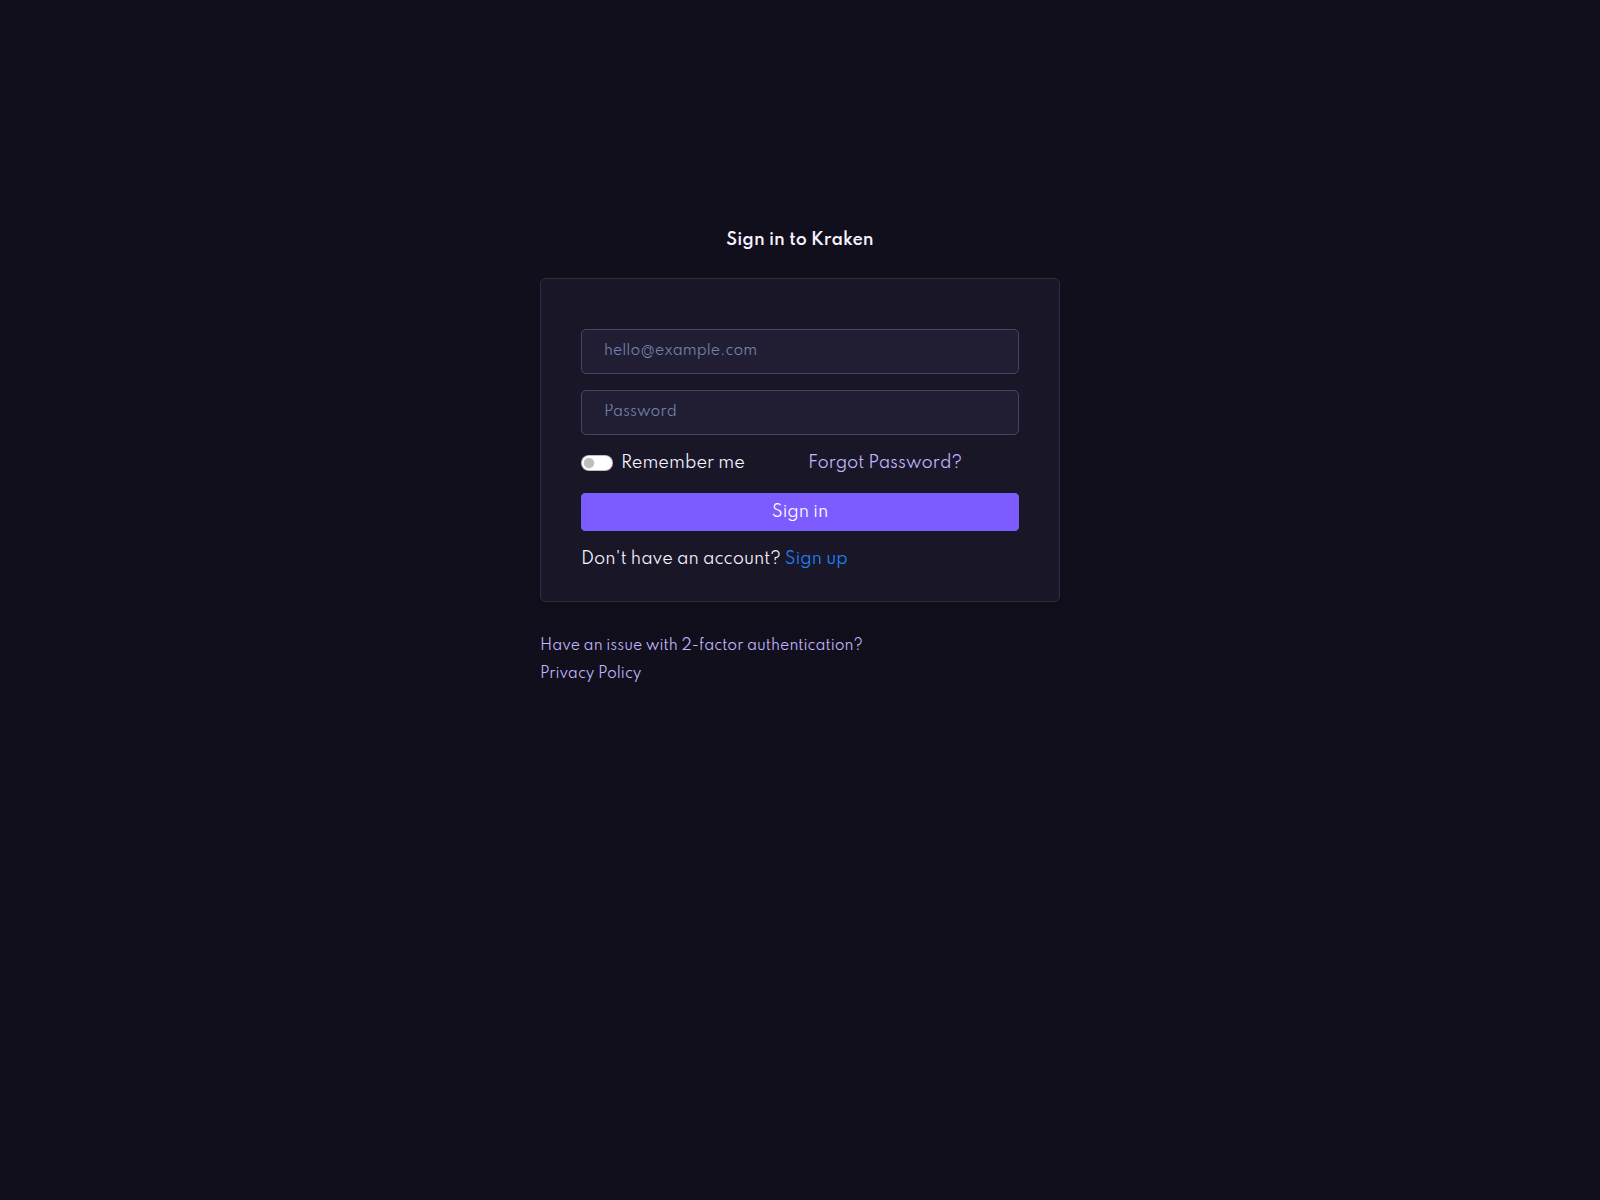
On 2026-11-06, krakenwalletseth.com redirected from consultation.php to signin.php on the same host, and the captured page displays a sign-in form. The heading reads "Sign in to Kraken" above a dark card containing an email field with placeholder "hello@example.com", a Password field, a "Remember me" toggle, a "Forgot Password?" link, and a purple "Sign in" button. Below the button, the text "Don't have an account? Sign up" appears, along with links for 2-factor authentication issues and a Privacy Policy.
URLScan截图 · 2026-11-06 00:50 UTC · SHA-256 298ec37a…08b4447
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-06, krakenwalletseth.com redirected from consultation.php to signin.php on the same host, and the captured page displays a sign-in form. The heading reads "Sign in to Kraken" above a dark card containing an email field with placeholder "hello@example.com", a Password field, a "Remember me" toggle, a "Forgot Password?" link, and a purple "Sign in" button. Below the button, the text "Don't have an account? Sign up" appears, along with links for 2-factor authentication issues and a Privacy Policy.
The stored VirusTotal domain result reports 11 detections out of 92 engines. CRDF reported "malicious"; VIPRE reported "malware".
krakenwalletseth.com: Recorded Sign-In Page with Kraken Branding
AI 描述
PhishDestroy records krakenwalletseth.com showing a sign-in page branded "Sign in to Kraken" with email and password fields and a Sign in button.
AI摘要
On 2026-11-06, krakenwalletseth.com redirected from consultation.php to signin.php on the same host, and the captured page displays a sign-in form. The heading reads "Sign in to Kraken" above a dark card containing an email field with placeholder "hello@example.com", a Password field, a "Remember me" toggle, a "Forgot Password?" link, and a purple "Sign in" button. Below the button, the text "Don't have an account? Sign up" appears, along with links for 2-factor authentication issues and a Privacy Policy. The stored VirusTotal domain result reports 11 detections out of 92 engines. CRDF reported "malicious"; VIPRE reported "malware".
证据层Availability: Reachable but protectedDNS: Resolved
最新的 HTTP 观察结果可接触但受保护CaptchaChallenge85%2026-11-22 11:29 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:29 UTClast content: 2026-11-17 23:21 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.