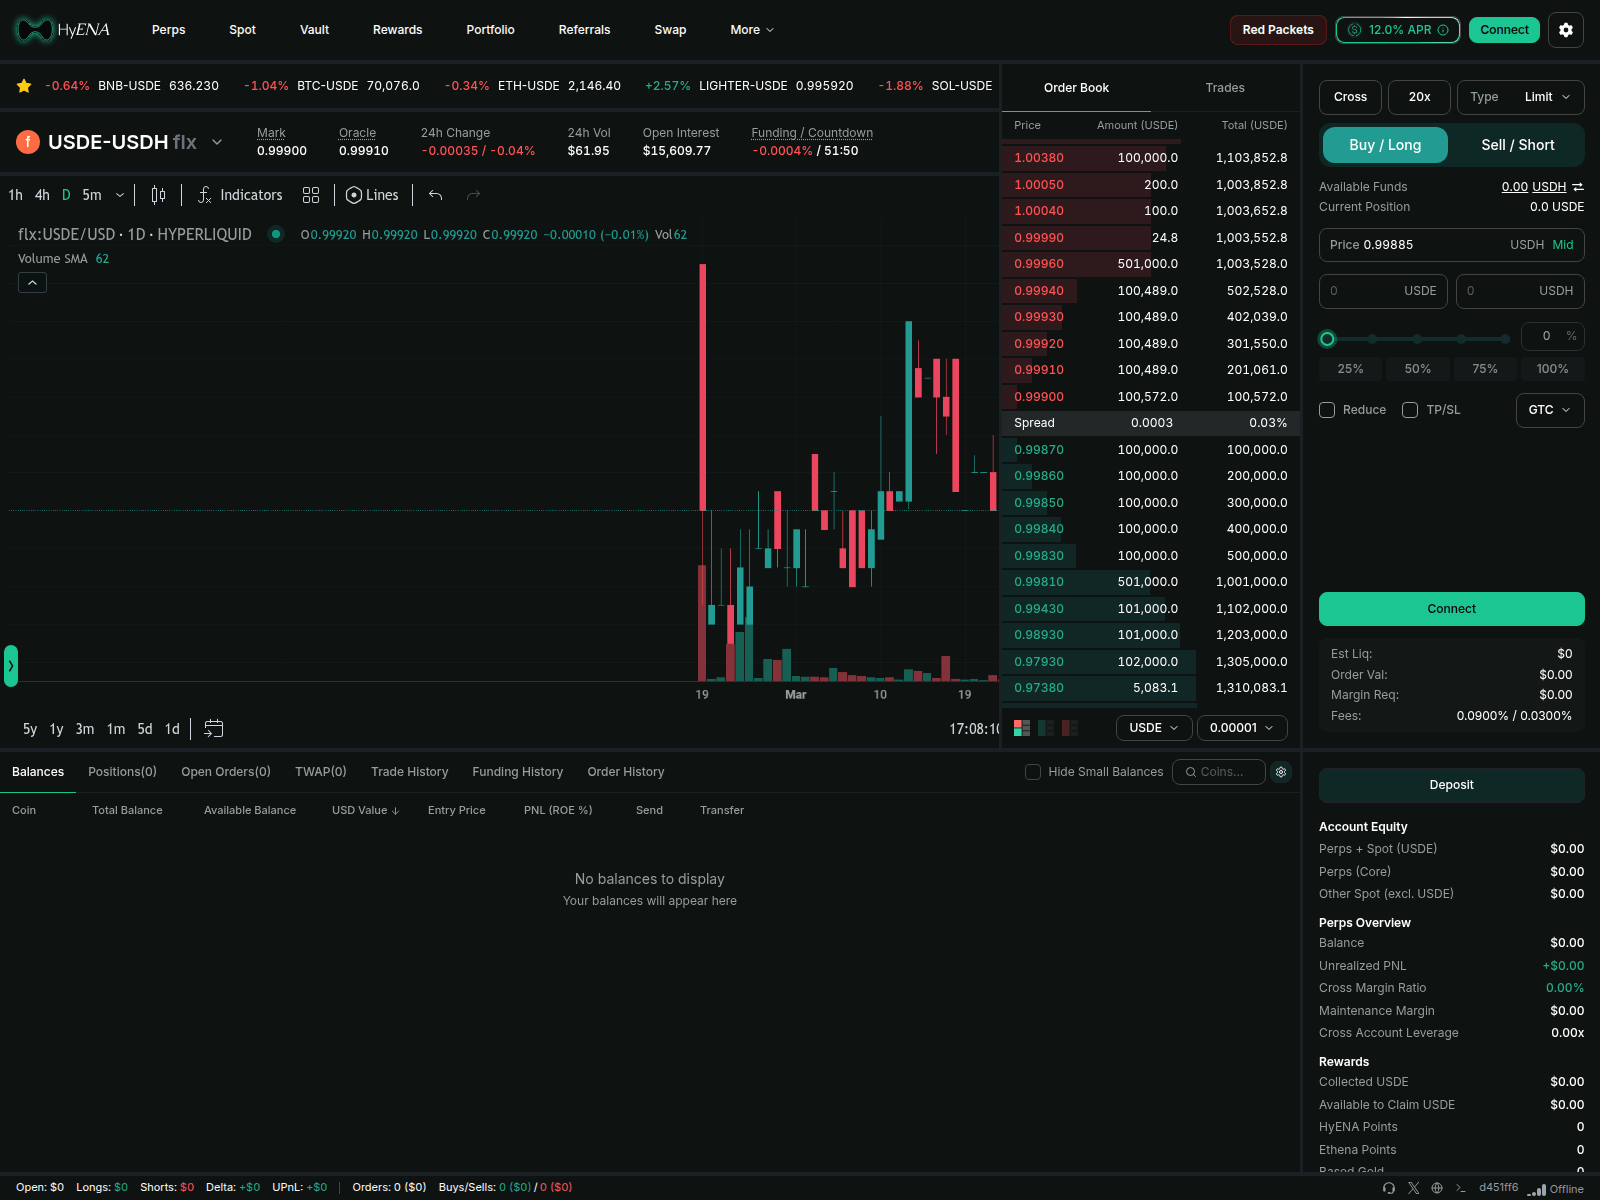
On 2026-11-08, hyanea.trade displayed a dark-themed trading interface branded "HyENA" in the header. The main area shows a candlestick chart for the USDE-USDH pair with mark, oracle, 24-hour change, volume, open interest, and funding countdown figures, alongside a ticker strip of other pairs. An order book panel lists bid and ask prices with amounts, and a right-hand panel offers Buy/Long and Sell/Short controls with price, quantity, leverage, and reduce-only options. A Connect button and account equity, perps overview, and rewards figures are shown, with a balances table stating no balances to display.
URLScan截图 · 2026-11-08 22:53 UTC · SHA-256 0b306fdc…9e532b3
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-08, hyanea.trade displayed a dark-themed trading interface branded "HyENA" in the header. The main area shows a candlestick chart for the USDE-USDH pair with mark, oracle, 24-hour change, volume, open interest, and funding countdown figures, alongside a ticker strip of other pairs. An order book panel lists bid and ask prices with amounts, and a right-hand panel offers Buy/Long and Sell/Short controls with price, quantity, leverage, and reduce-only options. A Connect button and account equity, perps overview, and rewards figures are shown, with a balances table stating no balances to display.
The stored VirusTotal domain result reports 2 detections out of 92 engines. Netcraft reported "malicious"; alphaMountain.ai reported "suspicious".
hyanea.trade: Recorded HyENA Perpetual Trading Terminal
AI 描述
PhishDestroy records hyanea.trade as a page presenting a HyENA-branded perpetual trading terminal with chart, order book, and order entry controls.
AI摘要
On 2026-11-08, hyanea.trade displayed a dark-themed trading interface branded "HyENA" in the header. The main area shows a candlestick chart for the USDE-USDH pair with mark, oracle, 24-hour change, volume, open interest, and funding countdown figures, alongside a ticker strip of other pairs. An order book panel lists bid and ask prices with amounts, and a right-hand panel offers Buy/Long and Sell/Short controls with price, quantity, leverage, and reduce-only options. A Connect button and account equity, perps overview, and rewards figures are shown, with a balances table stating no balances to display. The stored VirusTotal domain result reports 2 detections out of 92 engines. Netcraft reported "malicious"; alphaMountain.ai reported "suspicious".
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
证据层Availability: Content servingContent: Content served at rootDNS: ResolvedRegistration: Active
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 12:00 UTC
RDAP注册有效NICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765RDAP HTTP 200source: Rdap Status CollectorclientDeleteProhibitedclientTransferProhibitedexpires 2027-03-16 16:14 UTC已检查 2026-11-15 06:13 UTC
观测时间线last reachable: 2026-11-22 12:00 UTClast content: 2026-11-22 12:00 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 NiceNIC
 172.67.162.234


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT