Spamhaus DBL
网络钓鱼域名

The site fees.claimed.work presents a token market overview interface under the Claimed brand, featuring a prominent button to connect a Web3 wallet via Reown. Visitors should avoid connecting any cryptocurrency wallet or signing authorization requests on this page.
分析报告仅提供英文版本页面标题: “Claimed — Token rewards estimate”
选择实际发生的情况,并随着操作进程逐项勾选相应步骤。勾选记录仅保存在当前浏览器中。
专家视图包含所有部分:DNS、TLS、网络请求、哈希值以及原始 JSON 数据。
已发送报告日志记录了首份外发报告的时间为 。记录的收件人是 abuse@publicdomainregistry.com. 最新的存储可用性证据仍显示该域名可访问; 32 hours 自首份外发报告发布以来,已过去……
ICANN RAA §3.18 描述了域名注册商的滥用联系渠道及处理义务。本节记录了发送时间戳、收件人列表、案件标识符以及后续的可用性。本节内容本身并不构成对收件、确认、调查、整改或合同违约的证明。
PhishDestroy 保存了 fees.claimed.work 的记录。各来源的观测有各自的日期;缺少检查并不代表安全。
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
PhishDestroy 于 2026-11-20 首次记录了 fees.claimed.work。被外部黑名单列入:ScamSniffer。风险:高(证据评分 58/100)。注册商:PDR。状态:最后一次已知在线状态。托管:Cloudflare, Inc。PhishDestroy 已发送1 份滥用举报。请勿输入登录凭据,也不要连接钱包。
 188.114.96.3Cloudflare, Inc. · CDN
 PDR
URLScan截图 · 2026-11-20 20:29 UTC · SHA-256 27b081a9…5f82940
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
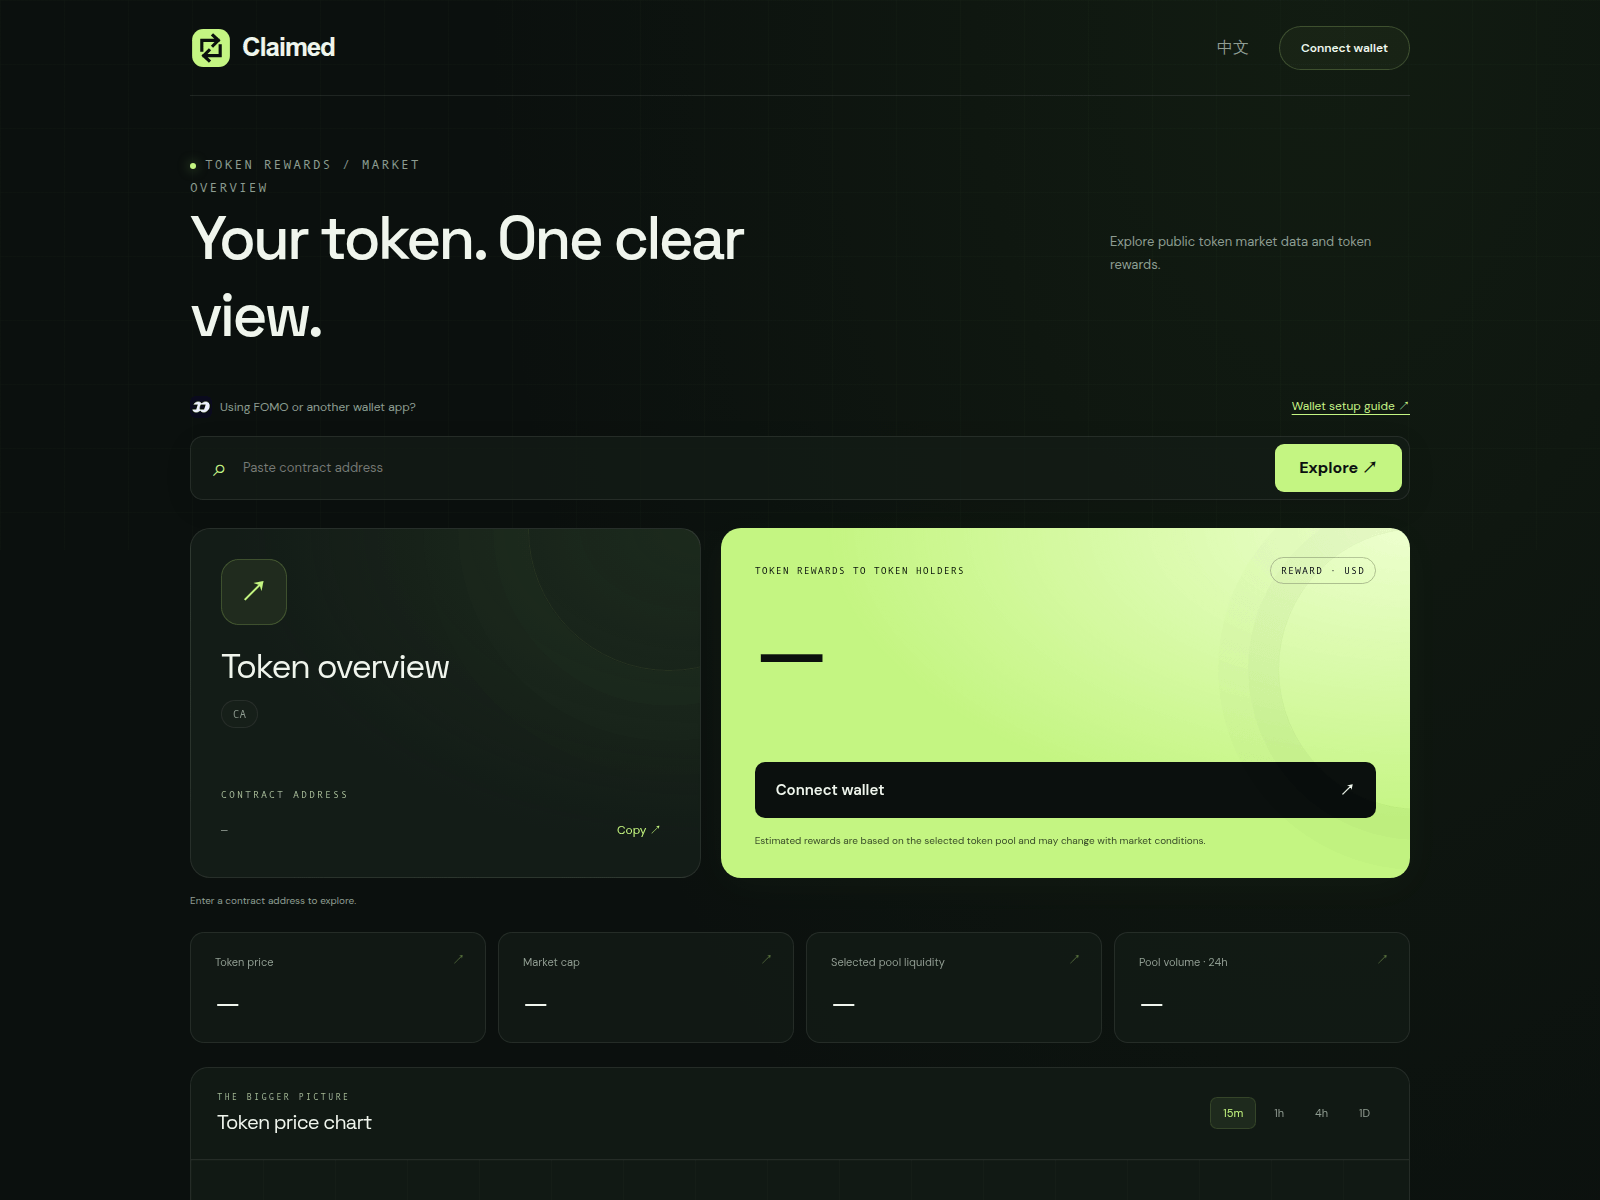
The page opens on a dark green grid background with the brand name "Claimed" in the top left corner, accompanied by a language toggle for Chinese and a "Connect wallet" button in the upper right. The main headline reads "Your token. One clear view." with a smaller subtitle stating "Explore public token market data and token rewards." Below the header, a search bar invites users to "Paste contract address" alongside an "Explore" button. Further down, the interface displays a card labeled "Token overview" next to a bright green section titled "Token rewards to token holders" which features a dark "Connect wallet" button and small text reading "Estimated rewards are based on the selected token pool and may change with market conditions." Additional metric cards at the bottom show placeholders for token price, market cap, selected pool liquidity, and pool volume, followed by a section titled "The bigger picture" showing a token price chart with time intervals of 15m, 1h, 4h, and 1D.
The primary interactive feature on the page is the wallet connection interface powered by Reown, which invites visitors to link their cryptocurrency wallet to view rewards or interact with token pools. Connecting a wallet through this prompt could lead to signing malicious transactions or token approvals that grant unauthorized access to digital assets.
It was registered on 10 Nov 2026, 9 days before it was first reported, presenting a brand-new interface while it sits behind Cloudflare, which hides the real server. The domain was registered through PDR Ltd. d/b/a PublicDomainRegistry.com and it still answered requests on 20 Nov 2026 at 21:30 UTC while offering no verified history or established track record under the Claimed brand name.
网络钓鱼域名
扫描报告
打开报告页面快照
SHA-256 58ad4c75…e76b5a0
单独存储的监控快照;不会替换主报告记录,也不会确定当前的可用性。
45 / 100 · 启发式得分 · 1 个品牌引用 · 0 个分类
仅为内容启发式评分;并非最终评分
打开报告此过时的监控分析与上文的主要PhishDestroy分析是分开的。启发式评分并非经过测量的概率。
叙事生成元数据
打开报告叙述生成日期与观测日期不同。这些是保留的出版字段,并非额外的独立检测结果。
结果反映各来源的采集时间。零检出不代表安全。OTX 引用为社区发布的内容。
已存档的页面、网络和扫描器观测结果,按来源和观测时间分组。
| DNS防护结果 | Resolvers: 12; Blocked count: 0 |
|---|---|
| 页面标题与元数据 | Title: Claimed — Token rewards estimate; Themecolor: #101410 |
| 追踪器 | Requests: 4; Trackers: (Name: Google Fonts; Company: Google; Country: US; Category: Hosting; Requests: 1) |
| 表单与混合内容 | Third party scripts: 0 |
| 状态 | Up: ✓; Code: 200; Timings: DNS: 0; Wait: 119; Download: 3; Response ms: 154 |
| TLS连接 | Alpn: h2; Cipher: TLS_AES_256_GCM_SHA384; Protocol: TLSv1.3; Versions: TLSv1, TLSv1.1, TLSv1.2, TLSv1.3; Authorized: ✓; Forward secrecy: ✓ |
| 端口 | Open: 80, 443, 8080 |
| Carbon | Bytes: 43791; Co2 grams: 0.0016; Cleaner than: 40 |
| DNS server | NS: (IP: 162.159.38.128; Host: walk.ns.cloudflare.com), (IP: 172.64.33.201; Host: lynn.ns.cloudflare.com); Zone: claimed.work |
| Quality | Cls: 0.021; Seo: 92; Si s: 1.66; Fcp s: 1.66; Lcp s: 1.66; Tbt ms: 1406; Performance: 74; Accessibility: 100; Best practices: 96 |
| 位置 | IP: 188.114.96.3; ASN: 13335; Org: Cloudflare, Inc.; City: Francisco; Country: US |
| SSL | San: *.claimed.work, claimed.work; Bits: 256; Chain: claimed.work, YE2, Root YE, ISRG Root X2, ISRG Root X1; Issuer: Let's Encrypt / YE2; Serial: 05FCF6B9053564398C8E92F659C8F71B0740; SHA256: 1ad2ee07145a85fbbb388708fd2214b6c8bc5015830a1e8d499cddde5c9e8898; Subject: claimed.work; Valid to: 2027-02-08T20:57:43Z; Valid from: 2026-11-10T20:57:44Z |
| DNS 记录 | A: 188.114.97.3, 188.114.96.3 |
| DNSsec | Ds: ✗; Rrsig: ✗; Dnskey: ✗ |
| Hsts | Message: Site does not serve any HSTS headers. |
| HTTP 安全策略 | Xframeoptions: ✗; Referrerpolicy: ✗; Xxssprotection: ✗; Permissionspolicy: ✗; Xcontenttypeoptions: ✗; Contentsecuritypolicy: ✗; Stricttransportpolicy: ✗; Crossoriginopenerpolicy: ✗; Crossoriginembedderpolicy: ✗; Crossoriginresourcepolicy: ✗ |
| 防火墙 | Waf: Cloudflare; Has waf: ✓ |
| Get IP | IP: 188.114.96.3; Family: 4 |
| 重定向 | Chain: https://fees.claimed.work |
| 技术栈 | Technologies: Node.js, Vue.js, Nuxt.js, lit-html 3.3.3, lit-element 4.2.2, Cloudflare, HTTP/3 |
| 页面链接 | Internal: https://fees.claimed.work/, https://fees.claimed.work/wallet-guide; Internal count: 2 |
| 注册记录 | Registrar: PDR Ltd. d/b/a PublicDomainRegistry.com; Registrar iana ID: 303; Registrar URL: publicdomainregistry.com; Created: 2026-11-10T21:51:41Z; Updated: 2026-11-15T21:51:41Z; Expires: 2027-11-10T21:51:41Z; Status: clientTransferProhibited https://icann.org/epp, serverTransferProhibited https://icann.org/epp; Nameservers: lynn.ns.cloudflare.com, walk.ns.cloudflare.com; Dnssec: unsigned |
| HTTP 头 | Headers: Server: cloudflare; Content type: text/html; charset=utf-8 |
根据记录在案的证据,PhishDestroy将fees.claimed.work评定为高风险等级(证据评分 58/100);该记录首次出现于2026-11-20。被外部黑名单列入:ScamSniffer。本站评分和名单收录本身不能证明欺诈。请核对每个来源的日期和具体网址。
鉴于上述风险信号,请勿在此处连接钱包、签署消息或approve代币权限。已确认的区块链交易无法撤销。
请保留地址、日期、付款或交易详情以及相关信息,以便向警方或其他主管机关报案。 报案并不保证能追回款项。 分步帮助指南:紧急处理指南。
最近检查
27b081a9…5f82940 提供给模型的预处理副本的 SHA-256 哈希值: ff65097c…4d86f8e 27b081a901bcf64c360f15fdd4e6ef3abbefbca862d90cd2c09f11be75f82940 · 135063 bytes 27b081a901bcf64c360f15fdd4e6ef3abbefbca862d90cd2c09f11be75f82940 · 135063 bytes 917967fe4942f5e8a12eb226420b6c00ea9642fe2d114e1efac460d19def1470 · 145542 bytes 9ac37e5114525a4f745ed2316d1ca45be5322a8220f56cb72f93071baaffdf0f · 438659 bytes 188.114.96.3 Cloudflare 共享边缘 源IP已隐藏 Edge-IP 声誉不属于此域。 (DE) 此子域名所属的可注册域名: claimed.work. 对于该 gTLD,上述注册商依据 ICANN 认证协议运营。以下链接提供官方收费标准及现行的 DNS 滥用合规指南。
RAA 第 3.18 条规定了滥用行为联系渠道及处理要求。本报告可记录已存储的外发通知及后续技术观察结果;但报告本身并不构成对收悉、调查、整改或合同违约的认定。
188.114.96.3Francisco, USEdge-IP 声誉不属于此域。
lynn.ns.cloudflare.comwalk.ns.cloudflare.com位置信息描述的是 IP 网络。
1ad2ee07145a85fbbb388708fd2214b6c8bc5015830a1e8d499cddde5c9e8898*.claimed.workclaimed.work已保存的证书元数据。未带时区的证书日期按存档原样显示。传输加密并不能证明该网站值得信任。
最近一次检查时,该网站仍在提供其页面。
Google PageSpeed Insights — 移动端性能审核: fees.claimed.work ·
由本地采集流程保留的带时间戳的响应元数据。以下各项数值均对应所显示的存档时间。
https://fees.claimed.work/Content-Type: text/html; charset=UTF-8Cache-Control: private, max-age=0, no-store, no-cache, must-revalidate, post-check=0, pre-check=0服务器: cloudflareh3=":443"; ma=86400private, max-age=0, no-store, no-cache, must-revalidate, post-check=0, pre-check=0a5da390ad9462103-LHRkeep-alive7249text/html; charset=UTF-8Fri, 20 Nov 2026 20:32:33 GMTThu, 01 Jan 1970 00:00:01 GMTsame-origin120cloudflarecfEdge;dur=19275,cfOrigin;dur=0SAMEORIGIN由采集器保留的数值;较长的值可能在采集时被截短。
估算时间描述的是一个观测时间窗口。它并不能证明注册商采取了措施,也不代表网站变为不可访问的确切时刻。
网络请求: 34 SHA-256 哈希值: 28 URLScan扫描:
URLScan在加载页面时记录的网络请求。URLScan并非为每个请求都提供哈希值。 PhishDestroy 于 2026-11-21 03:30 UTC 检索到了此列表。
在 URLScan 上打开此扫描 01a1fc26-827b-773c-af94-1f0386eabac0 ↗
加载已保存的数据;不会打开该可疑网站。
| # | 网络请求 | HTTP方法 · 状态码 | 类型 | 未压缩大小 | 响应正文的SHA-256哈希值 |
|---|
由监测程序和来源采集器保留的带日期变更记录。最新观测排在最前;来源状态并不能证明站点已被下架。
页面内容呈现
返回的页面内容
页面内容呈现
返回的页面内容
可访问
已记录事件:10。这些记录描述了收集到的证据、外发通知及黑名单发布情况;它们并不意味着调查已完全结束或该网站已被下线。
生命周期
在注册后10天 5小时报告
我们扫描可疑网址,审查公开检测结果,并通过相应的滥用举报渠道提交证据。上方的带日期事件记录了该域名的相关记录。下方的目录说明了更全面的工作流程。
捕获渲染后的页面、请求以及可见的基础设施。
比较各引擎的检测结果,并保留分析时间戳。
检查Google当前是否将该URL列为不安全。
查看公开扫描结果及其记录的网络和分类数据。
查找相关指标参考及相关社区情报。
对比存档的截图并保留历史背景信息。
查找匹配的指标及相关威胁记录。
检查证书记录及相关主机名。
比较安全解析器的响应,并记录观察到的拦截情况。
检查公共DNS、TLS、HTTP及技术暴露面。
用于扫描、信誉检查和报告的安全服务列于下方。某项服务被列出并不意味着该服务已收到、接受或针对该特定域名采取了行动。已记录的提交内容显示在上方通知历史记录中。
 GoogleSafe Browsing↗ GoogleWeb Risk↗
 MicrosoftSmartScreen↗
 VirusTotalURL分析↗
 Cloudflare雷达 / 滥用行为举报↗
 YandexSafe Browsing↗
 URLScan.io公开扫描↗
 ESET示例 / URL 提交↗
 BitdefenderURL提交↗
 NortonSafe Web↗
 Symantec网站评审↗
 AviraURL 报告↗
 Avast / AVGURL 报告↗
 卡巴斯基OpenTIP↗
 Dr.Web在线扫描器↗
 Netcraft滥用行为报告↗
 PhishTank社区举报↗
 APWG eCX网络钓鱼情报↗
 PhishStats公开信息流↗
 Phish.Report主机滥用↗
 Spamhaus域名声誉↗
 PolySwarm多引擎分析↗
 CheckPhishURL 扫描↗
 Quttera恶意软件扫描↗
 URLquery浏览器分析↗
 Criminal IP资产情报↗
 CRDFThreat Center↗
 Scamadviser信誉检查↗
 MyWOT社区声誉↗
按来源浏览该域名的完整历史记录。下载内容包含所选来源的每条记录。日期将保留其原始字段标签。
将所有记录下载为 JSON 格式| ID | 存储的数据 |
|---|
类似标题 辅助信号 1
注册商:PDR 仅限探索 6
每条辐条代表该域名与本报告相关联的一个原因。节点大小表示VirusTotal的检测结果,虚线节点表示已下线,完整列表如下。 相关报告完整列表
通过同一家注册商注册。一家注册商通常为数百万互不相关的客户提供服务,因此这仅表明数据归属同一群体,而非证明存在关联。
最近添加了来自 PhishDestroy 数据库的报告。这些发现链接并不意味着共享基础设施或所有权。
比较浏览器与爬虫各自收到的内容,并检查是否存在 Keitaro 流量分发。
fees.claimed.work PD-08D62C87B5413070B78E 收件人: abuse@publicdomainregistry.com Registrar policy. Per PDR Ltd. d/b/a PublicDomainRegistry.com's published terms: “Explicit policy to immediately suspend domains used for phishing, 419 scams, identity fraud, malware distribution without prior notice” Applicable law. Domestic legal framework (India): IT Act 2000 §§66C–66D (identity theft, cheating by personation), Indian Penal Code §420 / Bharatiya Nyaya Sanhita §318 (fraud).
根据您实际采取的行动采取相应措施。如果输入了密码:请立即更改密码,并检查是否在其他地方重复使用过该密码。如果支付过款项或提供过银行卡信息:请联系您的银行或支付服务商。如果下载了文件:请对设备进行病毒扫描。然后报告该事件。
该草稿仅供您个人保留。
首先确保资金安全:致电您的银行或撤销钱包授权。 当务之急 →
请根据您提供过的信息选择相应的步骤。请将本报告的副本与您自己的记录一并保存。
停止使用可疑网站。请通过官方应用或您已信任的网址访问真正的服务。
请将原始邮件、收据、消息和截图保存在安全的地方。基于事实的时间线有助于受理机构了解事件经过。 IC3 证据指南 ↗
fees.claimed.work)即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。
举报并不能保证追回损失或启动调查,但及时、准确的交易数据可以帮助执法机构和服务提供商追踪事件。
使用存储的阻止列表、WHOIS、DNS 和公共扫描证据进行威胁分析
立即扫描将可疑域名提交至我们的威胁数据库——保护社区
报告最近的网络钓鱼报告和观察到的可用性变化
监控本报告汇总了已保存的页面快照、注册与网络记录、扫描器结果以及 PhishDestroy 举报历史。每个来源均保留各自的观测日期。打开来源报告即可查看原始结果。
AI 辅助分析的撰写时间: . 该内容描述了当时可获得的证据;后续的来源核查可能会导致情况发生变化。
快照记录的是当时显示的内容。扫描器结果记录的是该服务商在检查时的评估。有效证书或零检出结果都不能保证安全。