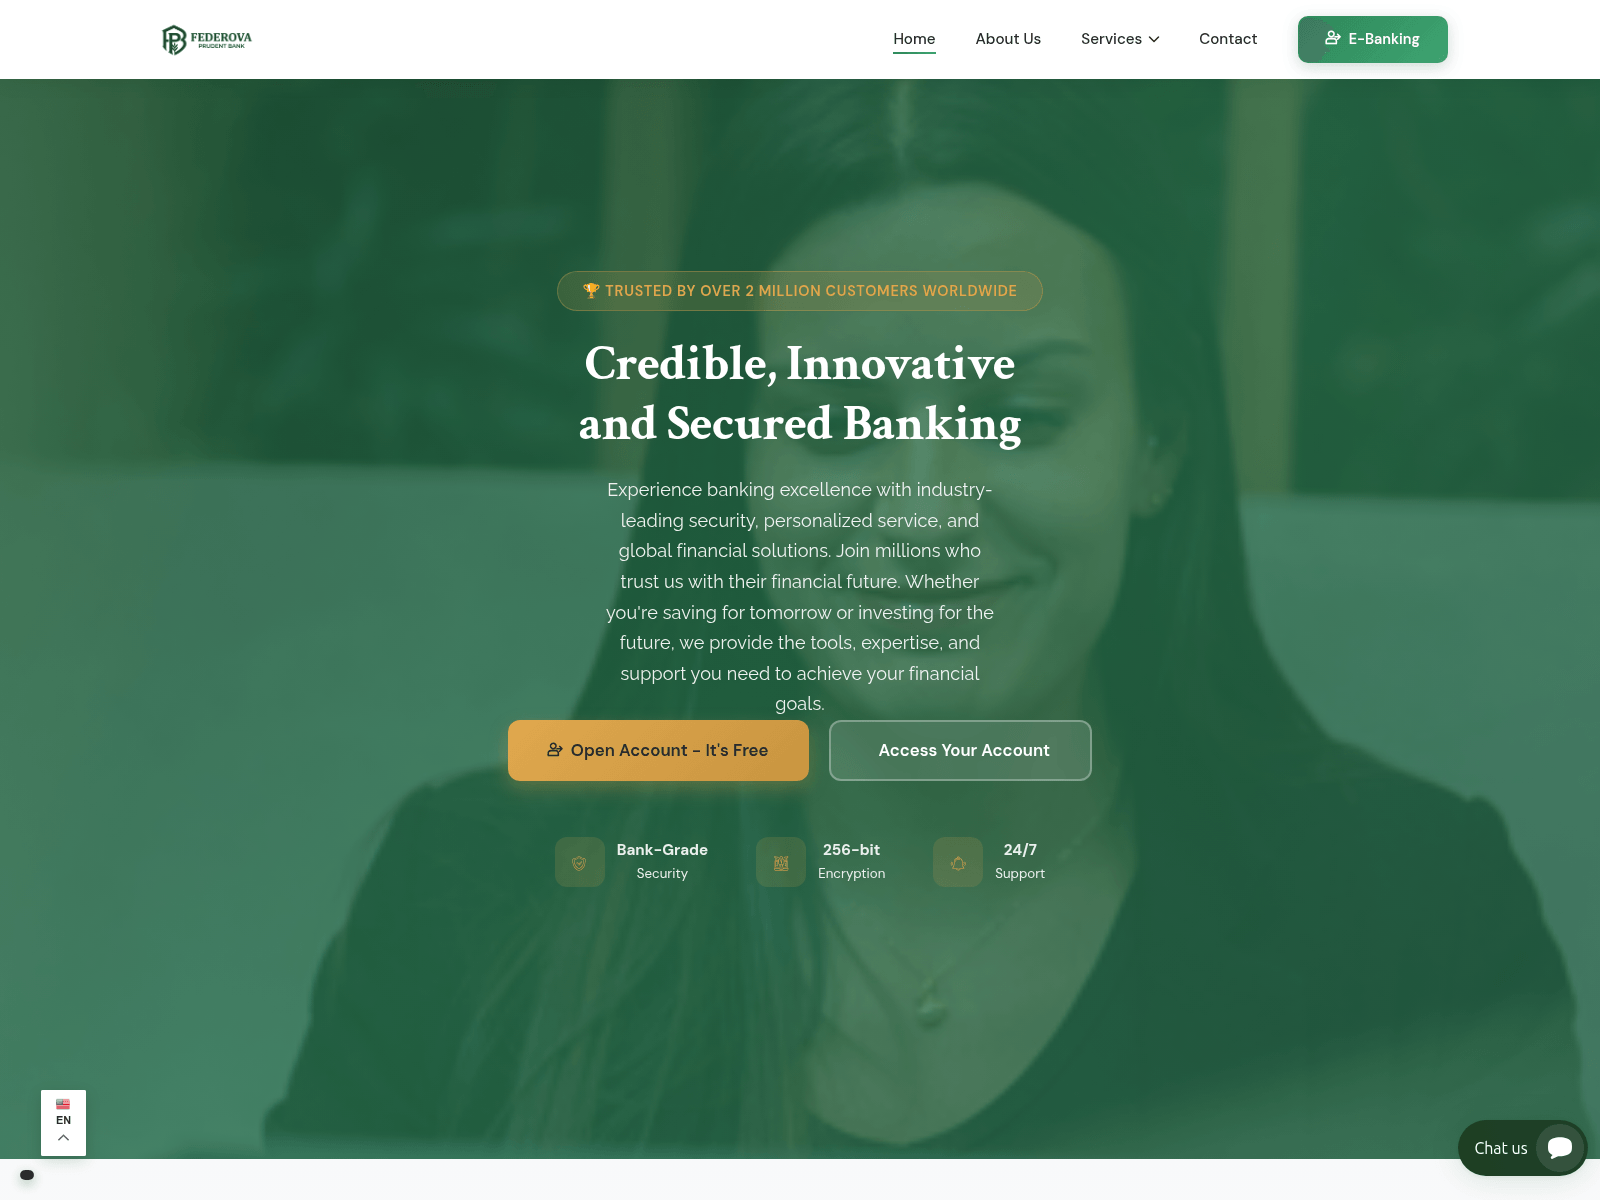
The captured page for federovaprudent.com presents a banking portal operated by an entity identifying as Federova Prudent Bank. The interface displays marketing text emphasizing secure global financial services, alongside prominent interactive controls allowing visitors to open a free account or access an existing one. Additional interface elements highlight bank-grade security and 24/7 customer support.
URLScan截图 · 2026-10-01 23:55 UTC · SHA-256 8ed3e6ab…9ce6aa6
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
The captured page for federovaprudent.com presents a banking portal operated by an entity identifying as Federova Prudent Bank. The interface displays marketing text emphasizing secure global financial services, alongside prominent interactive controls allowing visitors to open a free account or access an existing one. Additional interface elements highlight bank-grade security and 24/7 customer support.
The stored VirusTotal result for the domain reports 7 detections out of 92 security vendors on October 23, 2026. Among the flagging vendors, CRDF and Netcraft classified the target as malicious, while SOCRadar and Forcepoint ThreatSeeker labeled it as phishing, and Gridinsoft identified it as suspicious.
federovaprudent.com - Federova Prudent Bank Landing Page
AI 描述
PhishDestroy analyzes federovaprudent.com, featuring a captured banking landing page promoting online financial services and account access.
AI摘要
The captured page for federovaprudent.com presents a banking portal operated by an entity identifying as Federova Prudent Bank. The interface displays marketing text emphasizing secure global financial services, alongside prominent interactive controls allowing visitors to open a free account or access an existing one. Additional interface elements highlight bank-grade security and 24/7 customer support. The stored VirusTotal result for the domain reports 7 detections out of 92 security vendors on October 23, 2026. Among the flagging vendors, CRDF and Netcraft classified the target as malicious, while SOCRadar and Forcepoint ThreatSeeker labeled it as phishing, and Gridinsoft identified it as suspicious.


 86.107.77.205


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT