Tóm tắt nguồn được ghi lại
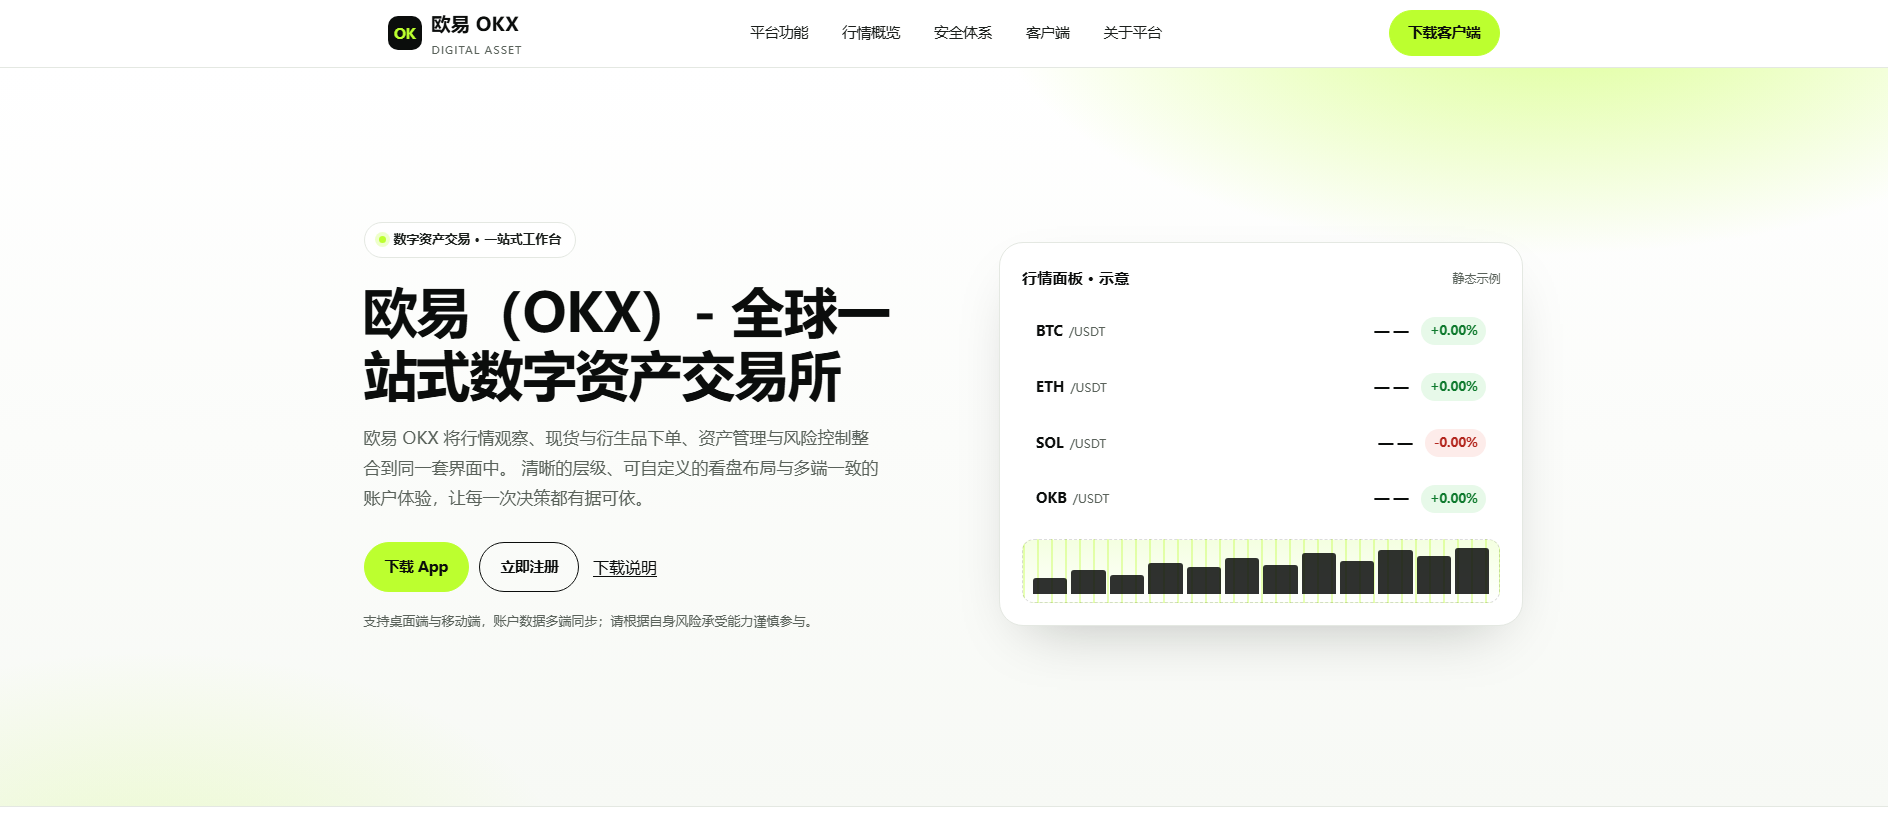
PhishDestroy first observed tempo-okx.com.cn on Nov 22, 2026. The hostname explicitly references OKX; stored content metadata identifies the same apparent target. The captured page title is “欧易(OKX)- 全球一站式数字资产交易所”. Current evidence score: 90/100 (critical).
Positive findings are stored from 5 sources: VirusTotal, MetaMask, SEAL, Google Safe Browsing, and URLScan. VirusTotal recorded 1 detections among 92 engines: Fortinet on Nov 22, 2026 at 01:44 UTC. MetaMask and SEAL listed the hostname in the separate external-blocklist snapshot on Nov 22, 2026 at 15:20 UTC. Google Safe Browsing flagged the domain: Social Engineering on Nov 22, 2026 at 16:04 UTC. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to okx and assigned phishing as its category on Nov 22, 2026 at 15:30 UTC.
HTTP 301 was recorded on Nov 22, 2026 at 15:31 UTC. Registration records for the domain list Dynadot Inc as the registrar and Nov 21, 2026 as the creation date. Registration preceded first observation by 1 day. At collection time, the hostname resolved to 172.67.132.157. The IP and ASN identify shared Cloudflare edge infrastructure; the origin server is not established by this address. The evidence archive retains 3 visual captures from PhishDestroy, URLScan, and Cloudflare Radar. TLS metadata lists Let's Encrypt / YE2 as the certificate issuer with validity through Feb 19, 2027.
The content indicators and 5 positive source findings support the current OKX impersonation and phishing classification. The target field identifies OKX.


 Dynadot


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT