전문가용 보기에는 DNS, TLS, 네트워크 요청, 해시, 원시 JSON 등 모든 섹션이 포함되어 있습니다.
ABUSE NOTICE · 7D+ OPEN 발송된 악용 신고는 기록되며, 저장된 최신 가용성 증거에 따르면 해당 도메인은 여전히 접속 가능한 상태입니다.
통지 및 현재 상황 관련 증거
전송된 보고서 원장에는 첫 번째 발신 보고서가 . 기록된 수신자: abuse@name.com. 가장 최근에 저장된 가용성 정보에 따르면 해당 도메인은 여전히 접속 가능한 것으로 나타납니다.; 29 days 첫 번째 발신 보고서 이후로 시간이 지났습니다.
ICANN RAA §3.18 등록기관의 악용 신고 연락처 및 처리 의무를 설명합니다. 이 섹션에는 발신 타임스탬프, 수신자 목록, 사건 식별자 및 추후 확인 가능 여부가 기록됩니다. 이 정보만으로는 수신, 확인, 조사, 시정 조치 또는 계약 불이행을 입증할 수 없습니다.
첫 보고 이후 경과한 기간
29 days
발송된 신고
1
최신 사례 ID
PD-20261024-DF179E
현재 현황
HTTP 403 가장 최근에 저장된 검사 결과
보고서 요약
PhishDestroy에 uspspayment.org 기록이 저장되어 있습니다. 각 출처의 관측 날짜는 다르며, 검사가 없다는 사실은 안전을 의미하지 않습니다.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
분석
도메인 요약
PhishDestroy는 2026-10-24에 uspspayment.org를 처음 기록했습니다. 저장된 VirusTotal 결과: 16/92 엔진에서 경고했습니다. 악성: 15. 의심: 1. 분석 시간(저장된 표기): 2026-10-23 04:09 UTC. 조회 시간(저장된 표기): 2026-10-24 15:10 UTC. 위험도: 심각 (증거 점수 100/100). 등록 대행자: Name.com. 상태: 연결 가능 · 액세스가 제한됨. 호스팅: Amazon.com, Inc. PhishDestroy는 악용 신고 1건을 보냈습니다. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Overview
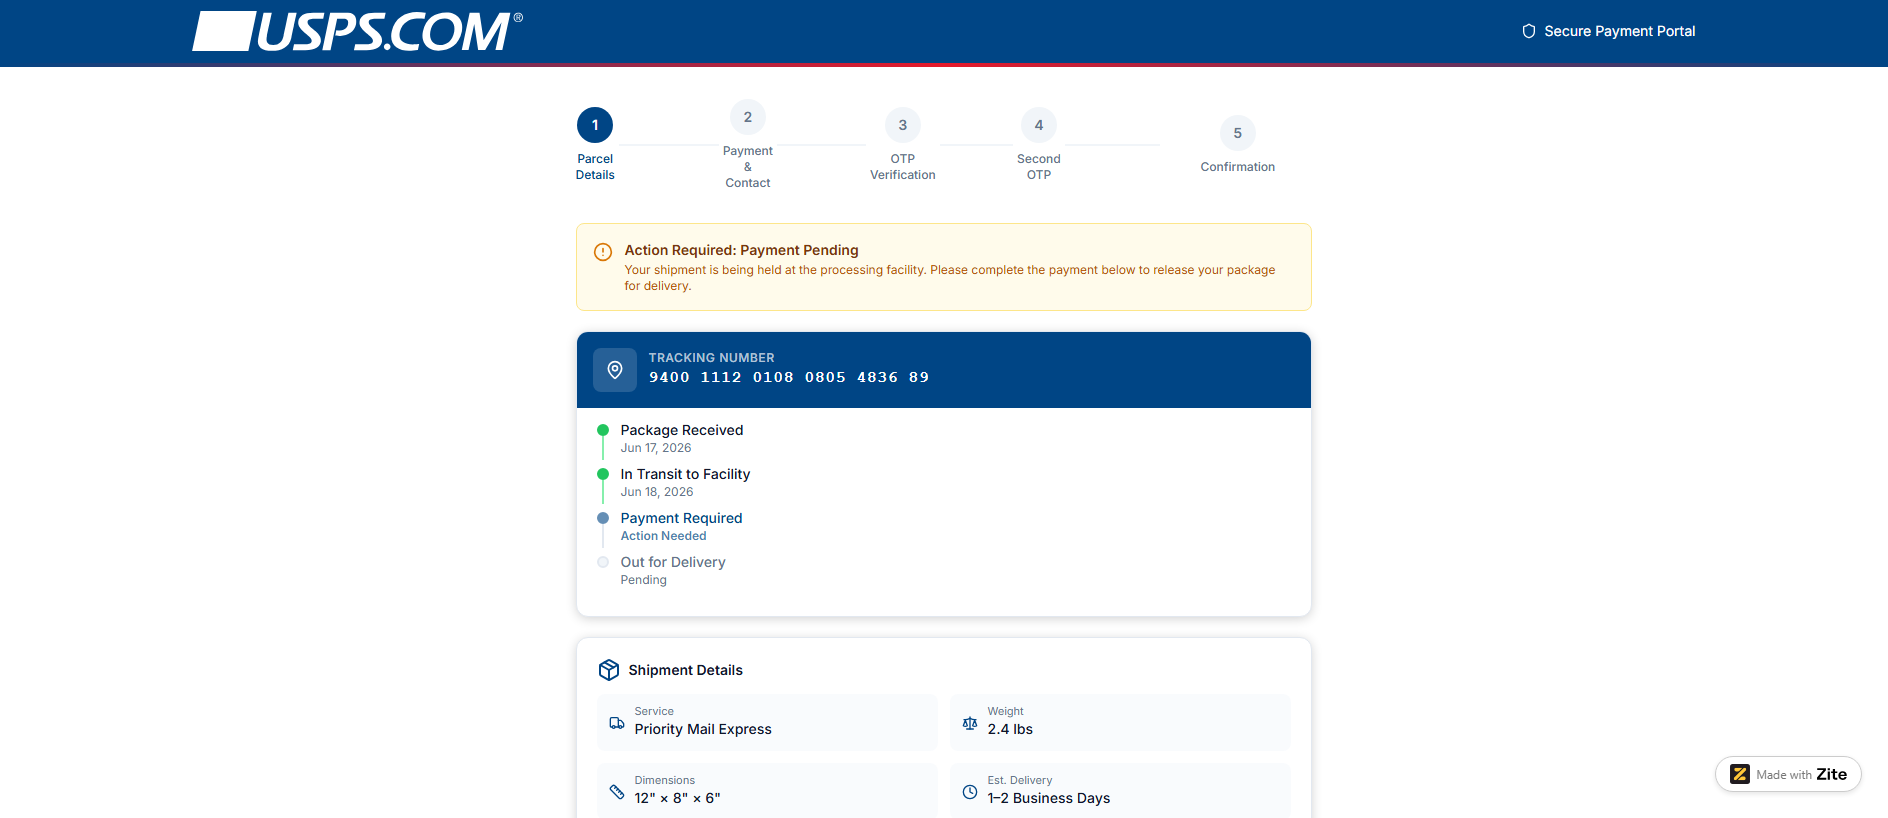
The captured screenshot shows a Secure Payment Portal header bearing the USPS wordmark and a five-step flow from Parcel Details through Confirmation. It warned of Action Required Payment Pending and displayed a tracking timeline, shipment details and a payment summary totaling $36.08. PhishDestroy listed it as an impersonation phishing page on 2026-10-24, its first-seen date.
사기 수법
The page presented a held-package notice urging payment to release a shipment, then collected payment and contact details before requesting an OTP and a second OTP. This payment-portal impersonation captures card details and one-time codes entered under time pressure. As a category risk, victims are steered into paying a fabricated postal fee.
증거
The screenshot shows a USPS-branded payment portal with a pending-shipment alert, a tracking timeline and a total due of $36.08; urlscan scored the capture malicious at 98 on 2026-10-24 under a phishing label, an earlier urlscan verdict on 2026-10-19 was clean, and Google Safe Browsing was not flagged on 2026-10-25. VirusTotal flagged the domain as malicious, with ESET labelling it phishing. Spamhaus returned no listing, external blocklists counted 0, and OTX recorded 0 pulses on 2026-10-24, while PhishDestroy internal blocklisting is recorded and a single-hop redirect chain with no cross-site redirect was observed. The capture made 14 requests, loaded Google Fonts, Google Static and Wikimedia trackers plus a Zite app runtime whose minified globals showed no unambiguous framework, and recorded 1 distinct script SHA256 hash for pivoting beginning 48fb0d76e762.
인프라
Notable weaknesses: no Content-Security-Policy, no HSTS, and absent X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP headers; DNSSEC unsigned; no SPF, DKIM or DMARC recorded. TLS 1.3 with AES-128-GCM, forward secrecy and ALPN h2; CAA records present. Registration was on 2026-06-19 through the Name.com registrar, and the capture recorded hosting on the AMAZON-02 network behind a Cloudflare WAF.
What to do
If you submitted payment card details, contact your card issuer about the charge and monitor statements for unauthorized activity; if you entered an account password, change it on the genuine USPS account and enable two-factor authentication. Avoid replying to or opening further messages that lead to this domain. Defenders should block uspspayment.org at DNS and proxy layers, hunt on the recorded script hash, and submit an impersonation takedown request.
PhishDestroy assesses uspspayment.org as an impersonation phishing page posing as a USPS package payment portal.
AI 요약
Overview The captured screenshot shows a Secure Payment Portal header bearing the USPS wordmark and a five-step flow from Parcel Details through Confirmation. It warned of Action Required Payment Pending and displayed a tracking timeline, shipment details and a payment summary totaling $36.08. PhishDestroy listed it as an impersonation phishing page on 2026-10-24, its first-seen date. How the scam works The page presented a held-package notice urging payment to release a shipment, then collected payment and contact details before requesting an OTP and a second OTP. This payment-portal impersonation captures card details and one-time codes entered under time pressure. As a category risk, victims are steered into paying a fabricated postal fee. Evidence The screenshot shows a USPS-branded payment portal with a pending-shipment alert, a tracking timeline and a total due of $36.08; urlscan scored the capture malicious at 98 on 2026-10-24 under a phishing label, an earlier urlscan verdict on 2026-10-19 was clean, and Google Safe Browsing was not flagged on 2026-10-25. VirusTotal flagged the domain as malicious, with ESET labelling it phishing. Spamhaus returned no listing, external blocklists counted 0, and OTX recorded 0 pulses on 2026-10-24, while PhishDestroy internal blocklisting is recorded and a single-hop redirect chain with no cross-site redirect was observed. The capture made 14 requests, loaded Google Fonts, Google Static and Wikimedia trackers plus a Zite app runtime whose minified globals showed no unambiguous framework, and recorded 1 distinct script SHA256 hash for pivoting beginning 48fb0d76e762. Infrastructure Notable weaknesses: no Content-Security-Policy, no HSTS, and absent X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP headers; DNSSEC unsigned; no SPF, DKIM or DMARC recorded. TLS 1.3 with AES-128-GCM, forward secrecy and ALPN h2; CAA records present. Registration was on 2026-06-19 through the Name.com registrar, and the capture recorded hosting on the AMAZON-02 network behind a Cloudflare WAF. What to do If you submitted payment card details, contact your card issuer about the charge and monitor statements for unauthorized activity; if you entered an account password, change it on the genuine USPS account and enable two-factor authentication. Avoid replying to or opening further messages that lead to this domain. Defenders should block uspspayment.org at DNS and proxy layers, hunt on the recorded script hash, and submit an impersonation takedown request. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a16e76-4f27-7498-8f0f-298bbd461fa7/ Cloudflare Radar report: https://radar.cloudflare.com/scan/ff2c5f0b-f90f-4367-b985-01746ea525dd URLQuery report: https://urlquery.net/report/fb33996a-7821-4baf-86b1-64d152d5e1b2 Stored capture screenshot: https://i.ibb.co/cBS5C6S/b3976eaba876.png Cloudflare Radar screenshot (2026-10-24T15:11:11Z): https://screenshots.phishdestroy.io/cf/ff2c5f0b-f90f-4367-b985-01746ea525dd.png URLScan screenshot (2026-08-18T13:46:21Z): https://screenshots.phishdestroy.io/us/01a0151f-6951-77fc-bae8-356c6984d617.png URLScan capture report: https://urlscan.io/result/01a0151f-6951-77fc-bae8-356c6984d617/ URLScan screenshot (2026-08-18T20:57:26Z): https://screenshots.phishdestroy.io/us/01a016aa-0caa-736f-8a11-1bb188c65983.png URLScan capture report: https://urlscan.io/result/01a016aa-0caa-736f-8a11-1bb188c65983/ URLScan screenshot (2026-09-05T07:13:23Z): https://screenshots.phishdestroy.io/us/01a0706a-139e-711a-8cef-cee8503e799c.png URLScan capture report: https://urlscan.io/result/01a0706a-139e-711a-8cef-cee8503e799c/ URLScan screenshot (2026-09-05T17:19:46Z): https://screenshots.phishdestroy.io/us/01a07295-3968-7408-adfe-09a41d0ec465.png URLScan capture report: https://urlscan.io/result/01a07295-3968-7408-adfe-09a41d0ec465/ URLScan screenshot (2026-10-24T15:07:20Z): https://screenshots.phishdestroy.io/us/01a16e73-9f38-707e-86c7-3aad23c8a392.png URLScan capture report: https://urlscan.io/result/01a16e73-9f38-707e-86c7-3aad23c8a392/ URLScan screenshot (2026-10-24T15:15:39Z): https://screenshots.phishdestroy.io/us/01a16e7a-cc25-7408-a72e-7f74c570d6b4.png URLScan capture report: https://urlscan.io/result/01a16e7a-cc25-7408-a72e-7f74c570d6b4/ VirusTotal report: https://www.virustotal.com/gui/domain/uspspayment.org Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=uspspayment.org Archived copy: https://web.archive.org/web/20261024150719/https://uspspayment.org/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Title: USPS (United States Postal Service); Ogtype: website; Ogimage: https://images.fillout.com/orgid-736675/flowpublicid-1mnkhwabxs/widgetid-default/cv7i3arfZJvL6PXmRUHFoa/united-states-postal-service-usps-logo-1.png; Ogtitle: USPS (United States Postal Service); Ogsitename: USPS (United States Postal Service); Themecolor: #ffffff; Description: USPS (United States Postal Service); Ogdescription: USPS (United States Postal Service)
The website's owner is hiding his identity on WHOIS using a paid service This website does not have many visitors This website has only been registered recently. IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
This website offers payment methods which allow you to get your money back According to the SSL check the certificate is valid DNSFilter considers this website safe
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
피싱 Security threats 피싱
uspspayment.org 관련 질문
uspspayment.org은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 uspspayment.org를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-10-24에 처음 기록되었습니다. 저장된 VirusTotal 결과: 16/92 엔진에서 경고했습니다. 악성: 15. 의심: 1. 분석 시간(저장된 표기): 2026-10-23 04:09 UTC. 조회 시간(저장된 표기): 2026-10-24 15:10 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
uspspayment.org에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
uspspayment.org을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
1차 평가 변수접근 가능하지만 보호됨reason: HTTP access restricted65% confidence
출처Cloudflaremechanism: Access Restrictionsource: Current Http Probe
증거 레이어Availability: Reachable but protectedDNS: Resolved
최신 HTTP 관측 결과접근 가능하지만 보호됨HTTP access restrictedCloudflareAccess Restriction65%2026-11-22 11:20 UTC
RDAP 등록
관측된 시간축last reachable: 2026-11-22 11:20 UTClast content: 2026-10-29 23:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
등록된 하위 도메인1
도메인 레코드 또는 인증서 투명성(Certificate Transparency) 캐시에 저장된 호스트 이름. 호스트 이름만으로는 현재 가용성이나 악의적인 활동을 판단할 수 없습니다.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.


 Name.com
 34.214.61.222


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT