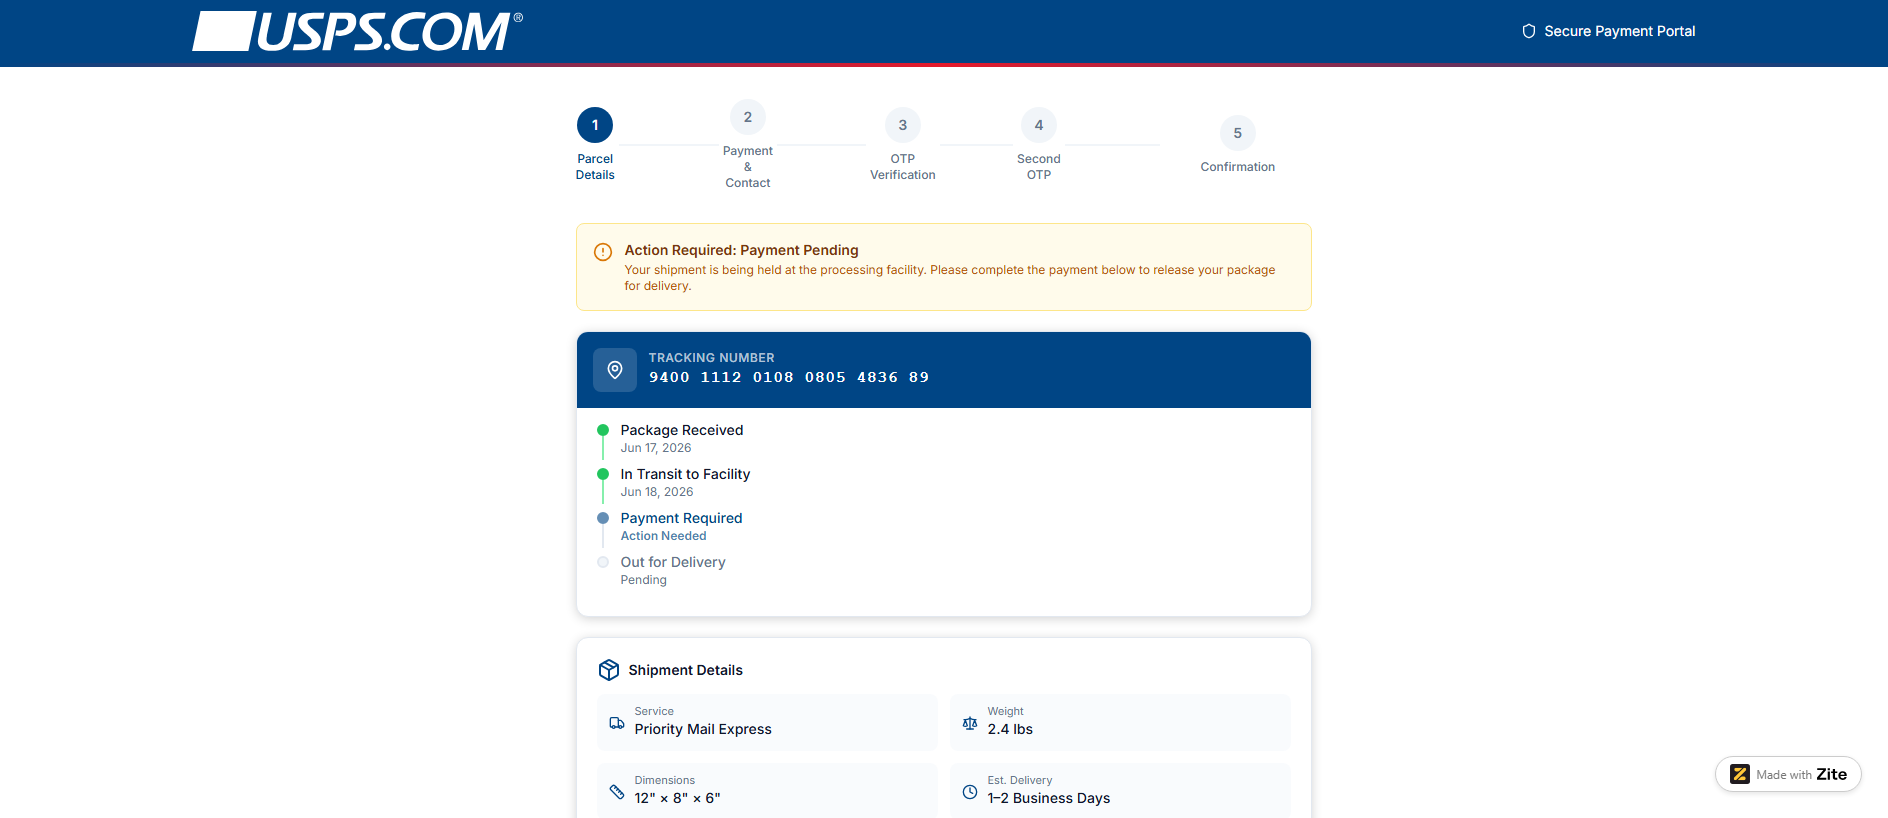
The captured screenshot shows a Secure Payment Portal header bearing the USPS wordmark and a five-step flow from Parcel Details through Confirmation. It warned of Action Required Payment Pending and displayed a tracking timeline, shipment details and a payment summary totaling $36.08. PhishDestroy listed it as an impersonation phishing page on 2026-10-24, its first-seen date.
诈骗手法解析
The page presented a held-package notice urging payment to release a shipment, then collected payment and contact details before requesting an OTP and a second OTP. This payment-portal impersonation captures card details and one-time codes entered under time pressure. As a category risk, victims are steered into paying a fabricated postal fee.
证据
The screenshot shows a USPS-branded payment portal with a pending-shipment alert, a tracking timeline and a total due of $36.08; urlscan scored the capture malicious at 98 on 2026-10-24 under a phishing label, an earlier urlscan verdict on 2026-10-19 was clean, and Google Safe Browsing was not flagged on 2026-10-25. VirusTotal flagged the domain as malicious, with ESET labelling it phishing. Spamhaus returned no listing, external blocklists counted 0, and OTX recorded 0 pulses on 2026-10-24, while PhishDestroy internal blocklisting is recorded and a single-hop redirect chain with no cross-site redirect was observed. The capture made 14 requests, loaded Google Fonts, Google Static and Wikimedia trackers plus a Zite app runtime whose minified globals showed no unambiguous framework, and recorded 1 distinct script SHA256 hash for pivoting beginning 48fb0d76e762.
基础设施
Notable weaknesses: no Content-Security-Policy, no HSTS, and absent X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP headers; DNSSEC unsigned; no SPF, DKIM or DMARC recorded. TLS 1.3 with AES-128-GCM, forward secrecy and ALPN h2; CAA records present. Registration was on 2026-06-19 through the Name.com registrar, and the capture recorded hosting on the AMAZON-02 network behind a Cloudflare WAF.
What to do
If you submitted payment card details, contact your card issuer about the charge and monitor statements for unauthorized activity; if you entered an account password, change it on the genuine USPS account and enable two-factor authentication. Avoid replying to or opening further messages that lead to this domain. Defenders should block uspspayment.org at DNS and proxy layers, hunt on the recorded script hash, and submit an impersonation takedown request.
PhishDestroy assesses uspspayment.org as an impersonation phishing page posing as a USPS package payment portal.
AI摘要
Overview The captured screenshot shows a Secure Payment Portal header bearing the USPS wordmark and a five-step flow from Parcel Details through Confirmation. It warned of Action Required Payment Pending and displayed a tracking timeline, shipment details and a payment summary totaling $36.08. PhishDestroy listed it as an impersonation phishing page on 2026-10-24, its first-seen date. How the scam works The page presented a held-package notice urging payment to release a shipment, then collected payment and contact details before requesting an OTP and a second OTP. This payment-portal impersonation captures card details and one-time codes entered under time pressure. As a category risk, victims are steered into paying a fabricated postal fee. Evidence The screenshot shows a USPS-branded payment portal with a pending-shipment alert, a tracking timeline and a total due of $36.08; urlscan scored the capture malicious at 98 on 2026-10-24 under a phishing label, an earlier urlscan verdict on 2026-10-19 was clean, and Google Safe Browsing was not flagged on 2026-10-25. VirusTotal flagged the domain as malicious, with ESET labelling it phishing. Spamhaus returned no listing, external blocklists counted 0, and OTX recorded 0 pulses on 2026-10-24, while PhishDestroy internal blocklisting is recorded and a single-hop redirect chain with no cross-site redirect was observed. The capture made 14 requests, loaded Google Fonts, Google Static and Wikimedia trackers plus a Zite app runtime whose minified globals showed no unambiguous framework, and recorded 1 distinct script SHA256 hash for pivoting beginning 48fb0d76e762. Infrastructure Notable weaknesses: no Content-Security-Policy, no HSTS, and absent X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP headers; DNSSEC unsigned; no SPF, DKIM or DMARC recorded. TLS 1.3 with AES-128-GCM, forward secrecy and ALPN h2; CAA records present. Registration was on 2026-06-19 through the Name.com registrar, and the capture recorded hosting on the AMAZON-02 network behind a Cloudflare WAF. What to do If you submitted payment card details, contact your card issuer about the charge and monitor statements for unauthorized activity; if you entered an account password, change it on the genuine USPS account and enable two-factor authentication. Avoid replying to or opening further messages that lead to this domain. Defenders should block uspspayment.org at DNS and proxy layers, hunt on the recorded script hash, and submit an impersonation takedown request. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a16e76-4f27-7498-8f0f-298bbd461fa7/ Cloudflare Radar report: https://radar.cloudflare.com/scan/ff2c5f0b-f90f-4367-b985-01746ea525dd URLQuery report: https://urlquery.net/report/fb33996a-7821-4baf-86b1-64d152d5e1b2 Stored capture screenshot: https://i.ibb.co/cBS5C6S/b3976eaba876.png Cloudflare Radar screenshot (2026-10-24T15:11:11Z): https://screenshots.phishdestroy.io/cf/ff2c5f0b-f90f-4367-b985-01746ea525dd.png URLScan screenshot (2026-08-18T13:46:21Z): https://screenshots.phishdestroy.io/us/01a0151f-6951-77fc-bae8-356c6984d617.png URLScan capture report: https://urlscan.io/result/01a0151f-6951-77fc-bae8-356c6984d617/ URLScan screenshot (2026-08-18T20:57:26Z): https://screenshots.phishdestroy.io/us/01a016aa-0caa-736f-8a11-1bb188c65983.png URLScan capture report: https://urlscan.io/result/01a016aa-0caa-736f-8a11-1bb188c65983/ URLScan screenshot (2026-09-05T07:13:23Z): https://screenshots.phishdestroy.io/us/01a0706a-139e-711a-8cef-cee8503e799c.png URLScan capture report: https://urlscan.io/result/01a0706a-139e-711a-8cef-cee8503e799c/ URLScan screenshot (2026-09-05T17:19:46Z): https://screenshots.phishdestroy.io/us/01a07295-3968-7408-adfe-09a41d0ec465.png URLScan capture report: https://urlscan.io/result/01a07295-3968-7408-adfe-09a41d0ec465/ URLScan screenshot (2026-10-24T15:07:20Z): https://screenshots.phishdestroy.io/us/01a16e73-9f38-707e-86c7-3aad23c8a392.png URLScan capture report: https://urlscan.io/result/01a16e73-9f38-707e-86c7-3aad23c8a392/ URLScan screenshot (2026-10-24T15:15:39Z): https://screenshots.phishdestroy.io/us/01a16e7a-cc25-7408-a72e-7f74c570d6b4.png URLScan capture report: https://urlscan.io/result/01a16e7a-cc25-7408-a72e-7f74c570d6b4/ VirusTotal report: https://www.virustotal.com/gui/domain/uspspayment.org Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=uspspayment.org Archived copy: https://web.archive.org/web/20261024150719/https://uspspayment.org/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Title: USPS (United States Postal Service); Ogtype: website; Ogimage: https://images.fillout.com/orgid-736675/flowpublicid-1mnkhwabxs/widgetid-default/cv7i3arfZJvL6PXmRUHFoa/united-states-postal-service-usps-logo-1.png; Ogtitle: USPS (United States Postal Service); Ogsitename: USPS (United States Postal Service); Themecolor: #ffffff; Description: USPS (United States Postal Service); Ogdescription: USPS (United States Postal Service)
The website's owner is hiding his identity on WHOIS using a paid service This website does not have many visitors This website has only been registered recently. IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
This website offers payment methods which allow you to get your money back According to the SSL check the certificate is valid DNSFilter considers this website safe
来源Cloudflaremechanism: Access Restrictionsource: Current Http Probe
证据层Availability: Reachable but protectedDNS: Resolved
最新的 HTTP 观察结果可接触但受保护HTTP access restrictedCloudflareAccess Restriction65%2026-11-22 11:20 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:20 UTClast content: 2026-10-29 23:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 Name.com
 34.214.61.222


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT