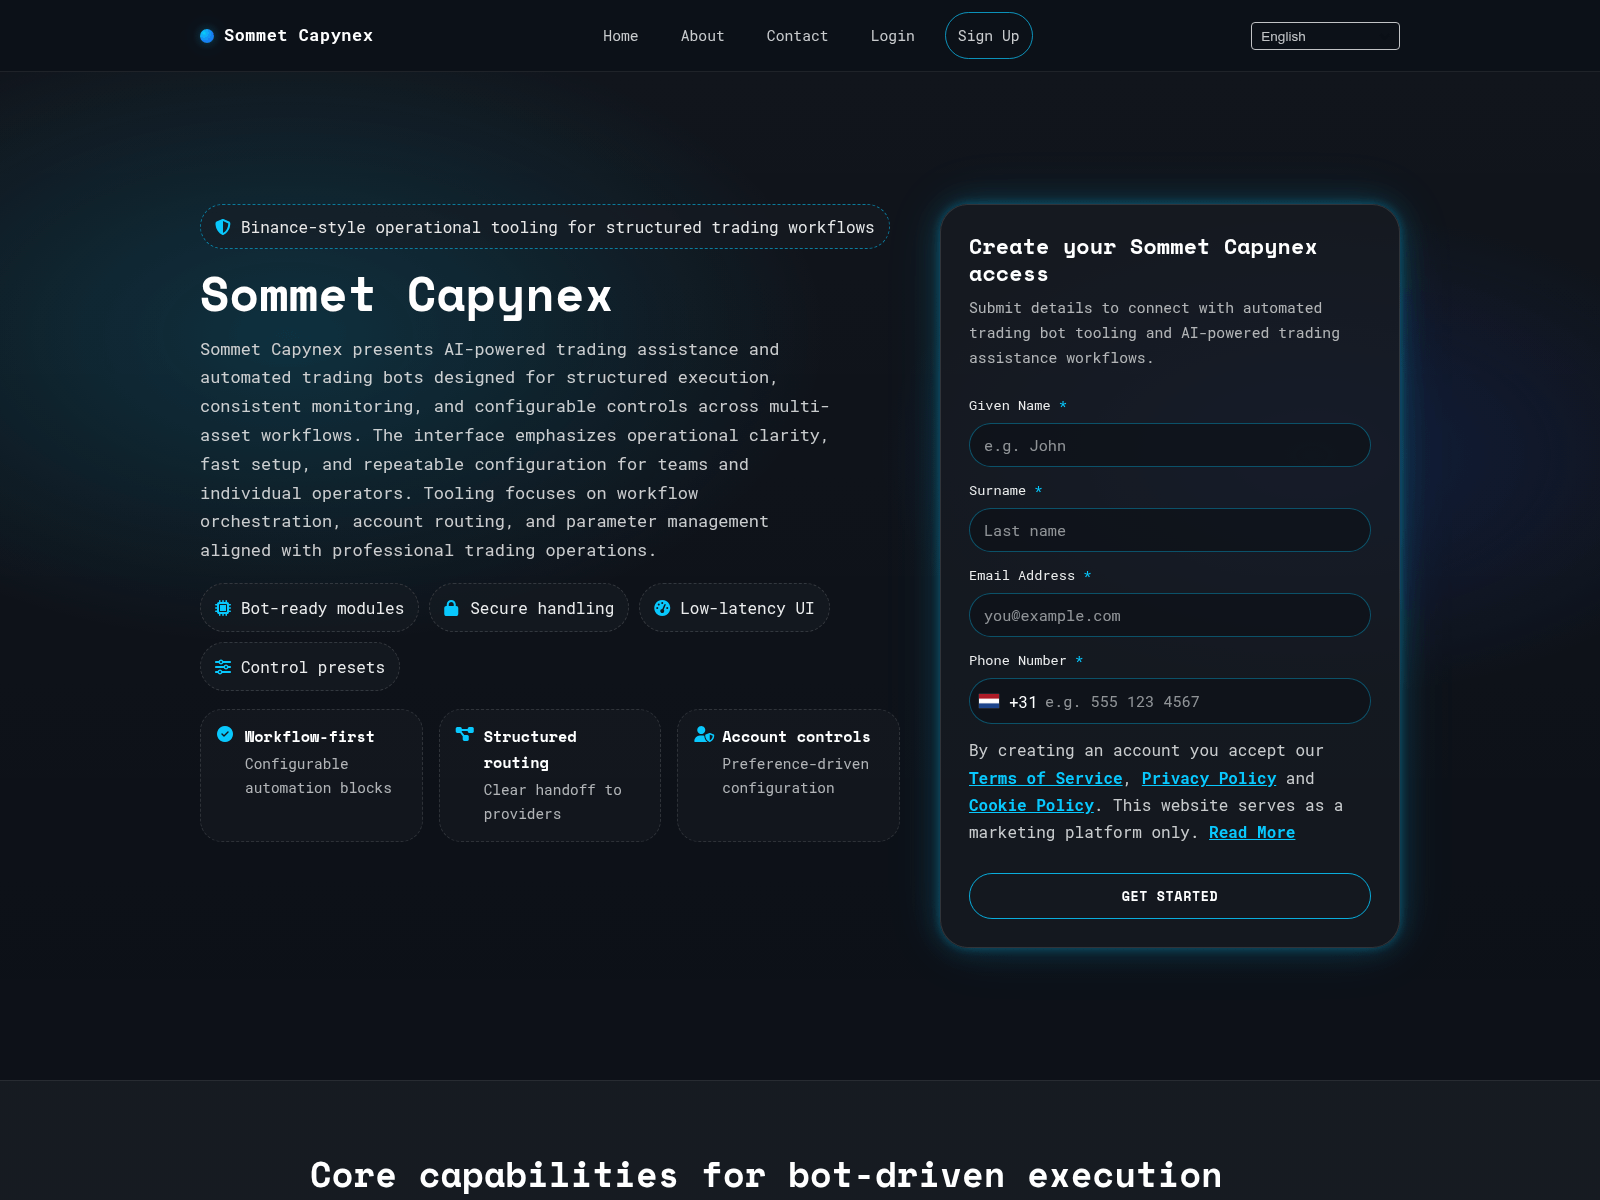
The sommetcapynex-engine.com page shows a dark-themed landing page branded "Sommet Capynex," labeled as Binance-style operational tooling for structured trading workflows. The main text states that Sommet Capynex presents AI-powered trading assistance and automated trading bots designed for structured execution, consistent monitoring, and configurable controls across multi-asset workflows, with feature labels such as bot-ready modules, secure handling, low-latency UI, and control presets. A sign-up panel titled "Create your Sommet Capynex access" asks for given name, surname, email address, and phone number, with a "Get Started" button and links to Terms of Service, Privacy Policy, and Cookie Policy.
분석 내용은 영어로만 제공됩니다.
페이지 제목: “Sommet Capynex | AI Trading Automation & Bot Controls”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 18/92 엔진에서 경고했습니다. 악성: 15. 의심: 3. 분석 시간(저장된 표기): 2026-11-01 23:45 UTC. 조회 시간(저장된 표기): 2026-11-05 00:06 UTC. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
URLScan 캡처 · 2026-07-22 11:01 UTC · SHA-256 6b009c10…807b88a
PhishDestroy 분석, 검토 완료된 버전
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
The sommetcapynex-engine.com page shows a dark-themed landing page branded "Sommet Capynex," labeled as Binance-style operational tooling for structured trading workflows. The main text states that Sommet Capynex presents AI-powered trading assistance and automated trading bots designed for structured execution, consistent monitoring, and configurable controls across multi-asset workflows, with feature labels such as bot-ready modules, secure handling, low-latency UI, and control presets. A sign-up panel titled "Create your Sommet Capynex access" asks for given name, surname, email address, and phone number, with a "Get Started" button and links to Terms of Service, Privacy Policy, and Cookie Policy.
The stored VirusTotal domain result reports 18 detections out of 92 engines. DNS8 reported "suspicious"; ESET reported "suspicious".
PhishDestroy records sommetcapynex-engine.com as a page presenting Sommet Capynex AI-powered trading assistance and a sign-up form to create access.
AI 요약
The sommetcapynex-engine.com page shows a dark-themed landing page branded "Sommet Capynex," labeled as Binance-style operational tooling for structured trading workflows. The main text states that Sommet Capynex presents AI-powered trading assistance and automated trading bots designed for structured execution, consistent monitoring, and configurable controls across multi-asset workflows, with feature labels such as bot-ready modules, secure handling, low-latency UI, and control presets. A sign-up panel titled "Create your Sommet Capynex access" asks for given name, surname, email address, and phone number, with a "Get Started" button and links to Terms of Service, Privacy Policy, and Cookie Policy. The stored VirusTotal domain result reports 18 detections out of 92 engines. DNS8 reported "suspicious"; ESET reported "suspicious".
결과는 각 출처의 수집 시점을 기준으로 합니다. 탐지 0건이 안전을 보장하지는 않습니다. OTX 참조는 커뮤니티 게시물입니다.
수집된 출처 세부 정보
저장된 페이지, 네트워크, 스캐너 관측 결과를 출처와 관측 시각별로 묶어 보여 줍니다.
저장된 모든 필드와 출처·날짜
웹사이트 점검출처의 원본 기록검색됨: 24개 필드
메일 설정
SPF 조회 수
0
DNS 보호 기능 결과
확인한 리졸버 수
12
차단한 곳
CloudFlare Family
차단한 리졸버 수
1
크롤러 규칙
사용자 에이전트
*
있음
예
사이트맵
있음
예
URL 수
203
페이지 제목 및 메타데이터
Open Graph URL
https://sommetcapynex-engine.com/
페이지 제목
Sommet Capynex | AI Trading Automation & Bot Controls
Open Graph 유형
website
색인 지시어
index, follow
Open Graph 제목
Sommet Capynex | AI Trading Automation & Bot Controls
Open Graph 사이트 이름
Sommet Capynex
테마 색상
#0d1118
설명
Sommet Capynex presents professional automation for trading workflows, including AI-powered trading assistance, bot controls, and operational tools for...
Twitter 카드
summary
표준 URL
https://sommetcapynex-engine.com/
Open Graph 설명
Sommet Capynex presents professional automation for trading workflows, including AI-powered trading assistance, bot controls, and operational tools for structured execution.
According to Tranco this site has a low rank High number of suspicious websites on this server This website is (very) young. This website has been marked as threat by DNSFilter in the last 30 days This website has been reported for Phishing by IPQS This website has been reported as Suspicious by IPQS
The SSL certificate is valid
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
Malware Malware Security threats
sommetcapynex-engine.com 관련 질문
sommetcapynex-engine.com은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 sommetcapynex-engine.com를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-11-04에 처음 기록되었습니다. 저장된 VirusTotal 결과: 18/92 엔진에서 경고했습니다. 악성: 15. 의심: 3. 분석 시간(저장된 표기): 2026-11-01 23:45 UTC. 조회 시간(저장된 표기): 2026-11-05 00:06 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
sommetcapynex-engine.com에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
sommetcapynex-engine.com을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
IP 평판185.62.57.140/100악용 점수 · 이 서버의 IP 주소에 대한 악용 신고 건수이며, 도메인에 대한 신고 건수가 아닙니다. 점수가 높을수록 상황이 더 심각합니다.이 IP 주소는 아직 악용 데이터베이스에 신고되지 않았으나, 도메인 자체는 피싱으로 인식되고 있습니다.신고 0건확인됨 2026-11-04
1차 평가 변수활성 콘텐츠reason: Ordinary HTTP content served90% confidence
출처source: Current Http Probe
증거 레이어Availability: Content servingContent: Content served at rootDNS: Resolved
최신 HTTP 관측 결과활성 콘텐츠일반 HTTP 콘텐츠 제공90%2026-11-22 11:28 UTC
RDAP 등록
관측된 시간축last reachable: 2026-11-22 11:28 UTClast content: 2026-11-22 11:28 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
등록된 하위 도메인1
도메인 레코드 또는 인증서 투명성(Certificate Transparency) 캐시에 저장된 호스트 이름. 호스트 이름만으로는 현재 가용성이나 악의적인 활동을 판단할 수 없습니다.
로컬 수집 파이프라인이 보관한 타임스탬프 포함 응답 메타데이터입니다. 아래의 각 값은 표시된 아카이브 시각을 기준으로 합니다.
보관된 HTTP 응답HTTP 200
요청된 URL:http://sommetcapynex-engine.com/
최종 URL:https://sommetcapynex-engine.com/
Sommet Capynex | AI Trading Automation & Bot Controls
Sommet Capynex presents professional automation for trading workflows, including AI-powered trading assistance, bot controls, and operational tools for...
Open Graph 제목:Sommet Capynex | AI Trading Automation & Bot Controls
Open Graph 설명:Sommet Capynex presents professional automation for trading workflows, including AI-powered trading assistance, bot controls, and operational tools for structured execution.
Twitter 카드:summary
Saved response-header values · 9
Alt-Svc
h3=":443"; ma=2592000
Content-Encoding
gzip
Content-Type
text/html; charset=utf-8
날짜
Wed, 04 Nov 2026 20:40:07 GMT
Etag
"dm9jimqk8w5nqap-gzip"
Last-Modified
Tue, 20 Oct 2026 08:58:56 GMT
Referrer-Policy
no-referrer-when-downgrade
Transfer-Encoding
chunked
Vary
Accept-Encoding
수집기가 보관한 값입니다. 긴 값은 수집 과정에서 축약될 수 있습니다.
등록 및 참관 안내3
가용성 관측값
마지막 접속 가능 관측
마지막 콘텐츠 관측
추정 기준
현재 접속 가능
추정 시각은 관측 구간을 나타냅니다. 레지스트라의 조치나 사이트가 접속 불가 상태가 된 정확한 시점을 입증하지는 않습니다.
기록된 이벤트: 12. 이 기록들은 수집된 증거, 발송된 알림 및 차단 목록 등재를 설명하며, 조사가 완료되었거나 해당 사이트가 차단되었음을 확인하는 것은 아닙니다.
선제적 탐지 및 데이터 수집위협 데이터 수집 완료기록됨
위협 데이터 수집 완료
sommetcapynex-engine.com이 탐지되어 전체 분석을 위해 대기열에 추가됨
위협 인텔리전스 확인URLScan.io 캡처 · URLScan 판정 결과 · Cloudflare Radar 보고서 · 웹 아카이브 · VirusTotal · OTX 커뮤니티 참조 자료 · Cloudflare Radar: 악성 · 자동 브랜드 라벨: Binance · 수집된 포렌식 증거 · 기록된 기술 분석기록됨
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.