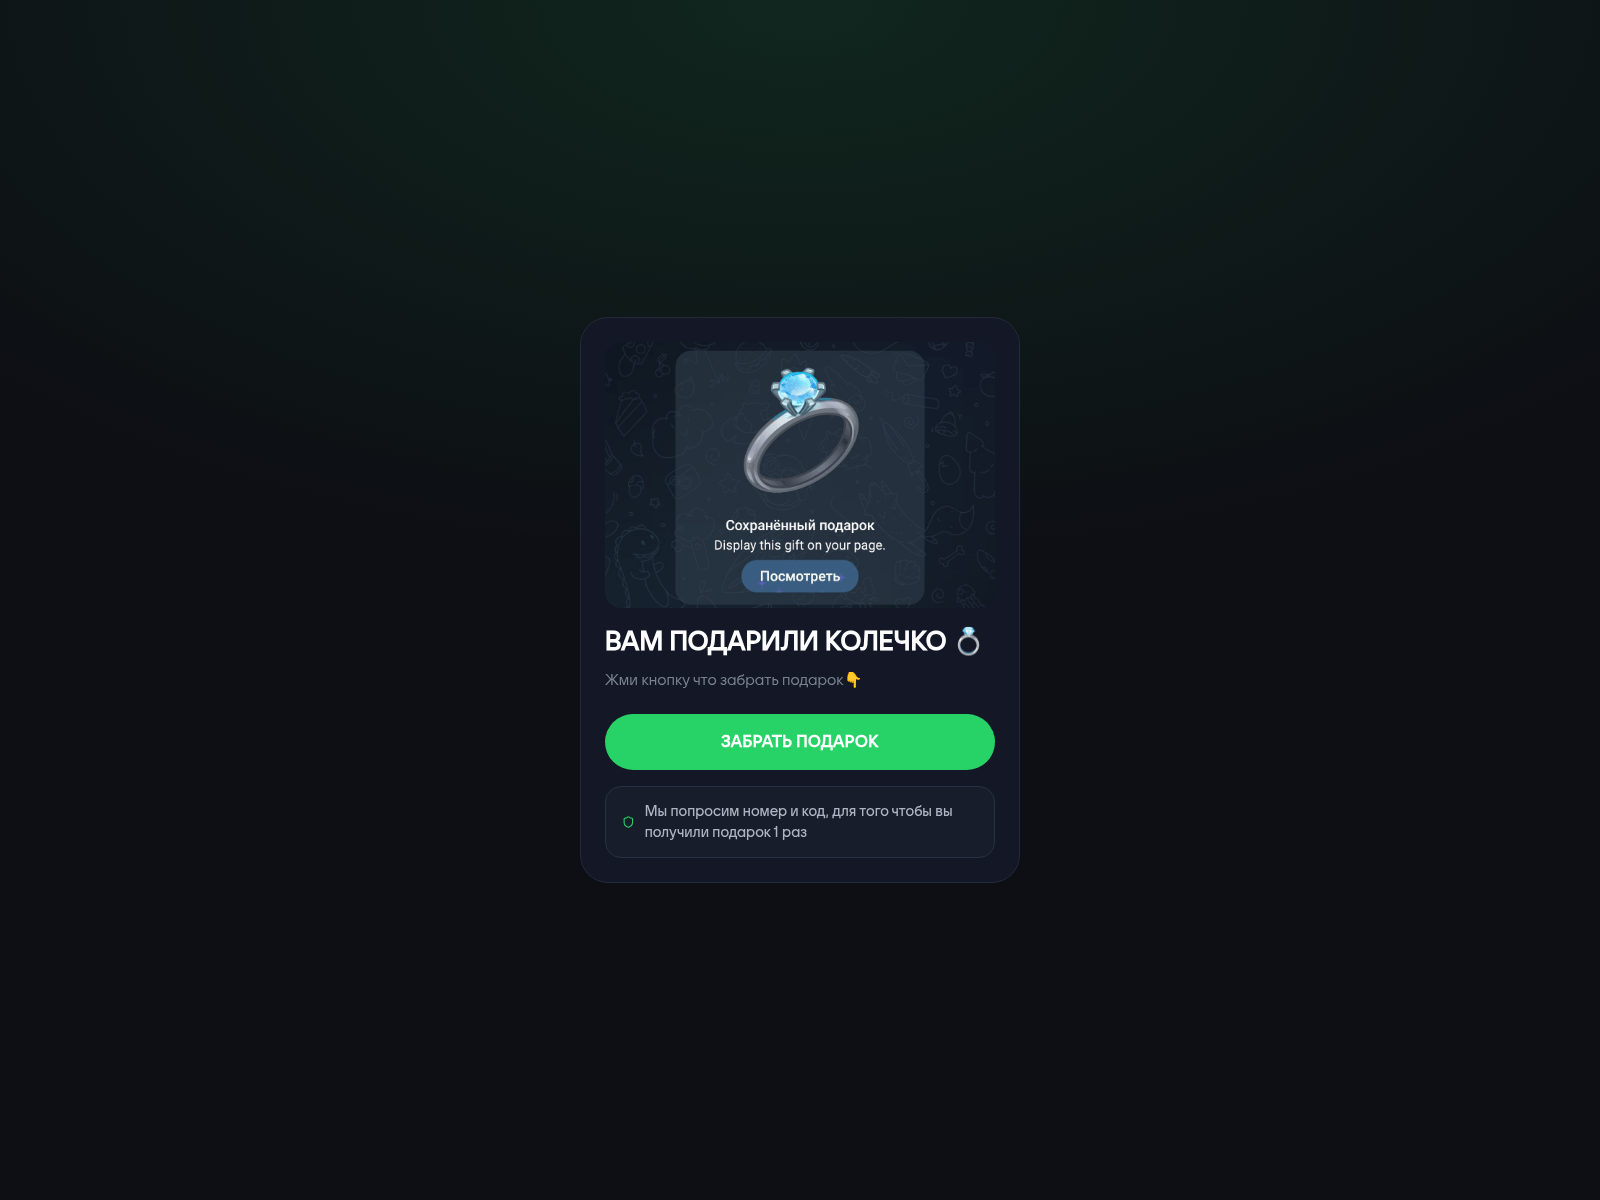
rullsmax.net presents a Russian-language gift claim page featuring a ring graphic and prompting visitors for a phone number and verification code. Visitors who encountered this page should avoid entering personal phone numbers or codes.
분석 내용은 영어로만 제공됩니다.
페이지 제목: “ВАМ ПОДАРИЛИ КОЛЕЧКО 💍”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 1/92 엔진에서 경고했습니다. 악성: 0. 의심: 1. 분석 시간(저장된 표기): 2026-11-19 22:50 UTC. 조회 시간(저장된 표기): 2026-11-20 09:15 UTC. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
전문가용 보기에는 DNS, TLS, 네트워크 요청, 해시, 원시 JSON 등 모든 섹션이 포함되어 있습니다.
ABUSE NOTICE · 24H+ OPEN 발송된 악용 신고는 기록되며, 저장된 최신 가용성 증거에 따르면 해당 도메인은 여전히 접속 가능한 상태입니다.
통지 및 현재 상황 관련 증거
전송된 보고서 원장에는 첫 번째 발신 보고서가 . 기록된 수신자: abuse@ordertld.com. 가장 최근에 저장된 가용성 정보에 따르면 해당 도메인은 여전히 접속 가능한 것으로 나타납니다.; 2 days 첫 번째 발신 보고서 이후로 시간이 지났습니다.
ICANN RAA §3.18 등록기관의 악용 신고 연락처 및 처리 의무를 설명합니다. 이 섹션에는 발신 타임스탬프, 수신자 목록, 사건 식별자 및 추후 확인 가능 여부가 기록됩니다. 이 정보만으로는 수신, 확인, 조사, 시정 조치 또는 계약 불이행을 입증할 수 없습니다.
첫 보고 이후 경과한 기간
2 days
발송된 신고
1
최신 사례 ID
PD-0B2B00358158082B54D7
현재 현황
가장 최근에 저장된 검사 시점에서 활성 상태로 관측됨
보고서 요약
PhishDestroy에 rullsmax.net 기록이 저장되어 있습니다. 각 출처의 관측 날짜는 다르며, 검사가 없다는 사실은 안전을 의미하지 않습니다.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
분석
도메인 요약
PhishDestroy는 2026-11-20에 rullsmax.net를 처음 기록했습니다. 저장된 VirusTotal 결과: 1/92 엔진에서 경고했습니다. 악성: 0. 의심: 1. 분석 시간(저장된 표기): 2026-11-19 22:50 UTC. 조회 시간(저장된 표기): 2026-11-20 09:15 UTC. 위험도: 높음 (증거 점수 60/100). 등록 대행자: CNOBIN INFORMATION TEC…. 호스팅: Cloudflare, Inc. PhishDestroy는 악용 신고 1건을 보냈습니다. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
URLScan 캡처 · 2026-11-20 09:11 UTC · SHA-256 11efaa03…80b6755
PhishDestroy 분석, 검토 완료된 버전
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Gift claim interface on rullsmax.net
The page displayed on rullsmax.net is presented entirely in Russian against a dark background with subtle icons. At the center, a card shows a ring illustration above the headline "BAM ПОДАРИЛИ КОЛЕЧКО" and smaller text reading "Жми кнопку что забрать подарок". A prominent green button labeled "ЗАБРАТЬ ПОДАРОК" sits below, accompanied by a smaller box stating "Мы попросим номер и код, для того чтобы вы получили подарок 1 раз". Above the main graphic, a smaller preview box includes the text "Сохранённый подарок" and "Display this gift on your page" with a blue button saying "Посмотреть". The interface is designed to ask for contact information under the guise of delivering a virtual gift.
Registration timeline and independent findings
It was registered on 19 Nov 2026 and reported the same day, and 1 of 92 VirusTotal engines flagged it on 19 Nov 2026. These factors show the domain was spun up rapidly, matching patterns often seen with short-lived collection pages rather than established platforms.
Risks and where phone verification claims lead
Pages requesting phone numbers and verification codes typically use free virtual gifts as a lure to hijack accounts or subscribe visitors to unrequested services. Because the interface prompts for codes under the banner "Мы попросим номер и код", entering details can lead directly to unauthorized access attempts or unwanted service sign-ups. Visitors who already submitted their phone number and code should immediately check their active account sessions, revoke access from unrecognized devices, and monitor their phone carrier accounts for unauthorized subscriptions.
서술 생성 날짜는 관측 날짜와 별개입니다. 이는 보존된 게시 필드일 뿐, 별도의 독립적인 탐지 결과가 아닙니다.
AI 제목
rullsmax.net — Russian gift claim page with a ring graphic
AI 설명
rullsmax.net displays a virtual gift claim page requesting phone numbers, flagged by 1 VirusTotal engine, and users should avoid submitting personal details.
AI 요약
Gift claim interface on rullsmax.net The page displayed on rullsmax.net is presented entirely in Russian against a dark background with subtle icons. At the center, a card shows a ring illustration above the headline "BAM ПОДАРИЛИ КОЛЕЧКО" and smaller text reading "Жми кнопку что забрать подарок". A prominent green button labeled "ЗАБРАТЬ ПОДАРОК" sits below, accompanied by a smaller box stating "Мы попросим номер и код, для того чтобы вы получили подарок 1 раз". Above the main graphic, a smaller preview box includes the text "Сохранённый подарок" and "Display this gift on your page" with a blue button saying "Посмотреть". The interface is designed to ask for contact information under the guise of delivering a virtual gift. Registration timeline and independent findings It was registered on 19 Nov 2026 and reported the same day, and 1 of 92 VirusTotal engines flagged it on 19 Nov 2026. These factors show the domain was spun up rapidly, matching patterns often seen with short-lived collection pages rather than established platforms. Risks and where phone verification claims lead Pages requesting phone numbers and verification codes typically use free virtual gifts as a lure to hijack accounts or subscribe visitors to unrequested services. Because the interface prompts for codes under the banner "Мы попросим номер и код", entering details can lead directly to unauthorized access attempts or unwanted service sign-ups. Visitors who already submitted their phone number and code should immediately check their active account sessions, revoke access from unrecognized devices, and monitor their phone carrier accounts for unauthorized subscriptions.
PhishDestroy는 기록된 증거를 바탕으로 rullsmax.net를 높음 위험 등급(증거 점수 60/100)으로 평가했으며, 이는 2026-11-20에 처음 기록되었습니다. 저장된 VirusTotal 결과: 1/92 엔진에서 경고했습니다. 악성: 0. 의심: 1. 분석 시간(저장된 표기): 2026-11-19 22:50 UTC. 조회 시간(저장된 표기): 2026-11-20 09:15 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
rullsmax.net에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
rullsmax.net을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
Registrar policy. Per Cnobin Information Technology Limited's published terms: ““Domains used for phishing, online fraud, malware and illegal activity are strictly prohibited; registrar may lock, suspend or cancel abusive domains.””
Applicable law. Domestic legal framework (China): PRC Criminal Law Art.286; PRC Cybersecurity Law; MIIT regulations.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.

 CNOBIN INFORMATION TEC…
 172.67.201.68


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT