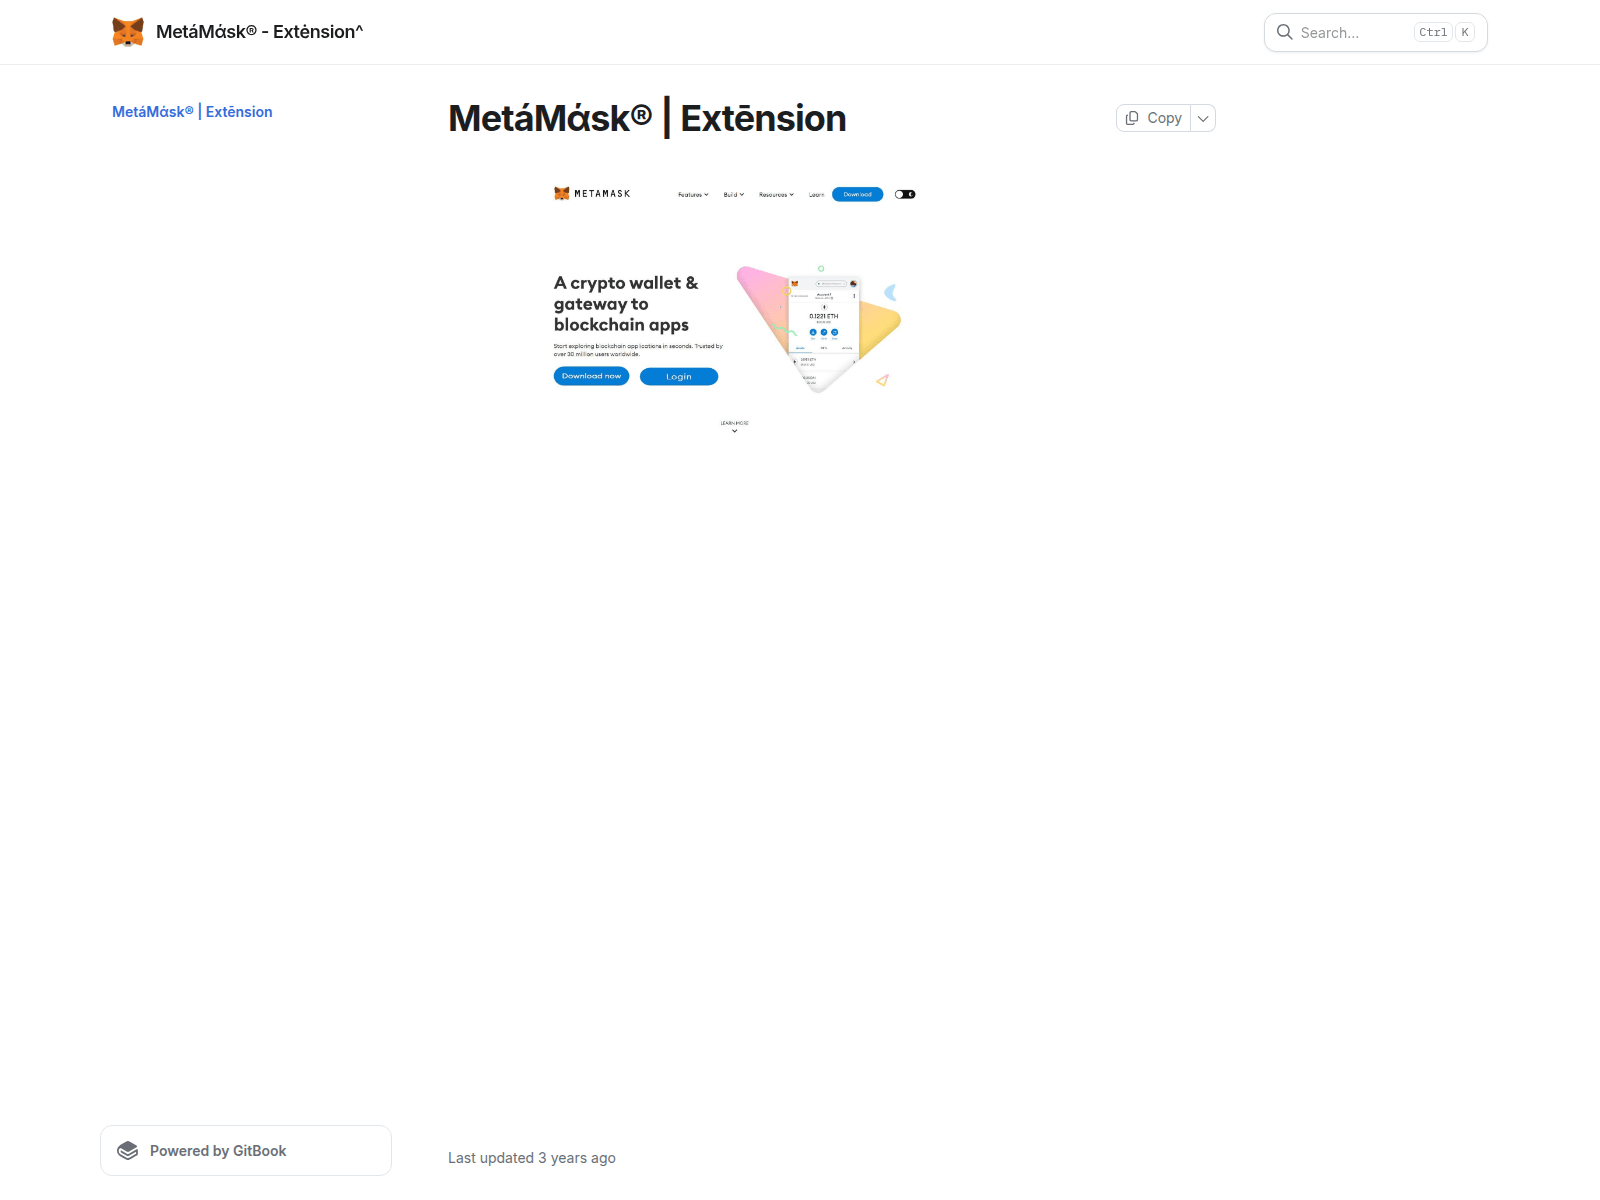
The memetamskextin.gitbook.io page mimics MetaMask documentation to trick visitors into interacting with fraudulent links. If you visited this page, close the tab immediately and do not download any files or connect your crypto wallet.
분석 내용은 영어로만 제공됩니다.
페이지 제목: “MetáMάsk® | Extēnsion | MetáMάsk® - Extėnsion^”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 18/92 엔진에서 경고했습니다. 악성: 17. 의심: 1. 분석 시간(저장된 표기): 2026-11-17 11:02 UTC. 조회 시간(저장된 표기): 2026-11-18 09:50 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
전문가용 보기에는 DNS, TLS, 네트워크 요청, 해시, 원시 JSON 등 모든 섹션이 포함되어 있습니다.
보고서 요약
PhishDestroy에 memetamskextin.gitbook.io 기록이 저장되어 있습니다. 각 출처의 관측 날짜는 다르며, 검사가 없다는 사실은 안전을 의미하지 않습니다.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
분석
도메인 요약
PhishDestroy는 2026-11-18에 memetamskextin.gitbook.io를 처음 기록했습니다. 저장된 VirusTotal 결과: 18/92 엔진에서 경고했습니다. 악성: 17. 의심: 1. 분석 시간(저장된 표기): 2026-11-17 11:02 UTC. 조회 시간(저장된 표기): 2026-11-18 09:50 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 위험도: 심각 (증거 점수 100/100). 등록 대행자: Cloudflare. 상태: 마지막으로 확인된 활성 상태. 호스팅: Cloudflare, Inc. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
URLScan 캡처 · 2026-11-18 01:06 UTC · SHA-256 d55abbbd…e29fc97
PhishDestroy 분석, 검토 완료된 버전
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Page layout and design
The page hosted on memetamskextin.gitbook.io uses GitBook to present itself as official MetaMask documentation. The header features the MetaMask fox logo alongside stylized text reading "MetáMásk® | Extênsion". Below this heading, the page embeds a screenshot of an interface showing promotional text such as "A crypto wallet & gateway to blockchain apps" and "Trusted by over 30 million users worldwide". Two primary buttons labelled "Download now" and "Login" sit beside an illustration of a mobile wallet interface. At the very bottom, a small badge indicates the site is "Powered by GitBook" alongside a timestamp noting it was last updated years ago.
Security detections and verification
urlscan classified the page as malicious, 18 of 92 VirusTotal engines flagged it on 17 Nov 2026, and MetaMask, OpenPhish and SEAL block it, confirming that independent tools flag the site. Furthermore, PhishDestroy's evidence score for it is 85/100 (critical), reflecting the severe risk posed to visitors. Security vendors and threat intelligence feeds recognize this GitBook space as a deceptive setup designed to mimic official brand resources.
Recommended actions
Visitors should verify they are navigating to the official website at metamask.io rather than interacting with third-party documentation hosting providers. Anyone who has interacted with links on memetamskextin.gitbook.io should immediately disconnect their wallet sessions, revoke any pending smart contract approvals, and report the fraudulent URL to the hosting provider.
memetamskextin.gitbook.io hosted a deceptive MetaMask manual, flagged by urlscan and 18 VirusTotal engines. Do not input sensitive data or download software.
AI 요약
Page layout and design The page hosted on memetamskextin.gitbook.io uses GitBook to present itself as official MetaMask documentation. The header features the MetaMask fox logo alongside stylized text reading "MetáMásk® | Extênsion". Below this heading, the page embeds a screenshot of an interface showing promotional text such as "A crypto wallet & gateway to blockchain apps" and "Trusted by over 30 million users worldwide". Two primary buttons labelled "Download now" and "Login" sit beside an illustration of a mobile wallet interface. At the very bottom, a small badge indicates the site is "Powered by GitBook" alongside a timestamp noting it was last updated years ago. Security detections and verification urlscan classified the page as malicious, 18 of 92 VirusTotal engines flagged it on 17 Nov 2026, and MetaMask, OpenPhish and SEAL block it, confirming that independent tools flag the site. Furthermore, PhishDestroy's evidence score for it is 85/100 (critical), reflecting the severe risk posed to visitors. Security vendors and threat intelligence feeds recognize this GitBook space as a deceptive setup designed to mimic official brand resources. Recommended actions Visitors should verify they are navigating to the official website at metamask.io rather than interacting with third-party documentation hosting providers. Anyone who has interacted with links on memetamskextin.gitbook.io should immediately disconnect their wallet sessions, revoke any pending smart contract approvals, and report the fraudulent URL to the hosting provider.
The owner of the website is using a service to hide their identity on WHOIS According to Tranco this site has a low rank This site is a website within another website This website has been reported for Phishing by IPQS This website has been reported as Suspicious by IPQS
The SSL certificate is valid The domain name has been registered for more than one year in advance This website is (very) old This website is safe according to DNSFilter
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
피싱 피싱 Security threats
memetamskextin.gitbook.io 관련 질문
memetamskextin.gitbook.io은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 memetamskextin.gitbook.io를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-11-18에 처음 기록되었습니다. 저장된 VirusTotal 결과: 18/92 엔진에서 경고했습니다. 악성: 17. 의심: 1. 분석 시간(저장된 표기): 2026-11-17 11:02 UTC. 조회 시간(저장된 표기): 2026-11-18 09:50 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
memetamskextin.gitbook.io에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
memetamskextin.gitbook.io을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
1차 평가 변수Redirectingreason: HTTP redirect observed80% confidence
출처source: Current Http Probe
증거 레이어Availability: RedirectingDNS: Resolved
최신 HTTP 관측 결과RedirectingHTTP redirect observed80%2026-11-21 11:15 UTC
RDAP 등록
관측된 시간축last reachable: 2026-11-21 11:15 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
위협 인텔리전스 교차 확인 · source references
ScamAdviser공개 조회
한 대중 ScamAdviser 조회 기능이 제공됩니다. 해당 출처에서 현재 점수와 경고 사항을 확인하십시오. 조회 페이지가 존재한다고 해서 그 자체로 악성 판정을 의미하는 것은 아닙니다.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.


 Cloudflare
 104.18.40.47


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT