도메인 보안 및 위협 인텔리전스

koipay.digital
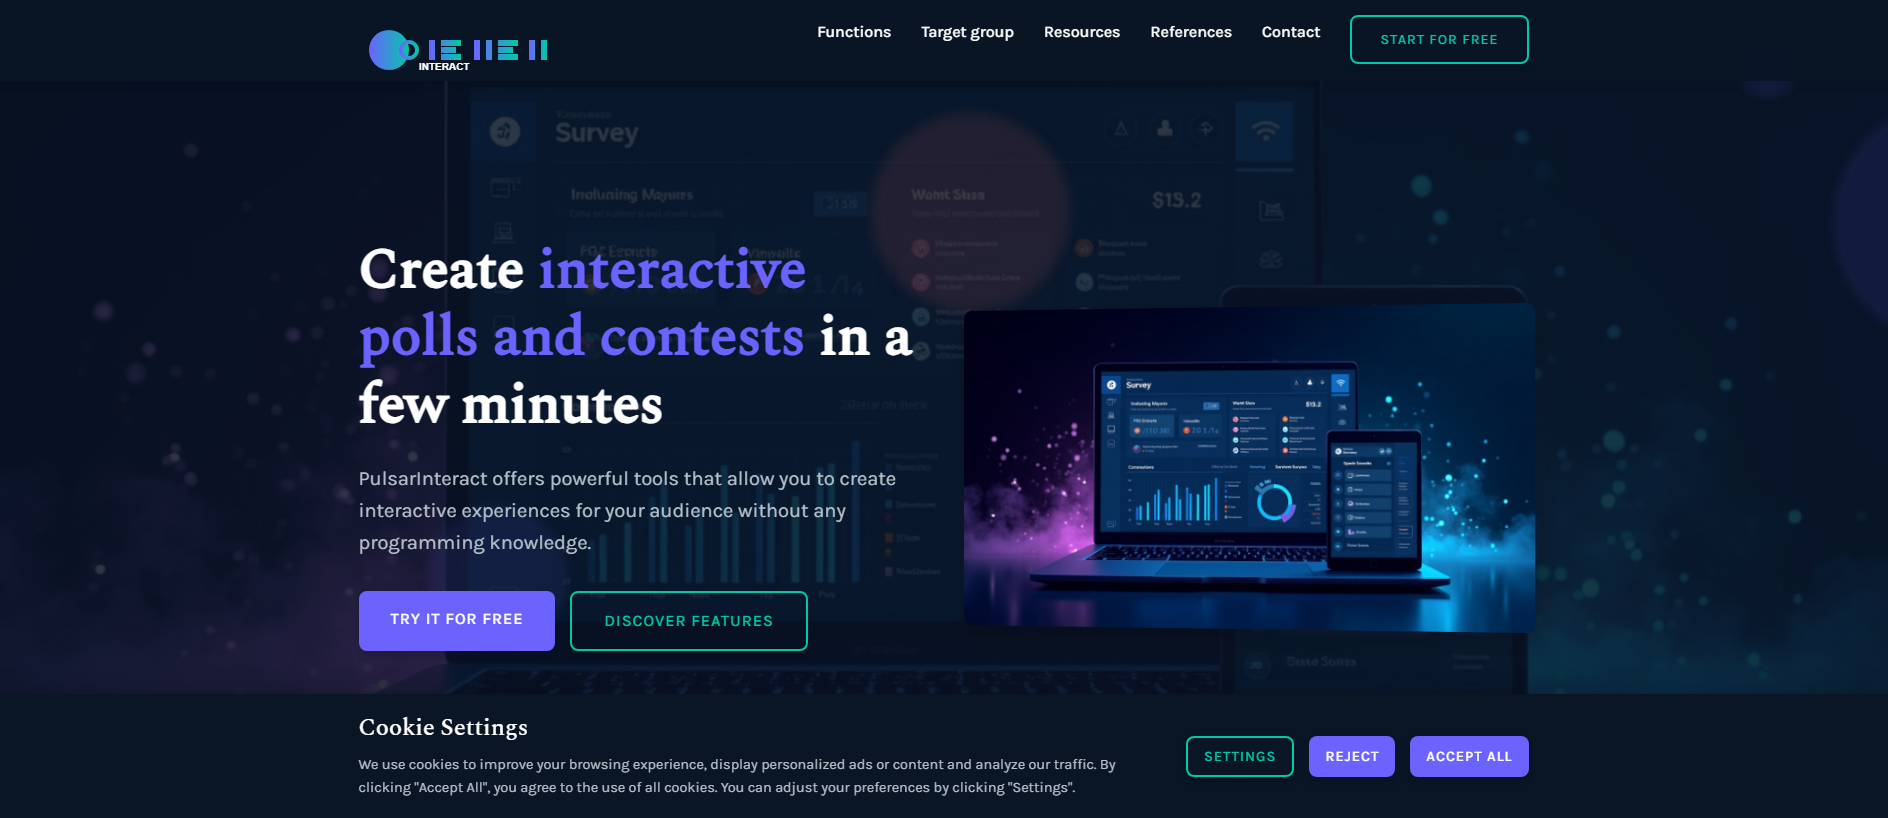
“PulsarInteract - Create interactive surveys and contests in minutes”
위협 평결
심각
85/100 증거 점수
가용성
마지막으로 알려진 활성
최근에 저장된 도달 가능성 관찰
위험 신호
VirusTotal 탐지: 6/91
Spamhaus DBL: DBL_PHISH
URLQuery threat systems: 1 alert
브랜드 사칭: Unknown
마지막으로 알려진 활성
Actions
API
보고서 요약
koipay.digital is a credential theft scam impersonating survey platforms. Domain flagged by 1/95 security vendors, mimics PulsarInteract branding, and remains.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
증거 요약
중요
This domain, koipay.digital, is actively engaged in credential theft operations targeting users of survey and contest platforms. Analysis of the site’s infrastructure reveals it impersonates PulsarInteract, a legitimate service for creating interactive surveys, to deceive victims into entering sensitive login credentials, personal data, or financial information. The fraudulent page title, 'PulsarInteract - Create interactive surveys and contests in minutes,' is designed to lend credibility and lower user suspicion, increasing the likelihood of successful exploitation. Technical indicators confirm the high-risk nature of this domain. VirusTotal reports that 1 out of 95 security vendors has flagged koipay.digital as malicious, while AlienVault OTX lists it in one threat intelligence pulse. The domain was registered on June 24, 2026, through NICENIC INTERNATIONAL GROUP CO., LIMITED, a registrar frequently associated with abusive registrations. It resolves to the IP address 188.114.97.3 and appears on one security blocklist, with a Gridinsoft trust score of 0/100. The SSL certificate, issued by Google Trust Services, provides a false sense of security, as encryption does not validate legitimacy. Users who have visited koipay.digital or entered credentials on the site should take immediate action. First, revoke any sessions or logins associated with the domain and change passwords for all accounts that may have been exposed, prioritizing email, financial, and administrative credentials. Enable multi-factor authentication where available to mitigate further risk. Monitor accounts for unauthorized activity, including logins, transactions, or profile changes. If financial data was entered, contact relevant institutions to report potential fraud and request account monitoring. Finally, scan the device used to access the domain for malware or unauthorized modifications, as credential theft sites often deploy secondary payloads.
VirusTotal
6 det.
URLQuery
1 threat alert
OTX references
URLScan
TLS 인증서
Google Trust Services
연령
3 mo New
관측 상태
마지막으로 알려진 활성 200

DestroyList
등재됨
데이터 적용 범위
VirusTotal
6 / 91
URLQuery
1 threat-system alert
OTX
1 community reference
CF 레이더
scan completed
URLScan capture
저장된 보고서
URLScan verdict
분석 완료
DNS 차단
14 확인됨 — 차단 없음
TLS
valid certificate, 86d
WHOIS
3 mo old
스크린샷
3 captures · 3 sources
네트워크 보안 인텔리전스 Registrar context
Threat Detection Systems
1 alert
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DNS4EU | koipay.digital |
malicious | Sinkholed |
Registrar context
NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
VirusTotal Detections Update Jun 28, 2026 · 18:14 UTCVirusTotal scanner detections updated from 1 to 1. Added scanner alerts: Fortinet.
위협 대응 Pipeline
발견
Checks
Reports
가용성
12/14
공개 차단 목록 상태
탐지 회피 분석
클로킹 의심: 스캐너와 방문자 제목이 다름
관찰되지 않음
저장된 스캔 결과에서는 클로킹 현상이 관찰되지 않았습니다.
이 호스트에 대해 저장된 크롤러 대 브라우저 관측 데이터와, 케이타로 스타일의 트래픽 분배 시스템을 위한 실시간 지문 확인 정보.
- 저장된 은신 플래그
- 관찰되지 않음
- 클로킹 점수
- 0/6
- 마지막 은폐 스캔
- 스캐너가 감지한 서버 헤더
cloudflare
스캐너 메모: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare
보안 스캐너에 표시된 제목Zephyr Wellness Institute - Personalized Weight Loss & Detox Programs in Toronto | Sustainable Management
브라우저 방문자에게 표시되는 제목PulsarInteract - Create interactive surveys and contests in minutes
TDS 지문 인식 실시간 확인
이 패널이 열려 있을 때 PhishDestroy 스캐너에서 실행되는 7개의 케이타로 지문과 크롤러 대 브라우저 비교 결과.
기다림
저장된 캡처 · 3 sources
도메인 인텔리전스
도메인
URLScan Verdict
분석 완료
score 0 report ↗
서버 / ASN
cloudflare · AS13335 Cloudflare, Inc.
IP Context
Cloudflare shared edge
origin IP hidden
Edge-IP 평판은 이 도메인에 귀속되지 않습니다.
등록기관
NiceNIC
 (RU)
PhishDestroy Investigation
(RU)
PhishDestroy Investigation
IP 주소
188.114.97.3
CDN
위치 Toronto, CA
네트워크AS13335 · CloudFlare, Inc.
원본 IP는 CDN 프록시 뒤에 숨겨져 있습니다. 에지 주소에 대한 역방향 IP 결과에는 관련되지 않은 테넌트가 포함되어 있습니다. 원본을 찾으려면 수동 DNS 또는 인증서 투명성 데이터가 필요합니다.
등록 정보생성됨 2026년 6월 24일 (89d · New) — Expires 2027년 6월 24일
HTTP 상태200
기술 세부 정보DNS, SSL SAN, 타임스탬프
최초 발견2026년 6월 28일
DOM Analysis
IoC Extraction
Submitted URLhttps://koipay.digital/
네임서버kehlani.ns.cloudflare.comlakas.ns.cloudflare.com
TLS Fingerprint
TLS Observation
Favicon Hash
ICANN OVERSIGHT
인증 및 RAA 상황
인증 및 RAA 상황
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
인증은 계약이지, 안전 보증 마크가 아닙니다.
ICANN 수수료 확인
RAA §3.18 읽기
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Latest Classified Outcome 2026-09-21 02:38:48 UTC
Primary outcome
활성 콘텐츠
reason: Ordinary HTTP content served 90% confidence
Attribution
source: Current Http Probe
Evidence layers
Availability: Content serving
Content: Content served at root
DNS: Resolved
Registration: Active
Latest HTTP observation
활성 콘텐츠 Ordinary HTTP content served 90% 2026-09-21 02:38:48 UTC
RDAP registration
활성 NICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765 RDAP HTTP 200 source: Rdap Status Collector clientDeleteProhibitedclientTransferProhibited expires 2027-06-24 11:39:12 UTC checked 2026-08-08 04:39:41 UTC
Observed timeline
last reachable: 2026-09-21 02:38:48 UTC last content: 2026-09-21 02:38:48 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
기술 · 8 identified
Bootstrap
UI frameworks
Amazon Web Services
PaaS
Unpkg
CDN
jsDelivr
CDN
HSTS
보안
Flickity
JavaScript libraries
Cloudflare
CDN
HTTP/3
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
이 도메인 신고하기
증거를 제출하고 다른 사람들을 보호하는 데 힘을 보태주세요
VirusTotal 분석
6 / 91 보안 공급업체가 이 도메인에 플래그를 지정했습니다.
View on VT
Last analyzed Previous stored snapshot: 6 detections
alphaMountain.ai
CRDF
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
SOCRadar
증거 및 외부 보고서
증권 분석
OSINT 및 정보
DNS 및 네트워크
SEO 및 도메인
이 사이트로 인해 영향을 받으셨나요?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.


PhishDestroy listing review 법 집행 보고서가 아님
도메인 이의신청
이 도메인을 소유하고 있고 목록이 잘못되었다고 생각되면 검토를 요청하세요.
회복 사기꾼들을 조심하세요! 범죄자는 수사관, 변호사, 회복요원인 척 하면서 피해자에게 다시 연락할 수도 있습니다. 선불 비용을 지불하거나 자격 증명을 공유하지 마십시오. 회복 관련 사기에 대해 자세히 알아보기 →
지역 당국에 신고하십시오
공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.
97개국 디렉토리
AI 지원 초안 - 사고 세부정보는 AI 제공업체에서 처리됩니다.
직접 검토하고 제출하세요.
관련 인프라 및 보고서
- 직접 링크 등록 정보나 동일한 피싱 키트를 공유합니다.
- 보조 신호 인프라 또는 대상 브랜드를 공유할 뿐, 단일 운영자라는 증거는 아닙니다.
- ‘디스커버리’ 전용 탐색용으로 나열됨; 이 호스트와 공통된 속성이 없음.
각 레인은 도메인이 이 호스트에 연결된 이유 중 하나를 나타냅니다. 노드의 크기는 VirusTotal 탐지 건수를 나타내며, 점선으로 표시된 노드는 이미 오프라인 상태입니다. 전체 목록은 아래와 같습니다.
Unknown 키트 8
Unknown 피싱 캠페인의 일부입니다. 모든 캠페인 도메인 보기 →
공유 Cloudflare 에지에 대한 기타 보고서 6
이러한 보고서는 동일한 공유 에지 IP로 확인됩니다. 이는 보고서 검색에 도움이 되지만 공통 소유권이나 공유 원본 서버를 의미하지는 않습니다.
Unknown 사칭 8
이 도메인들은 Unknown 사용자들도 표적으로 삼고 있습니다. Unknown의 모든 위협 보기 →
동일 등록기관: NiceNIC 6
동일한 등록 기관을 통해 등록되었습니다. 등록 기관은 서로 관련이 없는 수백만 명의 고객을 상대하기 때문에, 이는 두 항목 간의 연관성을 입증하기보다는 단순히 보고를 묶어놓은 것에 불과합니다.


최근 위협 보고서 6
최근 PhishDestroy 데이터베이스에서 보고서가 추가되었습니다. 이러한 검색 링크는 공유 인프라나 소유권을 의미하지 않습니다.