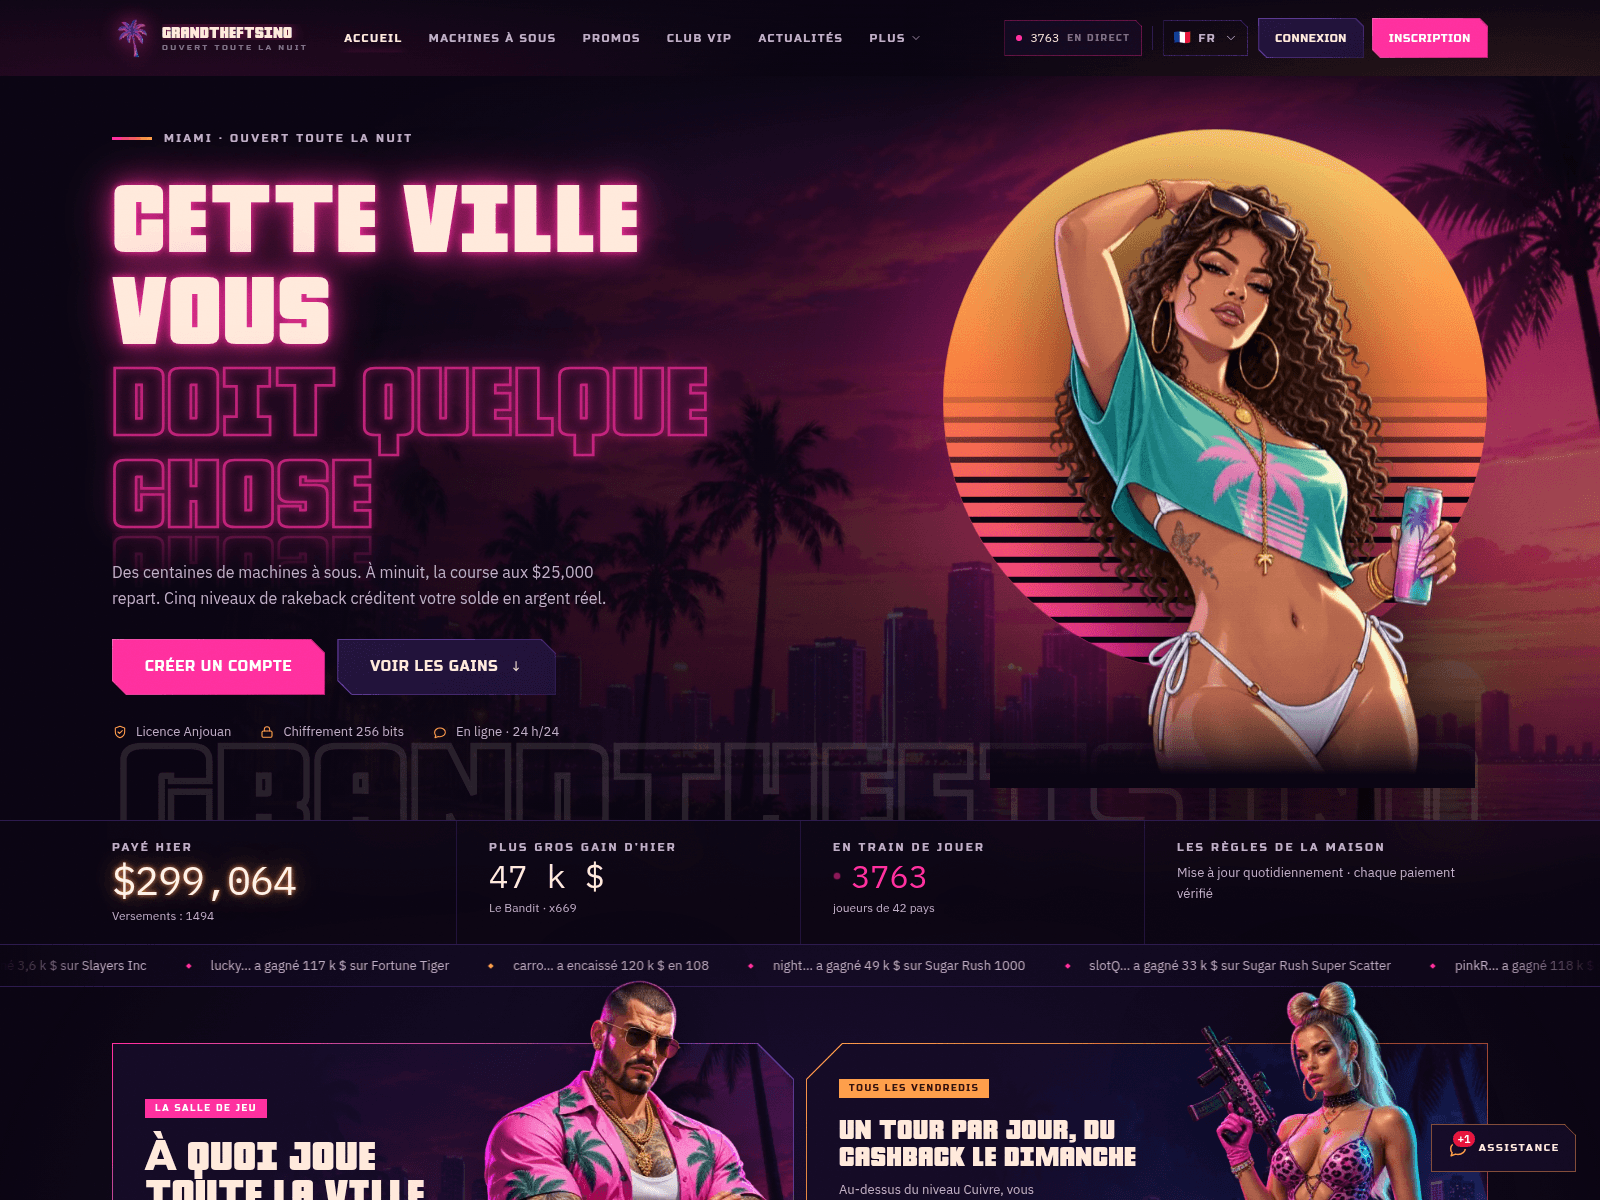
The site presents a French-language online casino interface titled "Grand Theft Sino" that prompts visitors to connect their Web3 wallets. Visitors who have interacted with the wallet connection prompts should immediately check their account permissions and revoke any granted token approvals.
분석 내용은 영어로만 제공됩니다.
페이지 제목: “Grandtheftsino — open all night”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 1/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-11-22 01:51 UTC. 조회 시간(저장된 표기): 2026-11-22 15:45 UTC. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
URLScan 캡처 · 2026-11-22 15:39 UTC · SHA-256 e478479d…fc2cff0
PhishDestroy 분석, 검토 완료된 버전
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Grand Theft Sino casino layout and Reown wallet integration
The grandtheftsino.com domain presents a French-language online casino portal designed with dark purples and neon pink accents. The top navigation bar includes brand links such as "ACCUEIL", "MACHINES À SOUS", "PROMOS", "CLUB VIP", "ACTUALITÉS", along with action buttons labelled "CONNEXION" and "INSCRIPTION". The main hero section displays neon typography stating "CETTE VILLE VOUS DOIT QUELQUE CHOSE" next to an illustration of a character holding a beverage against a sunset skyline backdrop. Subtext describes slot machines and prize pools, accompanied by buttons for "CRÉER UN COMPTE" and "VOIR LES GAINS". Footer notes mention "Licence Anjouan" and encryption details, while bottom tickers list recent payouts and active players. The platform integrates Reown wallet connection prompts, asking visitors to link their cryptocurrency wallets to the service.
Domain age and security telemetry findings
It was registered on 21 Nov 2026, 1 day before it was first reported, presenting a very brief operating history before its public listing. VirusTotal showed 1 of 92 engines flagging it on 22 Nov 2026, with Gridinsoft explicitly categorizing the address as a phishing threat, so the platform is not an isolated false alarm.
Wallet connection risks and token approval exposure
Because the portal prompts visitors to connect cryptocurrency wallets via Reown, interacting with these requests can expose digital assets to unauthorized transfers. Malicious or compromised dApp interfaces often request signature permissions that grant third-party contracts the ability to drain tokens from the user's wallet. Visitors who connected their wallets should check their account permissions on blockchain explorers and revoke any active spending approvals immediately.
grandtheftsino.com displays a French-language casino portal asking visitors to connect Web3 wallets, and it is flagged by 1 VirusTotal engine.
AI 요약
Grand Theft Sino casino layout and Reown wallet integration The grandtheftsino.com domain presents a French-language online casino portal designed with dark purples and neon pink accents. The top navigation bar includes brand links such as "ACCUEIL", "MACHINES À SOUS", "PROMOS", "CLUB VIP", "ACTUALITÉS", along with action buttons labelled "CONNEXION" and "INSCRIPTION". The main hero section displays neon typography stating "CETTE VILLE VOUS DOIT QUELQUE CHOSE" next to an illustration of a character holding a beverage against a sunset skyline backdrop. Subtext describes slot machines and prize pools, accompanied by buttons for "CRÉER UN COMPTE" and "VOIR LES GAINS". Footer notes mention "Licence Anjouan" and encryption details, while bottom tickers list recent payouts and active players. The platform integrates Reown wallet connection prompts, asking visitors to link their cryptocurrency wallets to the service. Domain age and security telemetry findings It was registered on 21 Nov 2026, 1 day before it was first reported, presenting a very brief operating history before its public listing. VirusTotal showed 1 of 92 engines flagging it on 22 Nov 2026, with Gridinsoft explicitly categorizing the address as a phishing threat, so the platform is not an isolated false alarm. Wallet connection risks and token approval exposure Because the portal prompts visitors to connect cryptocurrency wallets via Reown, interacting with these requests can expose digital assets to unauthorized transfers. Malicious or compromised dApp interfaces often request signature permissions that grant third-party contracts the ability to drain tokens from the user's wallet. Visitors who connected their wallets should check their account permissions on blockchain explorers and revoke any active spending approvals immediately.
Ogurl: https://grandtheftsino.com; Title: Grandtheftsino — open all night; Ogtype: website; Ogimage: https://grandtheftsino.com/designs/miami-roll/image/873d201a4b51c0f013d644162c4365a9bcc268f6f5850e391c5750bd6bf432a8/social-card.jpg; Ogtitle: Grandtheftsino — open all night; Ogsitename: Grandtheftsino; Description: Play at Grandtheftsino: a lit lobby, clear promotional terms and payouts you can follow stage by stage.; Twittercard: Summary large image; Ogdescription: Play at Grandtheftsino: a lit lobby, clear promotional terms and payouts you can follow stage by stage.
PhishDestroy는 기록된 증거를 바탕으로 grandtheftsino.com를 높음 위험 등급(증거 점수 63/100)으로 평가했으며, 이는 2026-11-22에 처음 기록되었습니다. 저장된 VirusTotal 결과: 1/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-11-22 01:51 UTC. 조회 시간(저장된 표기): 2026-11-22 15:45 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
grandtheftsino.com에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
grandtheftsino.com을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.


 Tucows


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT